

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
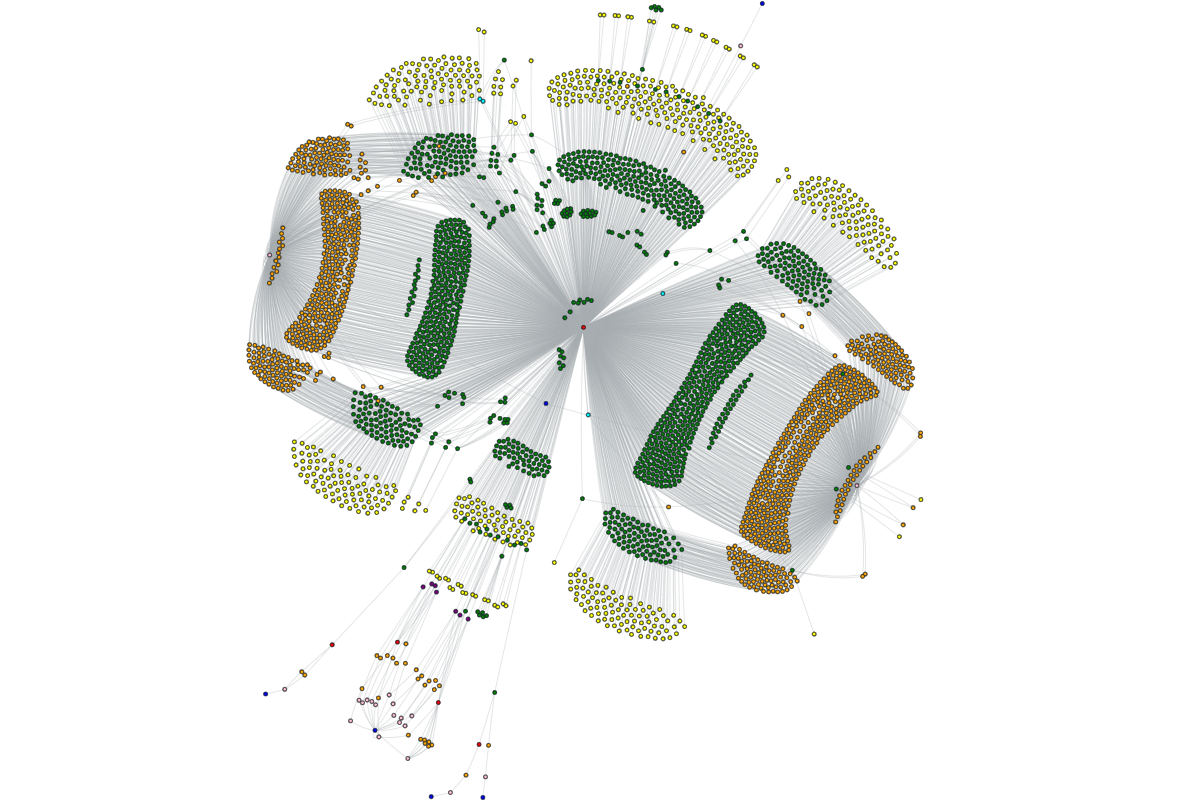 owasp-amass/amass
In-depth attack surface mapping and asset discovery

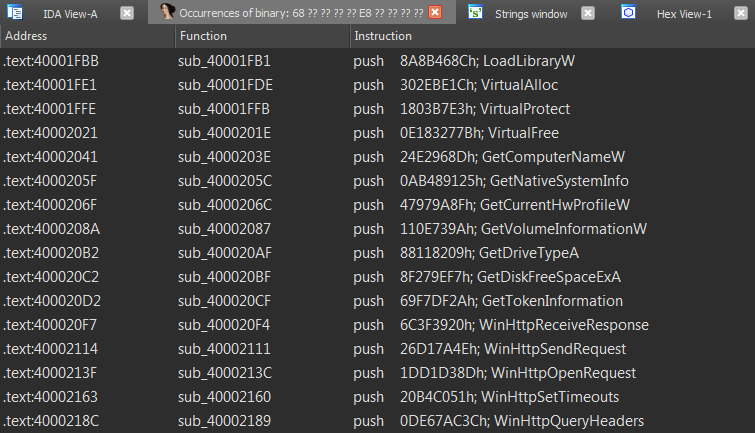 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 lucthienphong1120/full-60-ddos-tools
Collection of 60 Python-based DDoS attack tools for network stress testing and security assessment, featuring automated packet flooding scripts to…
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 abrewer251/cve-2025-1974_ingressnightmare_poc
Automates sending JSON payloads to multiple IPs via curl to test for CVE-2025-1974 (IngressNightmare), classifying responses and generating XML…
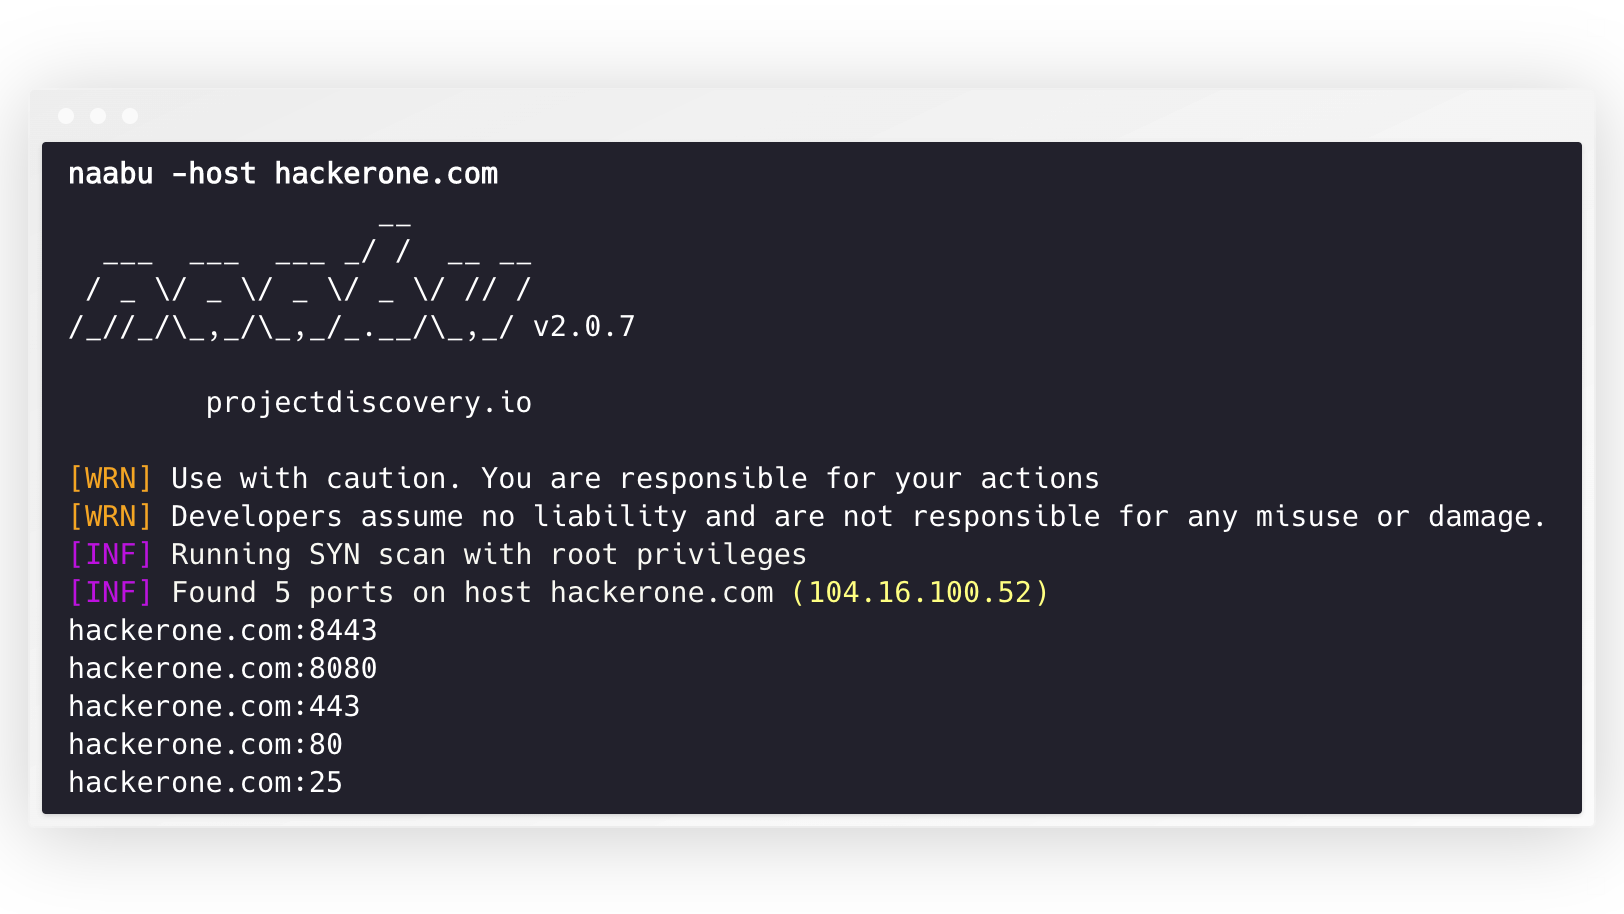 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 ap0dexme0/cve-2024-6387
OpenSSH RCE Massive Vulnerable Scanner
 psycostea/pi-zero-2w-bad-usb
Configure your Pi Zero 2W to be a BadUSB
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
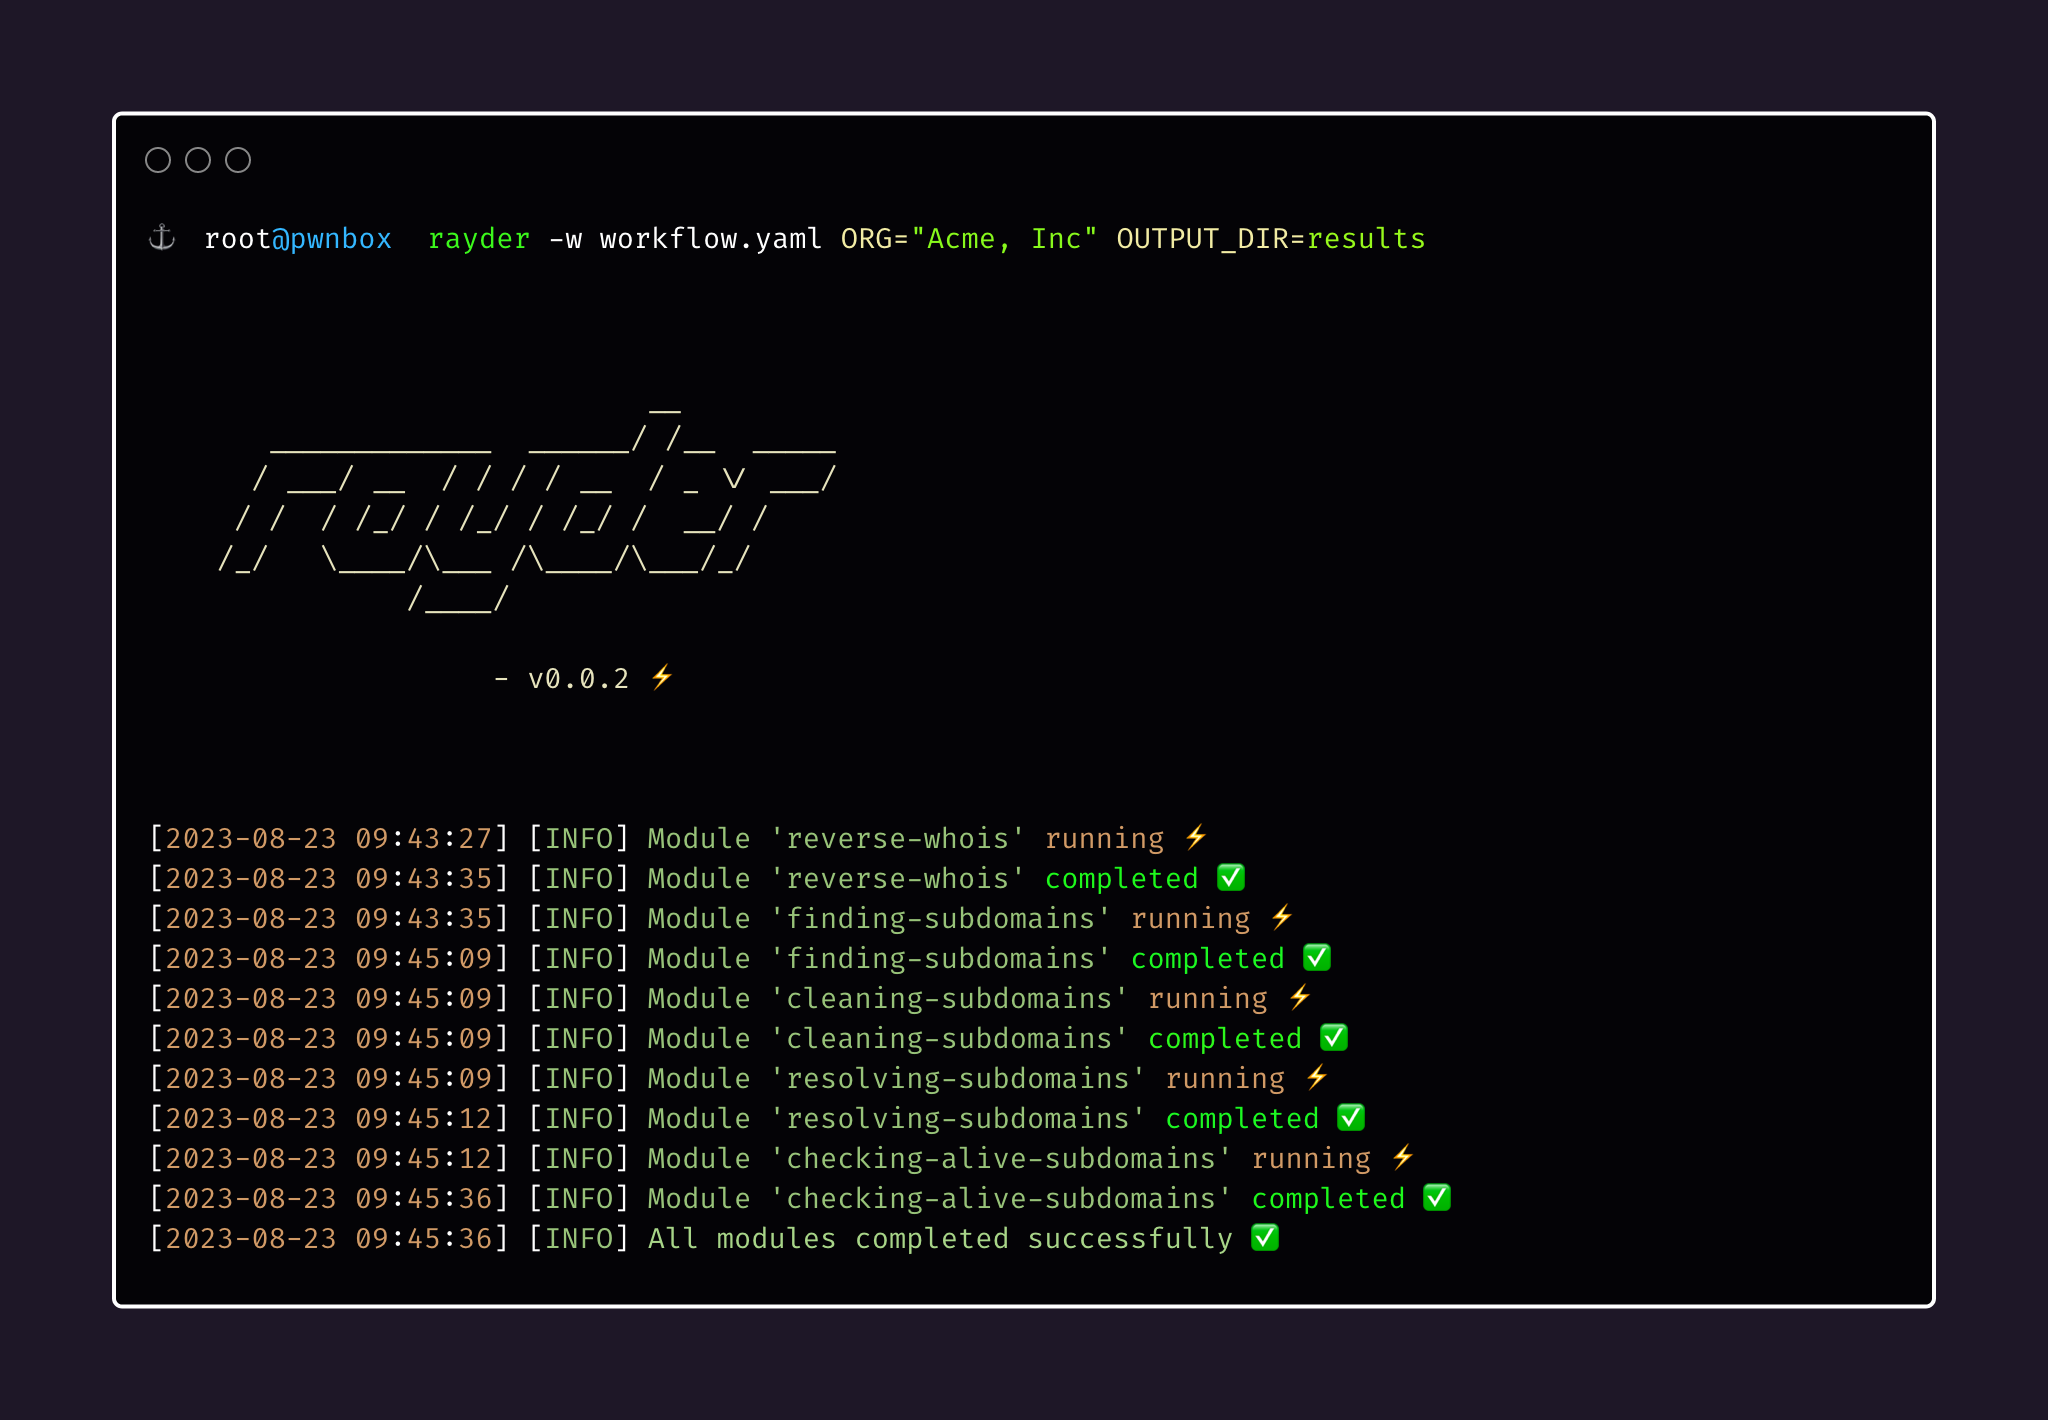 devanshbatham/rayder
A lightweight tool for orchestrating and organizing your bug hunting recon / pentesting command-line workflows
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.