

scapy
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
bluetooth-securitycryptographydata-exfiltration+23
12.6k
secdev/scapyPython-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
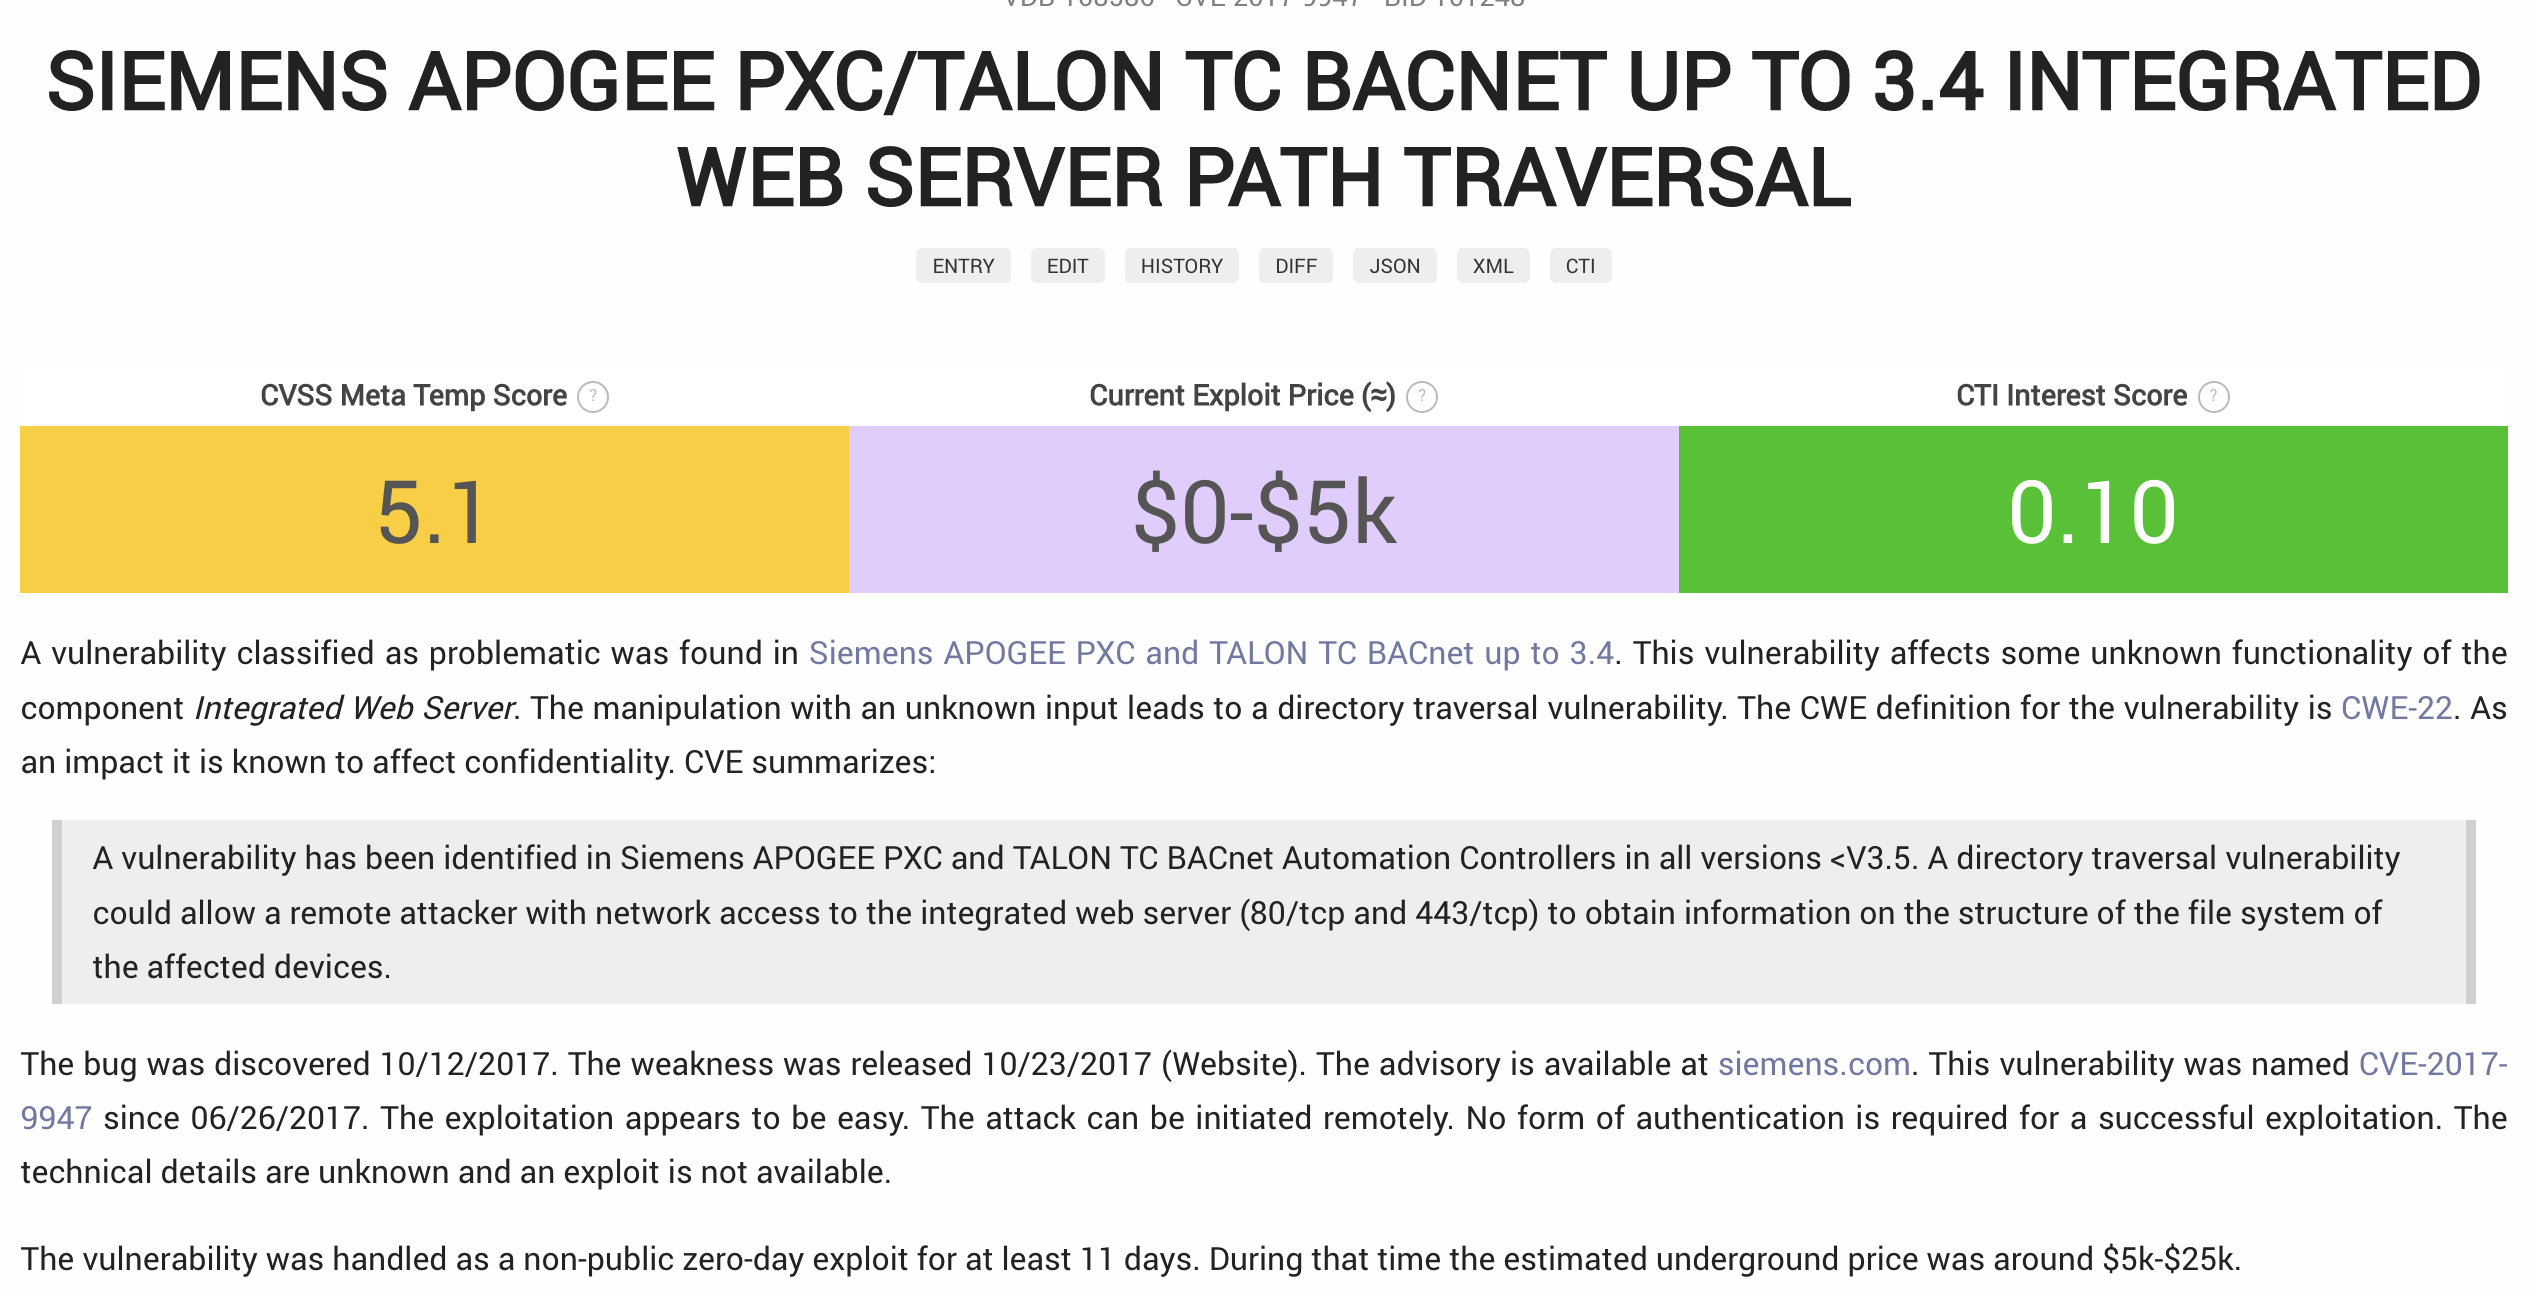 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 ret2/pwn2own-auto-2024-charx
Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…
 aliasrobotics/aztarna
aztarna, a footprinting tool for robots.
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
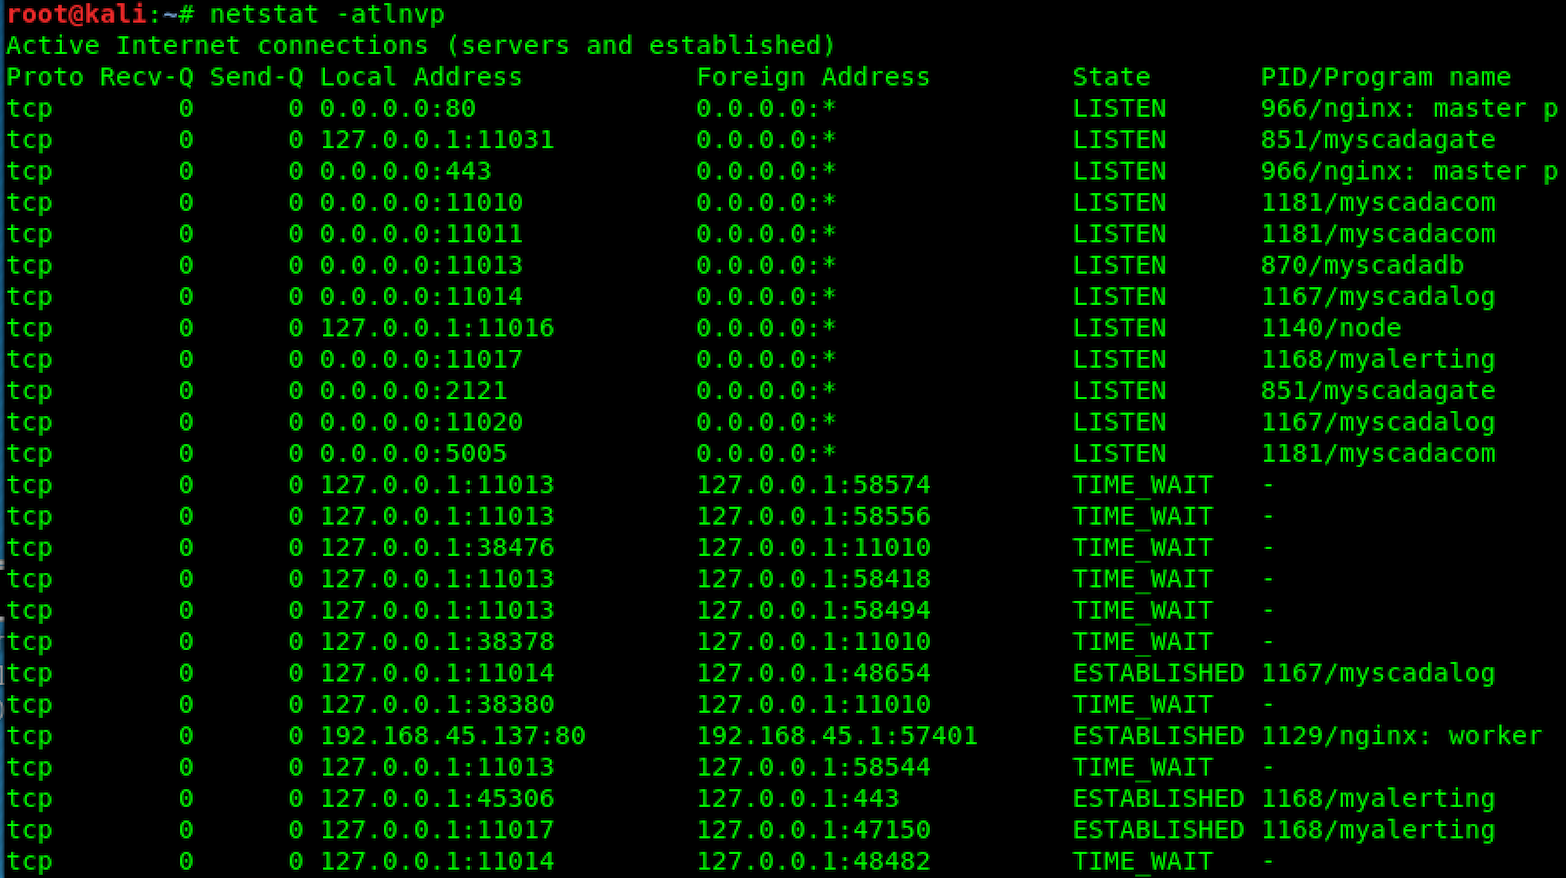 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 can/cve-2015-5374-dos-poc
DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 yanissec/cve-2018-7849
CVE-2018-7849
 yanissec/cve-2018-7845
CVE-2018-7845