
ICSFuzz
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
dynamic-code-analysisembedded-systems-securityfuzzing+3
30
momalab/icsfuzzInstrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 greenforcenetworks/cve-2025-41646---critical-authentication-bypass-
CVE-2025-41646 - Critical Authentication bypass
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
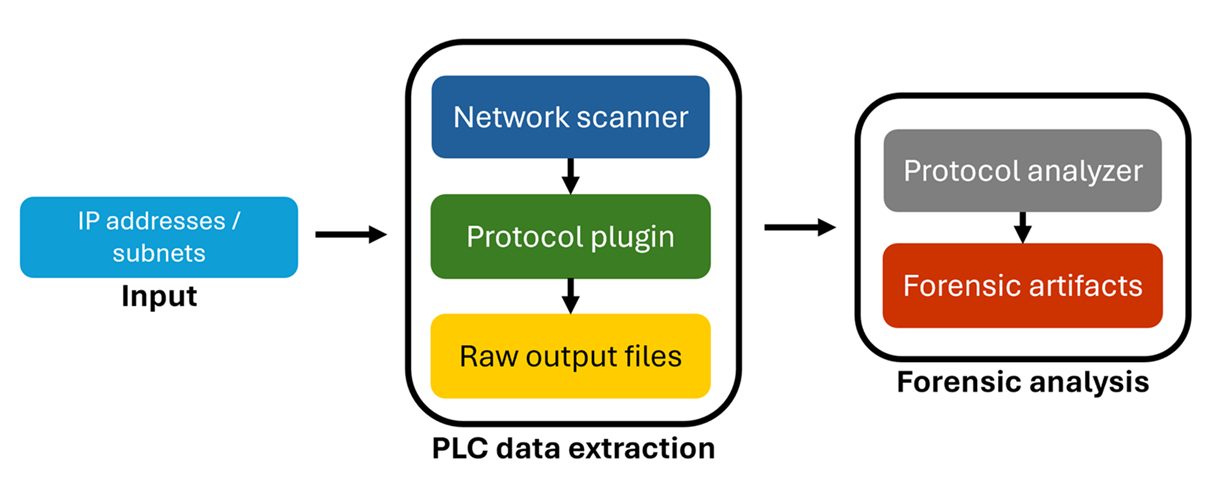 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
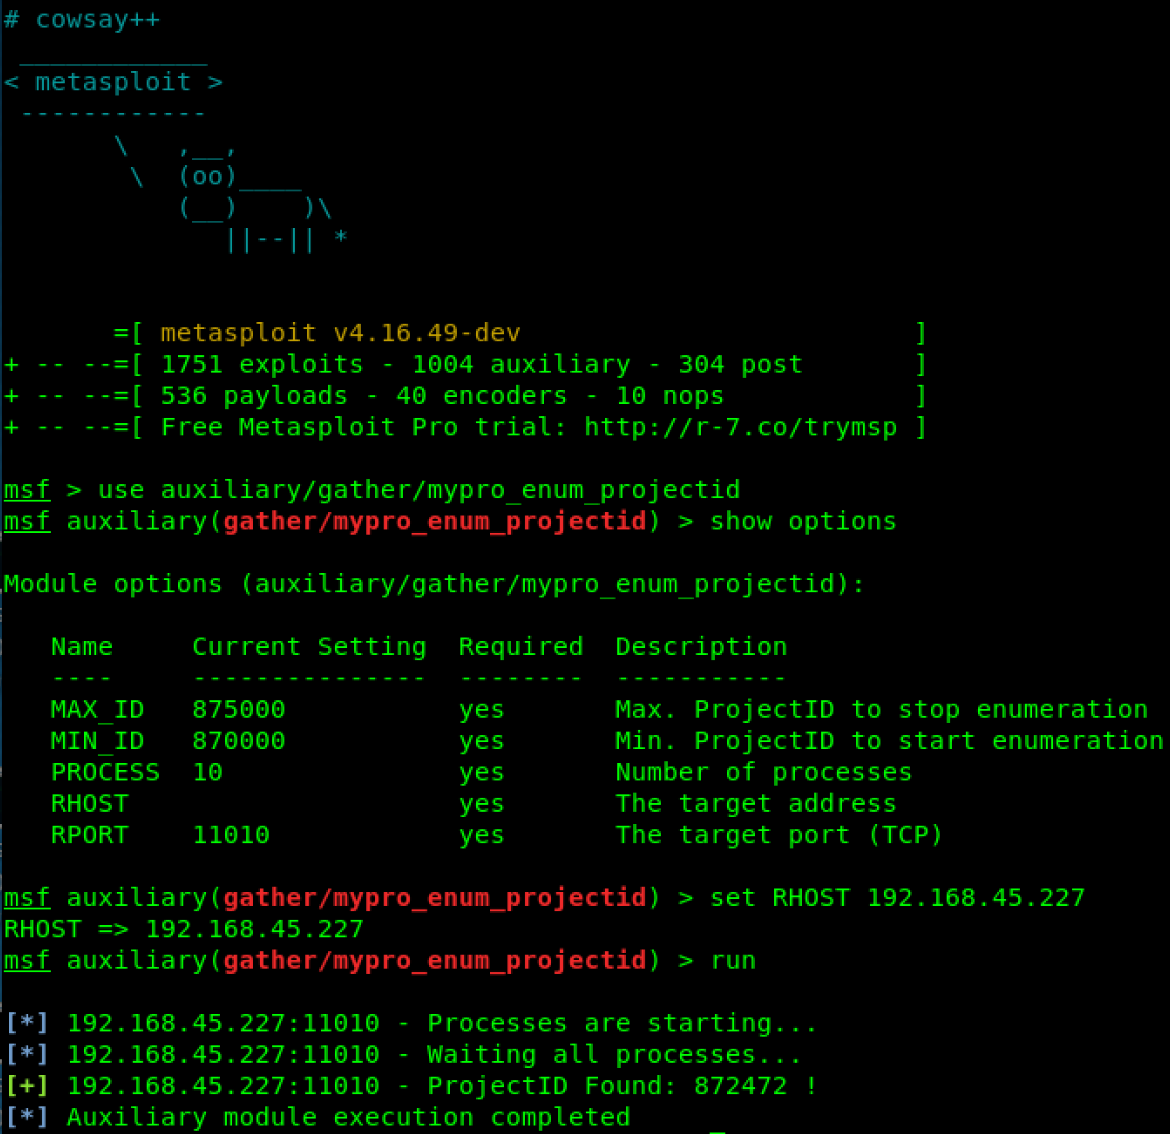 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.
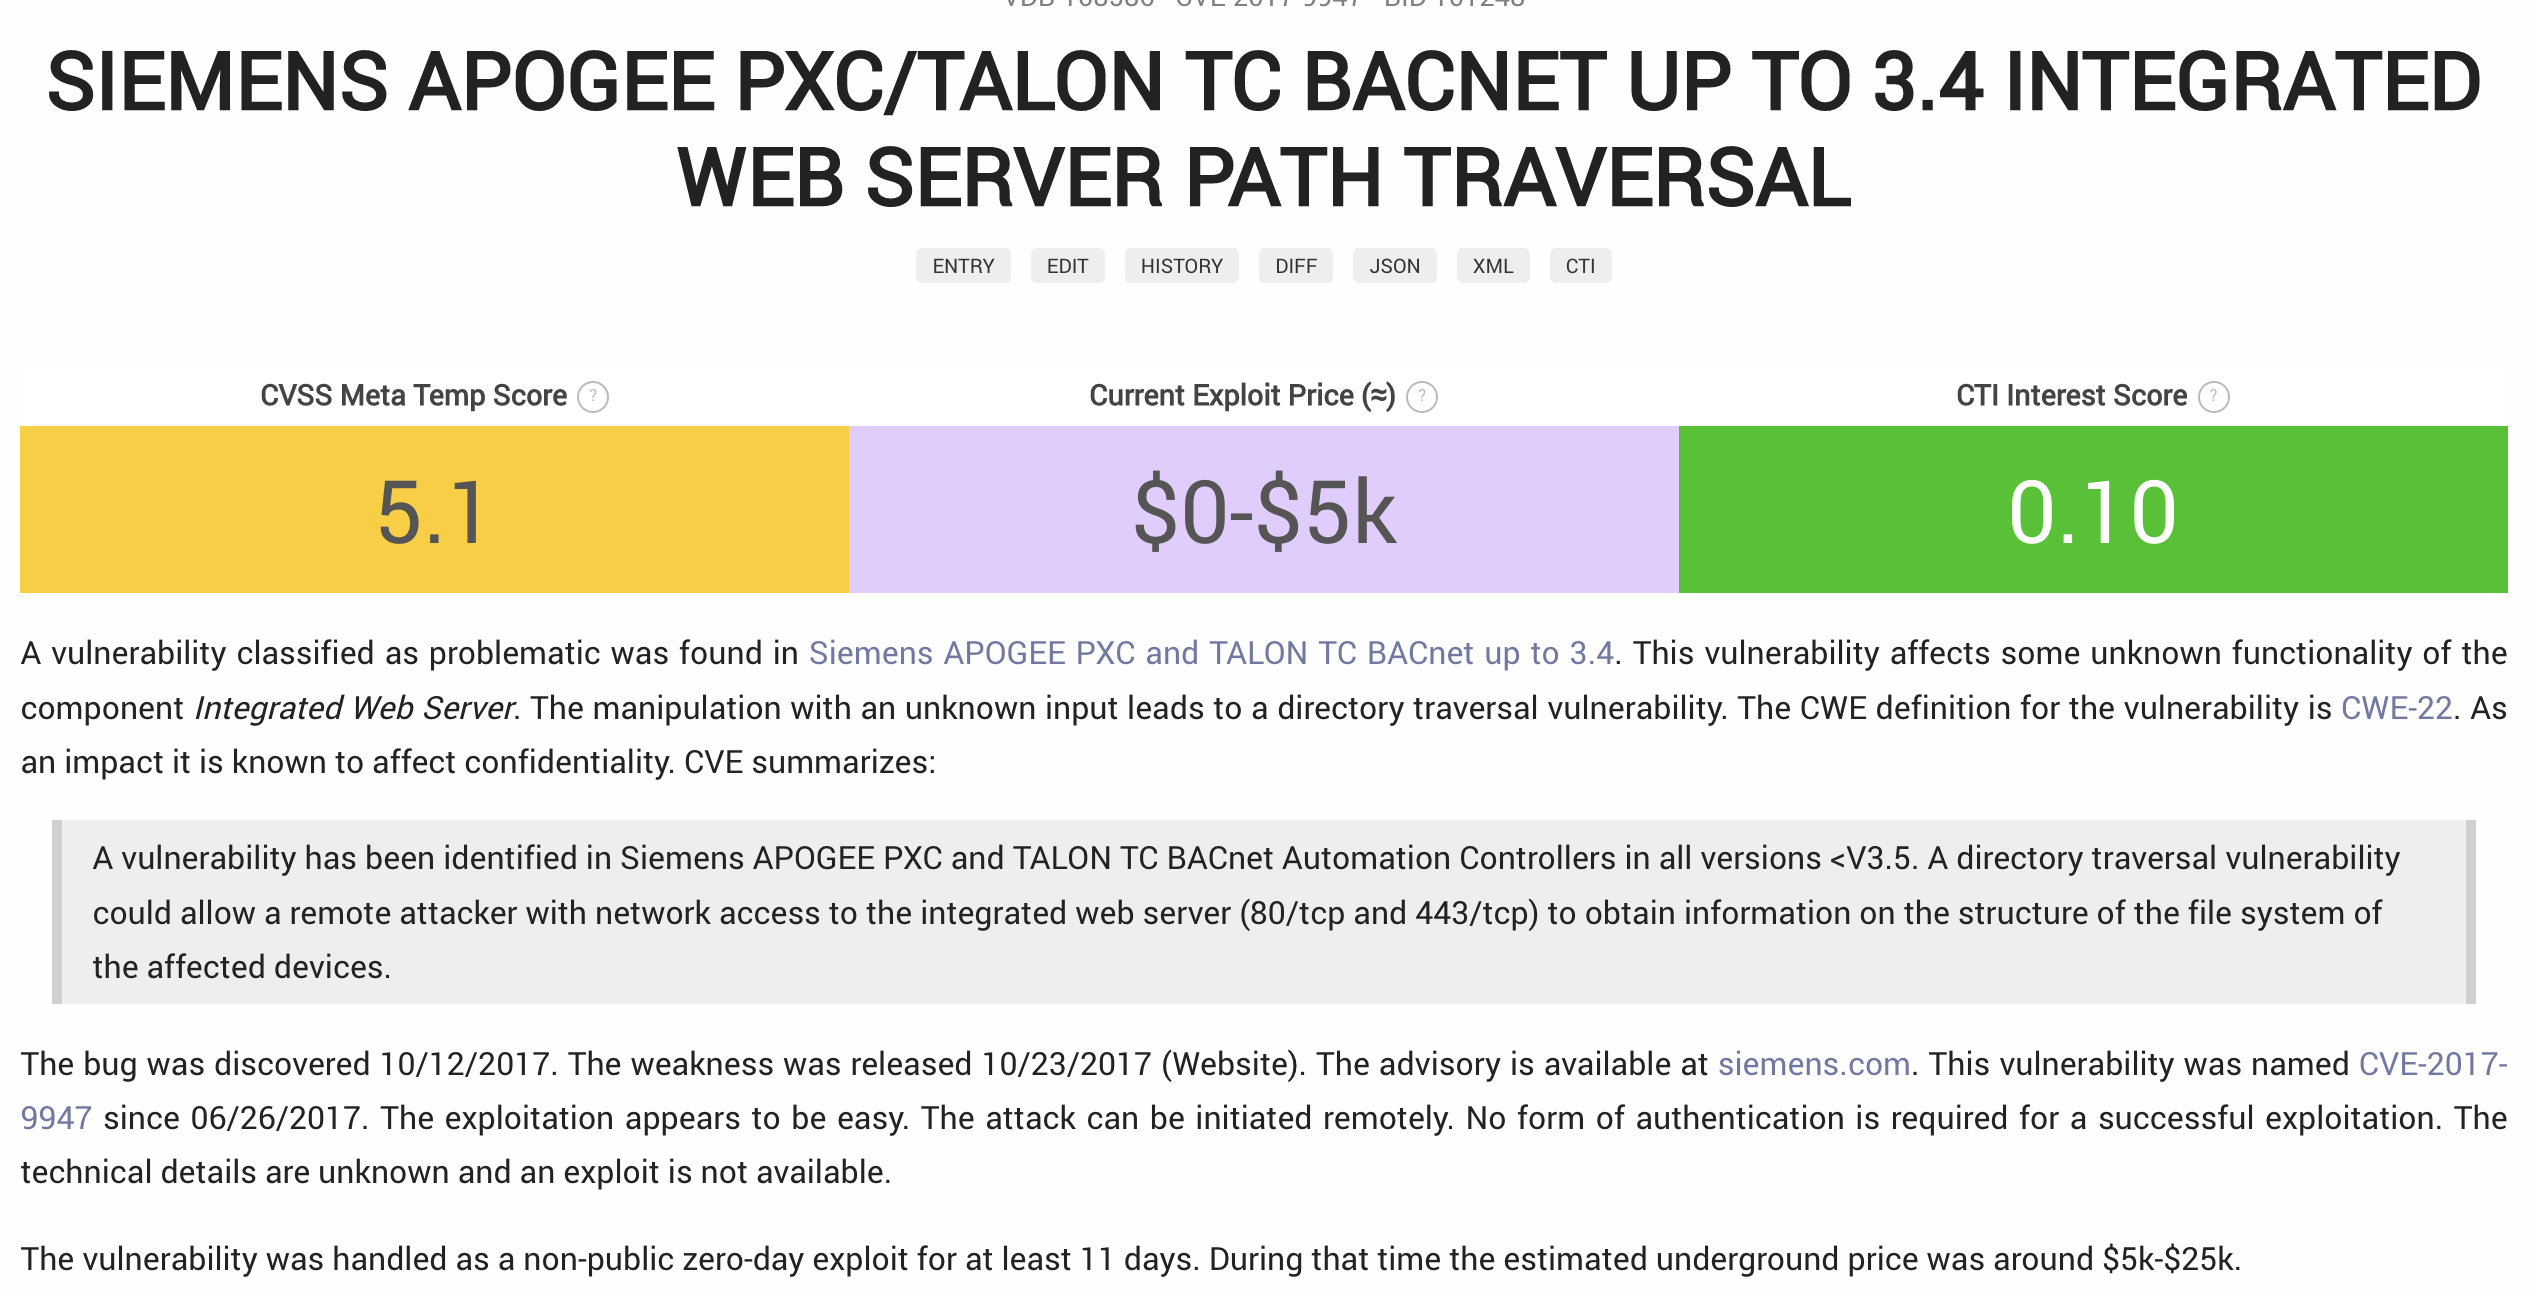 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 akbarq/cve-2009-0473-check
Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 webraybtl/cve-2022-1068
Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现