
ICS-Security-Tools
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
curated-resourcesdefensive-toolseducation+4
2.1k
iti/ics-security-toolsTools, tips, tricks, and more for exploring ICS Security.
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 shoucheng3/yamcs__yamcs_cve-2023-45277_5-8-6
Java-based mission control framework with YAML configuration, supporting telemetry, commanding, and simulation for spacecraft operations. Includes…
 spinfosecurity/rail-ot-protector
Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…
 geeknik/scada-scanner
A high-performance, asynchronous SCADA/ICS scanner
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
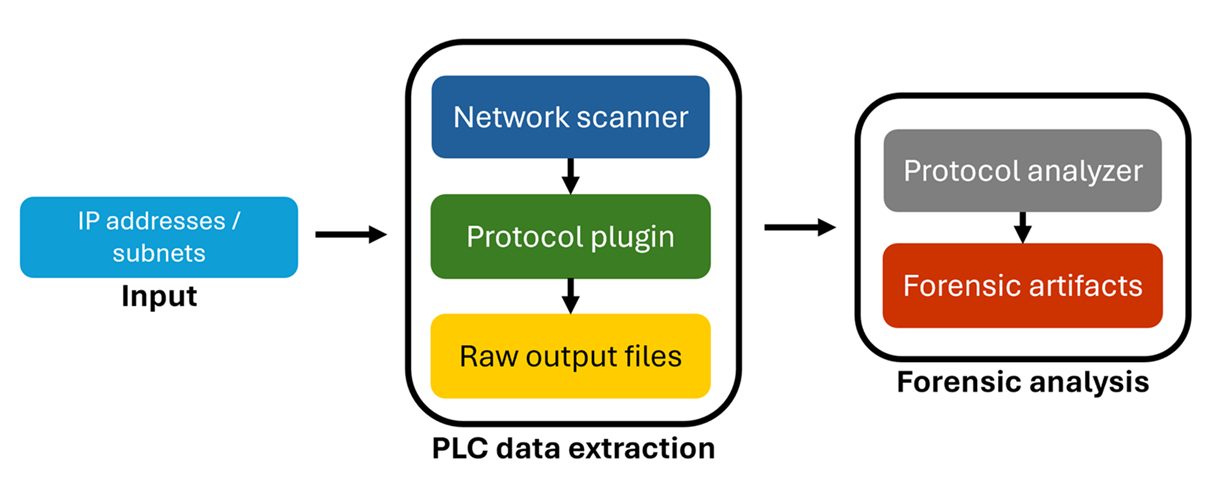 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 scy-phy/minicps
Real-time simulation framework for cyber-physical systems with physical process/control device models and Mininet-based network emulation, built for…
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
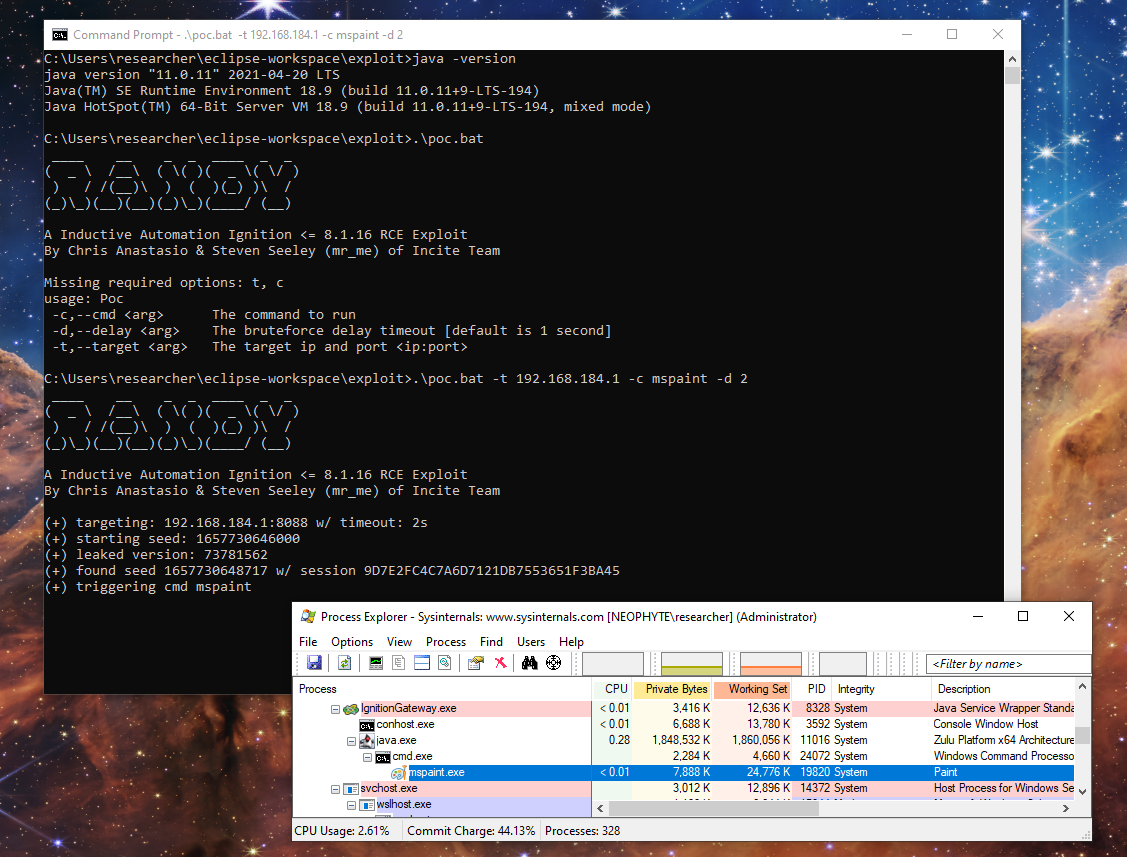 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 ret2/pwn2own-auto-2024-charx
Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability