
OpenPLC_v3
 tranquac/openplc_v3
To reproduce CVE-2021-31630
code-analysiscommand-and-controlexploitation+3
tranquac/openplc_v3To reproduce CVE-2021-31630
 greenforcenetworks/cve-2025-41646---critical-authentication-bypass-
CVE-2025-41646 - Critical Authentication bypass
 spanwich/sel4-ics-gateway-demo
Defensive security demo: seL4 microkernel gateway protecting vulnerable ICS from CVE-2019-14462
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 kevinherron/stack-overflow-poc
PoC for CVE-2018-12086 affecting various OPC UA stacks
 0xfml/cve-2023-30765
CVE-2023-30765 / ZDI-23-905 - Delta Electronics Infrasuite Device Master Privilege Escalation
 yanissec/cve-2018-7844
CVE-2018-7844
 yanissec/cve-2018-7842
CVE-2018-7842
 yanissec/cve-2018-7843
CVE-2018-7843
 yanissec/cve-2018-7852
CVE-2018-7852
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 kernoelpanic/cve-2015-8299
Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…
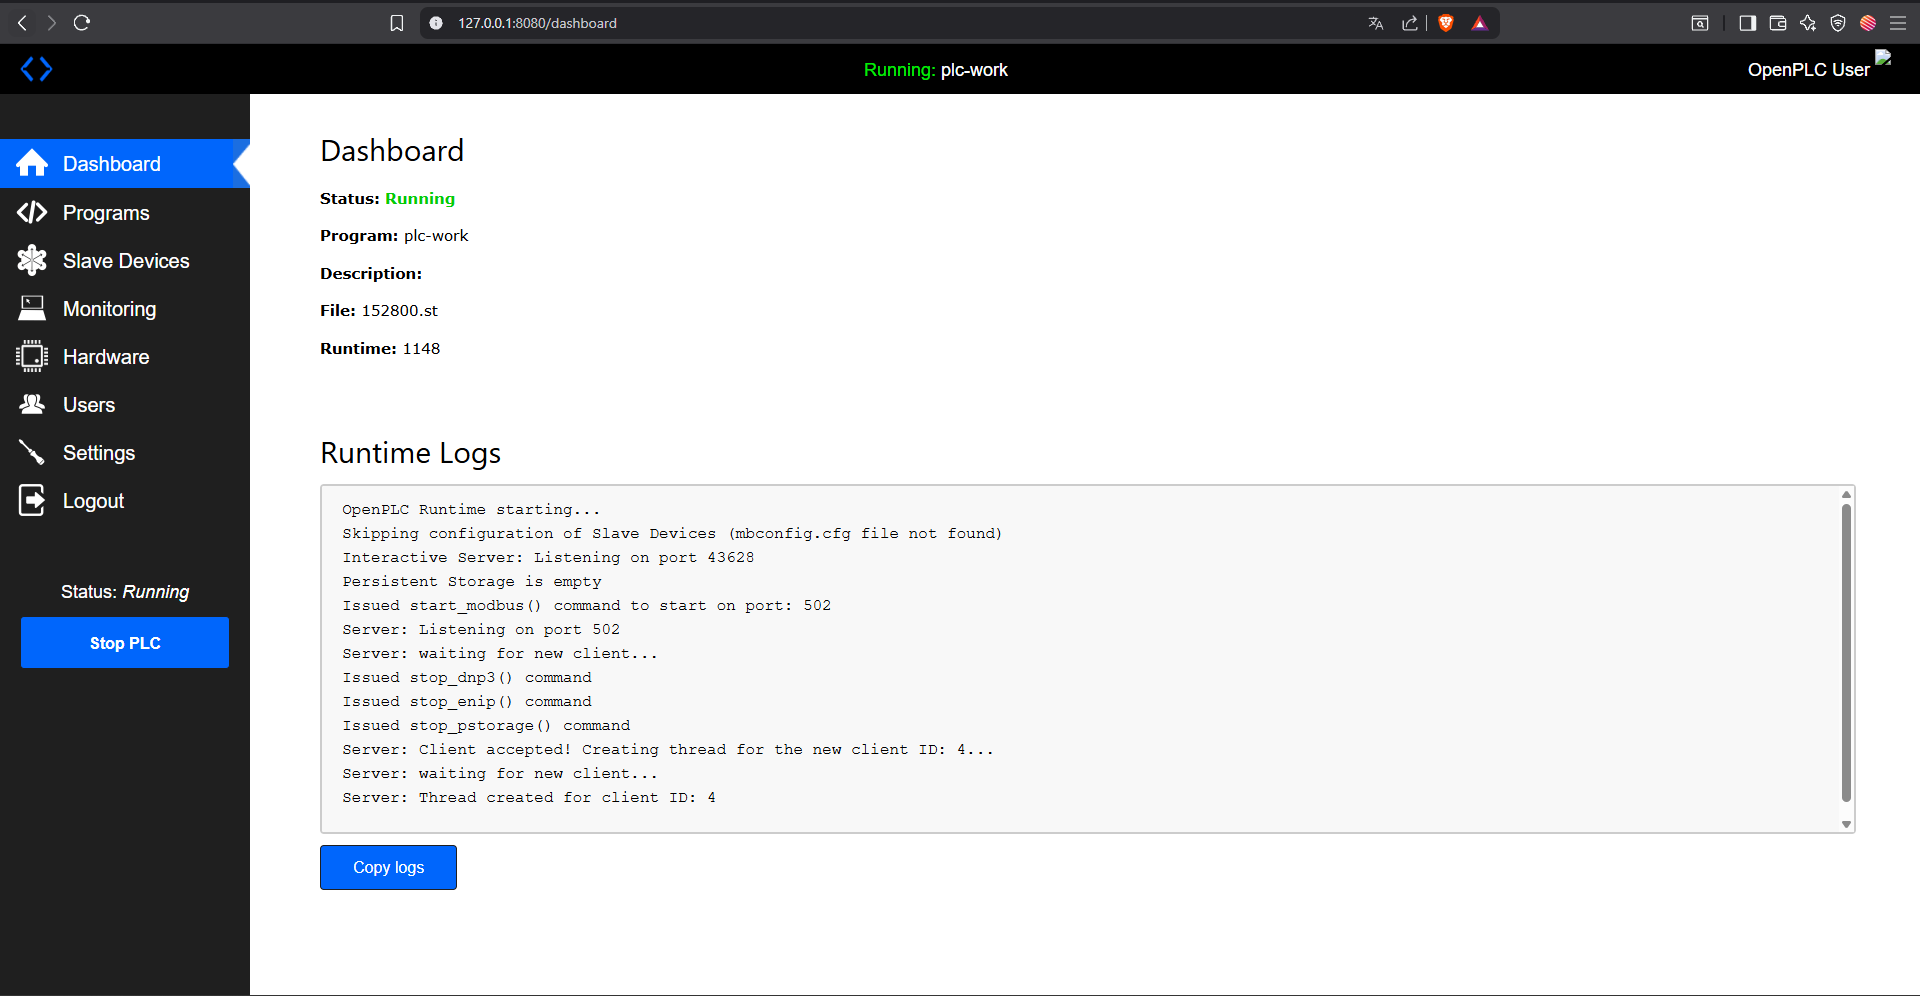 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 yanissec/cve-2018-7848
CVE-2018-7848
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 yanissec/cve-2018-7846
CVE-2018-7846
 yanissec/cve-2018-7854
CVE-2018-7854