Industrial Security Auditing Framework

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR

PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.

Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock

Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver

Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A

ICS-Park Smart Park Management System v2.0

Fuzzer for the Sparkplug B IIoT protocol

Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…

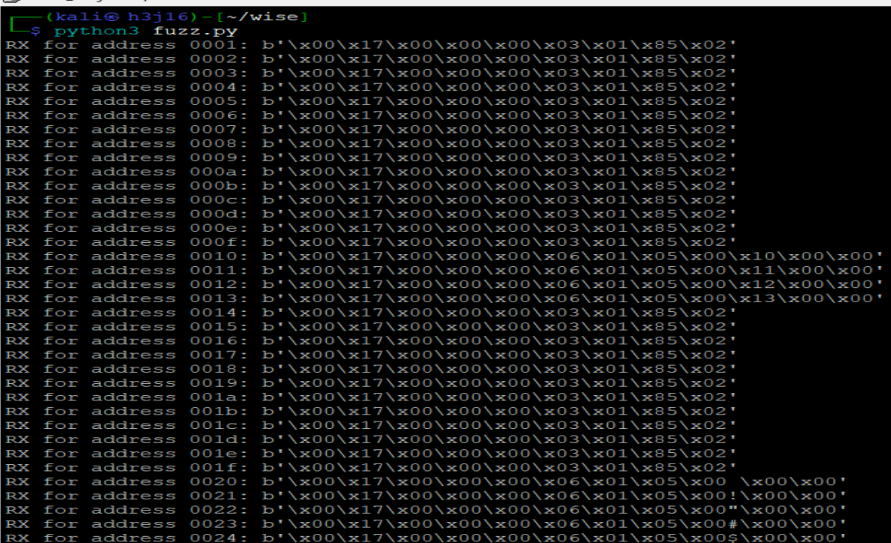
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control

Schneider Electric Magelis HMI Resource Consumption Vulnerabilities [ICSA-16-308-02, CVE-2016-8367, CVE-2016-8374]

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…

There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…

Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…

CVE-2018-7849

CVE-2018-7845

Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability

CVE-2016-3962-Exploit