
Archived
APOLOGEE
 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
authenticationexploitationexploit-frameworks+8
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
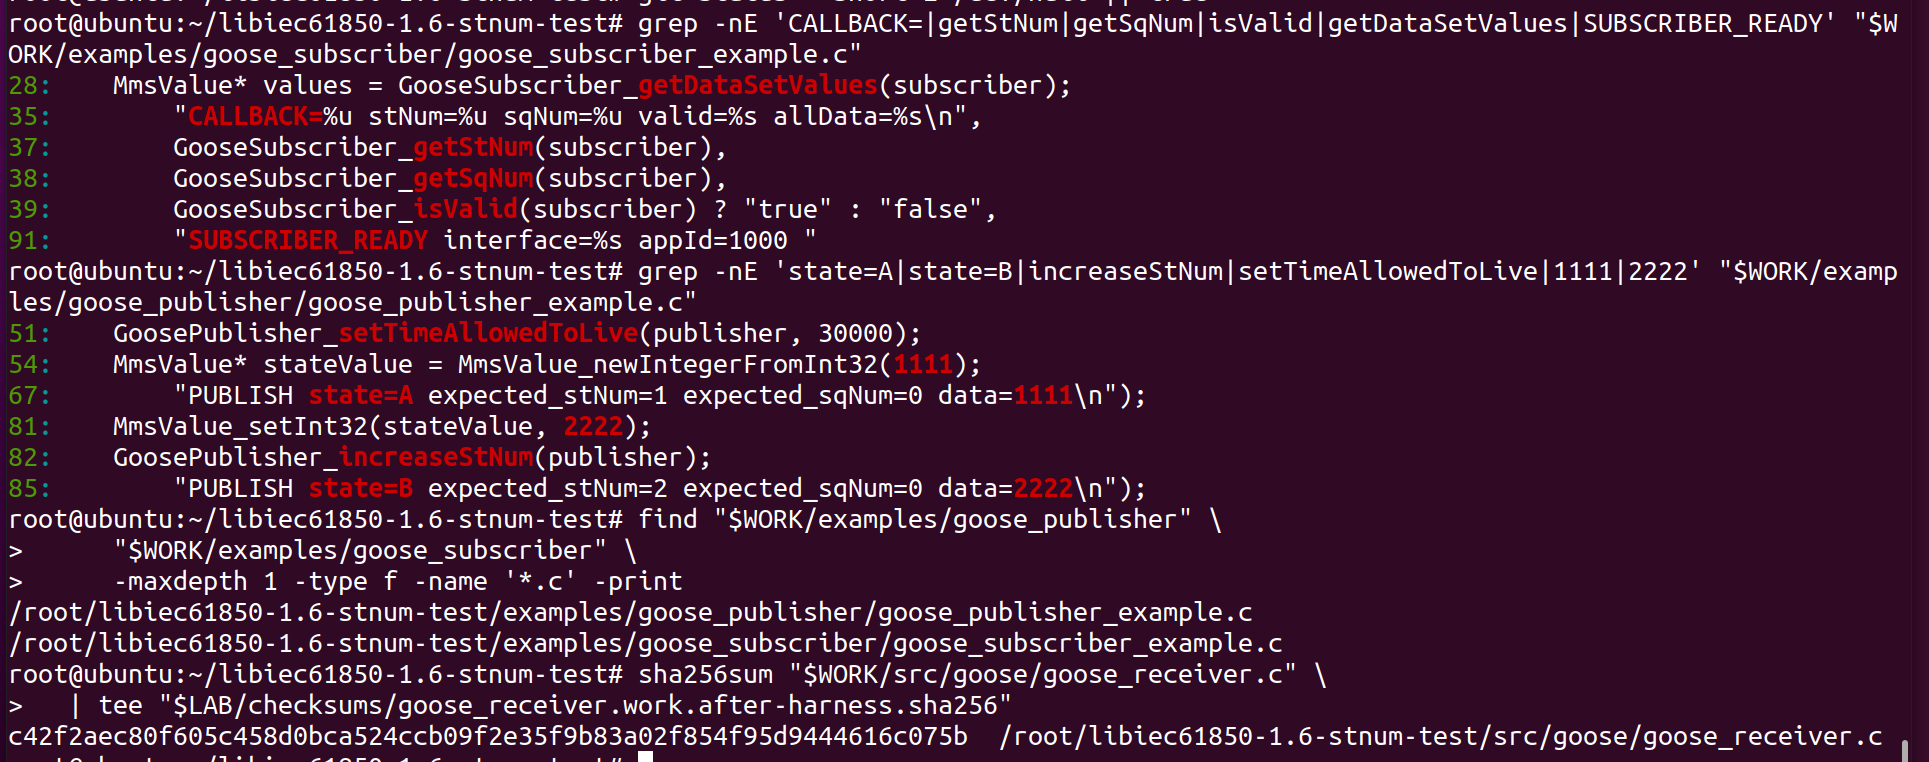 if-forget/cve-2026-52134-libiec61850
Public technical advisory and reproduction evidence for CVE-2026-52134 affecting GOOSE replay handling in libiec61850 v1.6.
 0xmhany/cve-2026-9645-scadabr-analysis
Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.
 murataydemir/purdue-model-for-industrial-control-system-environments
Purdue Model for Industrial Control System (ICS) Environments (Turkish)
 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 nullbyte8080/cve-2026-36226
Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
 cisagov/cset
Cybersecurity Evaluation Tool
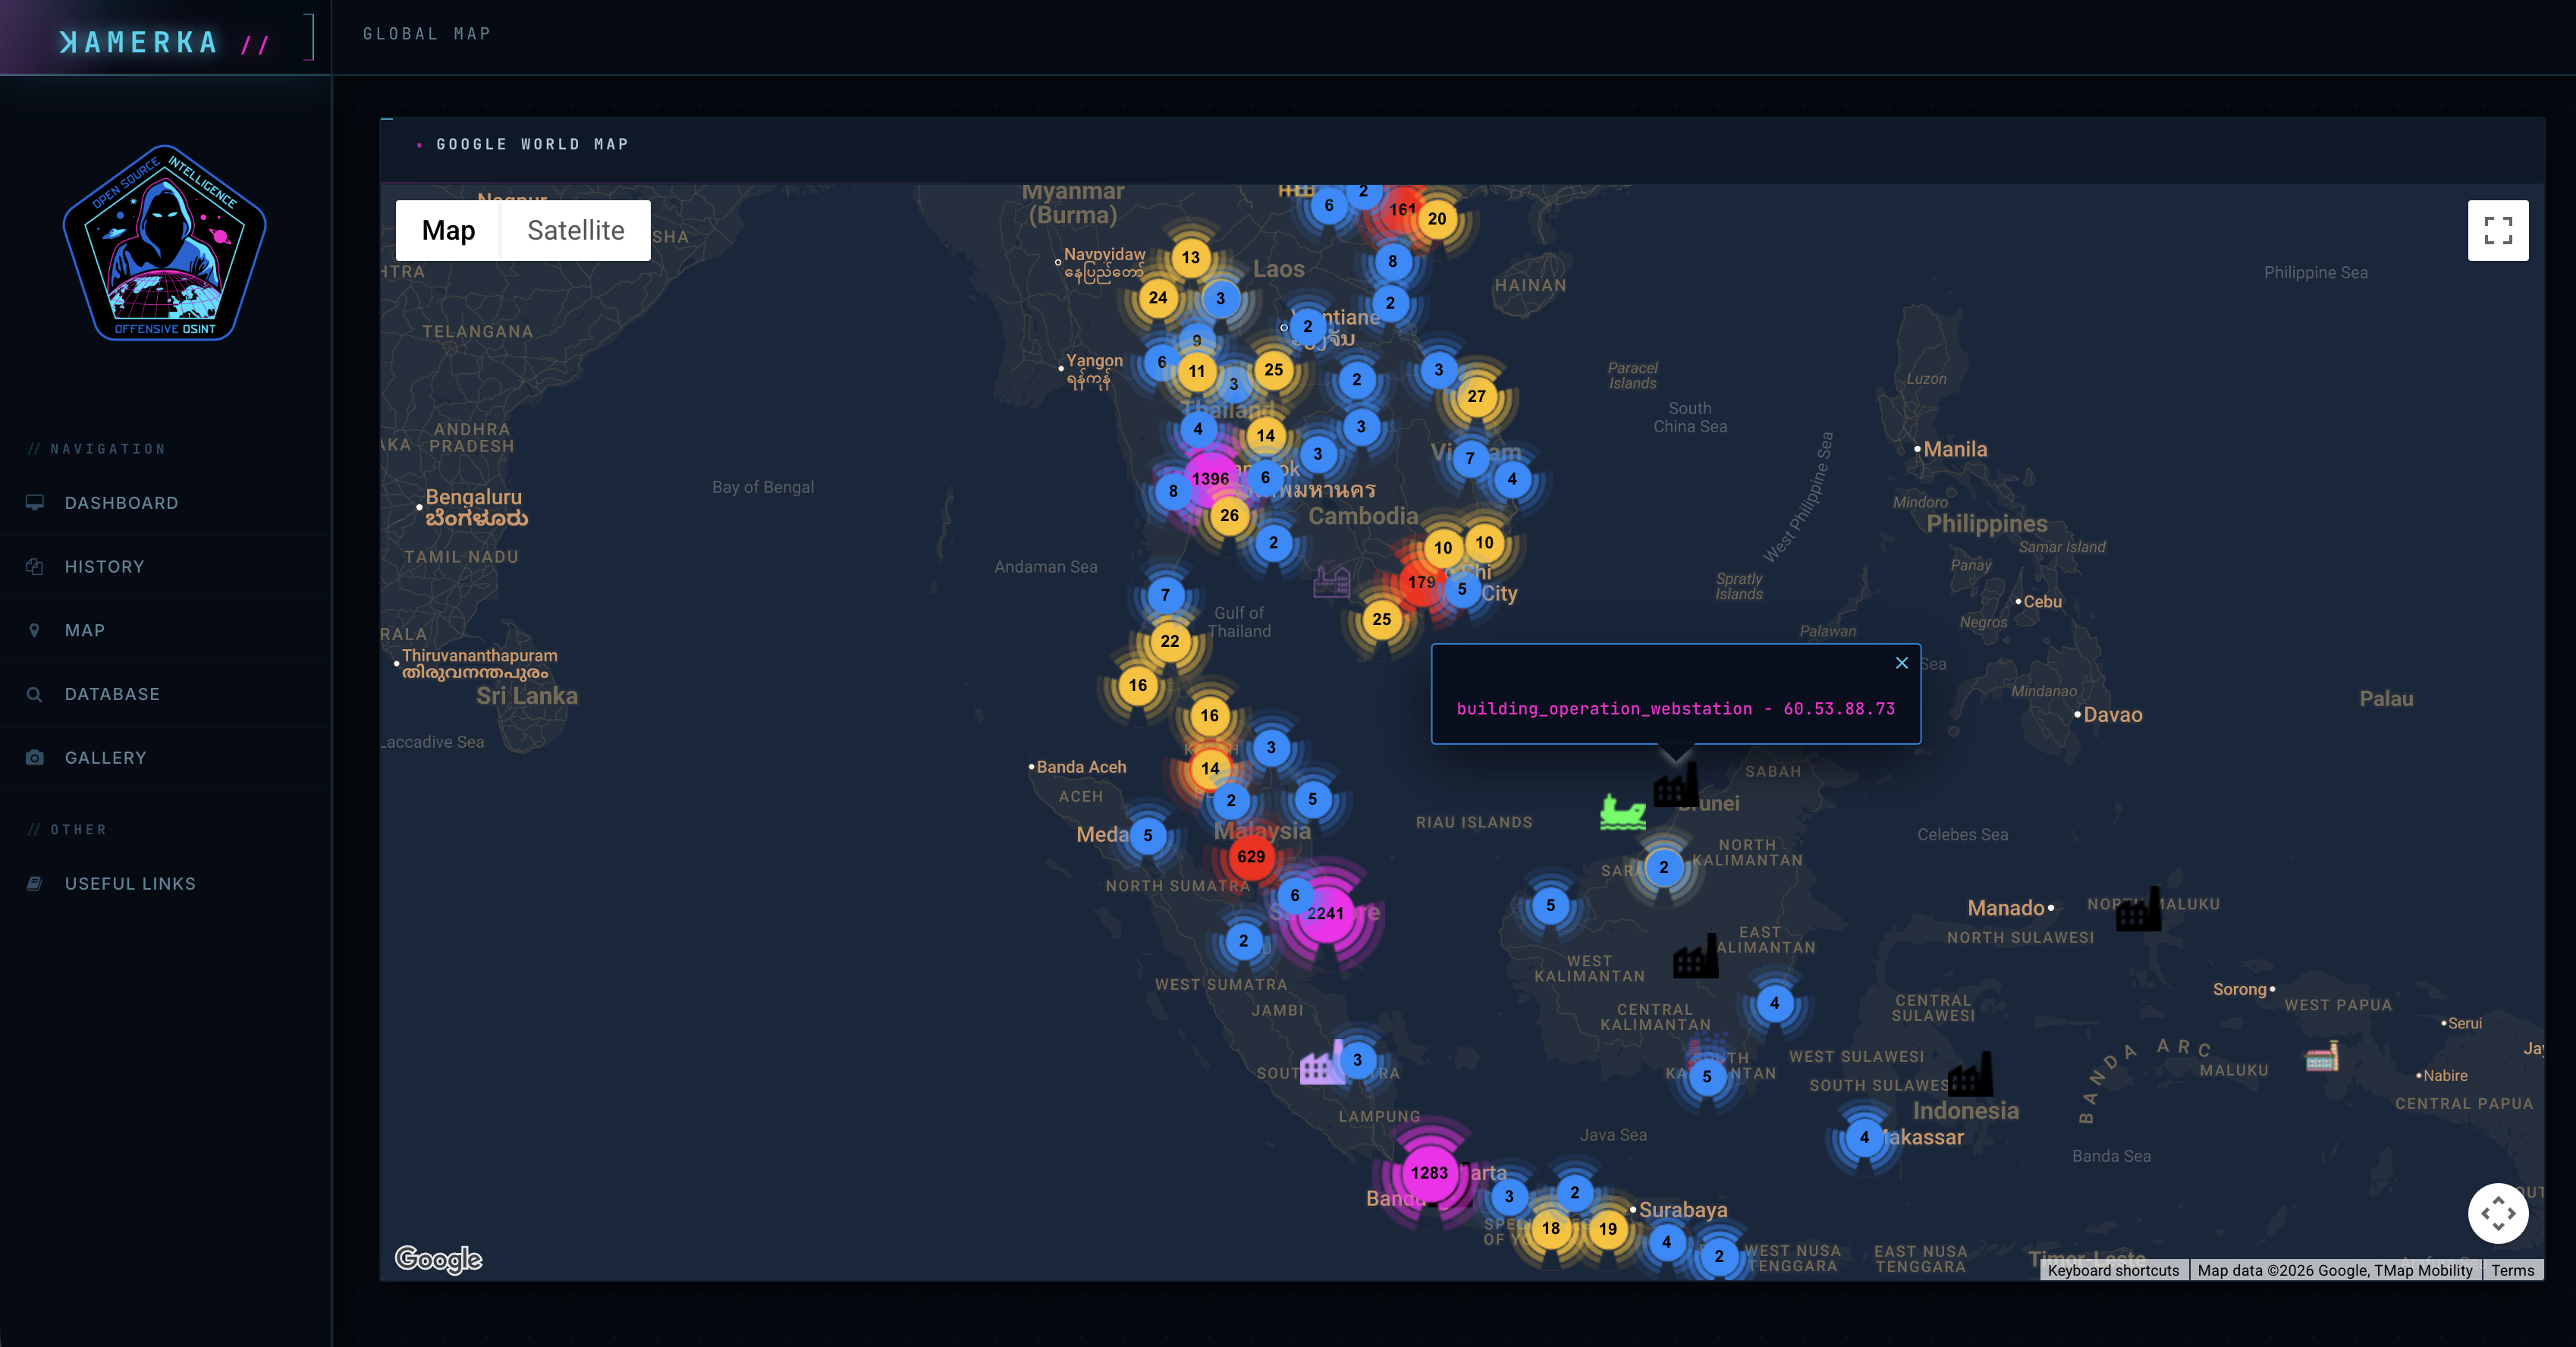 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
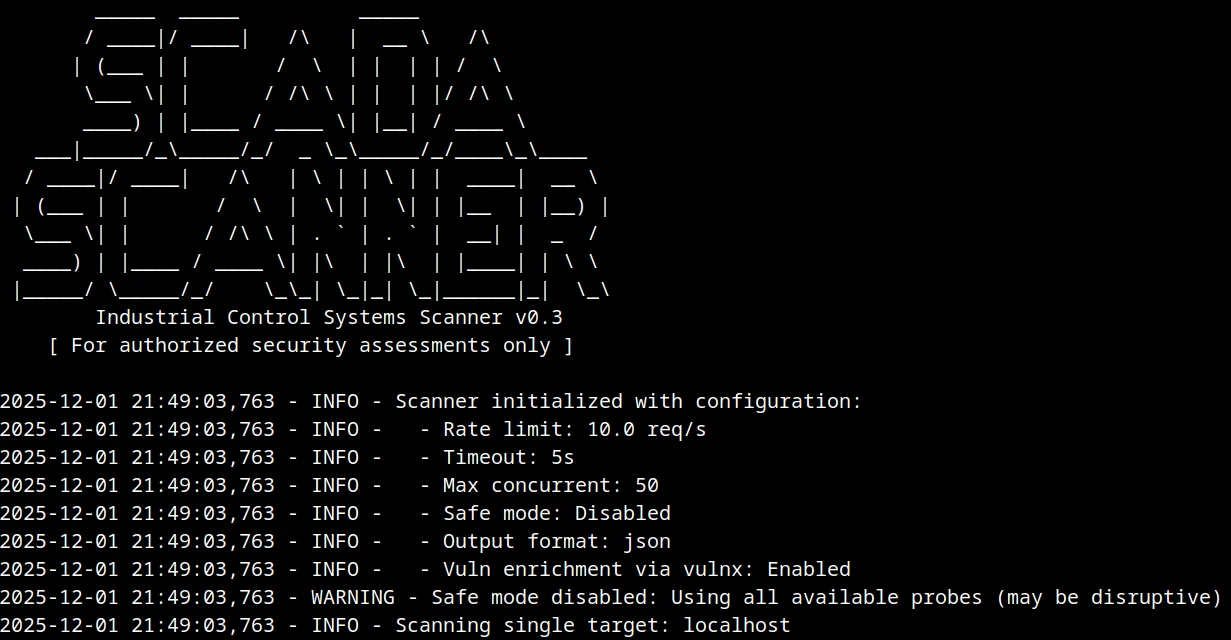 geeknik/scada-scanner
A high-performance, asynchronous SCADA/ICS scanner
 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA