

CVE-2023-31717
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
database-securityexploitationscada-ics-security+2
mateustesser/cve-2023-31717Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 yanissec/cve-2018-7848
CVE-2018-7848
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 yanissec/cve-2018-7846
CVE-2018-7846
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 yanissec/cve-2018-7854
CVE-2018-7854
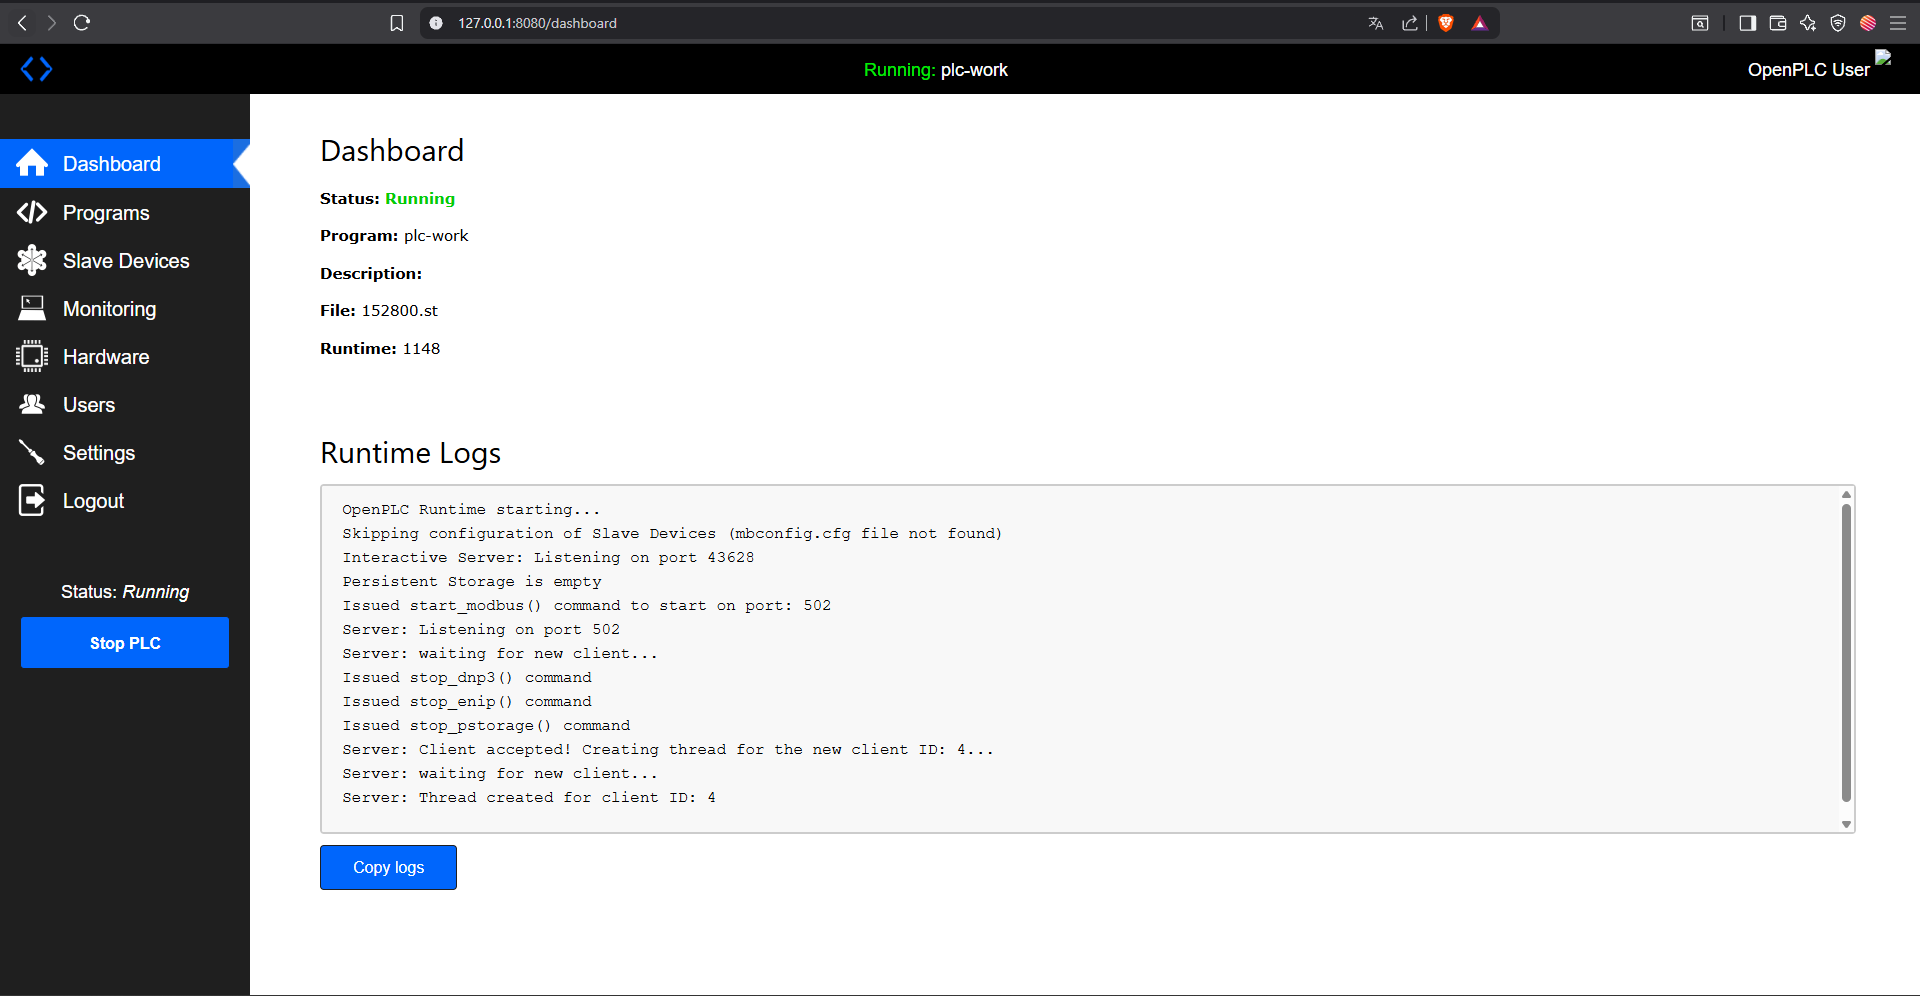 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 mateustesser/cve-2023-31716
Proof-of-concept exploit for CVE-2023-31716, a Local File Inclusion vulnerability in FUXA SCADA/HMI software versions <= 1.1.12, enabling arbitrary…
 spinfosecurity/bas-guardian
Free BACnet/BMS vulnerability scanner for building automation systems. Detects CVE-2026-3611 (CVSS 10.0), CVE-2026-24060, and exposed HVAC/BAS…
 spinfosecurity/rail-ot-protector
Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
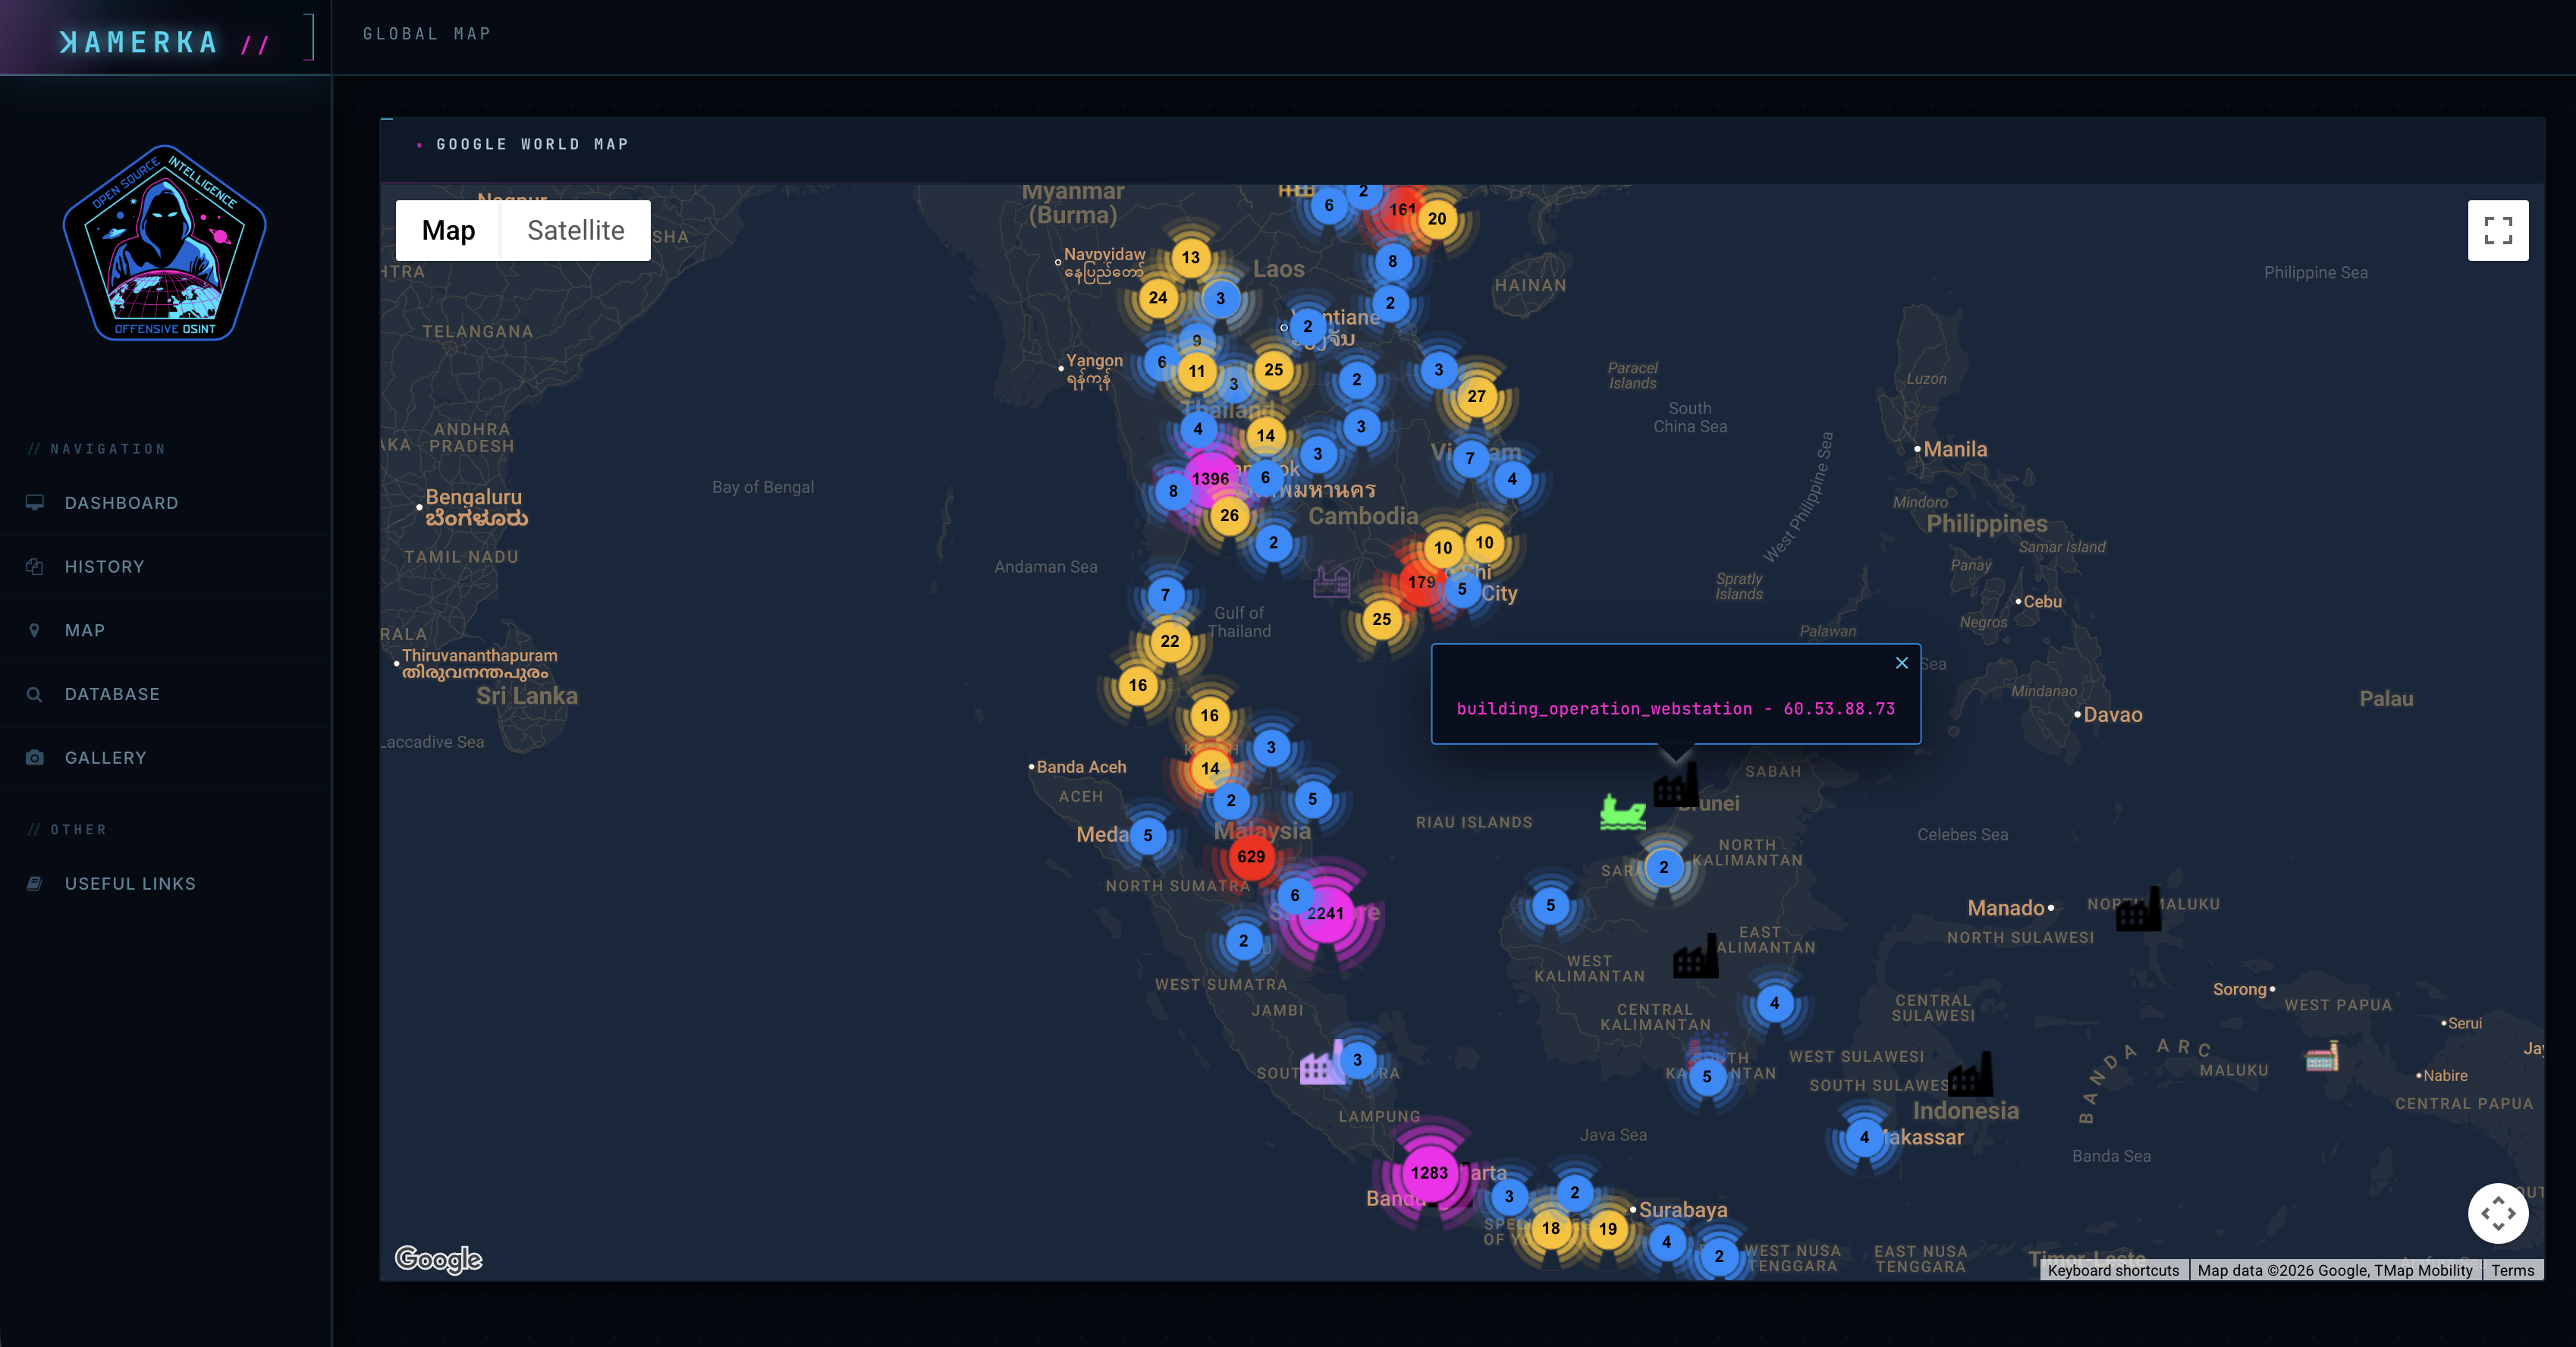 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition