Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
Pwn2Own-Auto-2024-CHARX preview

Pwn2Own-Auto-2024-CHARX

GitHubret2/pwn2own-auto-2024-charx

Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…

embedded-systems-securityexploitationiot-security+2
14
2 years ago
CVE-2022-29593 preview

CVE-2022-29593

GitHub9lyph/cve-2022-29593

Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…

authenticationexploitationfuzzing+8
81 year ago
CVE-2023-0861-POC preview

CVE-2023-0861-POC

GitHubseifallahhomrani1/cve-2023-0861-poc

Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers

educationembedded-systems-securityexploitation+5
73 years ago
scadapack-secure-lock-poc preview

scadapack-secure-lock-poc

GitHubabhinavagarwal07/scadapack-secure-lock-poc

Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock

cryptographydefensive-toolsexploitation+3
18 days ago
CVE-2026-9090-Modbus-TCP-Write-to-Read-Only-Coils-via-Function-Code-Spoofing preview

CVE-2026-9090-Modbus-TCP-Write-to-Read-Only-Coils-via-Function-Code-Spoofing

GitHubgeorge0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing

PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.

exploitationhardware-iot-securitymisconfiguration+4
1 month ago
CVE-2026-25938-FUXA-Unauthenticated-RCE preview

CVE-2026-25938-FUXA-Unauthenticated-RCE

GitHubjudgedbykira/cve-2026-25938-fuxa-unauthenticated-rce

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

exploitationiot-securitypayload-development+6
11 month ago
Active-Scanning-and-Information-Gathering-in-ICS-SCADA-Networks-Using-Network-Mapper-NMAP preview

Active-Scanning-and-Information-Gathering-in-ICS-SCADA-Networks-Using-Network-Mapper-NMAP

GitHubmurataydemir/active-scanning-and-information-gathering-in-ics-scada-networks-using-network-mapper-nmap

Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)

educationinformation-gatheringnetwork-mapping+3
26 years ago
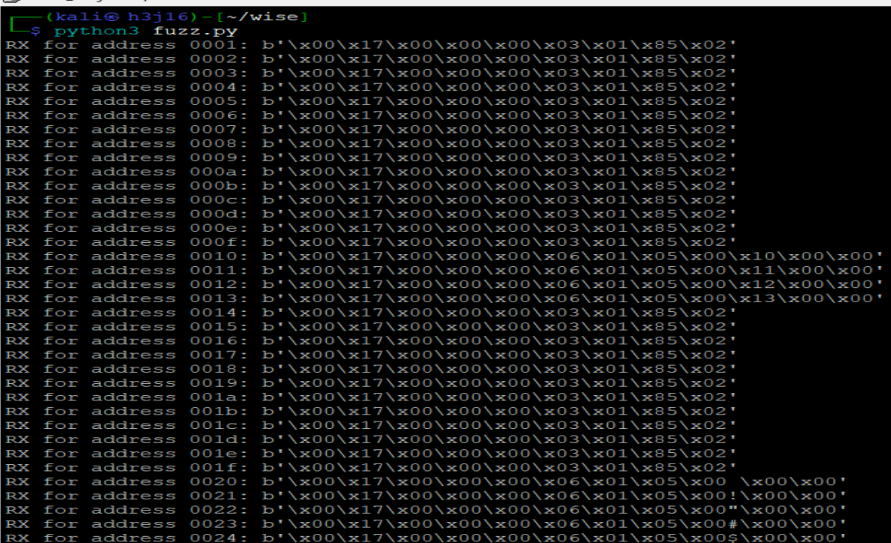
CVE-2025-48466 preview

CVE-2025-48466

GitHubshipcod3/cve-2025-48466

Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control

exploitationfuzzinghardware-iot-security+5
21 year ago
CVE-2026-32662 preview

CVE-2026-32662

GitHubxf-secops/cve-2026-32662

Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…

cloud-securityconfiguration-auditingiot-security+3
5 months ago
CVE-2025-34226 preview

CVE-2025-34226

GitHubeyodav/cve-2025-34226

OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.

database-securityexploitationmisconfiguration+3
0 years ago
yamcs__yamcs_CVE-2023-45277_5-8-6 preview

yamcs__yamcs_CVE-2023-45277_5-8-6

GitHubshoucheng3/yamcs__yamcs_cve-2023-45277_5-8-6

Java-based mission control framework with YAML configuration, supporting telemetry, commanding, and simulation for spacecraft operations. Includes…

configuration-auditingexploitationnetwork-security+3
1 year ago
Rail-OT-Protector preview
Archived

Rail-OT-Protector

GitHubspinfosecurity/rail-ot-protector

Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…

defensive-toolsinformation-gatheringnetwork-security+6
11 month ago
trommel preview
Archived

trommel

GitHubcertcc/trommel

TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators

embedded-systems-securityfirmware-analysishardware-security+6
2136 years ago
Industrial Security Auditing Framework preview

Industrial Security Auditing Framework

GitLabd0ubl3g/industrial-security-auditing-framework

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

exploit-frameworksnetwork-securitypenetration-testing+2
75 years ago
Redpoint preview

Redpoint

GitHubdigitalbond/redpoint

Nmap NSE scripts for ICS/SCADA discovery and enumeration—BACnet, EtherNet/IP, CoDeSys, Fox, Modicon, Omron, S7—using protocol queries for security…

information-gatheringnetwork-securitypenetration-testing+2
47210 years ago
ICSSecurityScripts preview

ICSSecurityScripts

GitHubtijldeneut/icssecurityscripts

Python scripts for security assessment of industrial PLCs: scanning, enumeration, control, and exploitation of Beckhoff, Siemens, Schneider,…

exploitationnetwork-mappingscada-ics-security+1
1527 months ago
sparkplugFuzzer preview

sparkplugFuzzer

GitHubbishopfox/sparkplugfuzzer

Fuzzer for the Sparkplug B IIoT protocol

authenticationdynamic-analysis-sandboxingfuzzing+5
22 months ago
Previous123Next