mySCADA-myPRO-7-Hardcoded-FTP-Username-and-Password

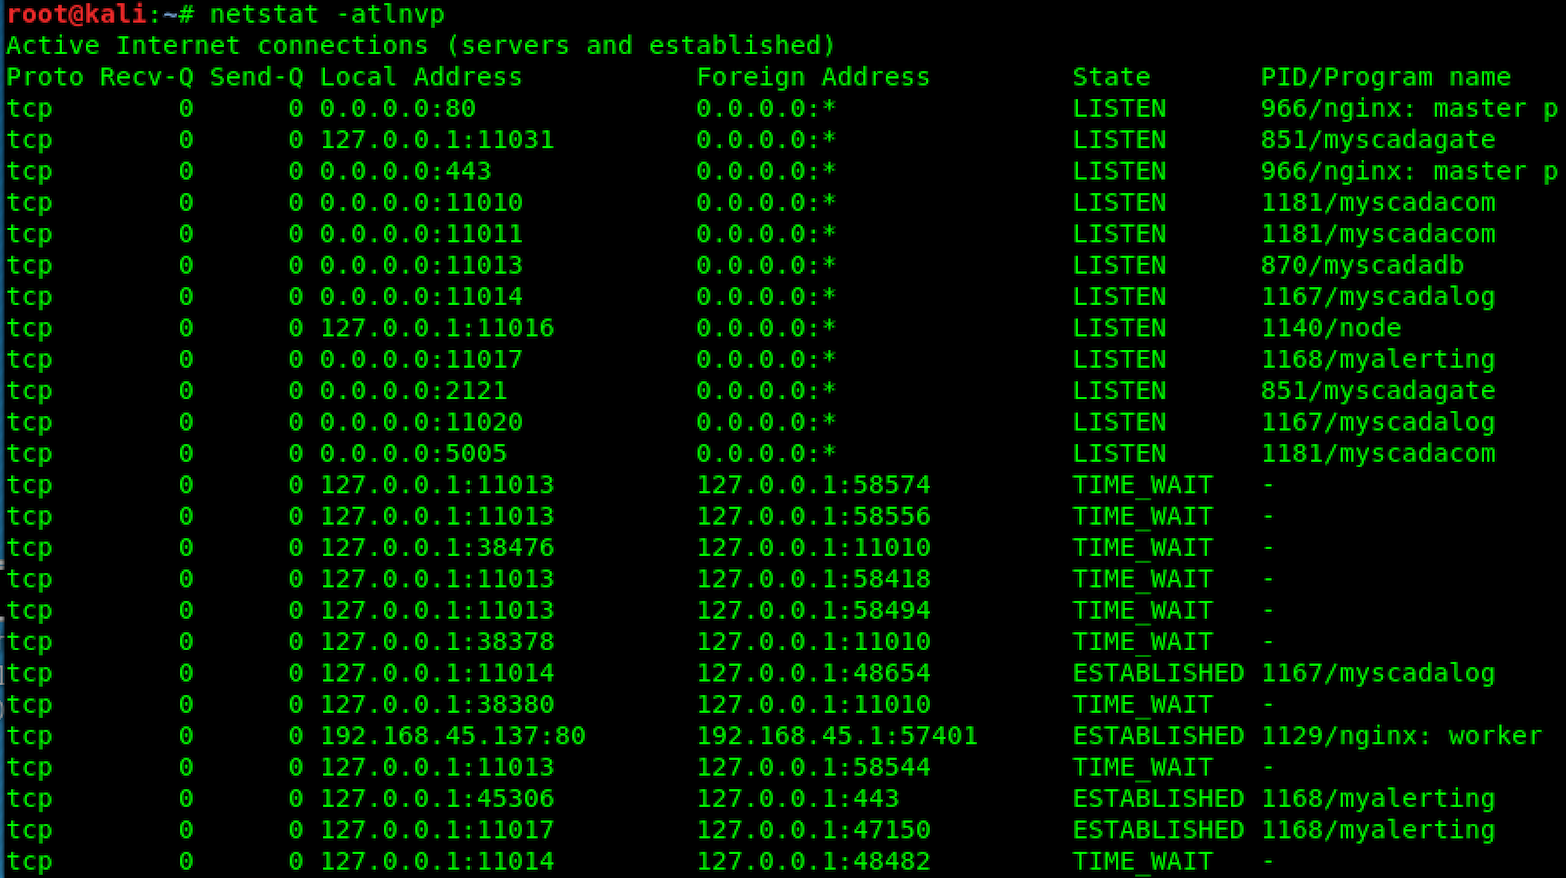
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656

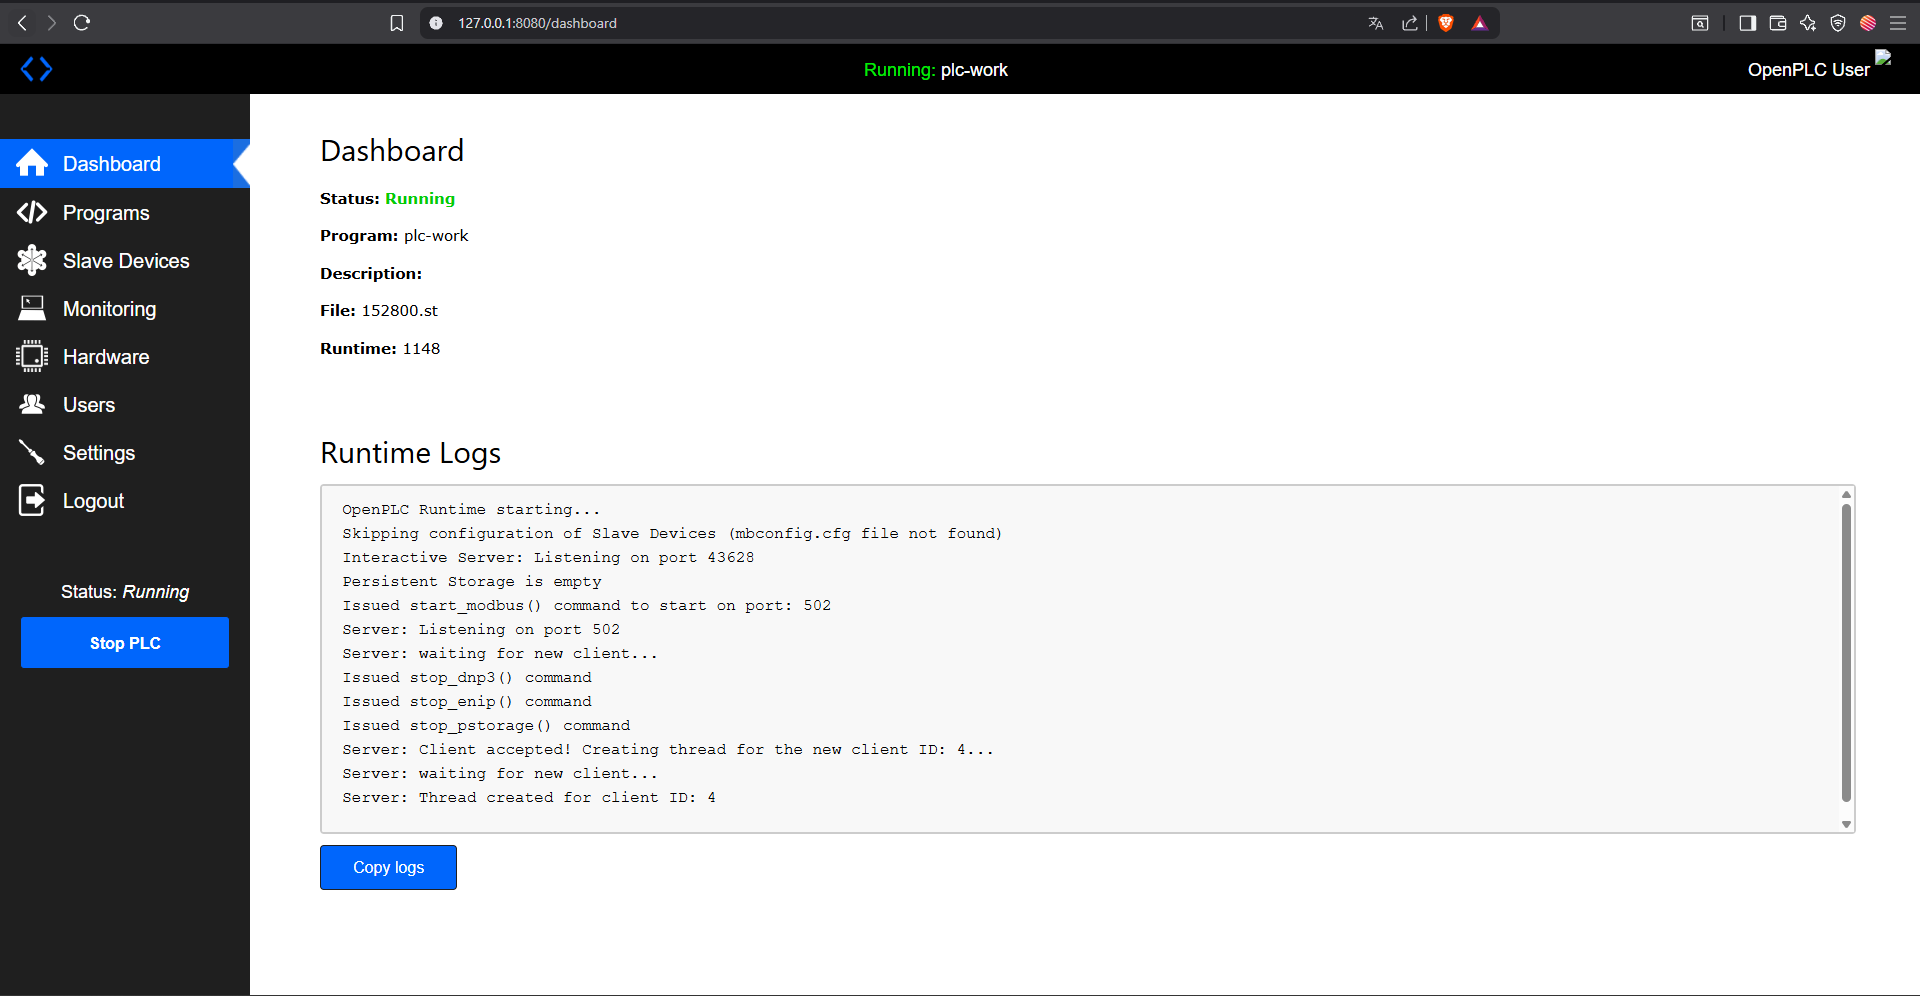
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.

Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers

Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…

Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…

PoC C&C for the Industroyer malware

CVE-2023-30459

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…

Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…

SpiderControl SCADA Web Server File Upload Vulnerability

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

Proof-of-concept exploit for CVE-2023-31716, a Local File Inclusion vulnerability in FUXA SCADA/HMI software versions <= 1.1.12, enabling arbitrary…

Purdue Model for Industrial Control System (ICS) Environments (Turkish)

Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)

Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…