Industrial Security Auditing Framework

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.

Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748

DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…

Research code implementing Dynamical Low-Rank Nash Equilibrium computation for stochastic ICS security games between advanced persistent threats and…

Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…

Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock

Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver

Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…

POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE

Fuzzer for the Sparkplug B IIoT protocol

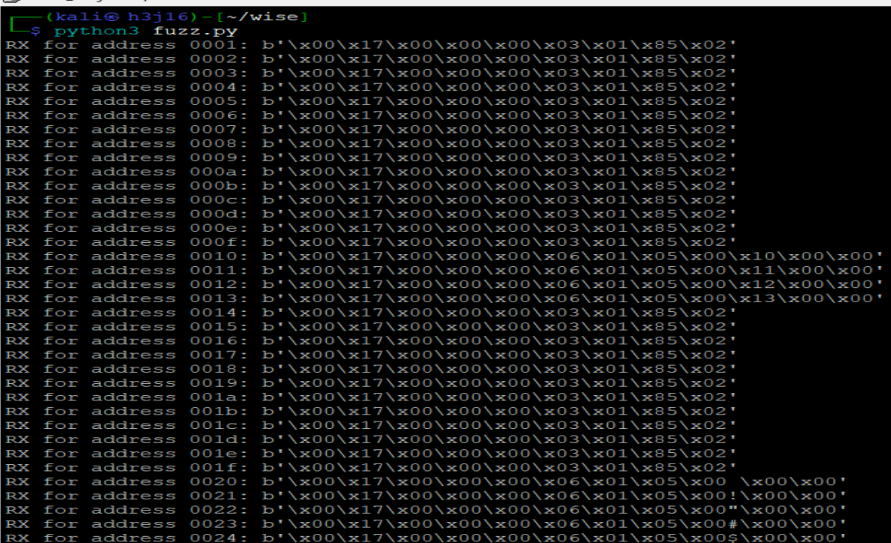
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…

Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability

Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…