
Terrminus-CVE-2026-2406
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
exploitationinformation-gatheringiot-security+8
2
ridpath/terrminus-cve-2026-2406AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 securifera/cve-2016-3962-exploit
CVE-2016-3962-Exploit
 aliasrobotics/aztarna
aztarna, a footprinting tool for robots.
 thingsboard/thingsboard
All-in-one IoT Platform - Device management, data collection, processing and visualization.
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 cisagov/cset
Cybersecurity Evaluation Tool
 thehappydinoa/awesome-censys-queries
A collection of fascinating and bizarre Censys Search Queries
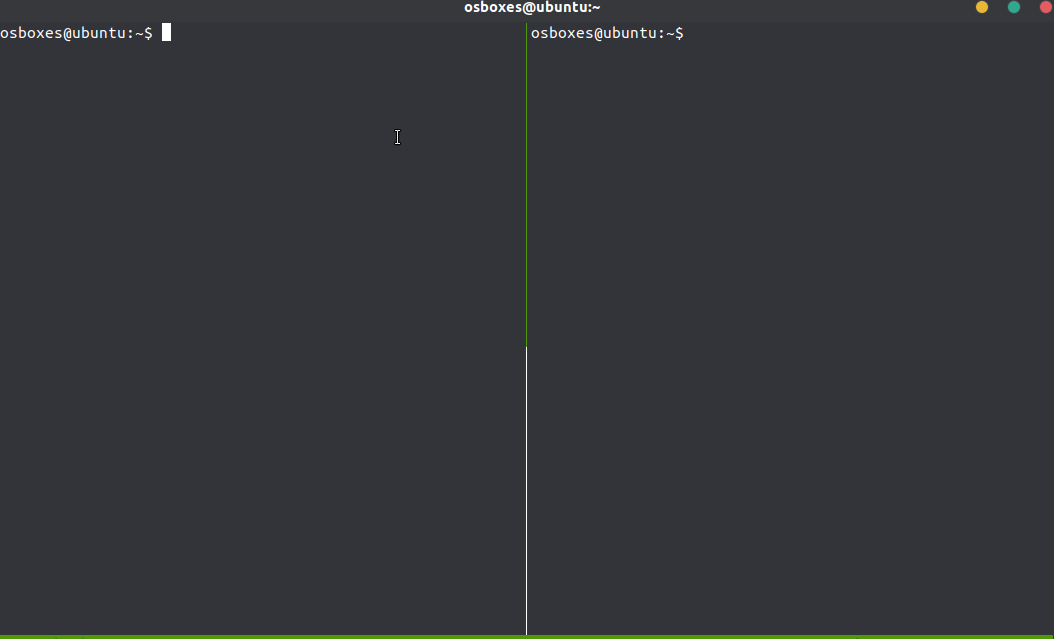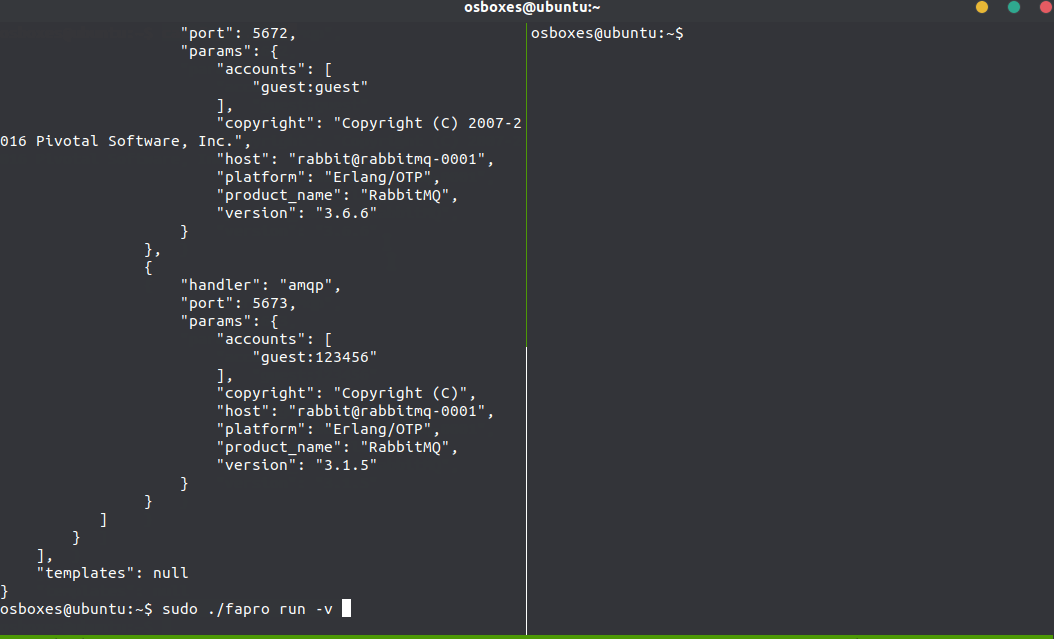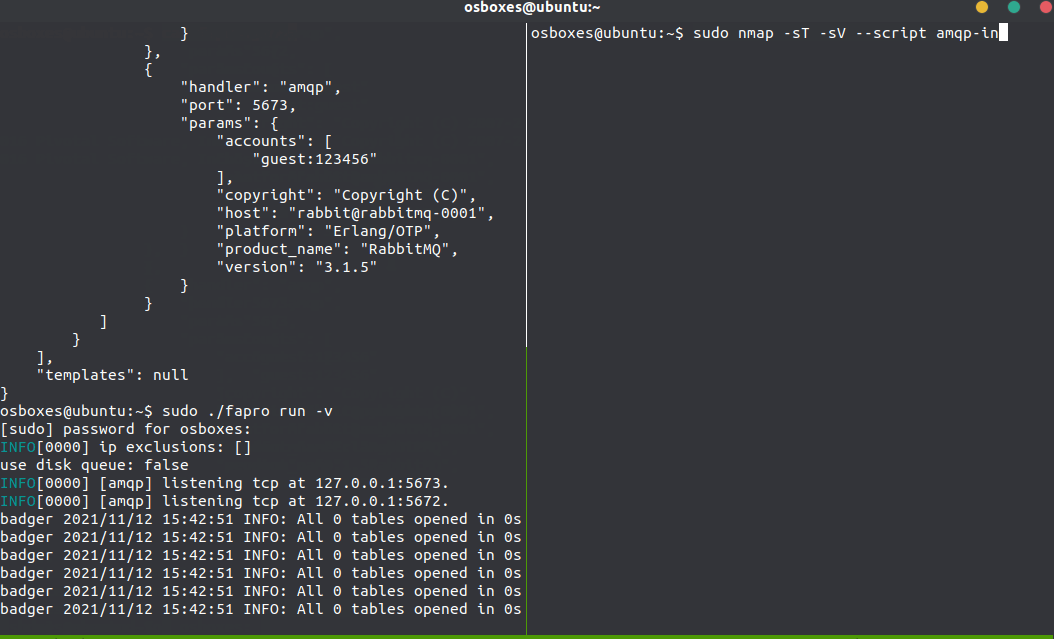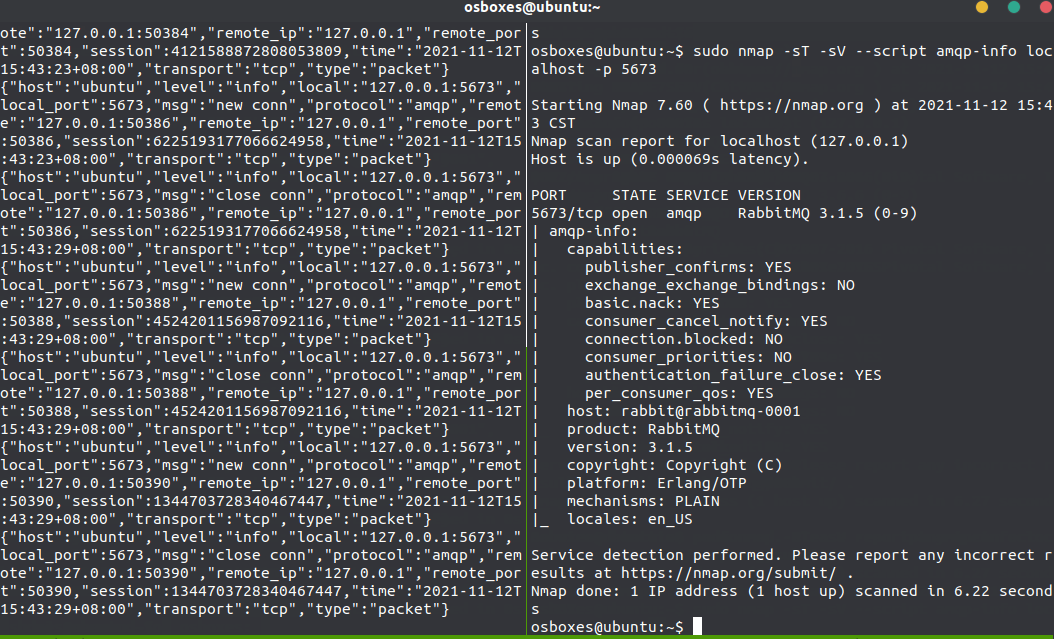 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

 bhdresh/dejavu
DejaVU - Open Source Deception Framework
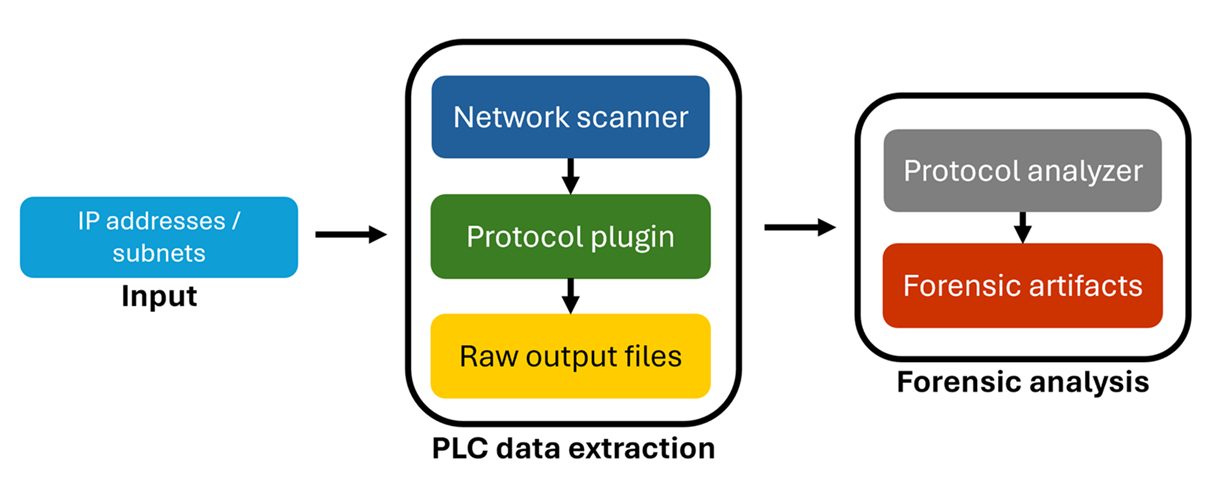 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
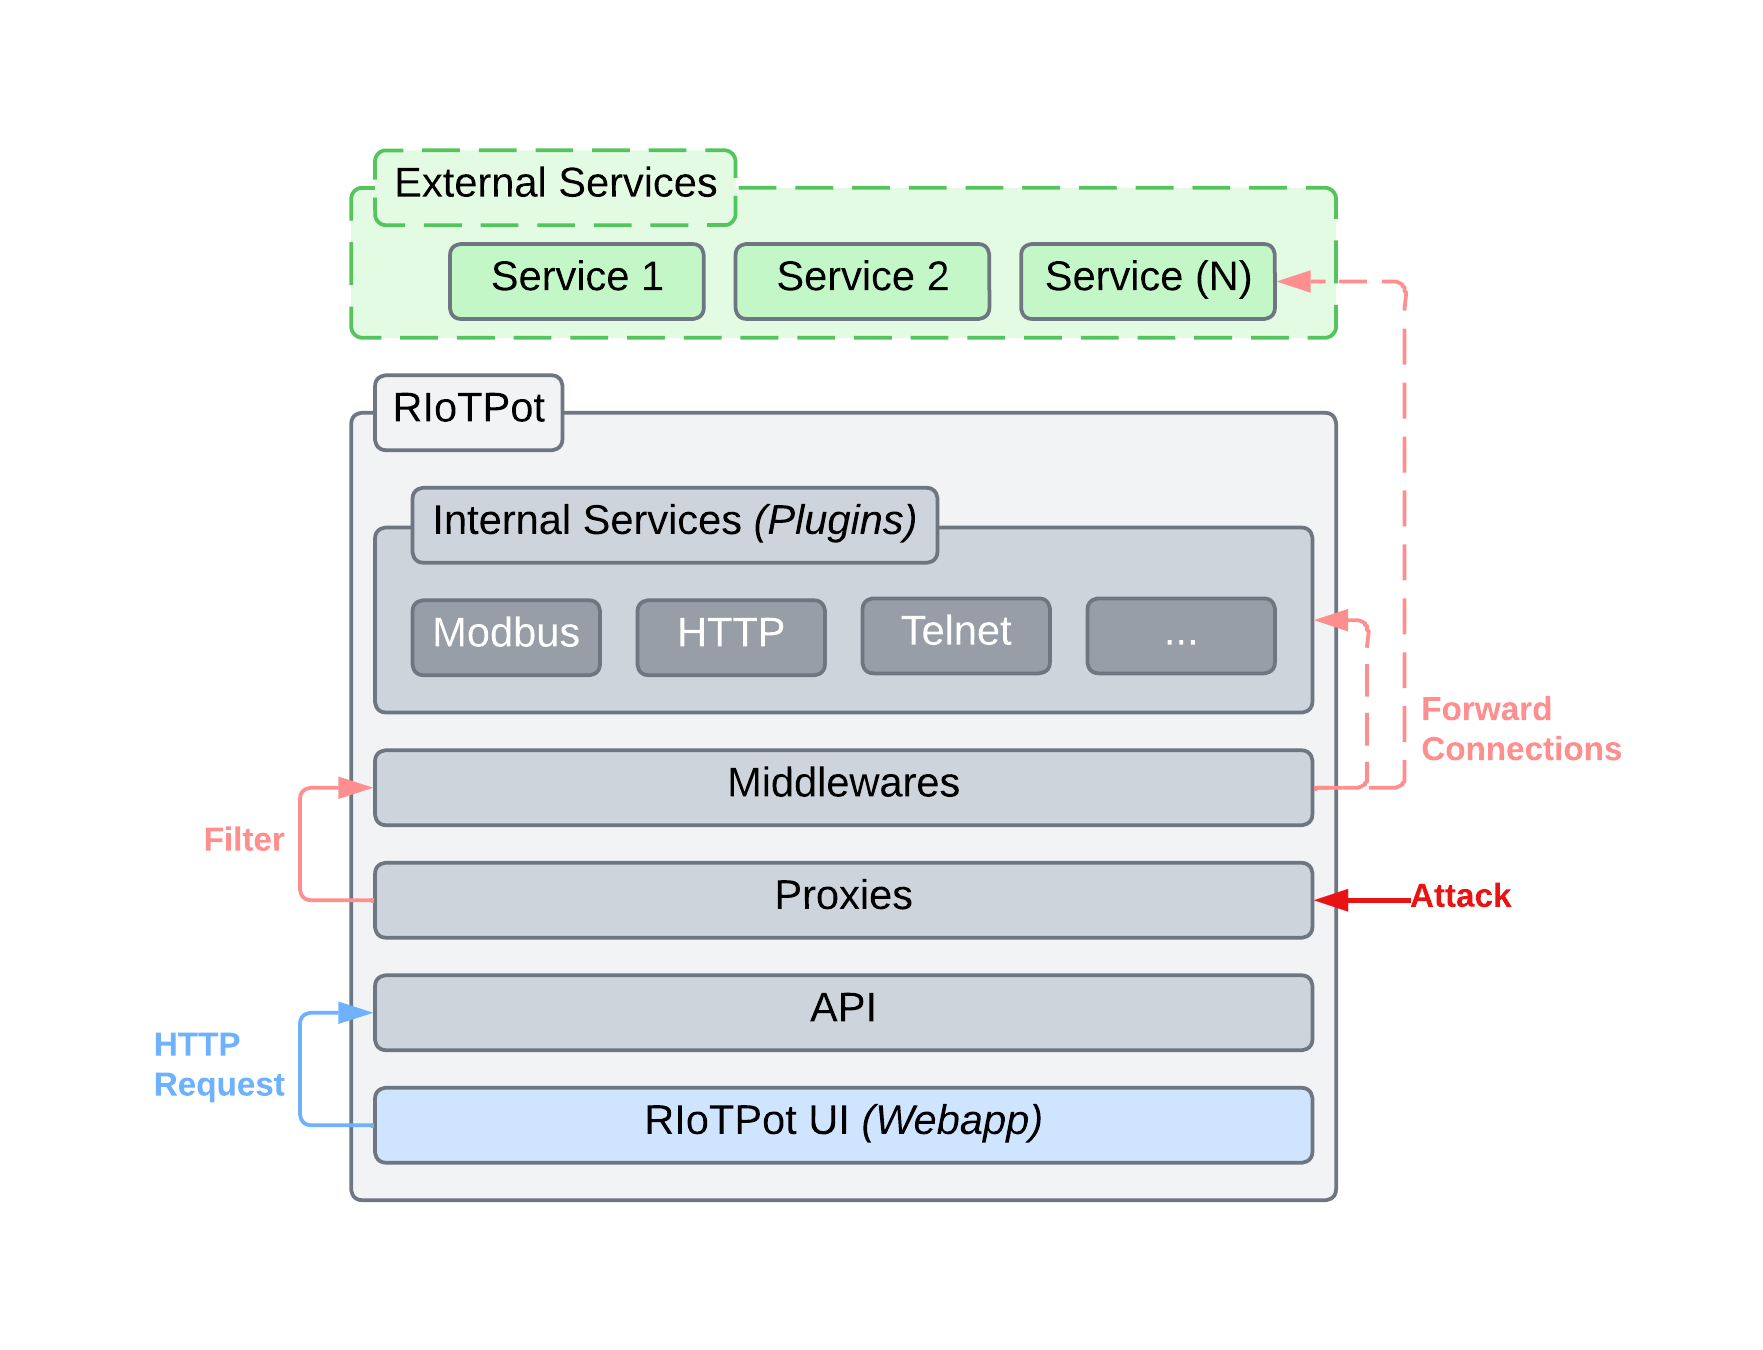 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
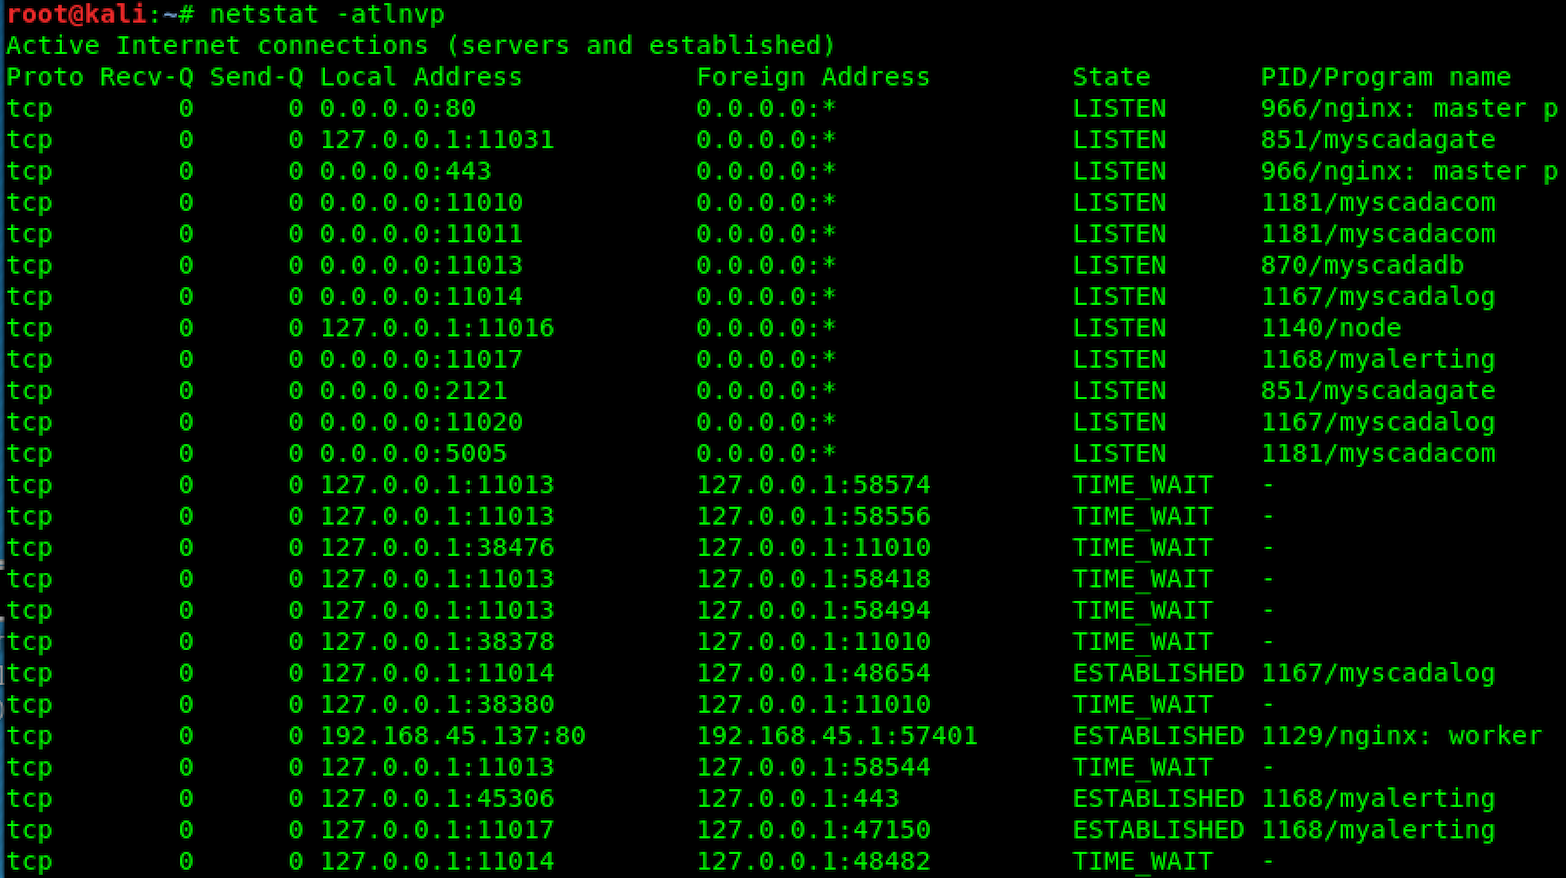 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability