
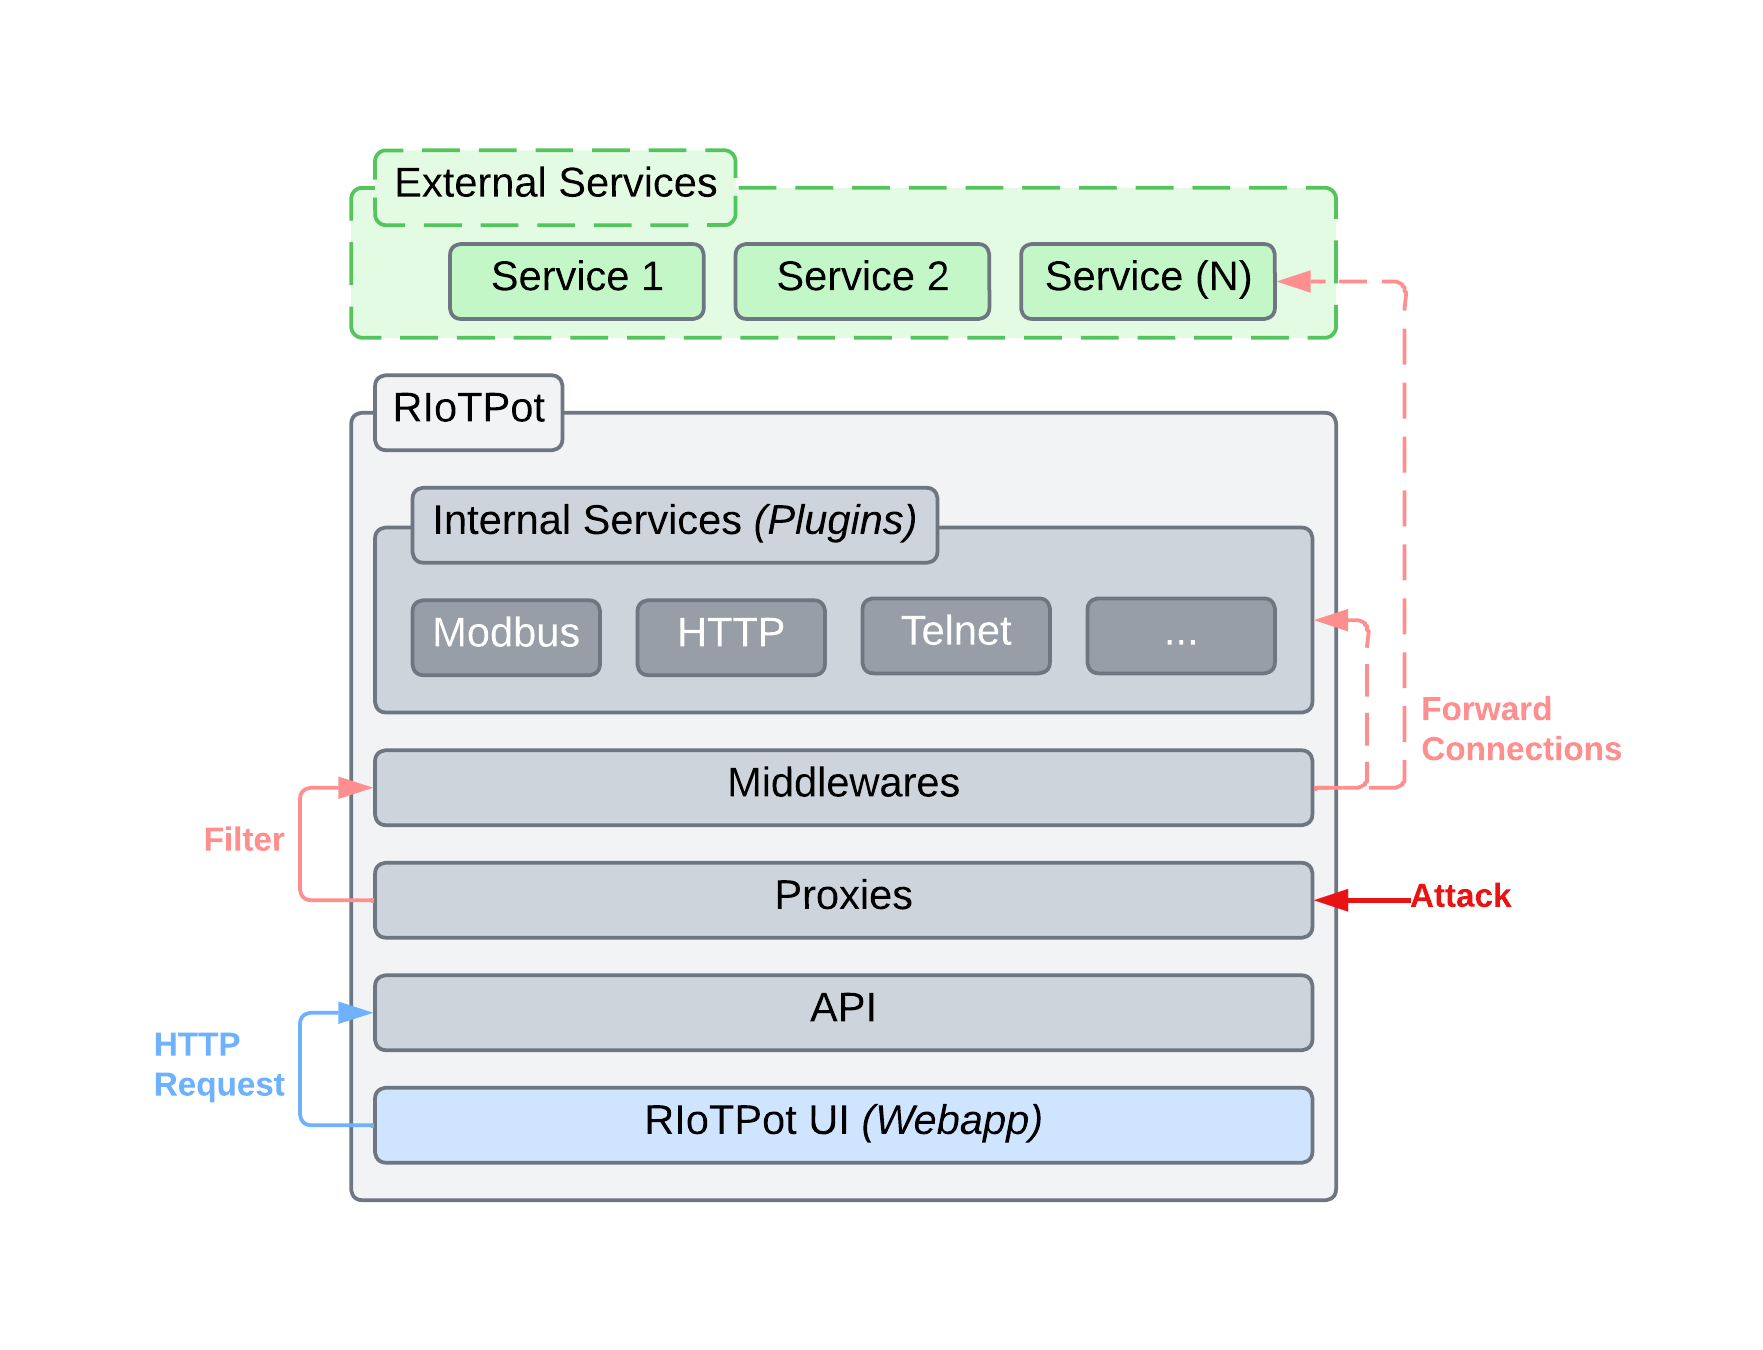
riotpot
 aau-network-security/riotpot
IoT and Operational Technology Honeypot
defensive-toolsinformation-gatheringiot-security+2
aau-network-security/riotpotIoT and Operational Technology Honeypot
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 ret2/pwn2own-auto-2024-charx
Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
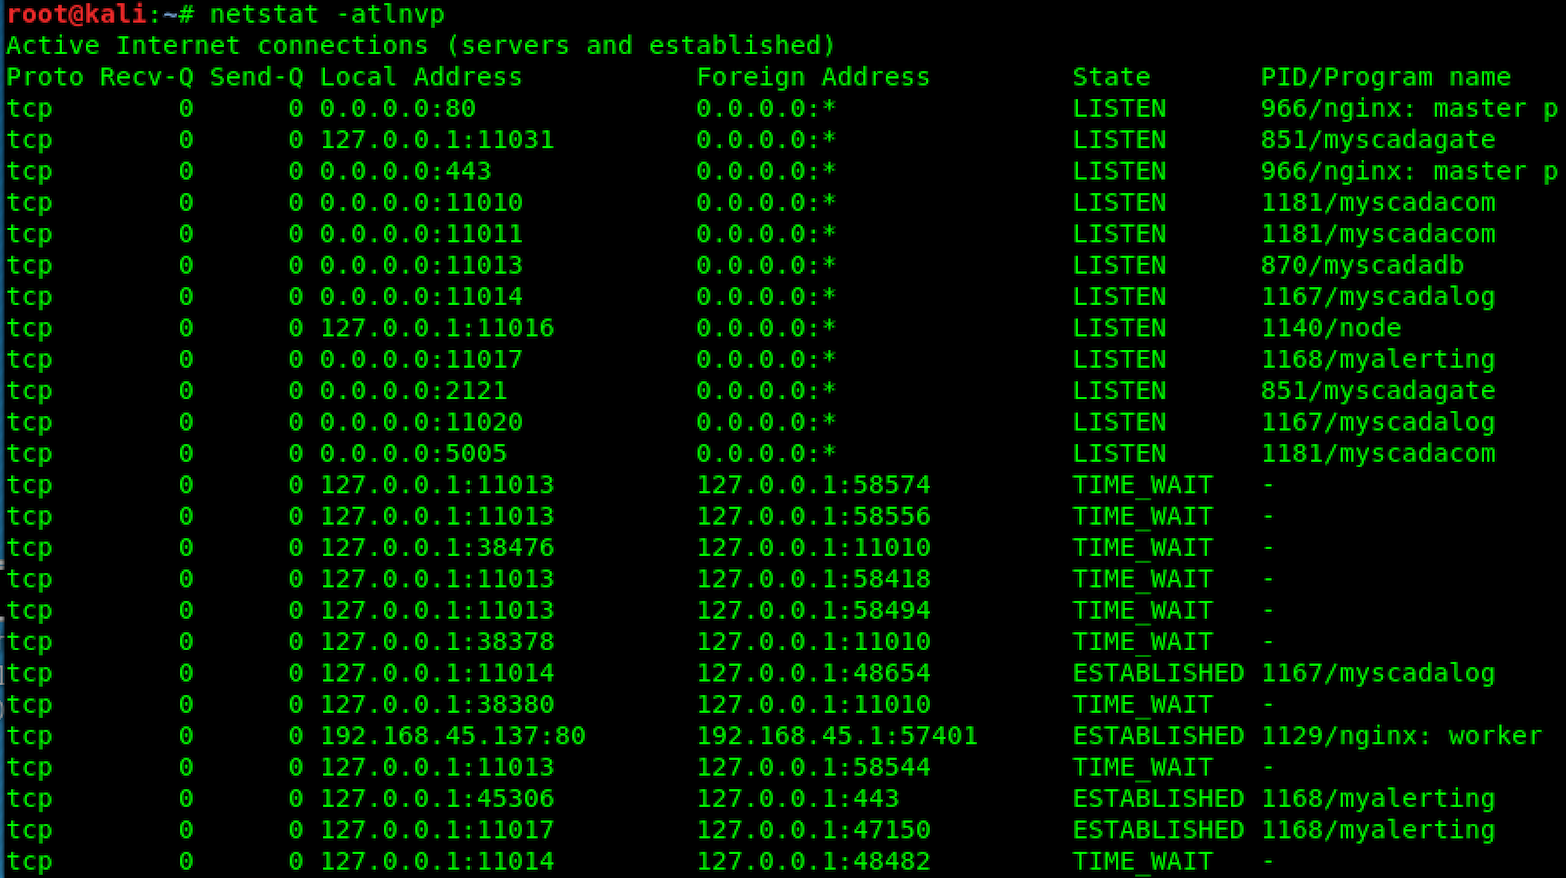 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 seifallahhomrani1/cve-2023-0861-poc
Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers
 gainsec/cve-2017-16744-and-cve-2017-16748-tridium-niagara
Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748
 can/cve-2015-5374-dos-poc
DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…
 tz98lab/dlr-ne-ics-security
Research code implementing Dynamical Low-Rank Nash Equilibrium computation for stochastic ICS security games between advanced persistent threats and…
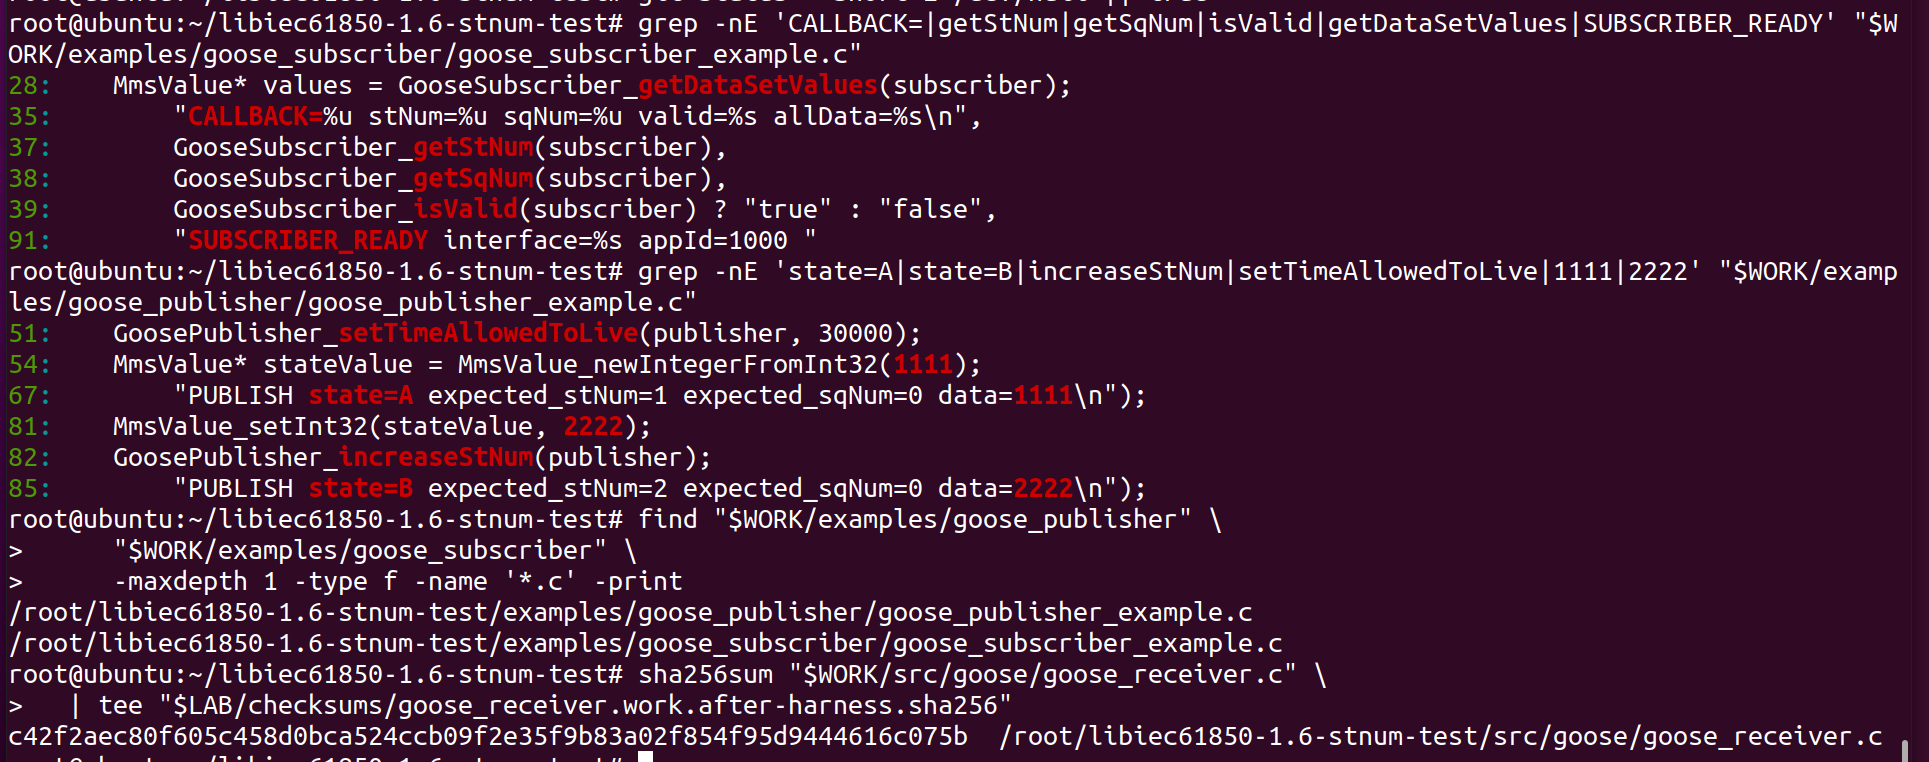 if-forget/cve-2026-52134-libiec61850
Public technical advisory and reproduction evidence for CVE-2026-52134 affecting GOOSE replay handling in libiec61850 v1.6.
 pcrosby-1990/cip-security-poc
Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…