Pwn2Own-Auto-2024-CHARX

Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…

Working exploit for Phoenix Contact CHARX SEC-3100 using Scapy raw Ethernet packets to trigger vulnerabilities and obtain an interactive connect-back…

Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.

Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…

Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748

Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…

Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver

Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…

Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

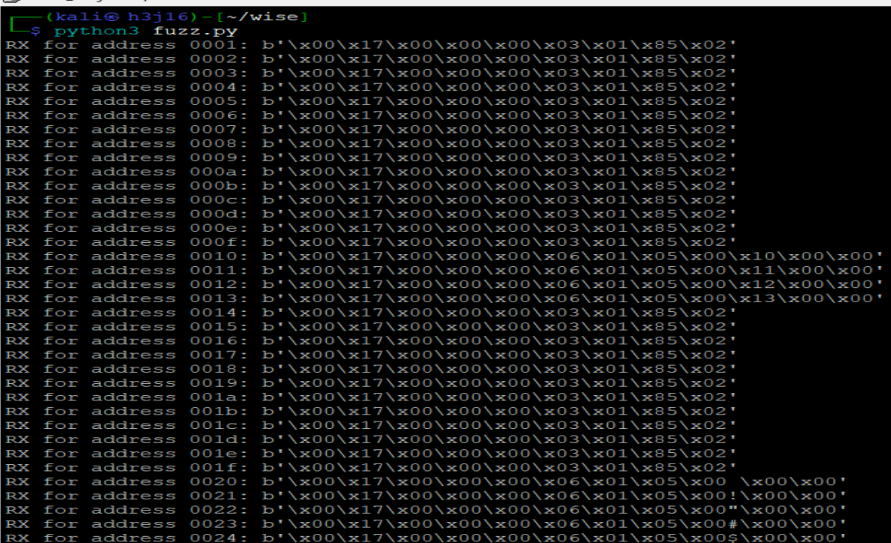
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control

PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…

Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability

Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…

Proof-of-concept exploit for CVE-2021-41579 enabling arbitrary file write/read and RCE via malicious .els project file in LAquis SCADA ≤4.3.1.1085.

PoC for CVE-2018-12086 affecting various OPC UA stacks