metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Free BACnet/BMS vulnerability scanner for building automation systems. Detects CVE-2026-3611 (CVSS 10.0), CVE-2026-24060, and exposed HVAC/BAS…

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.

Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…

Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…

Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

This repository contains a few vulnerabilities that were found and reported during vulnerability assessments.

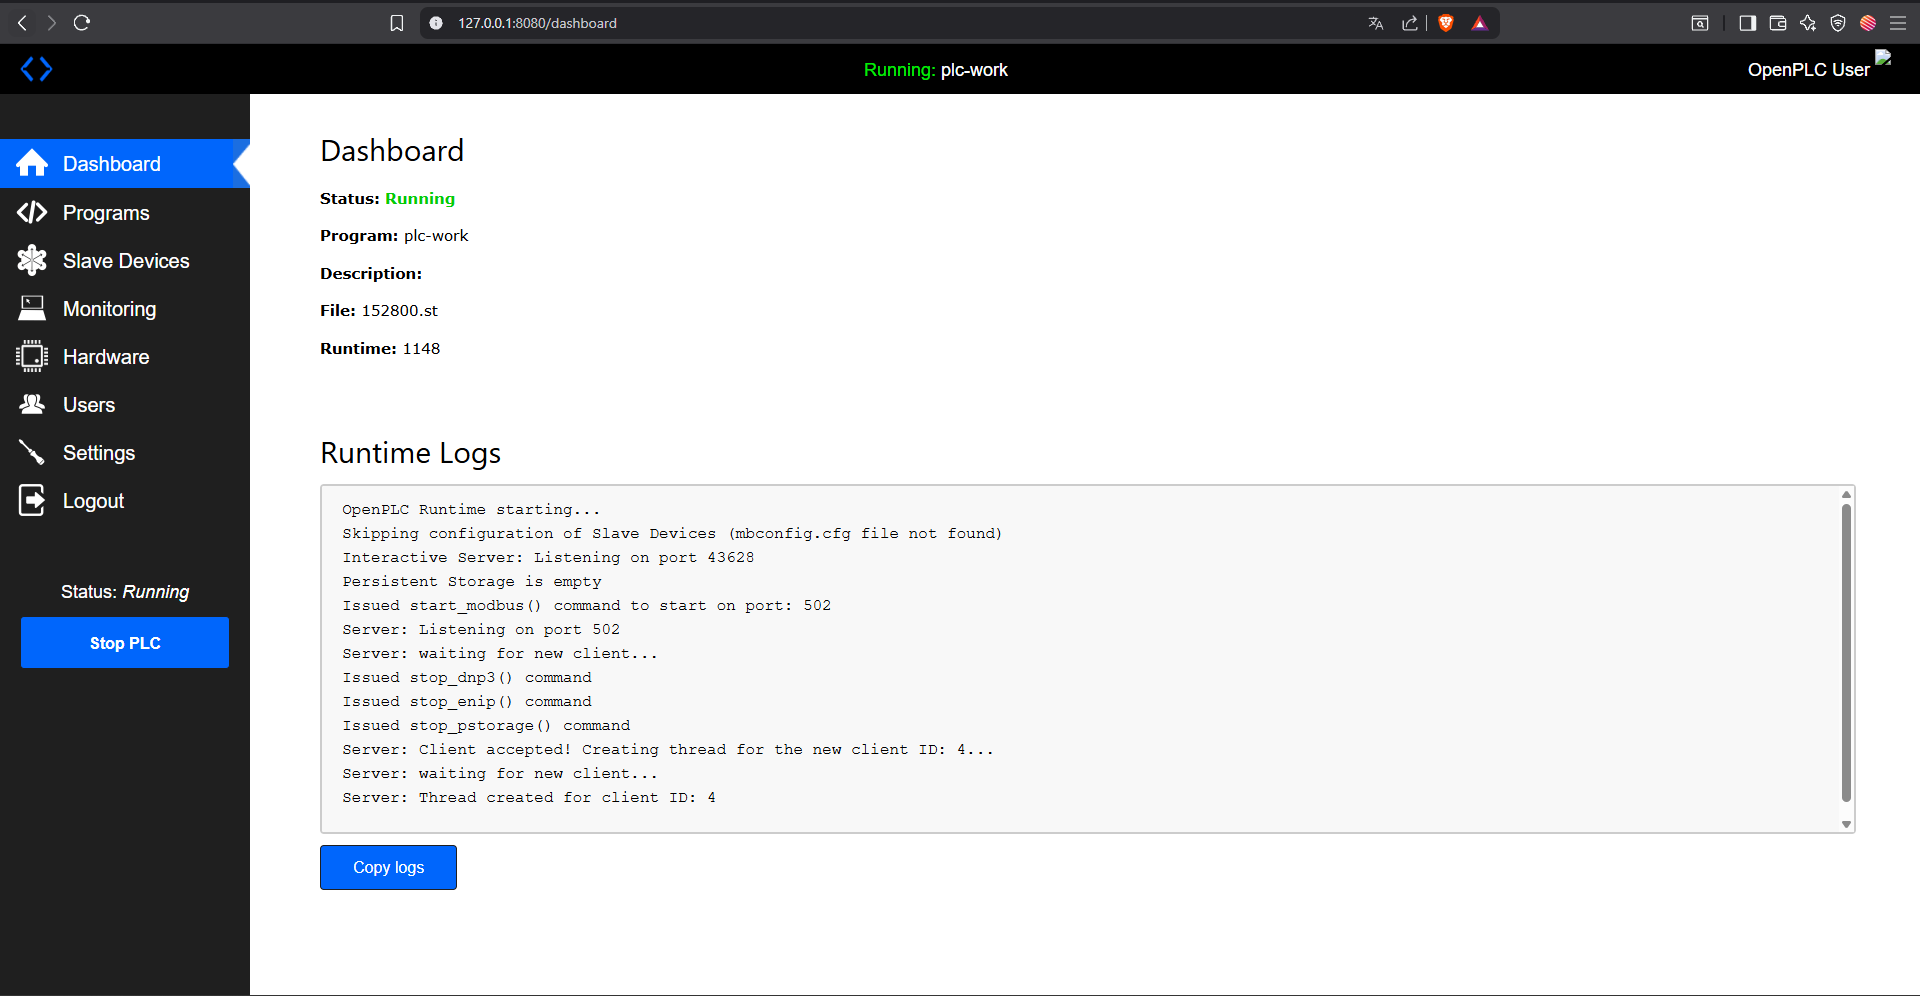
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.

Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…

CVE-2025-41646 - Critical Authentication bypass

SpiderControl SCADA Web Server File Upload Vulnerability

Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.

Collection of proof-of-concept exploits and vulnerability research artifacts published by Trend Micro's Zero Day Initiative, covering SCADA, RPC, and…

Security Vulnerability - Kardex Mlog MCC