

thingsboard
 thingsboard/thingsboard
Open-source IoT Platform - Device management, data collection, processing and visualization.
anomaly-detectioncloud-infrastructure-securityconfiguration-auditing+3
22.5k
thingsboard/thingsboardOpen-source IoT Platform - Device management, data collection, processing and visualization.

 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 abhinavagarwal07/scadapack-secure-lock-poc
Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 qflksheep/cve-2026-67687-ics-park-smart-park-management-system-v2.0
ICS-Park Smart Park Management System v2.0
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
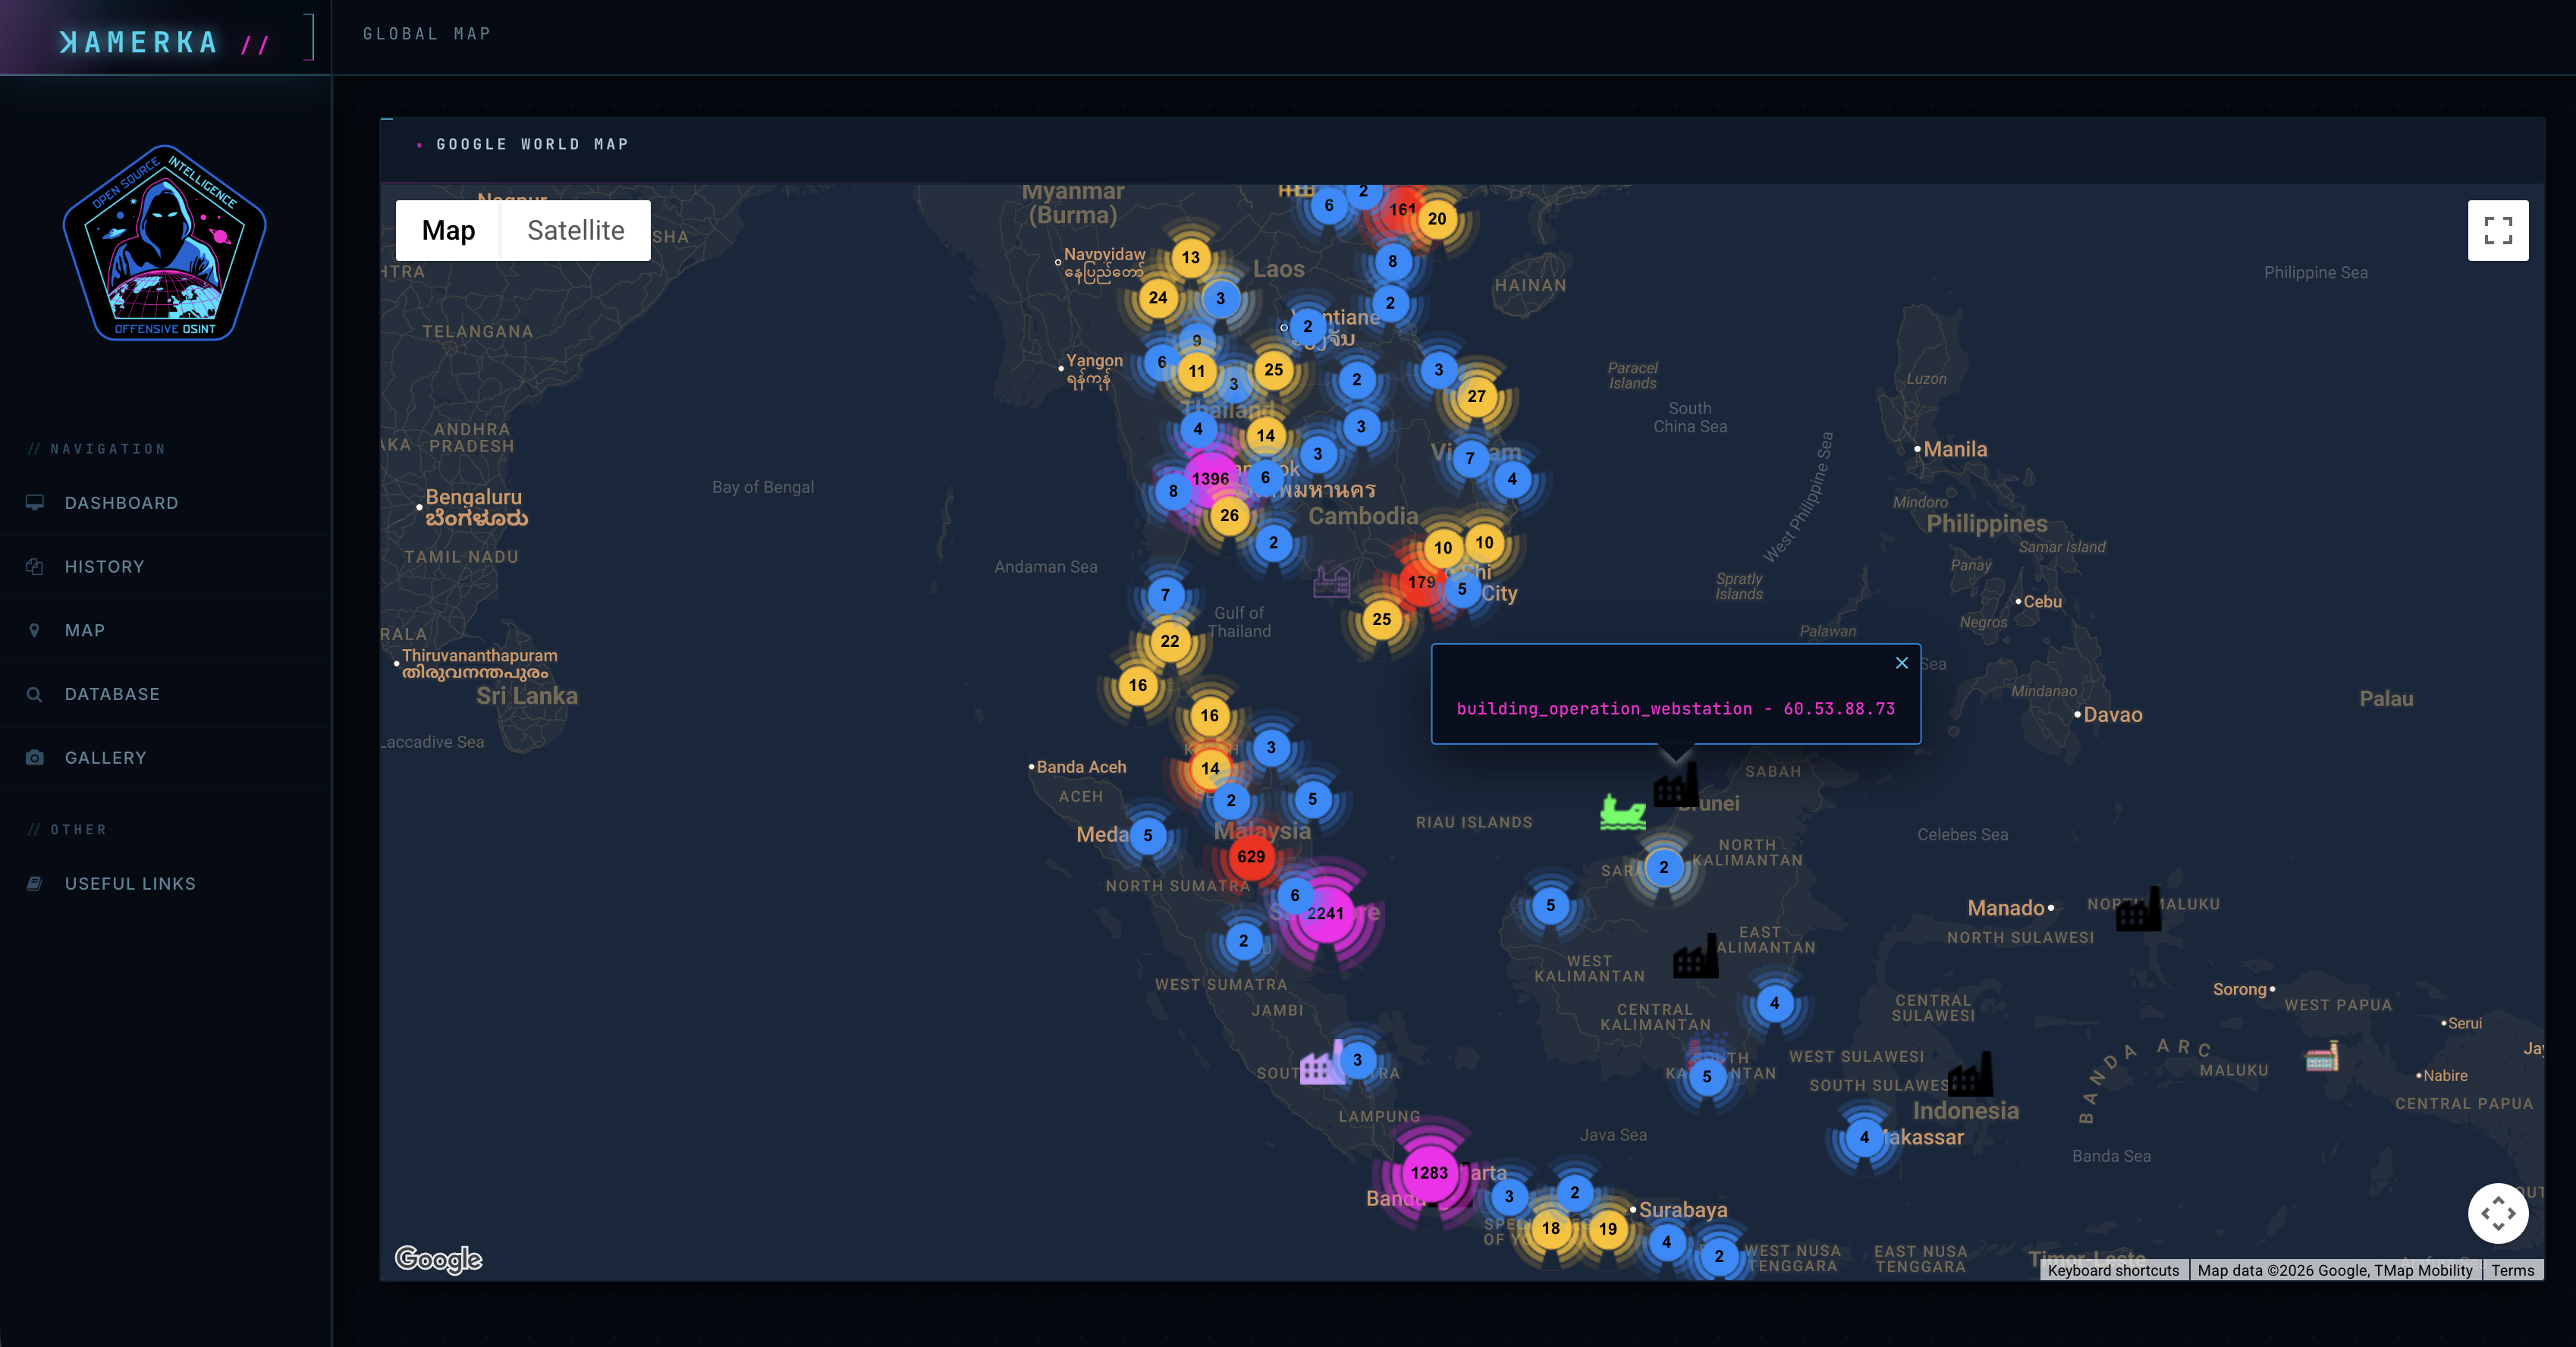 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…