


 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
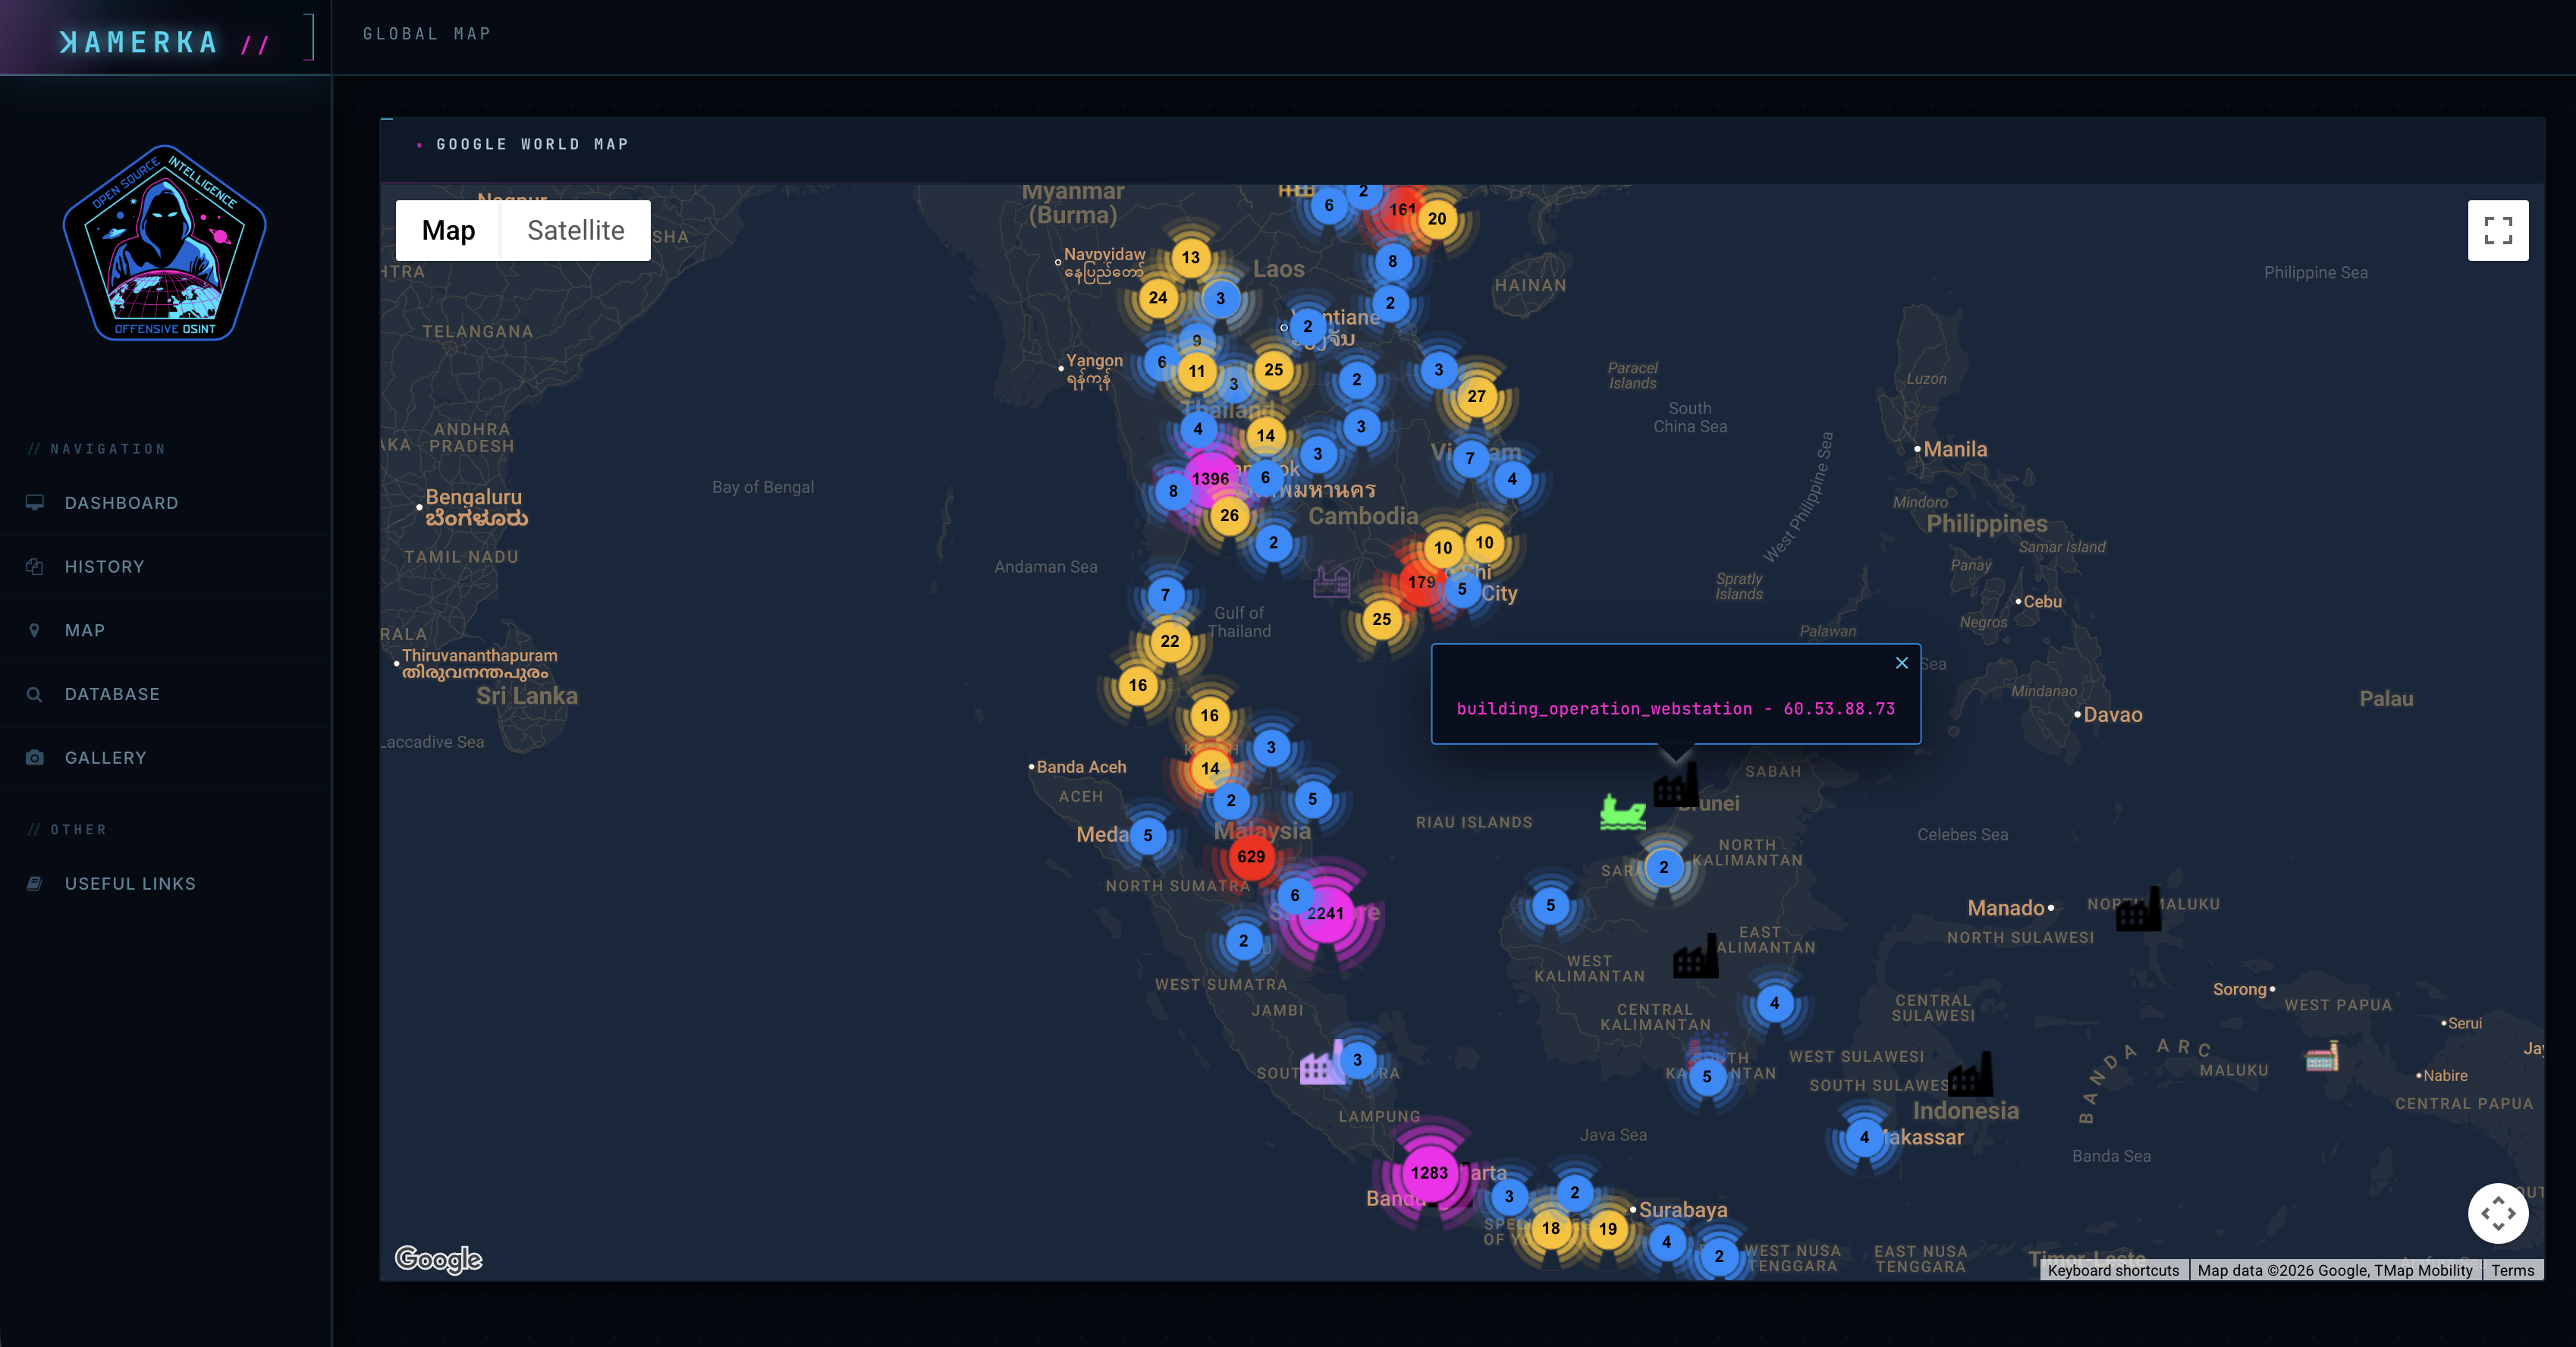 woj-ciech/kamerka-gui
Ultimate Internet of Things/Industrial Control Systems reconnaissance tool.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 tijldeneut/icssecurityscripts
Python scripts for security assessment of industrial PLCs: scanning, enumeration, control, and exploitation of Beckhoff, Siemens, Schneider,…
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
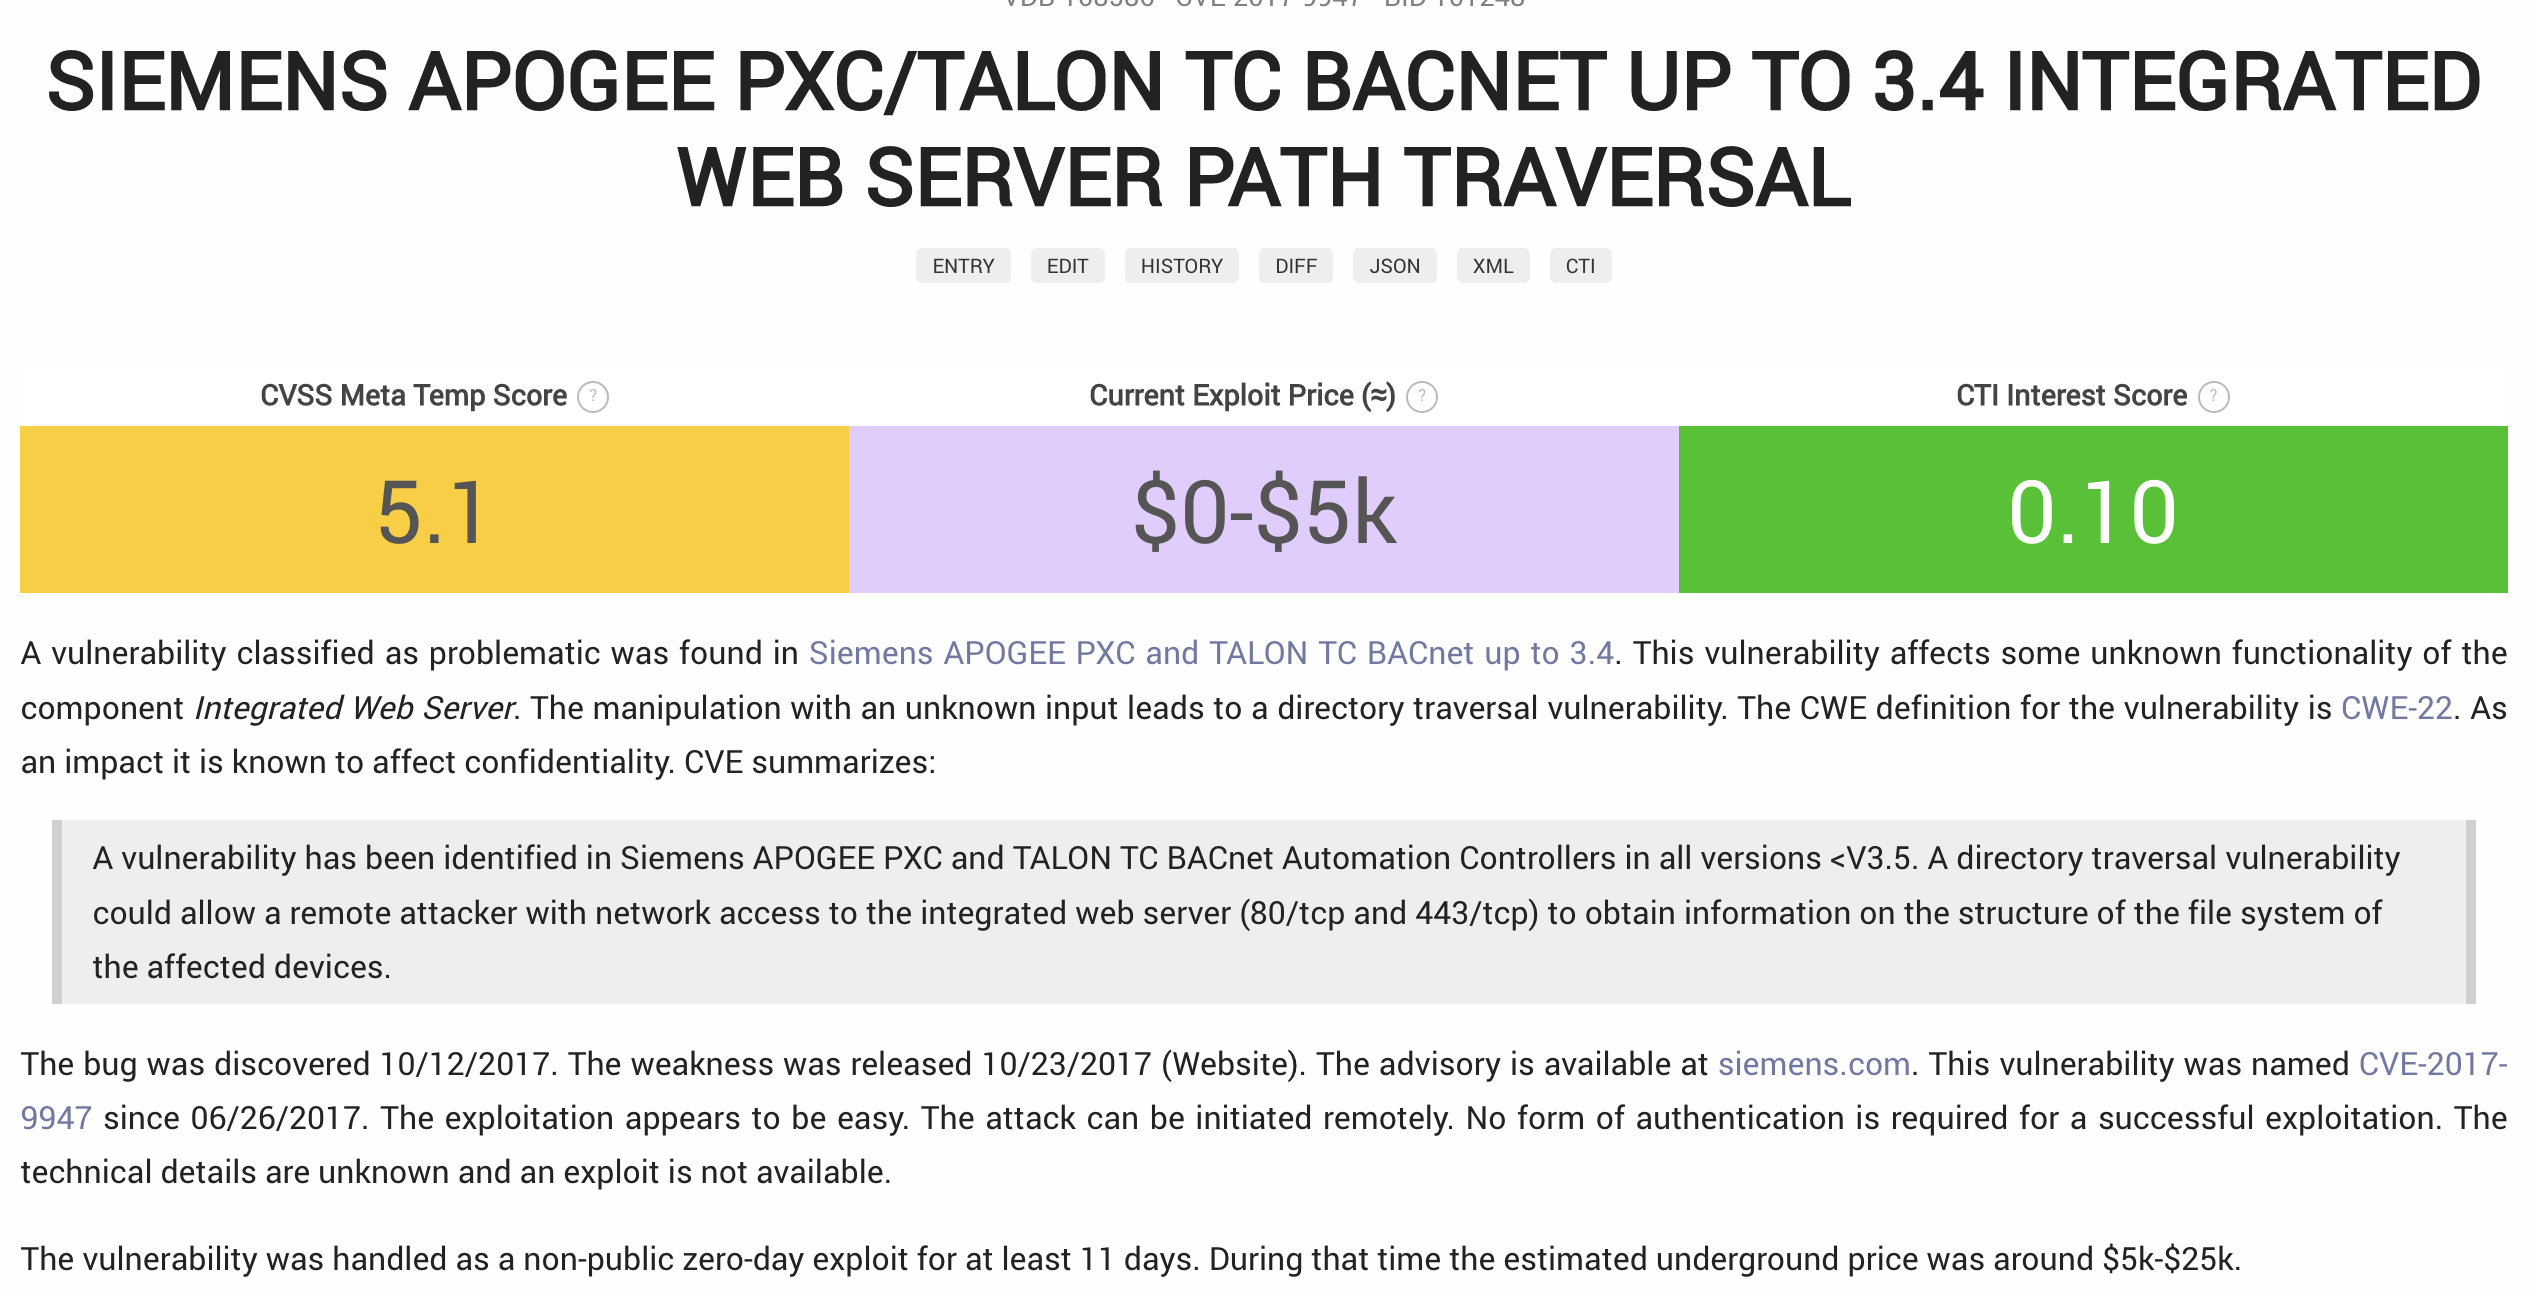 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
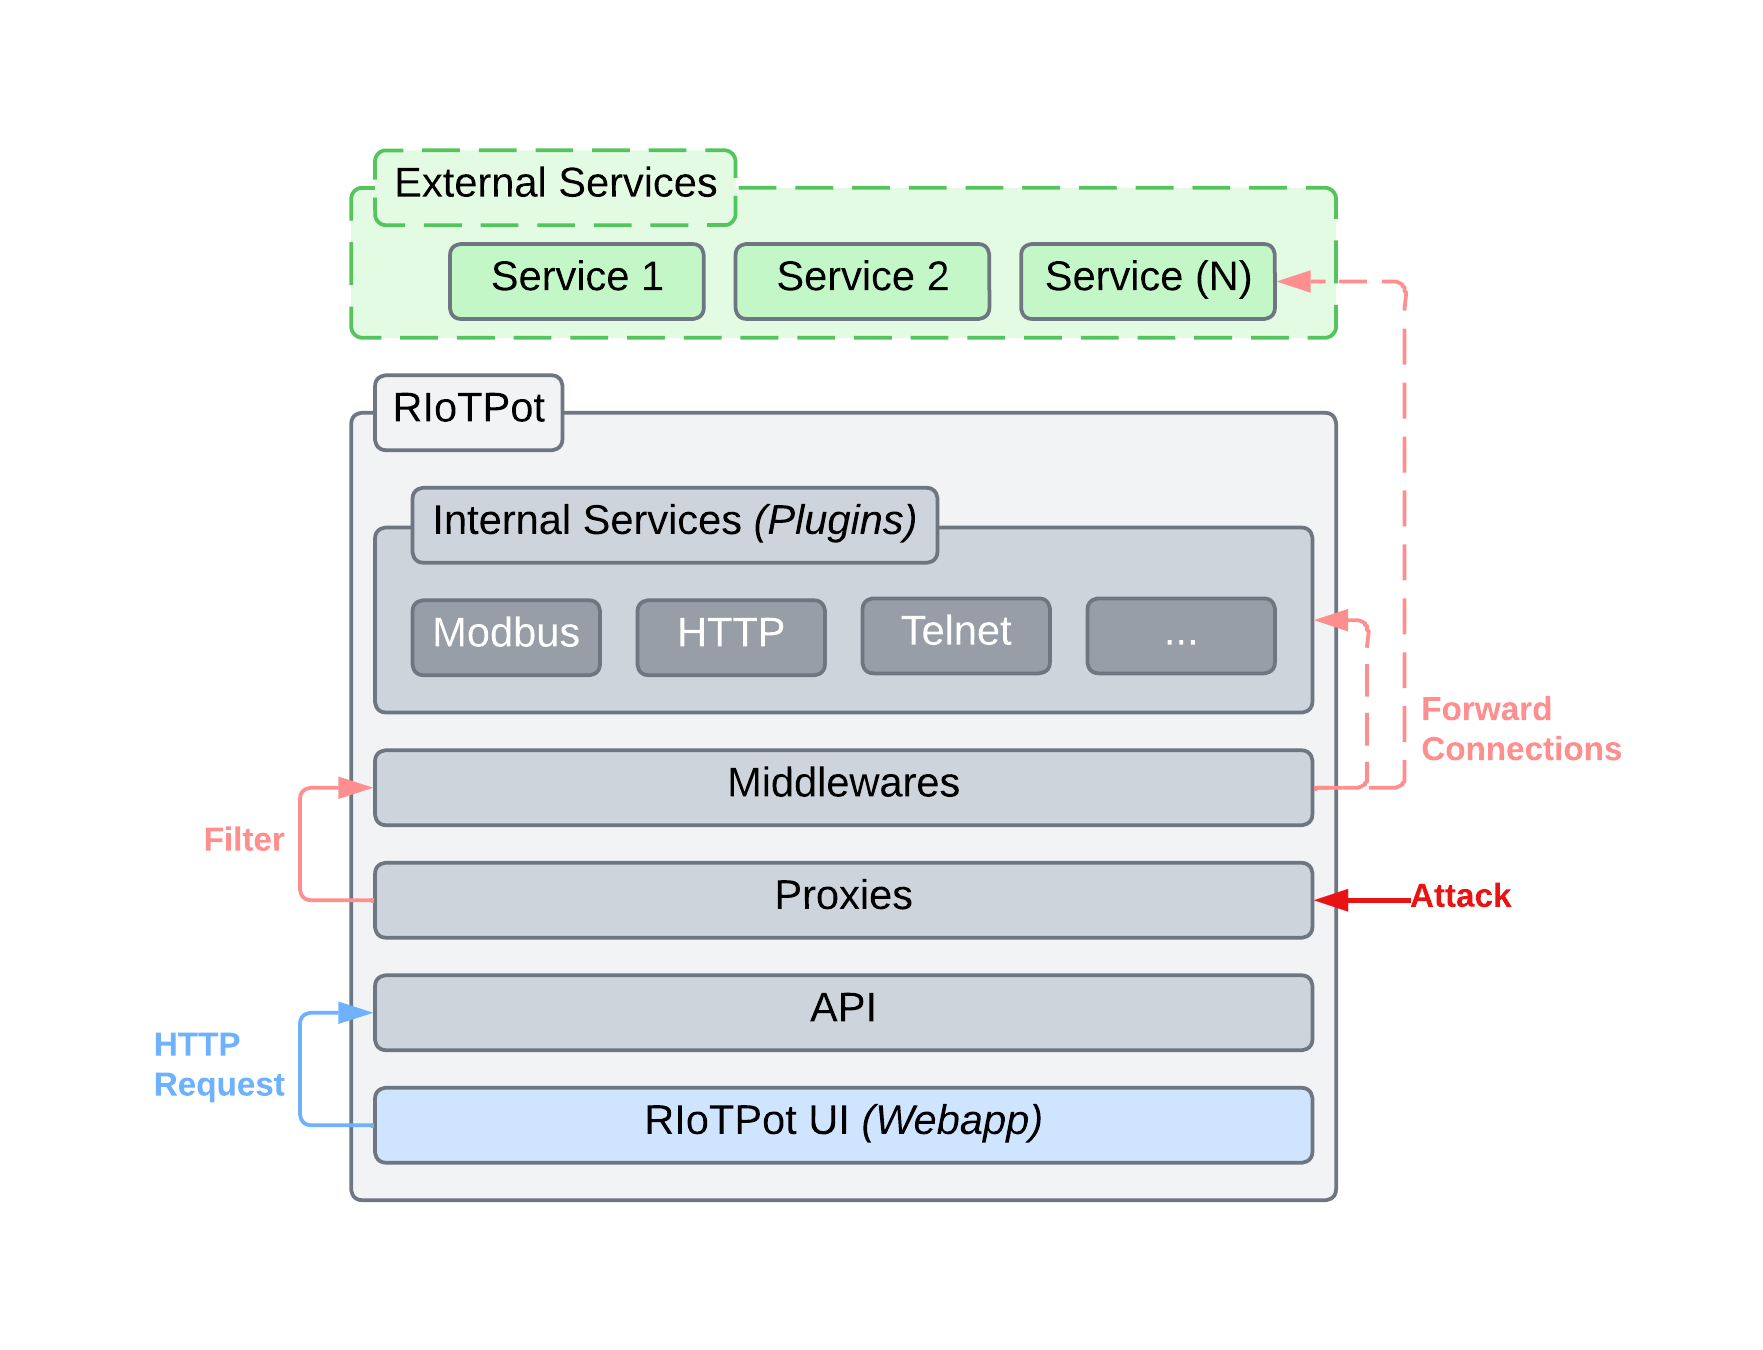 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
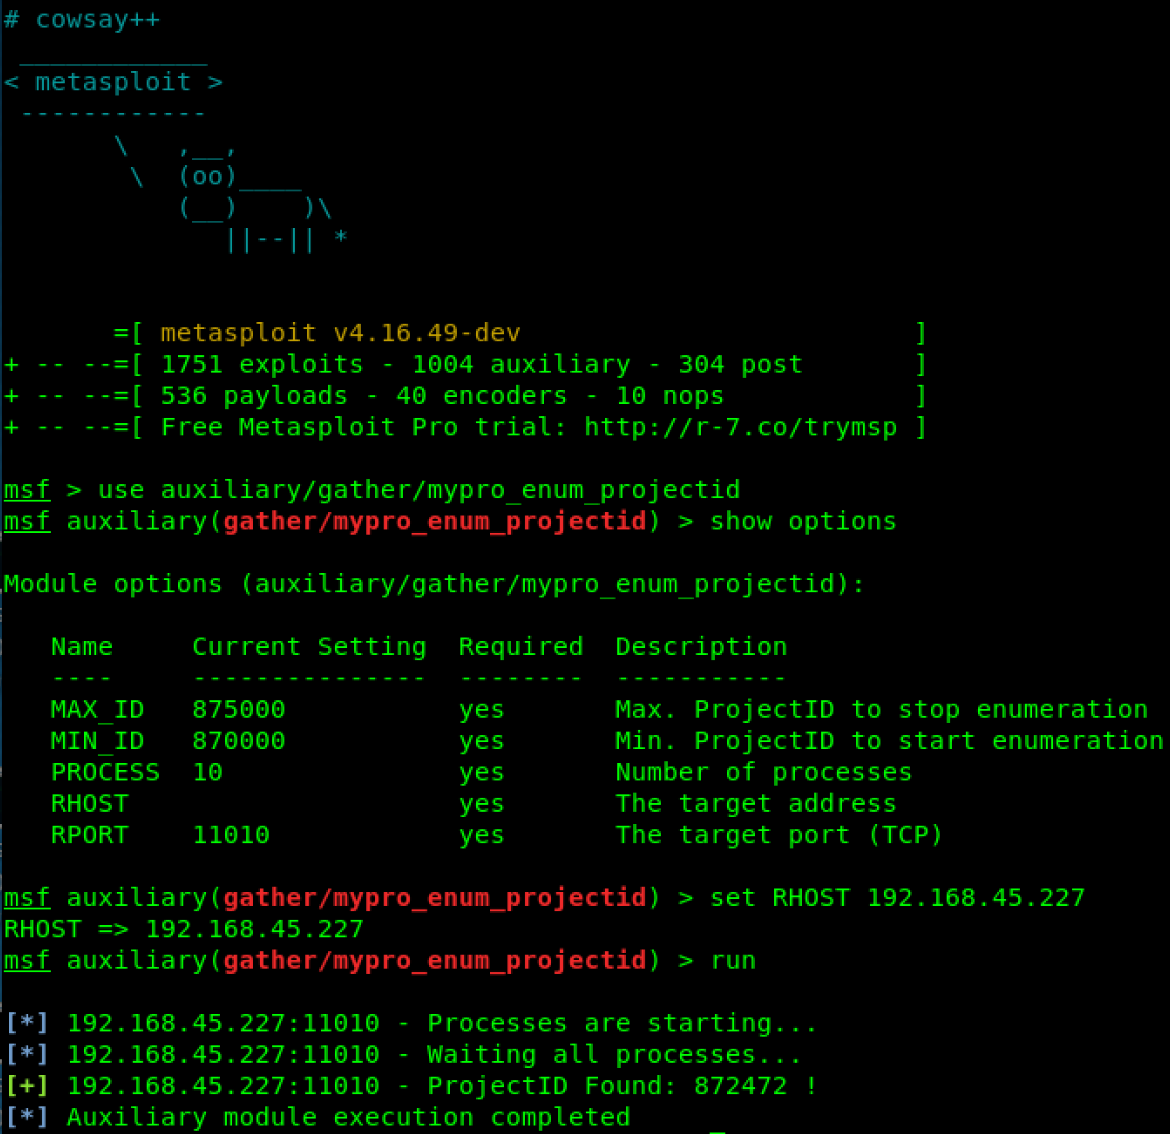 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.