metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…


High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Tools, tips, tricks, and more for exploring ICS Security.

Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…

Detect Tactics, Techniques & Combat Threats

A Curated list of Security Resources for all connected things

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

Python PoC for CVE-2026-8065: fingerprints Hitachi Energy RTU500 devices and probes firmware update endpoints for unauthenticated upload, with check,…

Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…

Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…

Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…

Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…

Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…

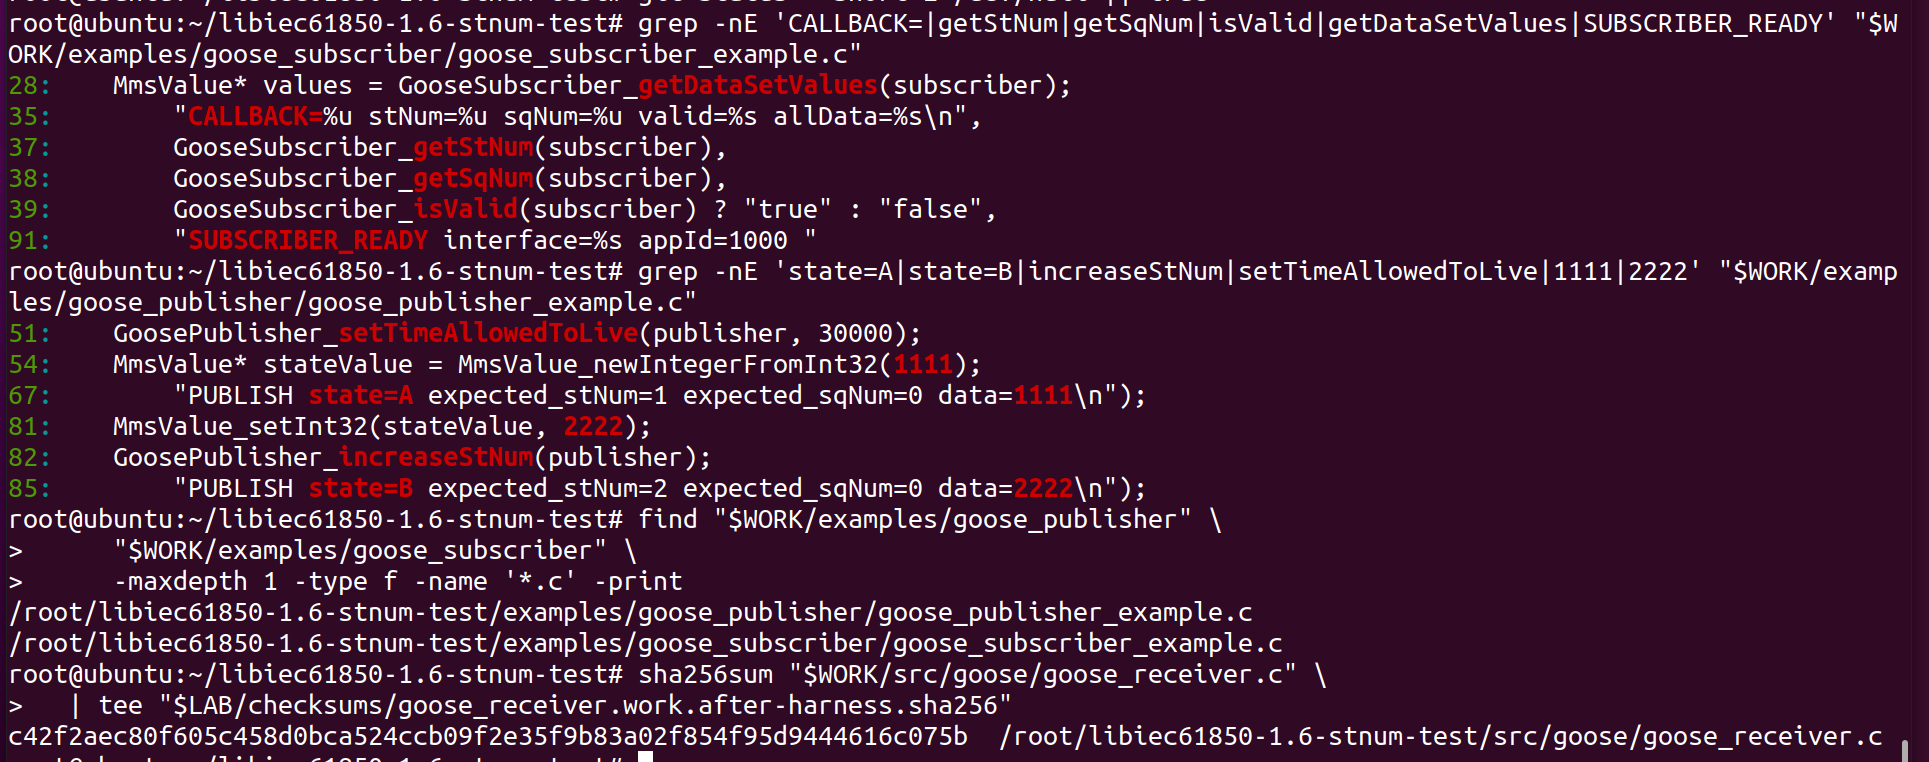
Public technical advisory and reproduction evidence for CVE-2026-52134 affecting GOOSE replay handling in libiec61850 v1.6.

Real-time simulation framework for cyber-physical systems with physical process/control device models and Mininet-based network emulation, built for…

Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…