EmbedXPL-Forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…

An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA

Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.

A Curated list of Security Resources for all connected things

Real world and CTFs exploiting web/binary POCs.

Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)

Purdue Model for Industrial Control System (ICS) Environments (Turkish)

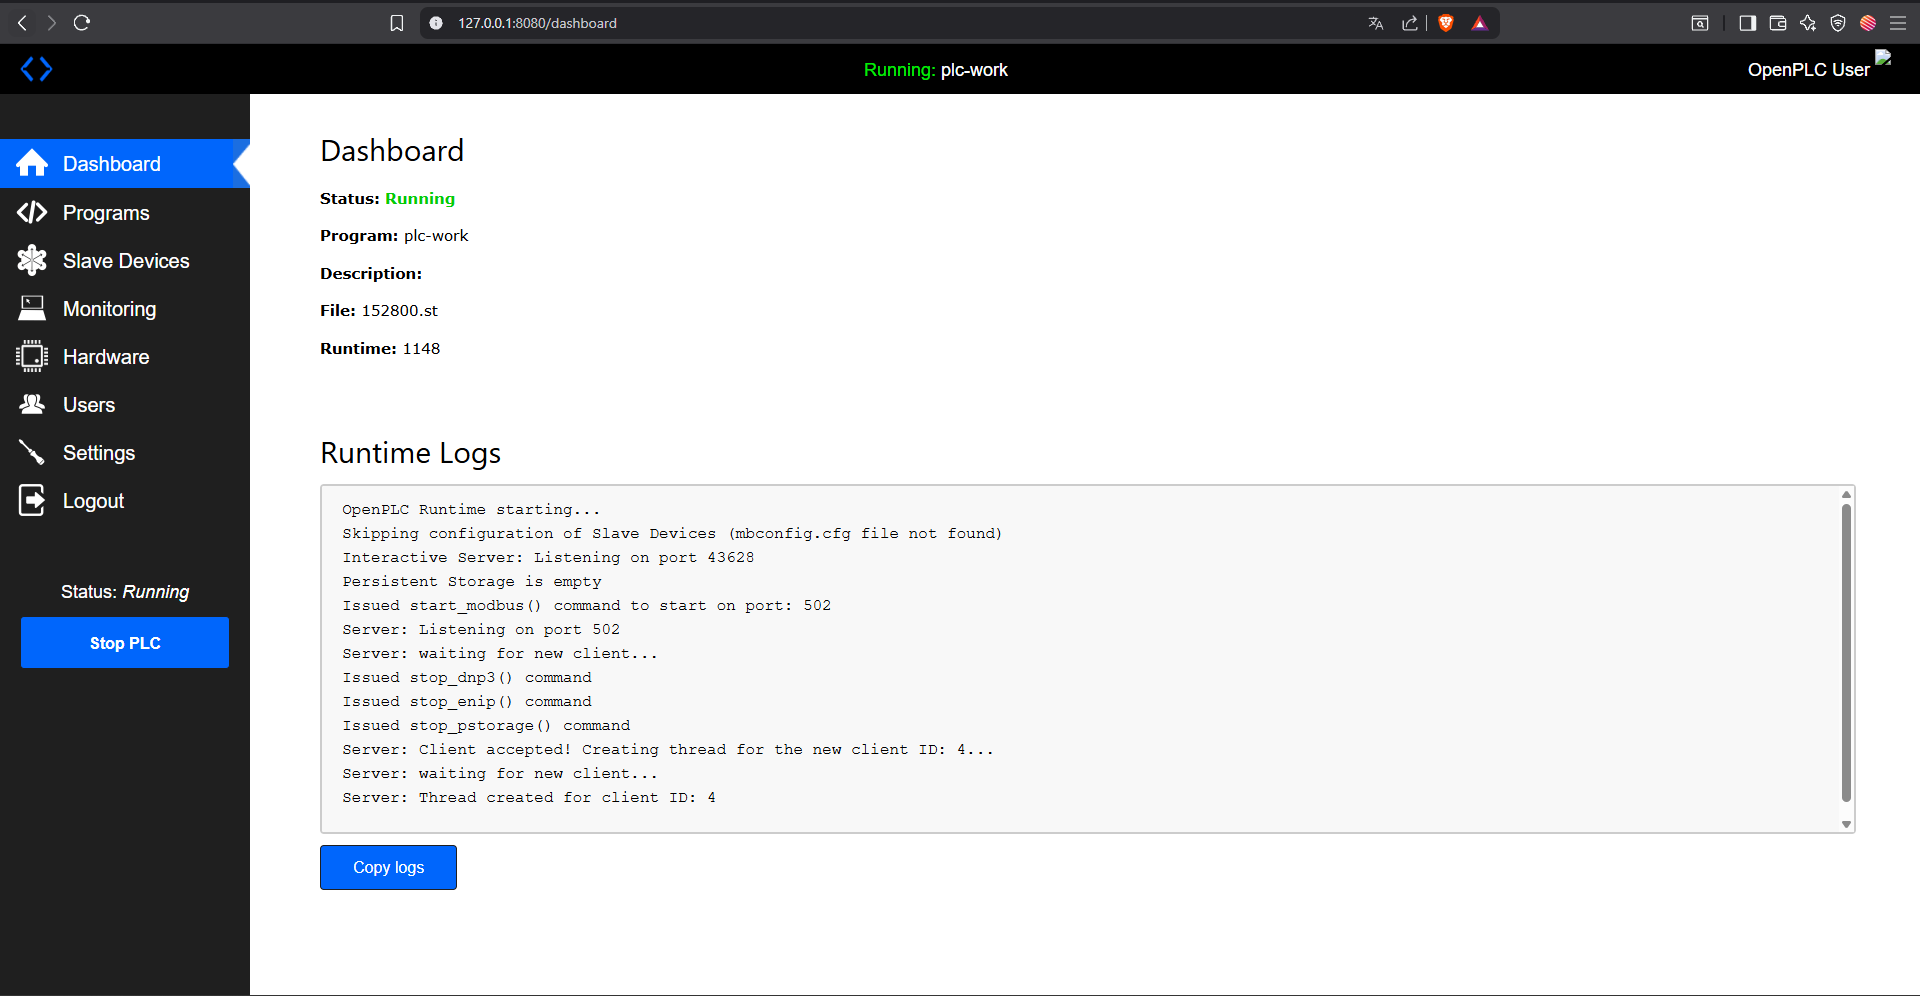
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…

POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE

Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…

This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656

SpiderControl SCADA Web Server File Upload Vulnerability

Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现

Security Vulnerability - Kardex Mlog MCC

Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers

proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.

All-in-one IoT Platform - Device management, data collection, processing and visualization.