CVE-2026-9645-ScadaBR-Analysis
 0xmhany/cve-2026-9645-scadabr-analysis
Technical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.
educationpapers-researchscada-ics-security+1
0xmhany/cve-2026-9645-scadabr-analysisTechnical vulnerability analysis and CVE briefing for CVE-2026-9645 affecting ScadaBR.
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 reidmefirst/moxapass
Small script to retrieve passwords from many types of Moxa device, including NPort, OnCell, MGate, etc.
 murataydemir/active-scanning-and-information-gathering-in-ics-scada-networks-using-network-mapper-nmap
Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)
 murataydemir/purdue-model-for-industrial-control-system-environments
Purdue Model for Industrial Control System (ICS) Environments (Turkish)
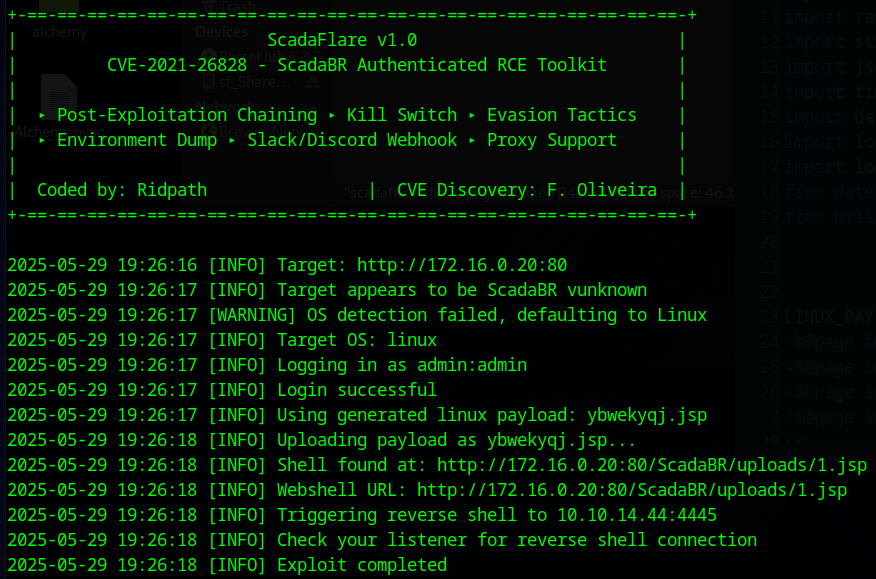 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 nullbyte8080/cve-2026-36226
Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…
 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 z3usx01/cve-2024-8232
SpiderControl SCADA Web Server File Upload Vulnerability
 webraybtl/cve-2022-1068
Modbus Slave缓冲区溢出漏洞CVE-2022-1068分析与复现
 vianic/cve-2023-22855
Security Vulnerability - Kardex Mlog MCC
 seifallahhomrani1/cve-2023-0861-poc
Analyzing and Reproducing the Command Injection Vulnerability (CVE-2023-0861) in NetModule Routers
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode