
OpcUaTrap
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
defensive-toolsincident-responseinformation-gathering+5
2
0xajstrike/opcuatrapHigh-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 shoucheng3/yamcs__yamcs_cve-2023-45277_5-8-6
Java-based mission control framework with YAML configuration, supporting telemetry, commanding, and simulation for spacecraft operations. Includes…
 rodolfomarianocy/unauthenticated-rce-fuxa-cve-2023-33831
Description and exploit of CVE-2023-33831 affecting FUXA web-based Process Visualization (SCADA/HMI/Dashboard) software.
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
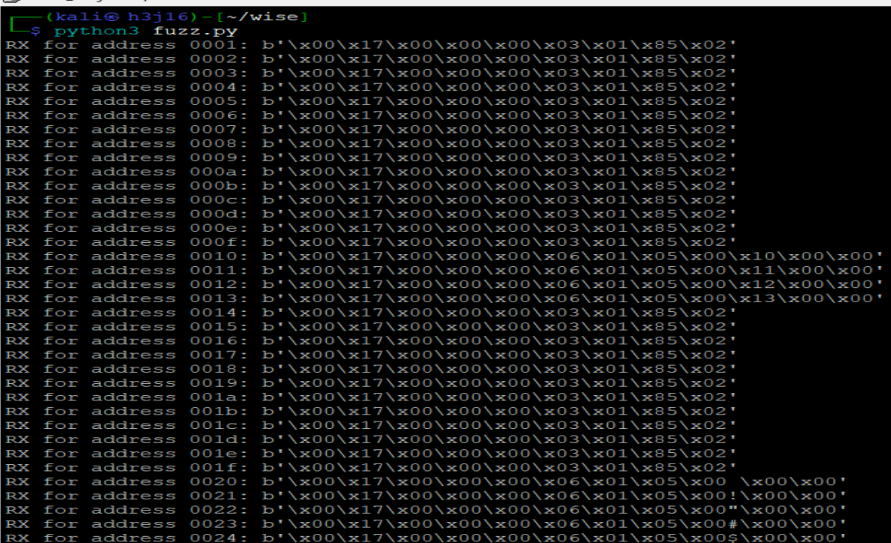 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 hunt3r0x/cve-2021-31630-htb
proof of Concept (PoC) exploit for CVE-2021-31630, targeting the OpenPLC service running on the WifineticTwo box on the Hack The Box platform.
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…