

Flipper
 uberguidoz/flipper
Playground (and dump) of stuff I make or modify for the Flipper Zero
curated-resourceseducationembedded-systems-security+3
17.6k2 months ago
uberguidoz/flipperPlayground (and dump) of stuff I make or modify for the Flipper Zero
 djsime1/awesome-flipperzero
🐬 A collection of awesome resources for the Flipper Zero device.
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 nfc-tools/mfcuk
Recovers cryptographic keys from MiFare Classic RFID cards using DarkSide and nested-auth attacks for security testing of NFC/RFID systems.
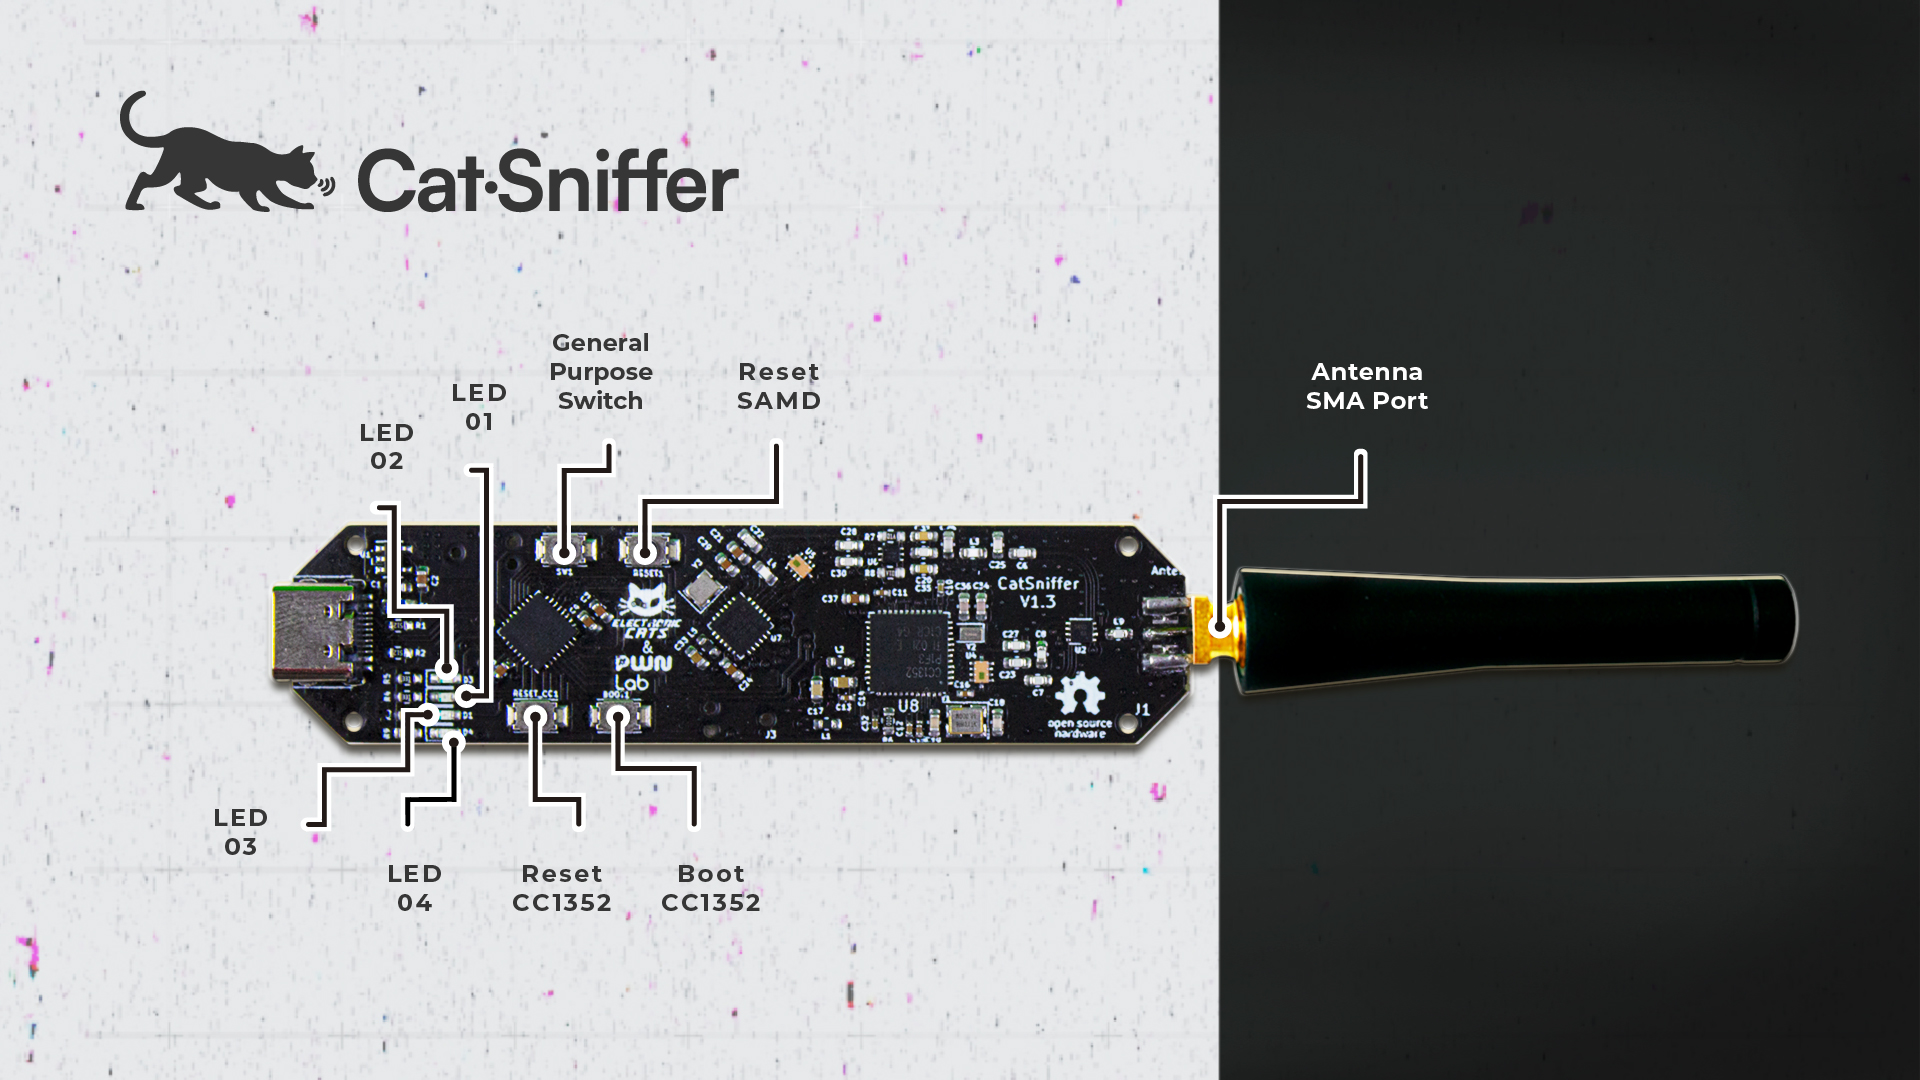 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
 nfc-tools/libfreefare
A convenience API for NFC cards manipulations on top of libnfc.
 x41sec/cve-2021-34600
Proof-of-concept exploit for CVE-2021-34600, demonstrating a key generation vulnerability in Telenot access control systems using Proxmark3 RFID…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

 adi0x90/attifyos
Attify OS - Distro for pentesting IoT devices
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…
 nfc-tools/milazycracker
Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 at0m-b0mb/specter-flipperzero
Specter — passive 13.56 MHz NFC reader/skimmer bug-sweep for Flipper Zero. Counter-surveillance EMF meter using the onboard NFC chip. No extra…