
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.

The open-source wireless research platform for ESP32.

Predatory ESP32 Firmware

Flipper Zero app for infrared electronic shelf-label (ESL) protocol research, featuring custom image transmission, NFC tag scanning, and a web-based…

Flipper Zero firmware source code

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…

A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol

BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.

🐬 A collection of awesome resources for the Flipper Zero device.

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…

Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…

Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…

Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.

Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…

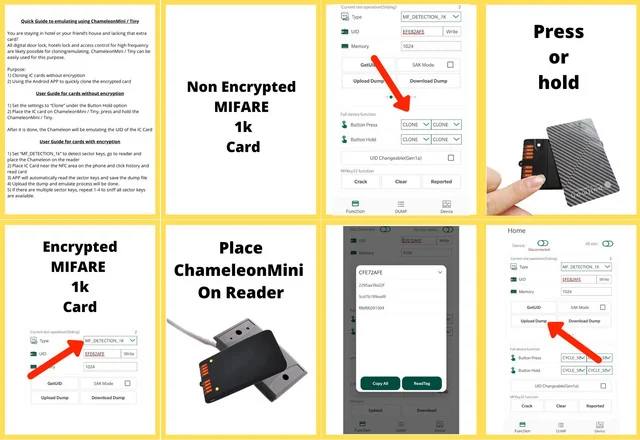
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…