flipper-mcp
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
ai-securitybluetooth-securitycommand-and-control+9
30
roostercoopllc/flipper-mcpAI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 brucedevices/firmware
Predatory ESP32 Firmware
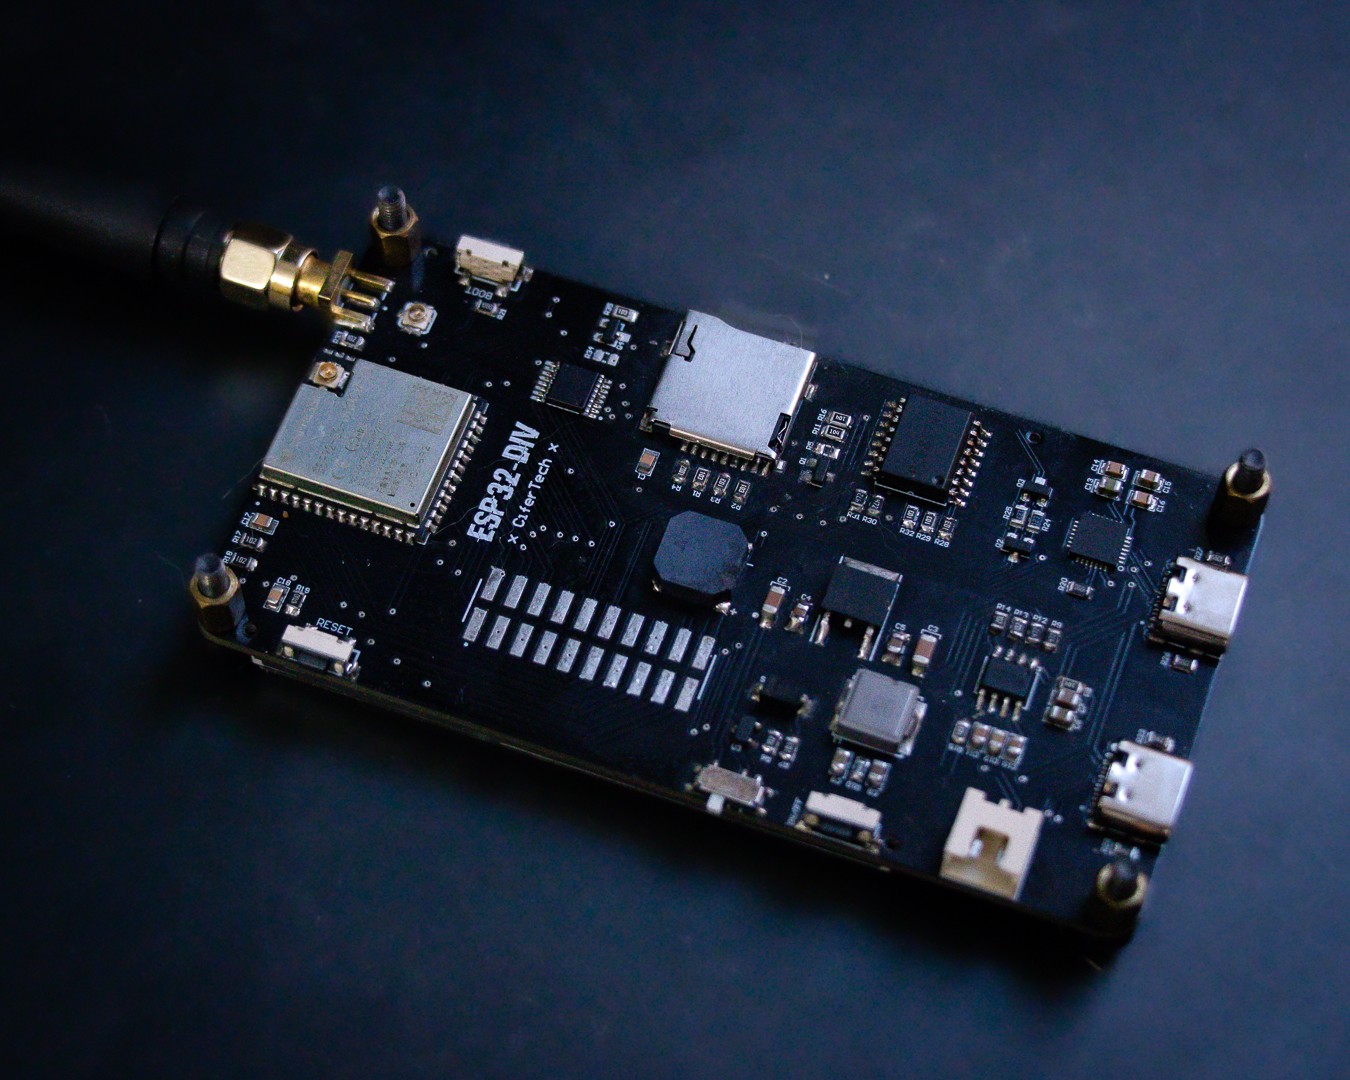 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 djsime1/awesome-flipperzero
🐬 A collection of awesome resources for the Flipper Zero device.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
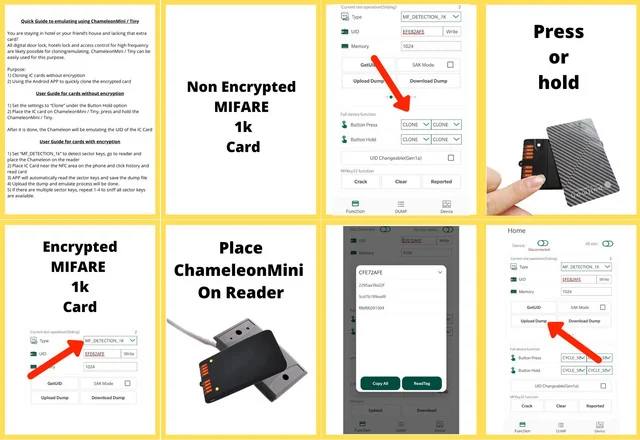 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
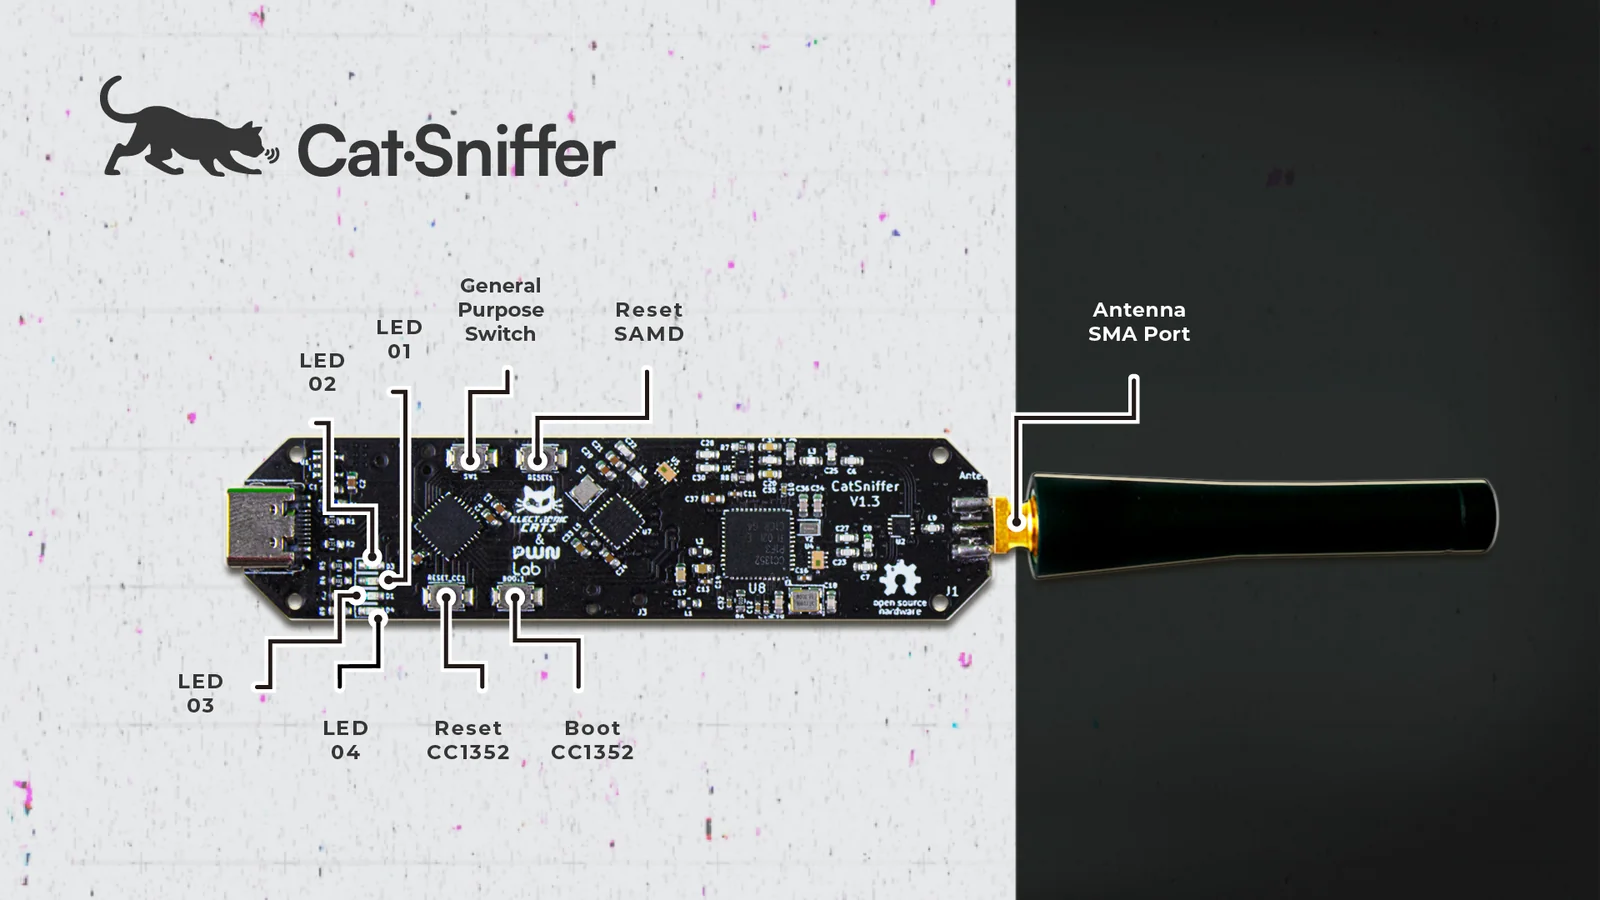 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
 nfc-tools/libnfc
Platform independent Near Field Communication (NFC) library
 nfc-tools/milazycracker
Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader