

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
410 results
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
Windows-PE-Packer preview

Windows-PE-Packer

GitHubczs108/windows-pe-packer

🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
binary-analysisexploitationpayload-generation+1
3671 year ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.

adversarial-attackbinary-analysiseducation+3
36410 months ago
ida_bochs_windows preview

ida_bochs_windows

GitHubtherealdreg/ida_bochs_windows

Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
binary-analysisdebuggersdynamic-code-analysis+1
613 years ago
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

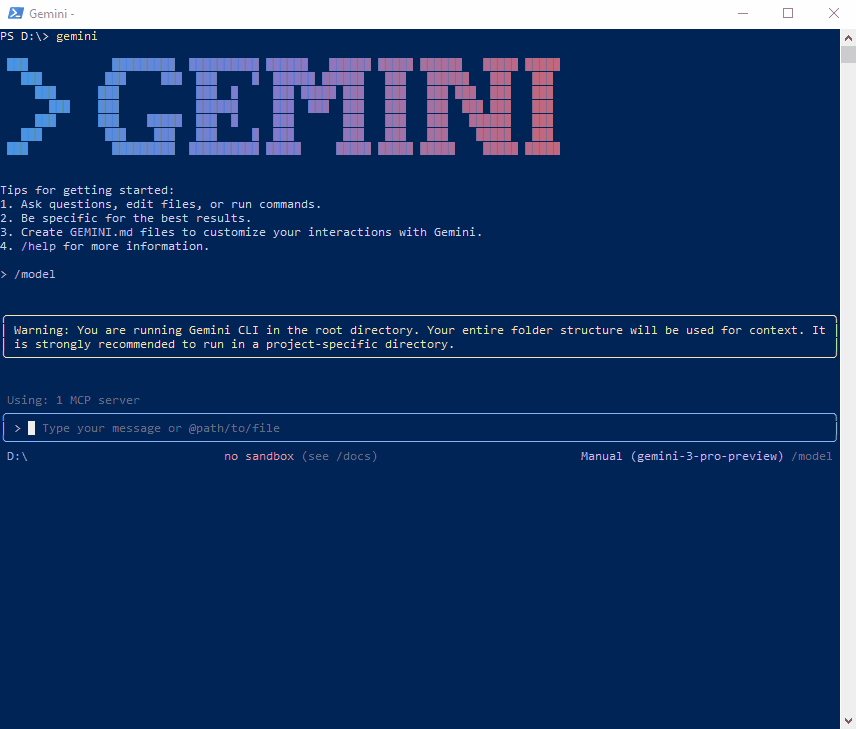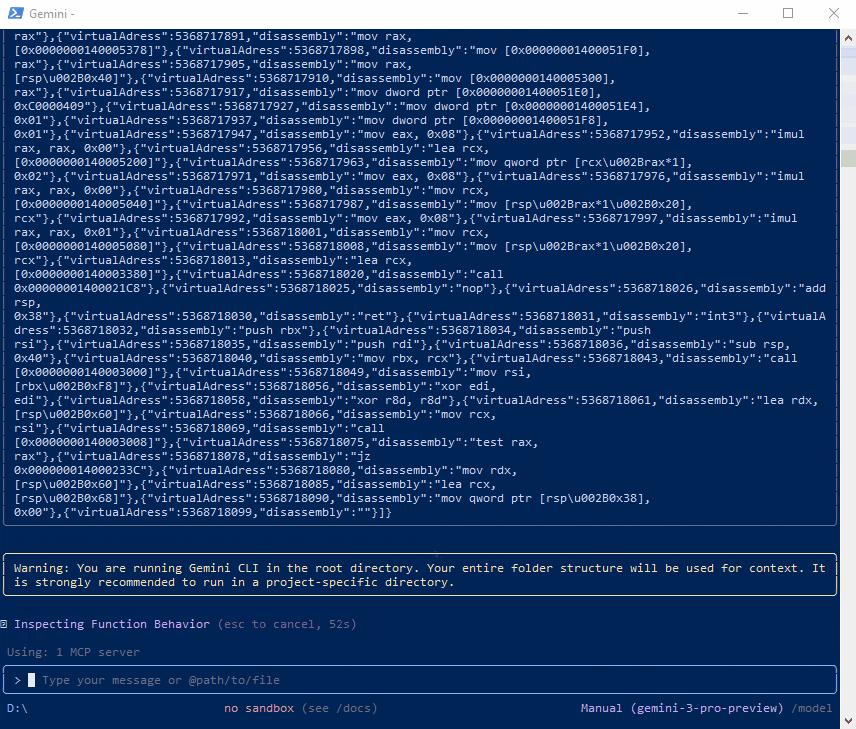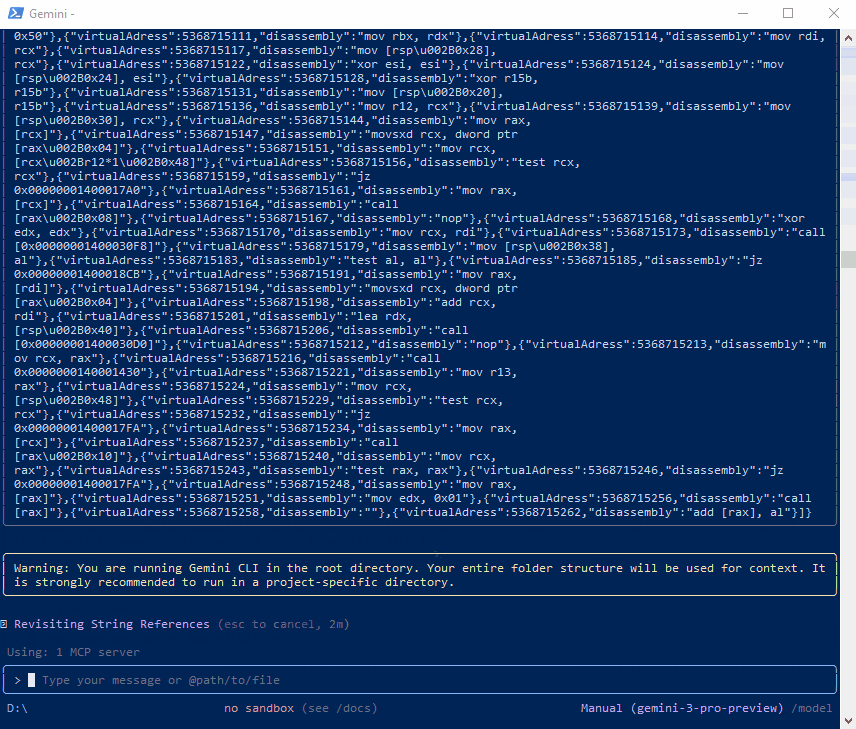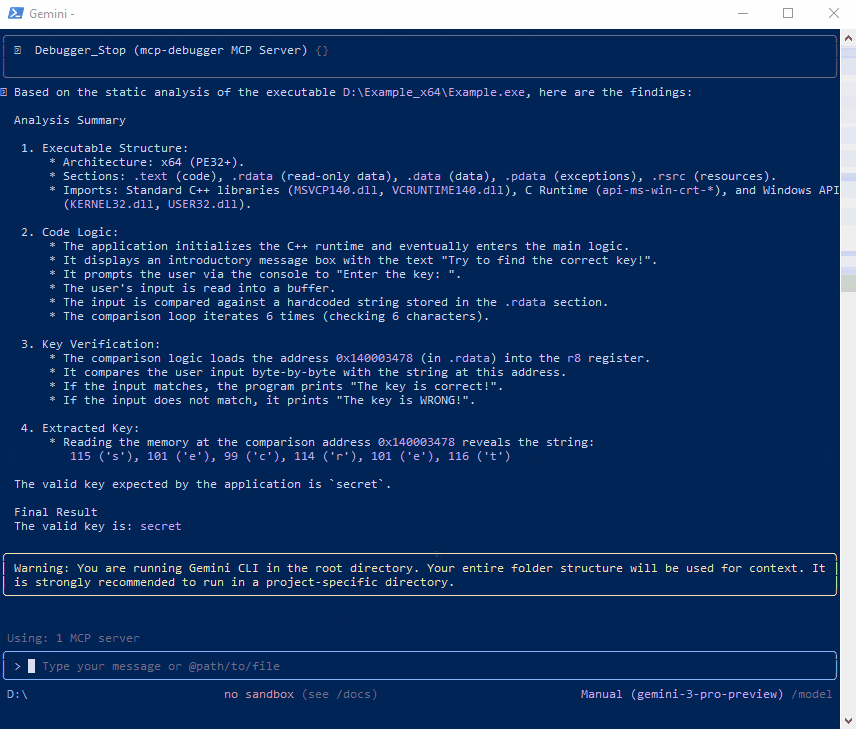
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
ai-assisted-reversingbinary-analysisdebuggers+4
136 months ago
peafl64 preview
Archived

peafl64

GitHubsentinel-one/peafl64

Static Binary Instrumentation tool for Windows x64 executables

binary-analysisdynamic-code-analysisfuzzing+2
2061 year ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

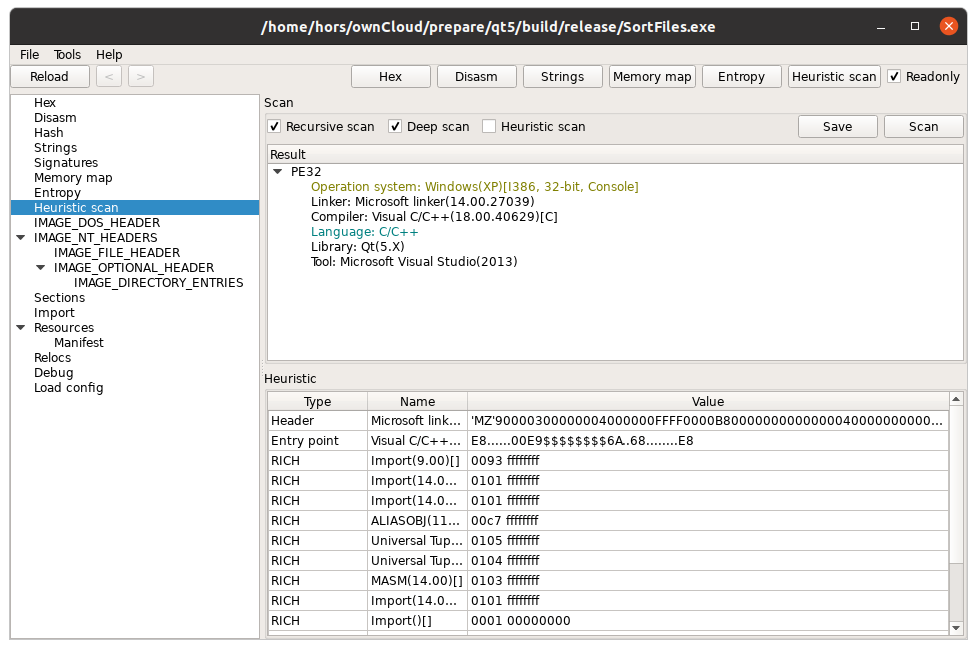
Program for determining types of files for Windows, Linux and MacOS.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k0 days ago
flare-vm preview

flare-vm

GitHubmandiant/flare-vm

A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
binary-analysisdebuggersdigital-forensics+10
9.1k3 months ago
malware_training_vol1 preview

malware_training_vol1

GitHubhasherezade/malware_training_vol1

Materials for Windows Malware Analysis training (volume 1)
binary-analysiseducationforensics+4
2.1k2 years ago
XPEViewer preview

XPEViewer

GitHubhorsicq/xpeviewer

PE file viewer/editor for Windows, Linux and MacOS.

binary-analysisreverse-engineeringstatic-analysis
1.2k1 day ago
XMachOViewer preview

XMachOViewer

GitHubhorsicq/xmachoviewer

XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
binary-analysiscode-analysismalware-analysis+2
96611h 12m ago
BugChecker preview

BugChecker

GitHubvitoplantamura/bugchecker

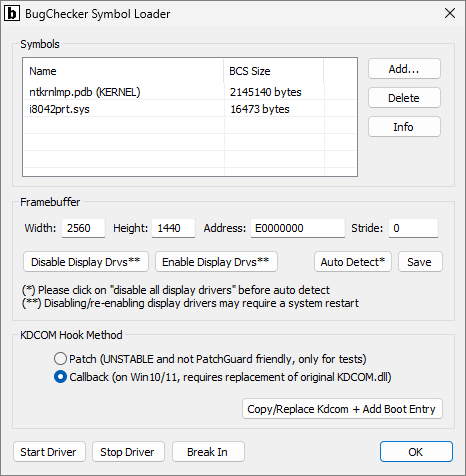
SoftICE-like kernel debugger for Windows 11
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1.1k3 years ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
8273 months ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
anti-botbinary-analysisdefensive-tools+4
33313 days ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
packer-tutorial preview

packer-tutorial

GitHubfrank2/packer-tutorial

A tutorial on how to write a packer for Windows!
binary-analysiseducationmalware-analysis+1
3182 years ago
JOP_ROCKET preview

JOP_ROCKET

GitHubbw3ll/jop_rocket

This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…

binary-exploitationeducationexploitation+4
1172 years ago
Previous12…23Next