
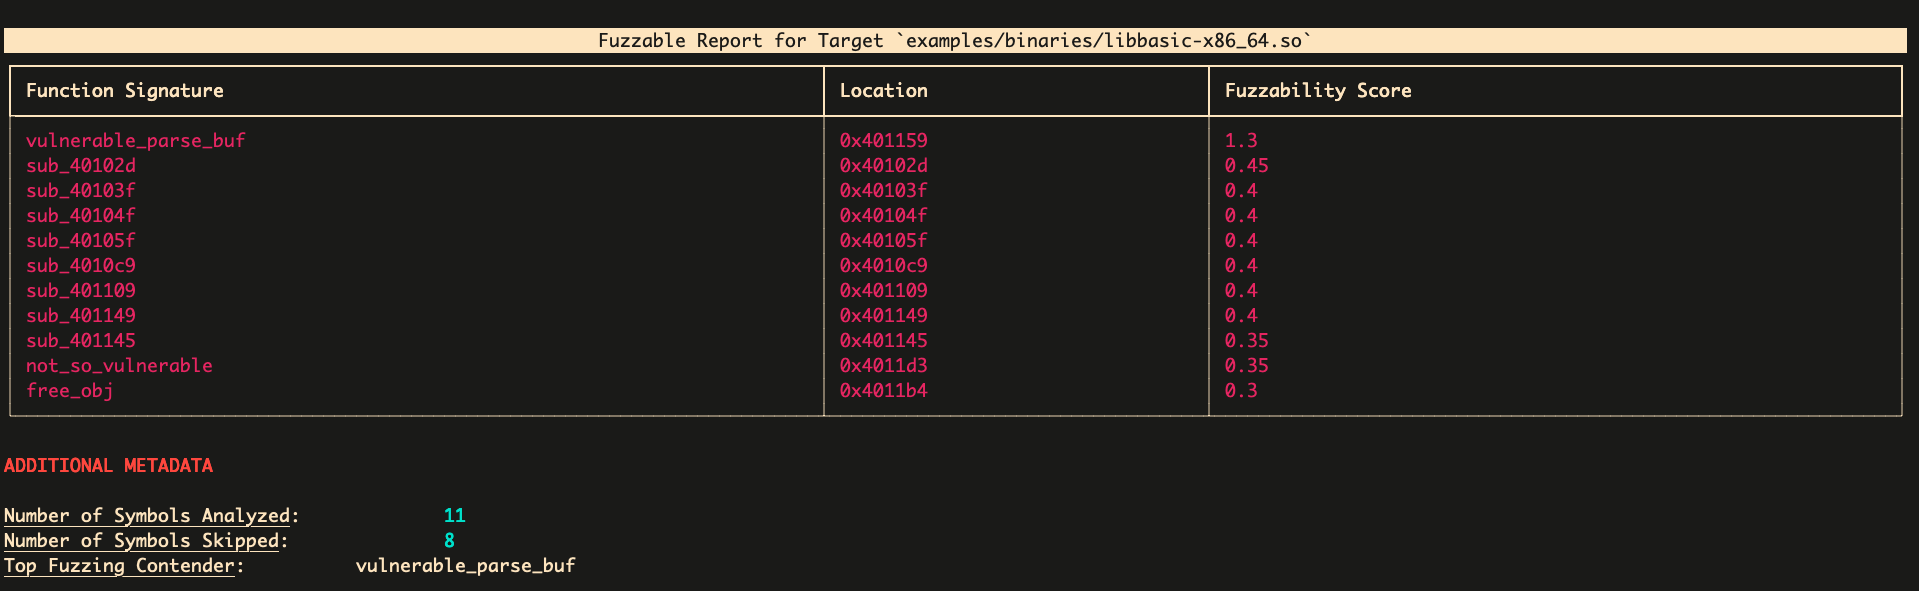
fuzzable
 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
binary-analysisfuzzingreverse-engineering+2
549
ex0dus-0x/fuzzableStatic analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…
 jonathansalwan/triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
 colton1skees/dna
LLVM based static binary analysis framework