
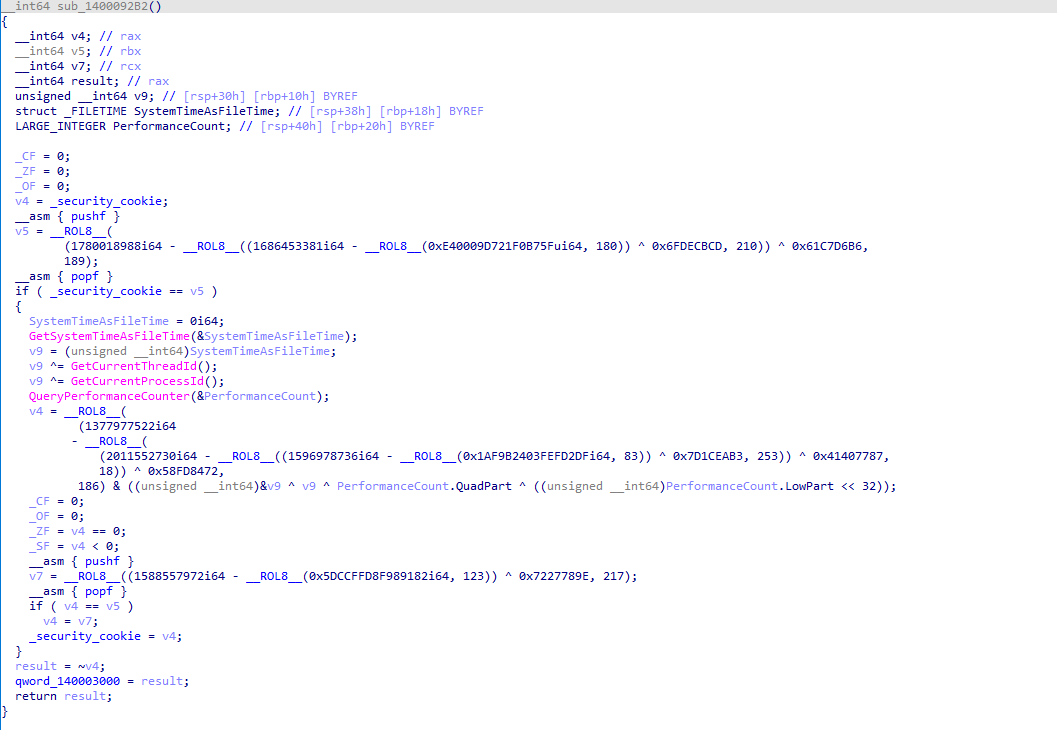
Alcatraz
 weak1337/alcatraz
x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
binary-analysisreverse-engineering
weak1337/alcatrazx64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
 ergrelet/unlicense
Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.
 allthingsida/allthingsida
Repository for the code snippets from the AllThingsIDA video channel
 zznop/bn-uefi-helper
Helper plugin for analyzing UEFI firmware
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses