

exploitation-course
 ashemery/exploitation-course
Offensive Software Exploitation Course
binary-exploitationeducationexploitation+7
2.5k3 years ago
ashemery/exploitation-courseOffensive Software Exploitation Course
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 live-ctf/livectf-defcon30
Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 ctn-qvo/auto_extract_offsets
Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.
 jprx/cve-2024-54507
Proof-of-concept exploit for CVE-2024-54507, an integer type confusion vulnerability in XNU kernel, with technical writeup and exploitation details.
 bytev0rtex/cve-2026-64788
Proof-of-concept for CVE-2026-64788, a use-after-free in IOGPUFamily kernel extension on iOS 26.6, demonstrating exploitation via Metal texture…
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 bytev0rtex/cve-2026-65349
Proof-of-concept for an out-of-bounds write in XNU's vfs_attr_pack_internal (getattrlist) on iOS 26.6, demonstrating kernel heap corruption and…
 fm0ss/cve-2025-9951-ffmpeg-jp2-poc
Proof-of-concept for CVE-2025-9951 demonstrating controlled callback execution in FFmpeg via JPEG 2000 component-mapping mismatch. Includes write-up,…
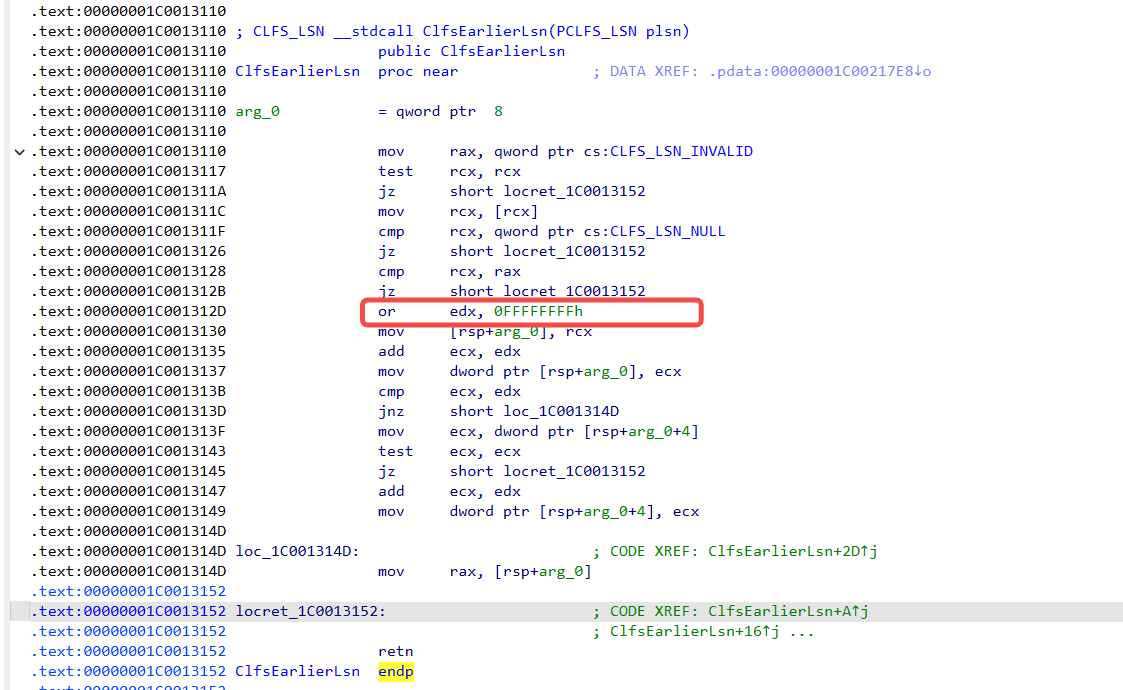 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…
 flamelu/cve-2020-17035-patch-analysis
Analysis of the patch for CVE-2020-17035, detailing the vulnerability and exploitation mechanism in the affected binary component.
 pazhanivelmani/av_cve-2020-0162_a10r33
Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
 khoatran107/cve-2025-38001
C-based proof-of-concept exploit for CVE-2025-38001, demonstrating vulnerability exploitation and code analysis for security research.
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
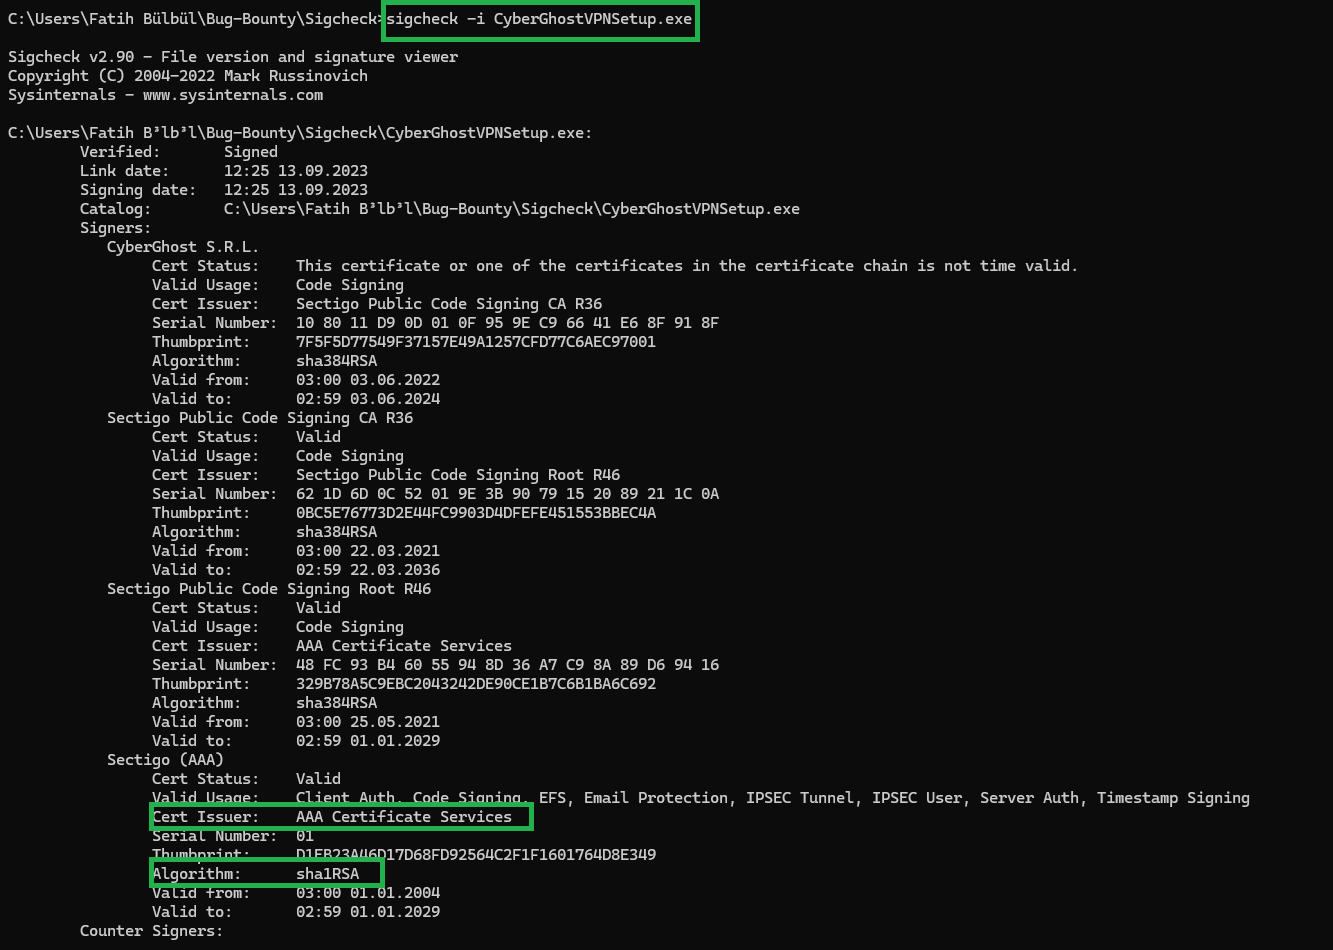 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…