
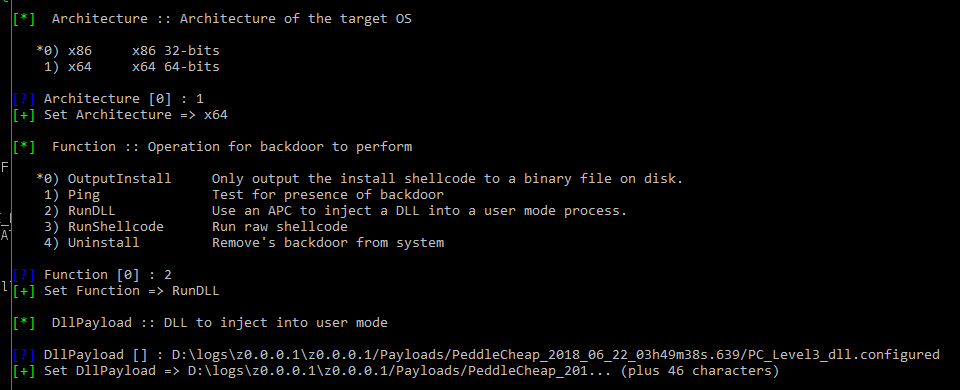
DanderSpritz_lab
 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
educationexploit-frameworkslabs-practice+5
4517 years ago
francisck/danderspritz_labA fully functional DanderSpritz lab in 2 commands
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 clearbluejar/cve-2024-20696
Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
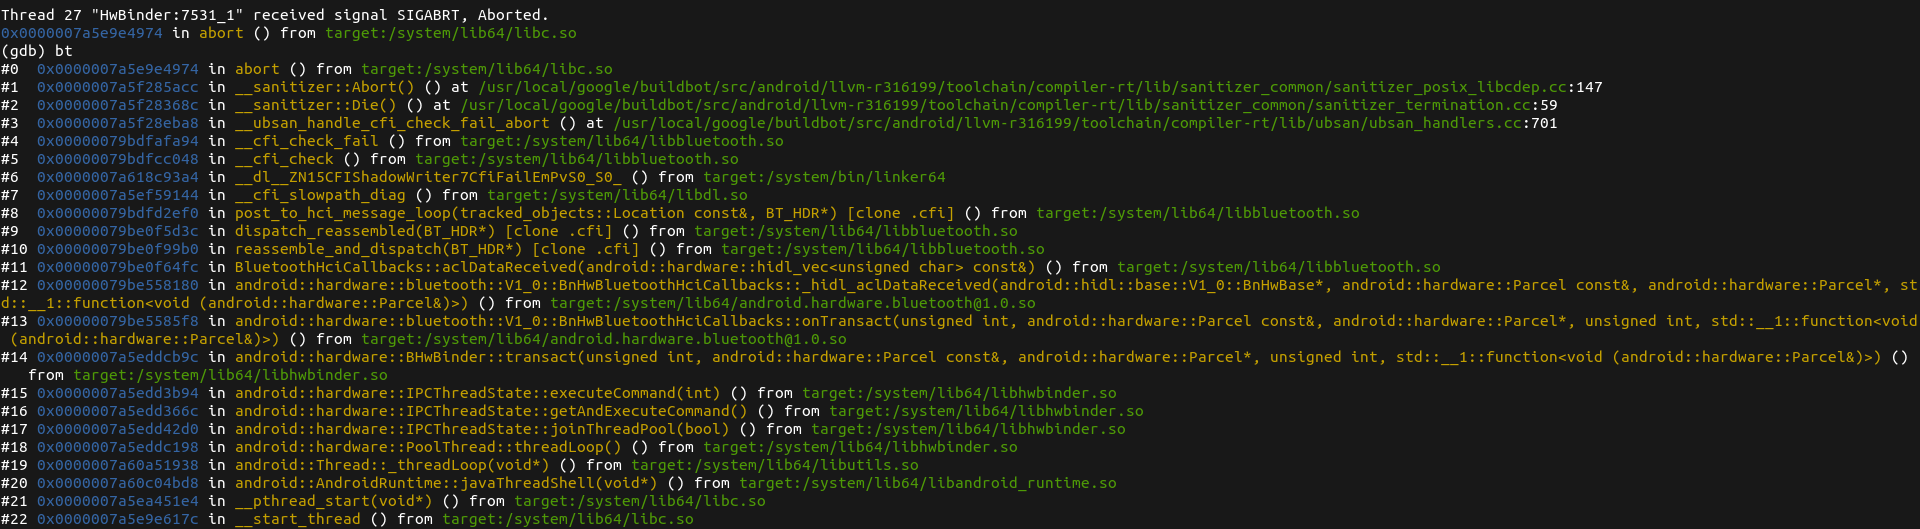 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
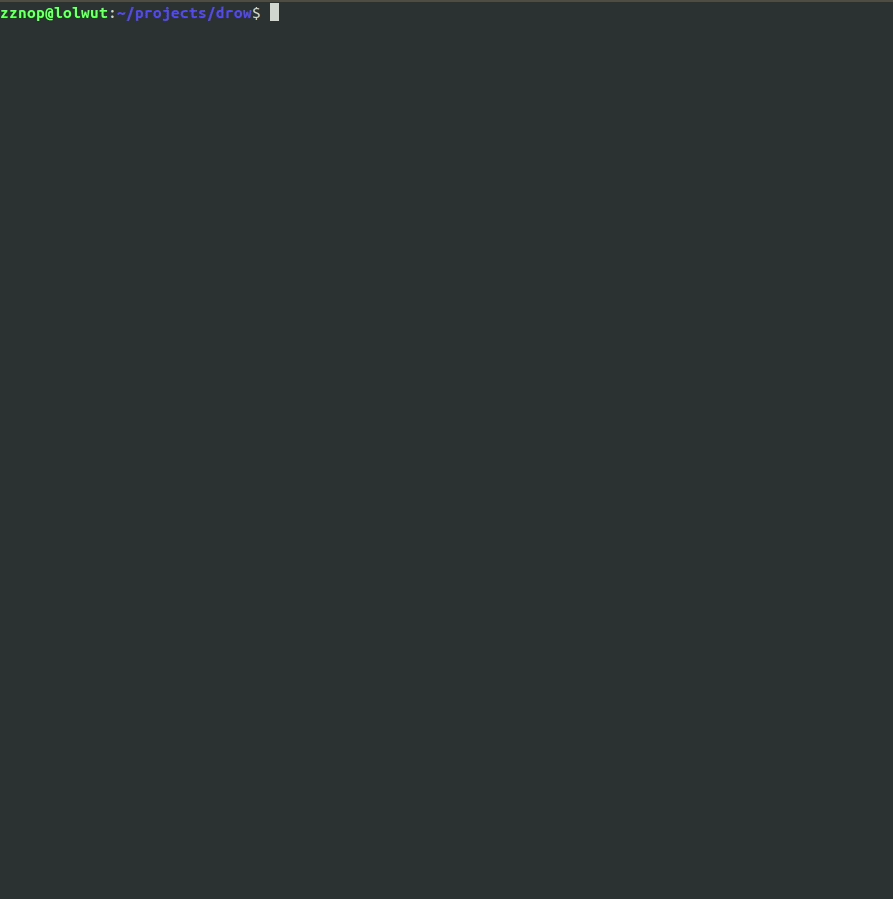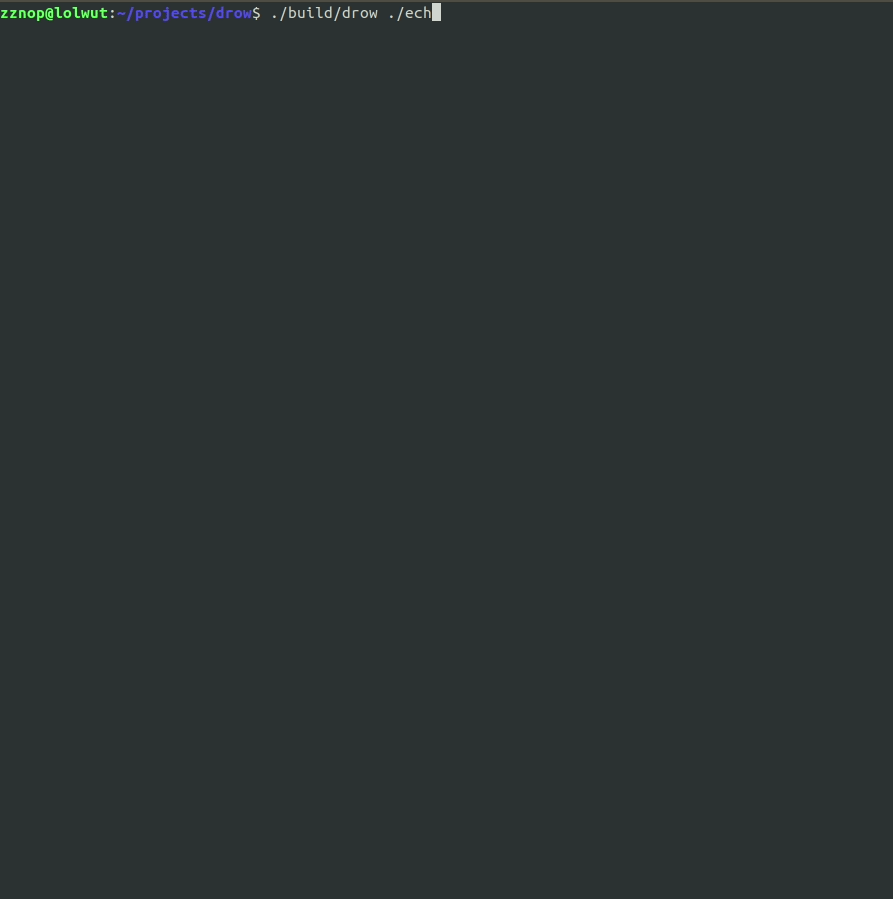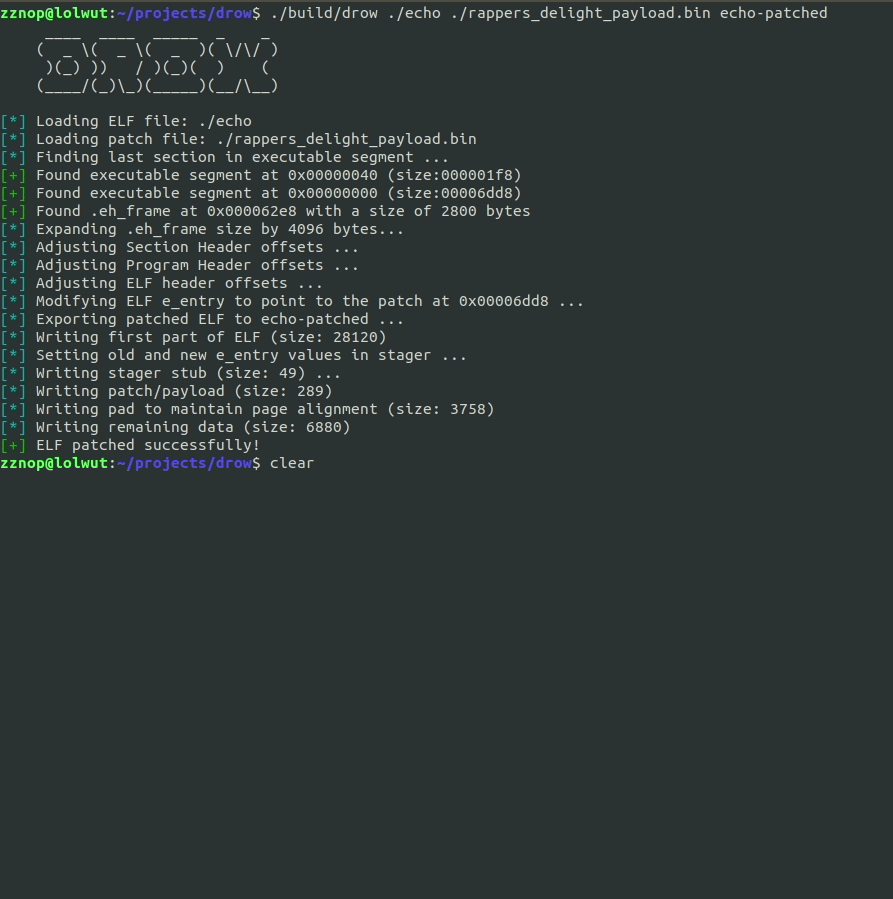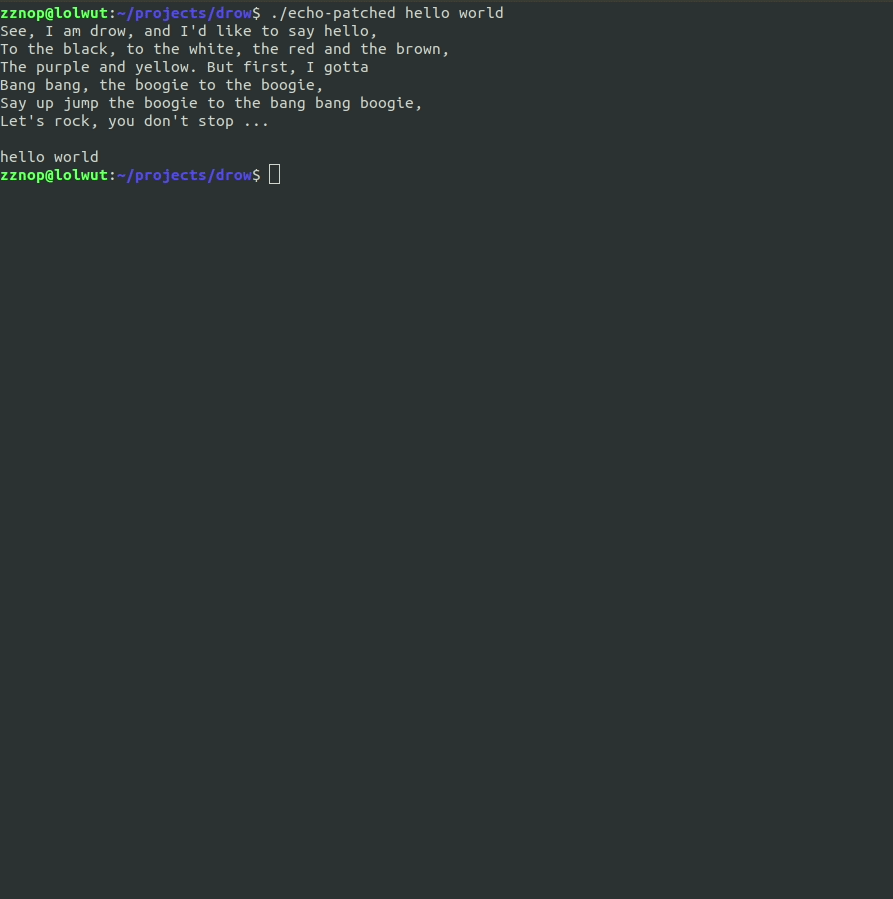 zznop/drow
Injects code into ELF executables post-build
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam