

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
8 results
win-def-clickfix preview

win-def-clickfix

GitHubbackdoorskid/win-def-clickfix

A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
binary-analysisdefensive-toolsmalware-analysis+3
2
7 days ago
CVE-2025-62821 preview

CVE-2025-62821

GitHubhyunjungg/cve-2025-62821

Microsoft HEIF Extension (msheif_store.dll) OOB-read

binary-analysisexploitationfuzzing+3
1 year ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
968 months ago
windiff preview

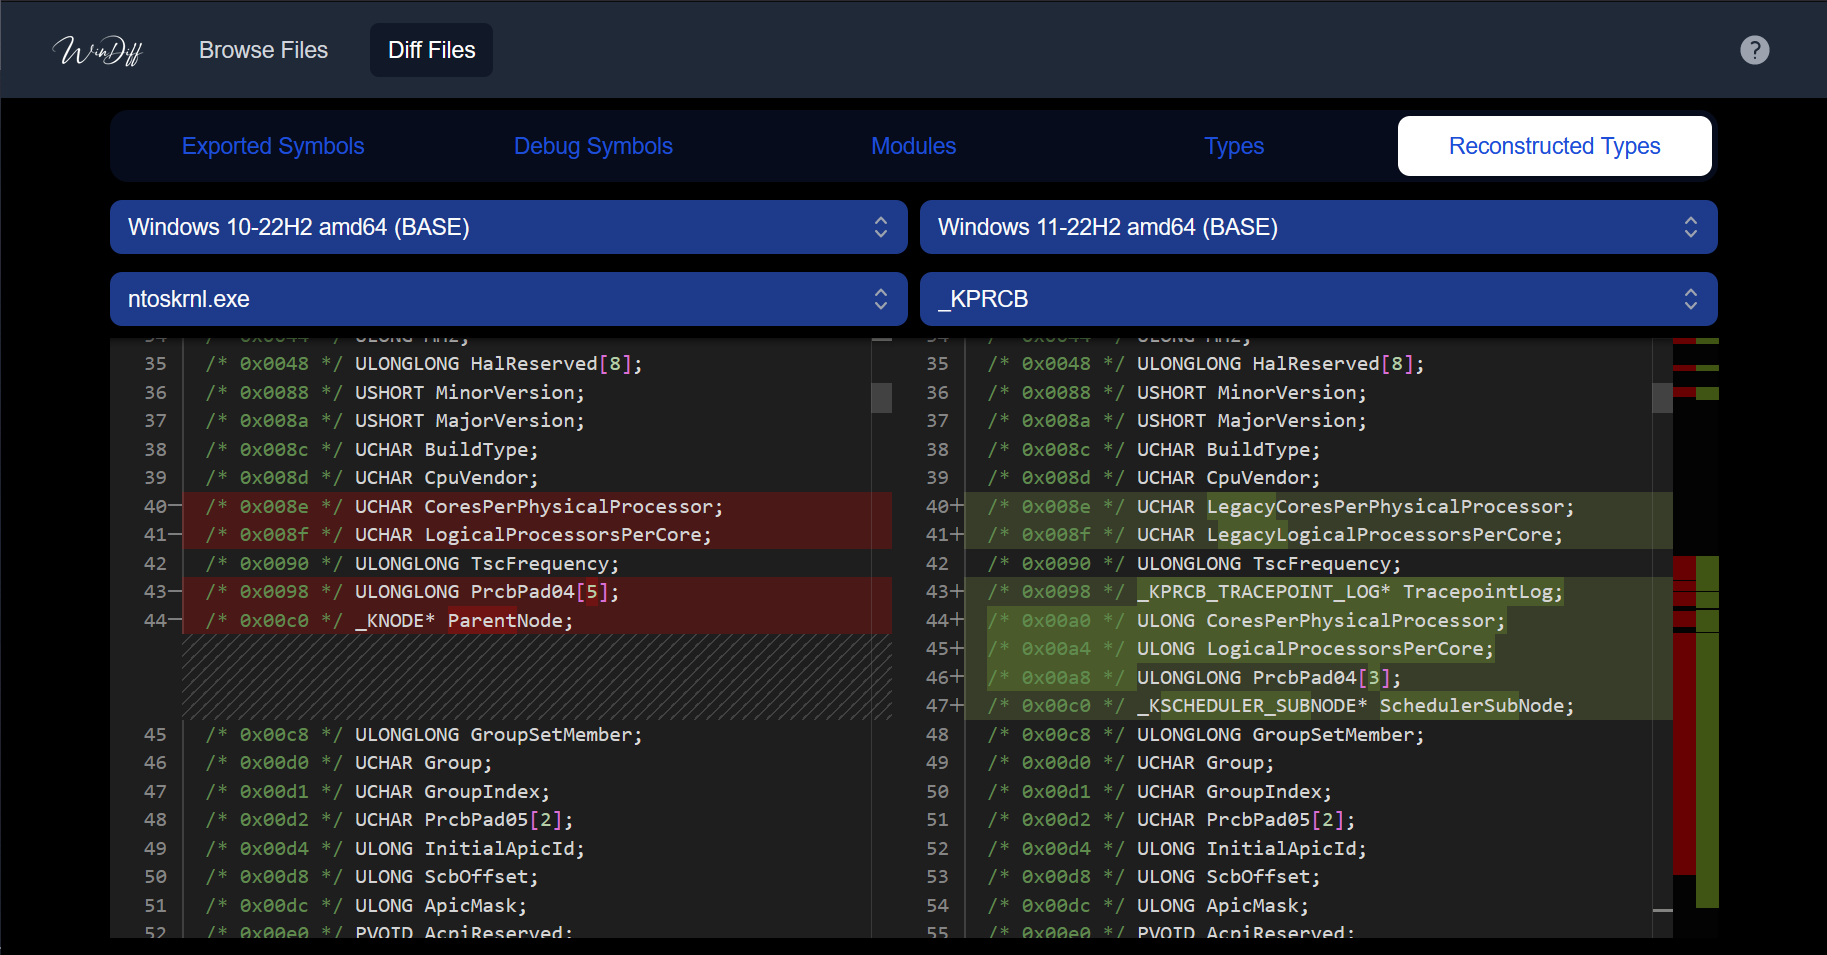
windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

binary-analysisinformation-gatheringreverse-engineering+1
3951 day ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
371 month ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
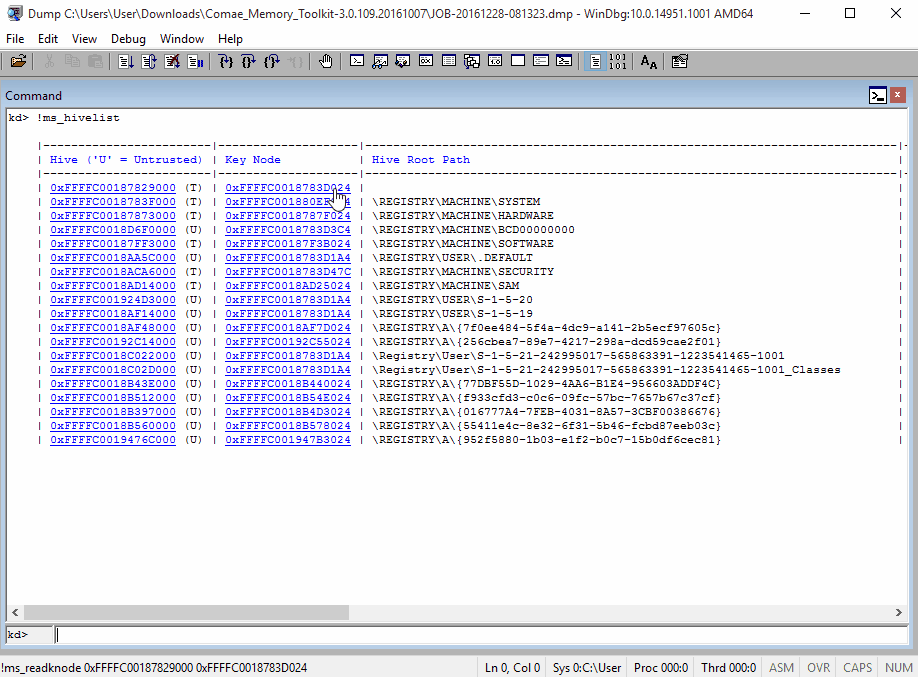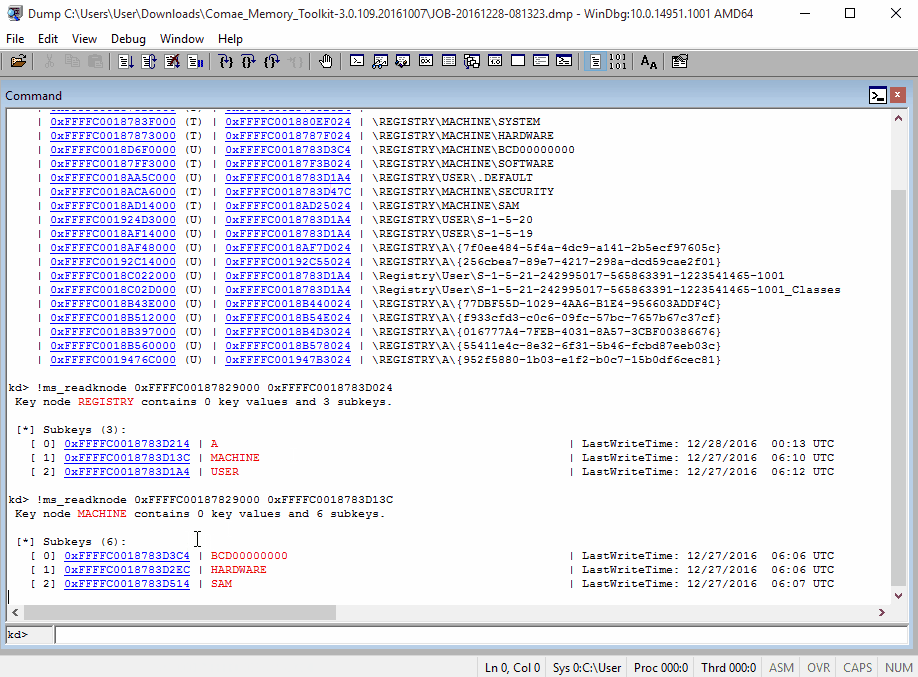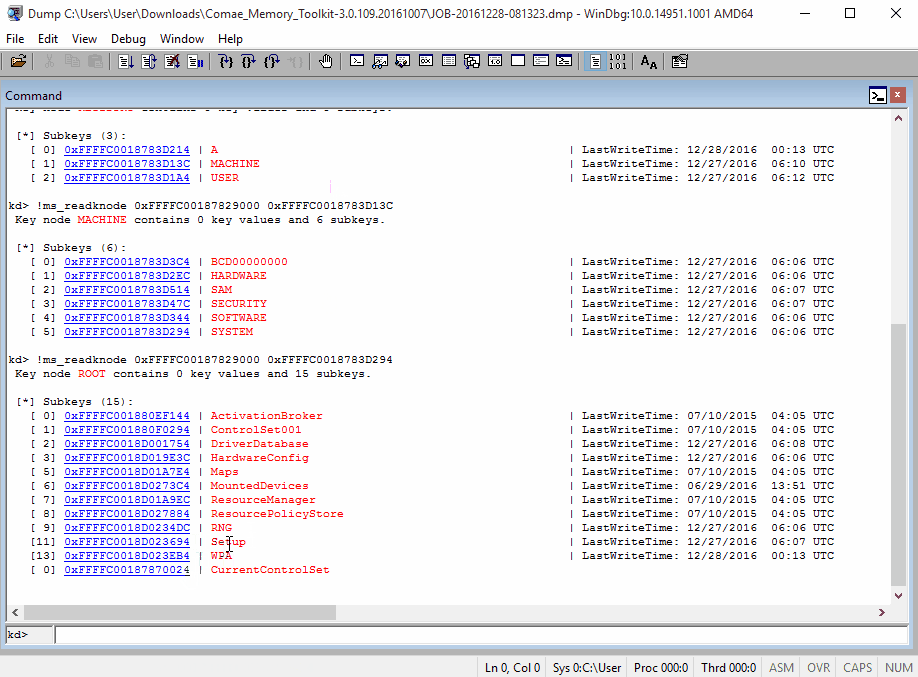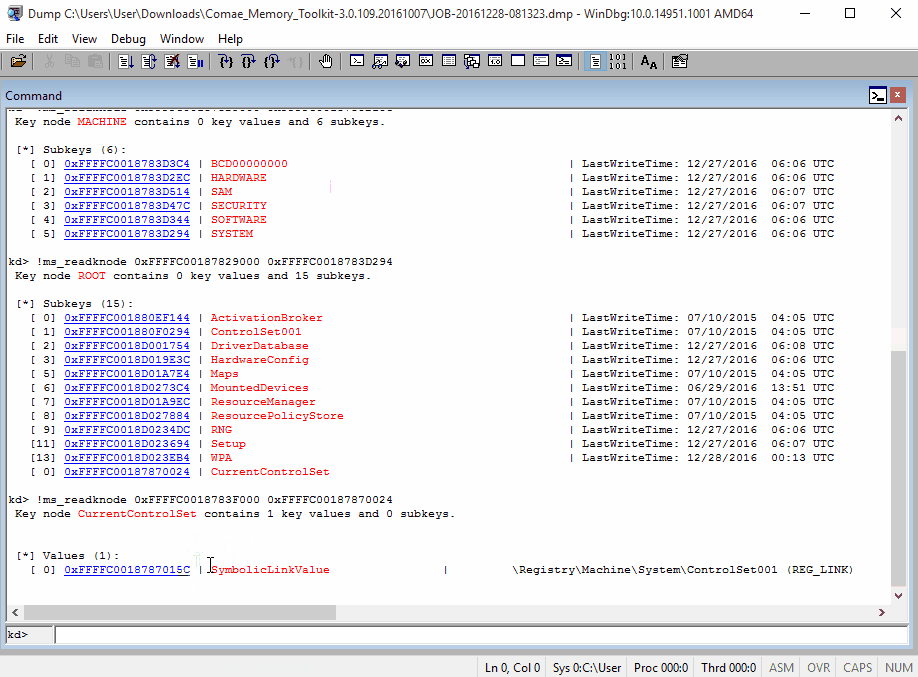
binary-analysiseducationforensics+7
33 months ago
SwishDbgExt preview

SwishDbgExt

GitHubmagnetforensics/swishdbgext

Incident Response & Digital Forensics Debugging Extension
debuggersdigital-forensicsincident-response+3
3997 years ago
NotSecDrv preview

NotSecDrv

GitHubalonhr/notsecdrv

A PoC for CVE-2018-7249

binary-exploitationeducationexploitation+3
151 year ago