

SwishDbgExt
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
debuggersdigital-forensicsincident-response+3
3997 years ago
magnetforensics/swishdbgextIncident Response & Digital Forensics Debugging Extension
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
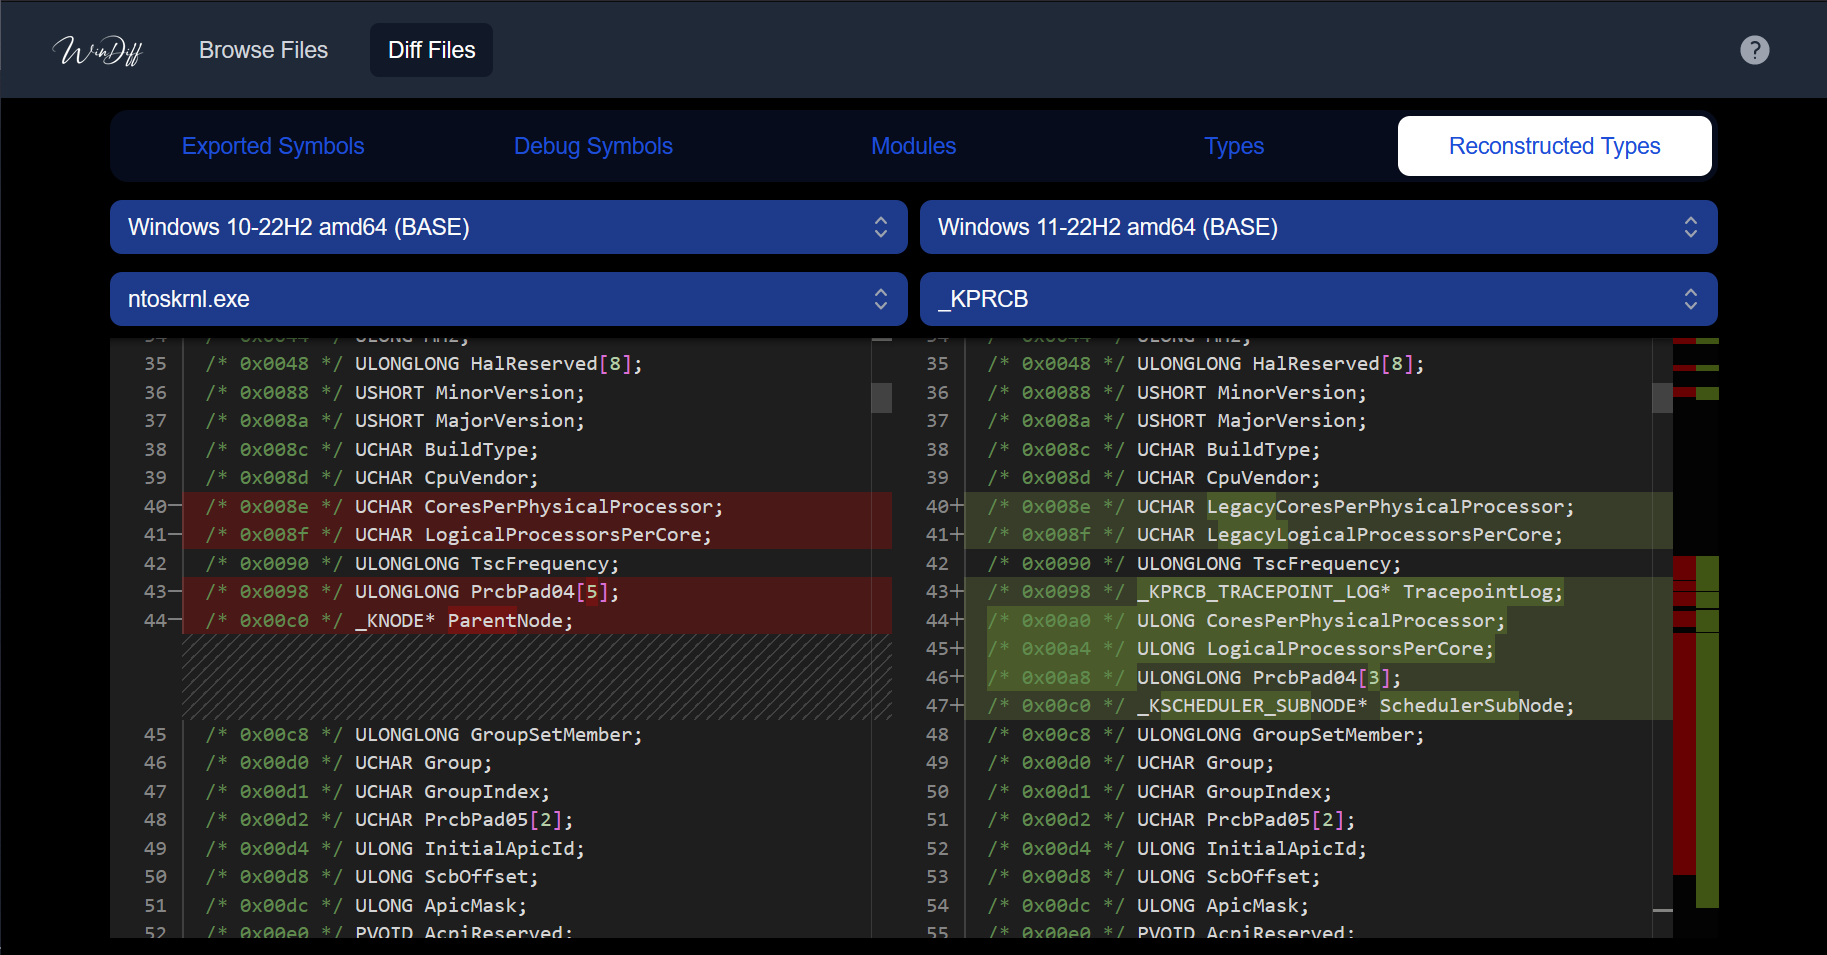 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 hackinglz/extracteddefender
Collection of extracted Microsoft Defender data for security research purposes
 ricardojoserf/p-invoke.net
Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
 witherornot/warbird-docs
Documentation of Microsoft's Warbird obfuscation
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
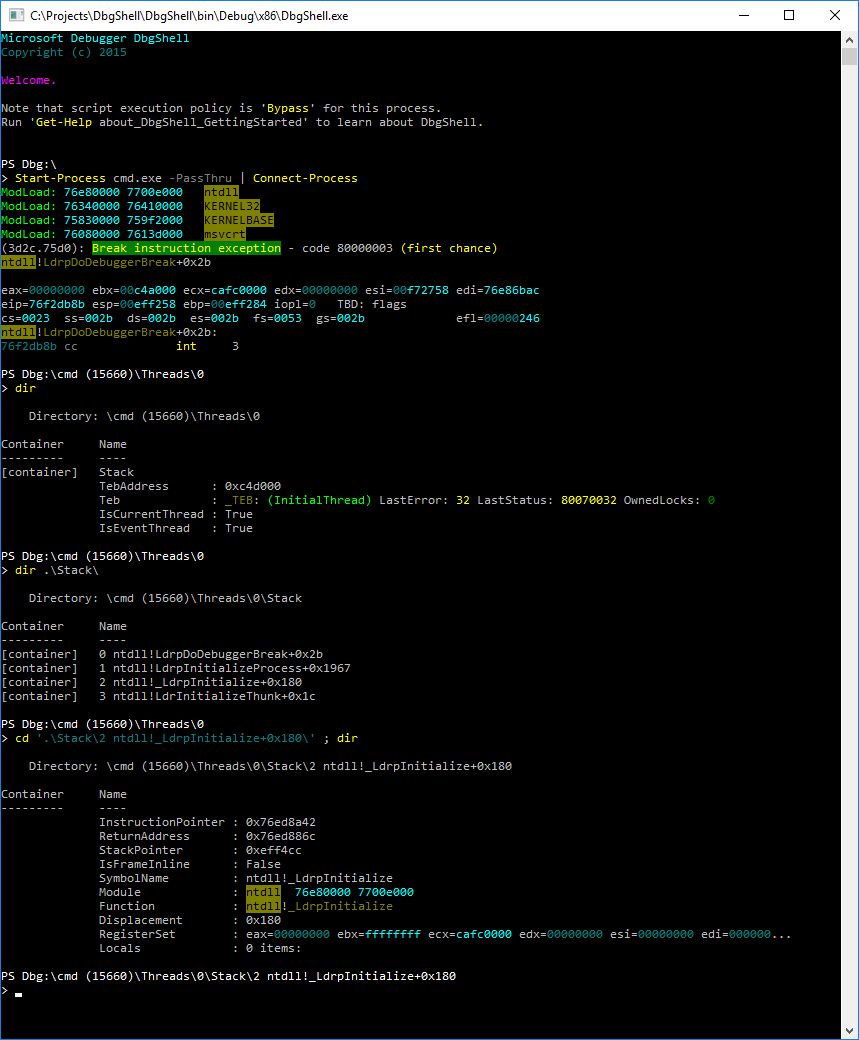 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.
 fboldewin/com-code-helper
Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio