
IOSSecuritySuite
 securing/iossecuritysuite
iOS platform security & anti-tampering Swift library
educationios-securitymobile-security+1
2.7k2 months ago
securing/iossecuritysuiteiOS platform security & anti-tampering Swift library
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.
 malrev/abd
Course materials for Advanced Binary Deobfuscation by NTT Secure Platform Laboratories
 smtimesiwndr/gdid-reversal
Reverse-engineered analysis of Microsoft's Global Device Identifier (GDID) revealing its generation as a server-assigned MSA Device PUID, storage in…
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 angr/angr
A powerful and user-friendly binary analysis platform!
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
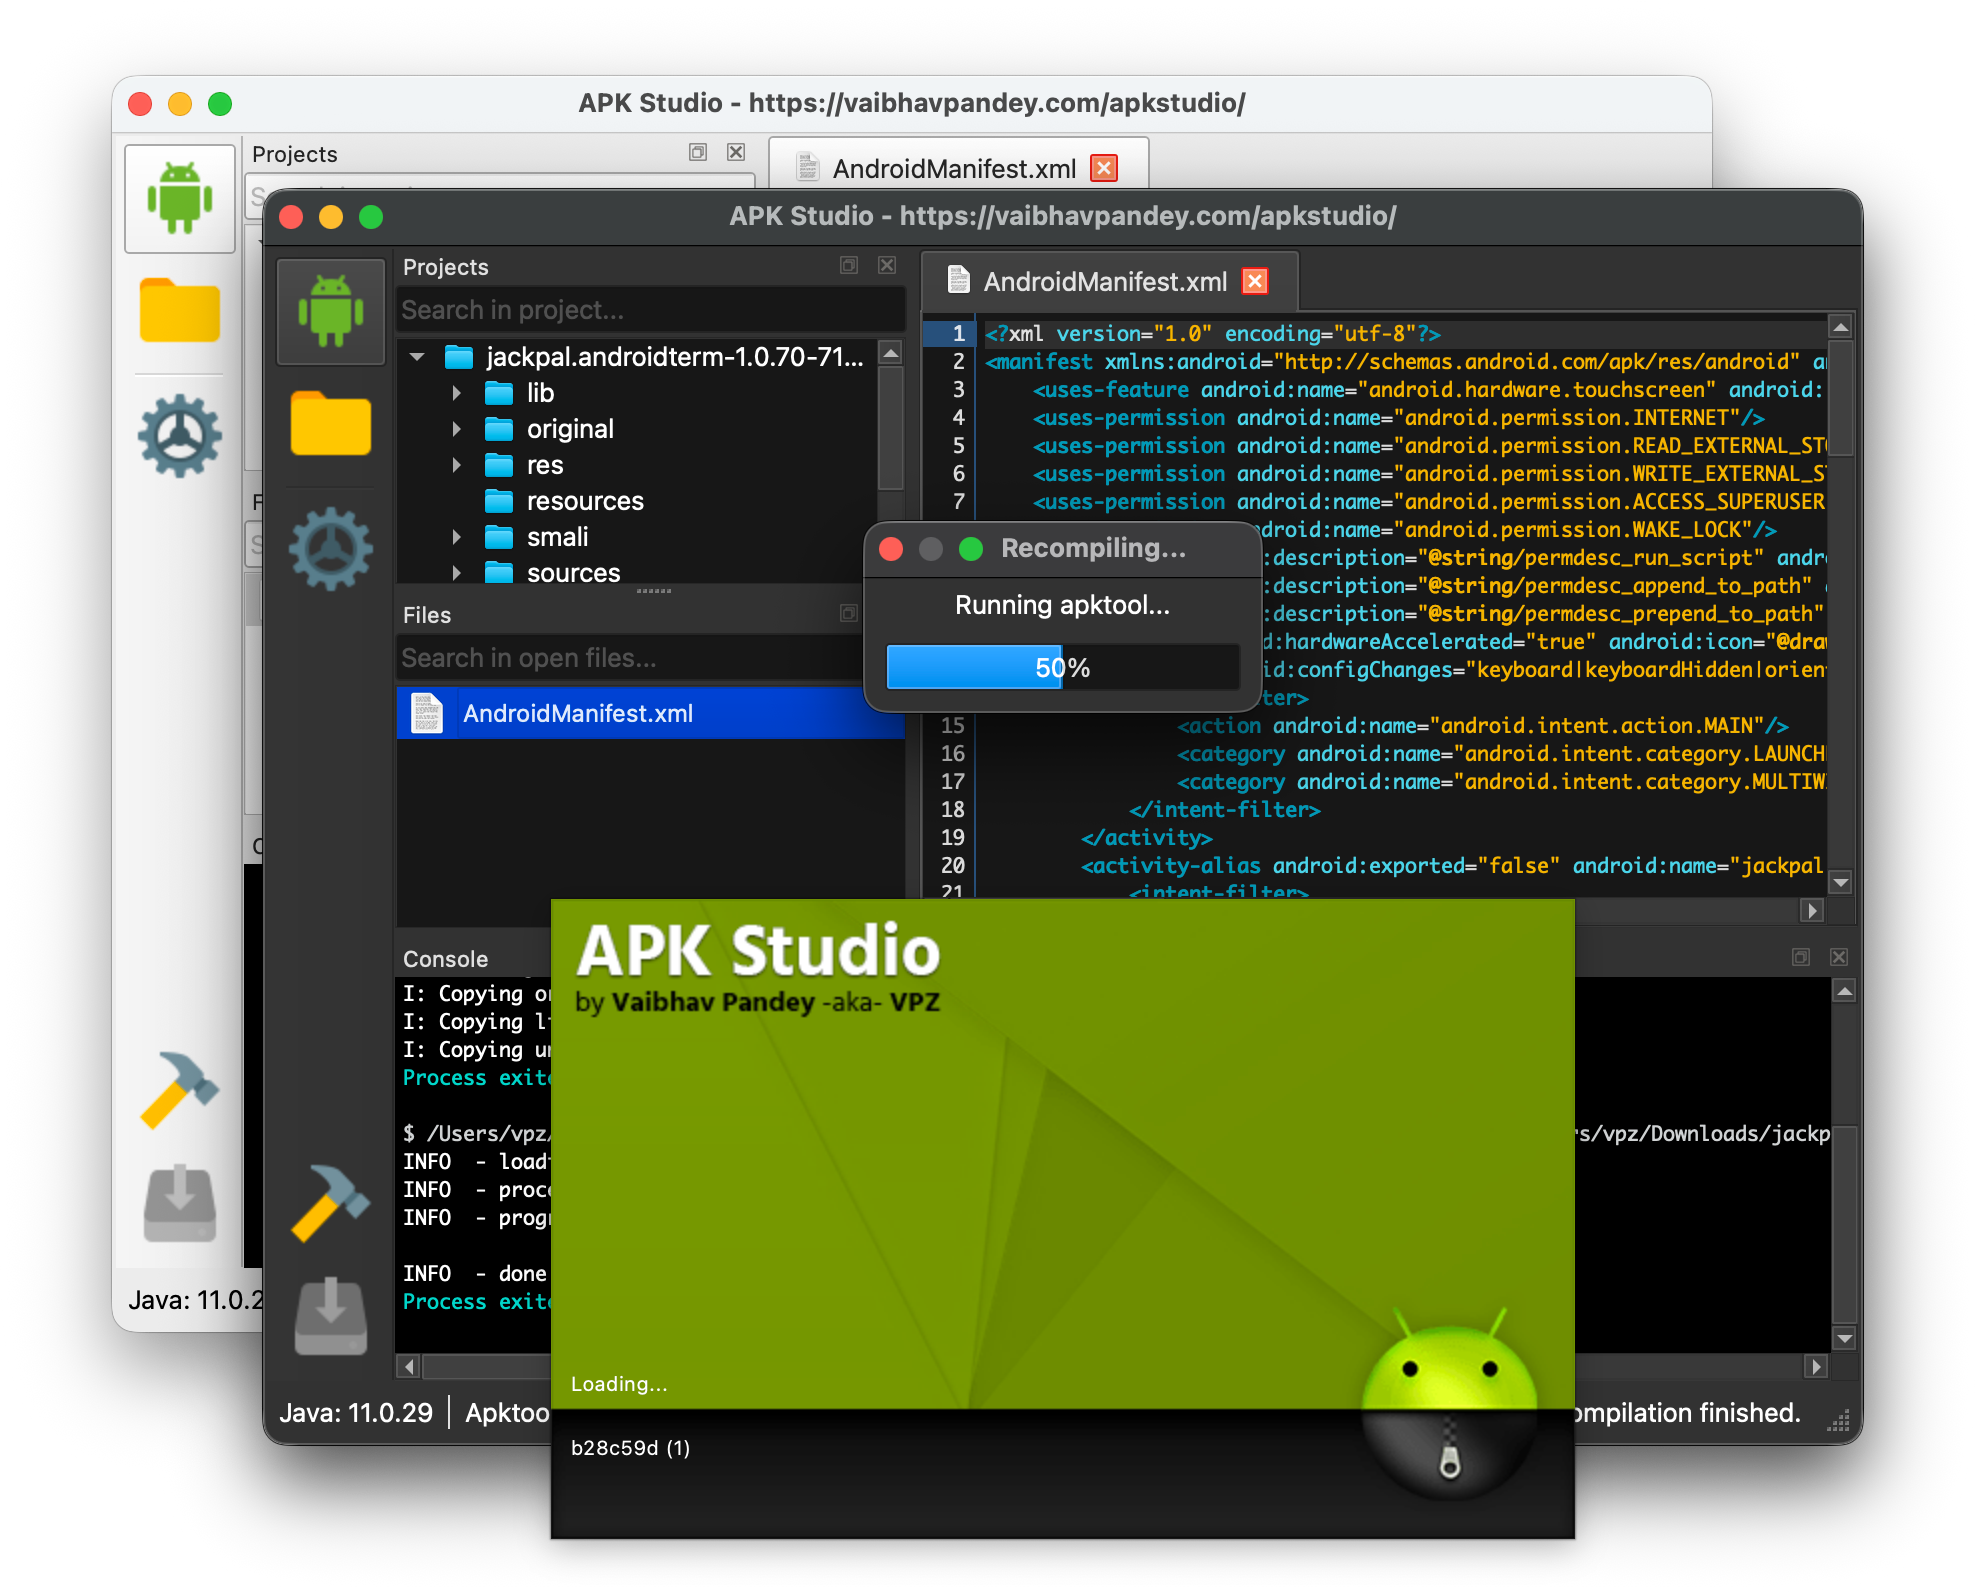 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
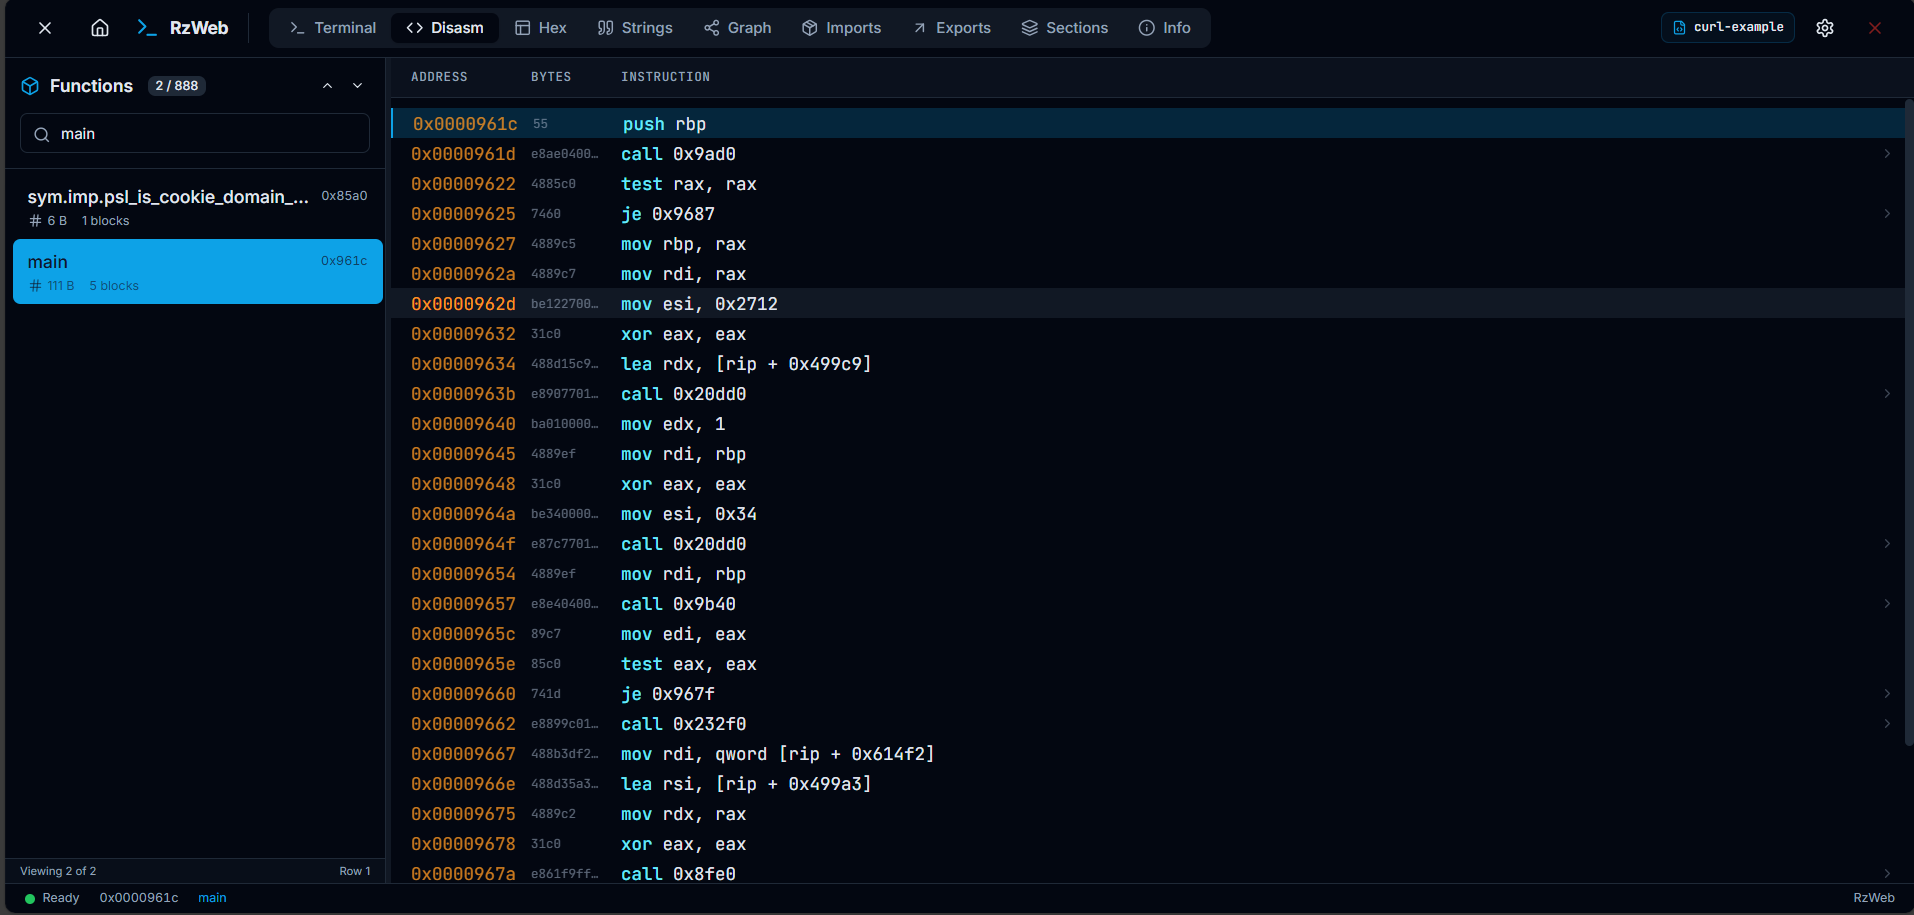 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
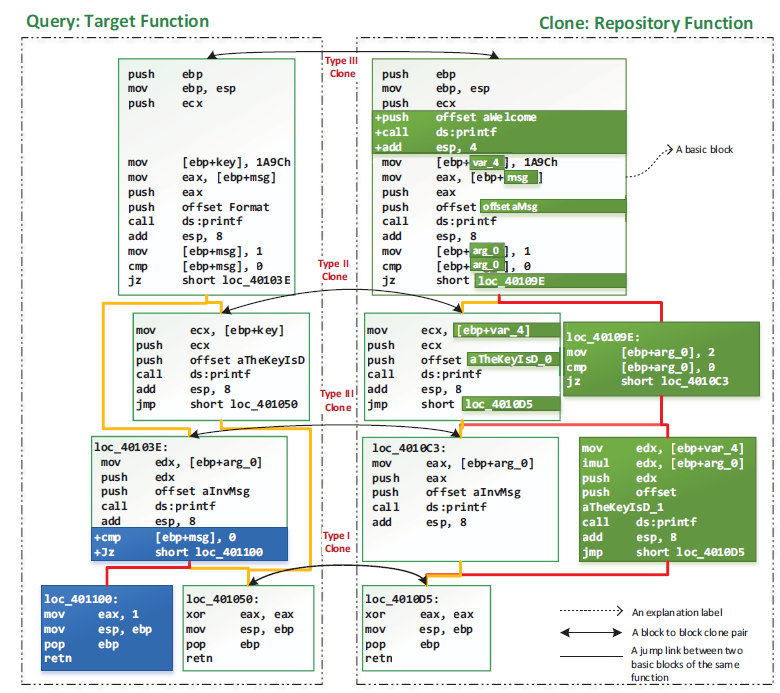 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
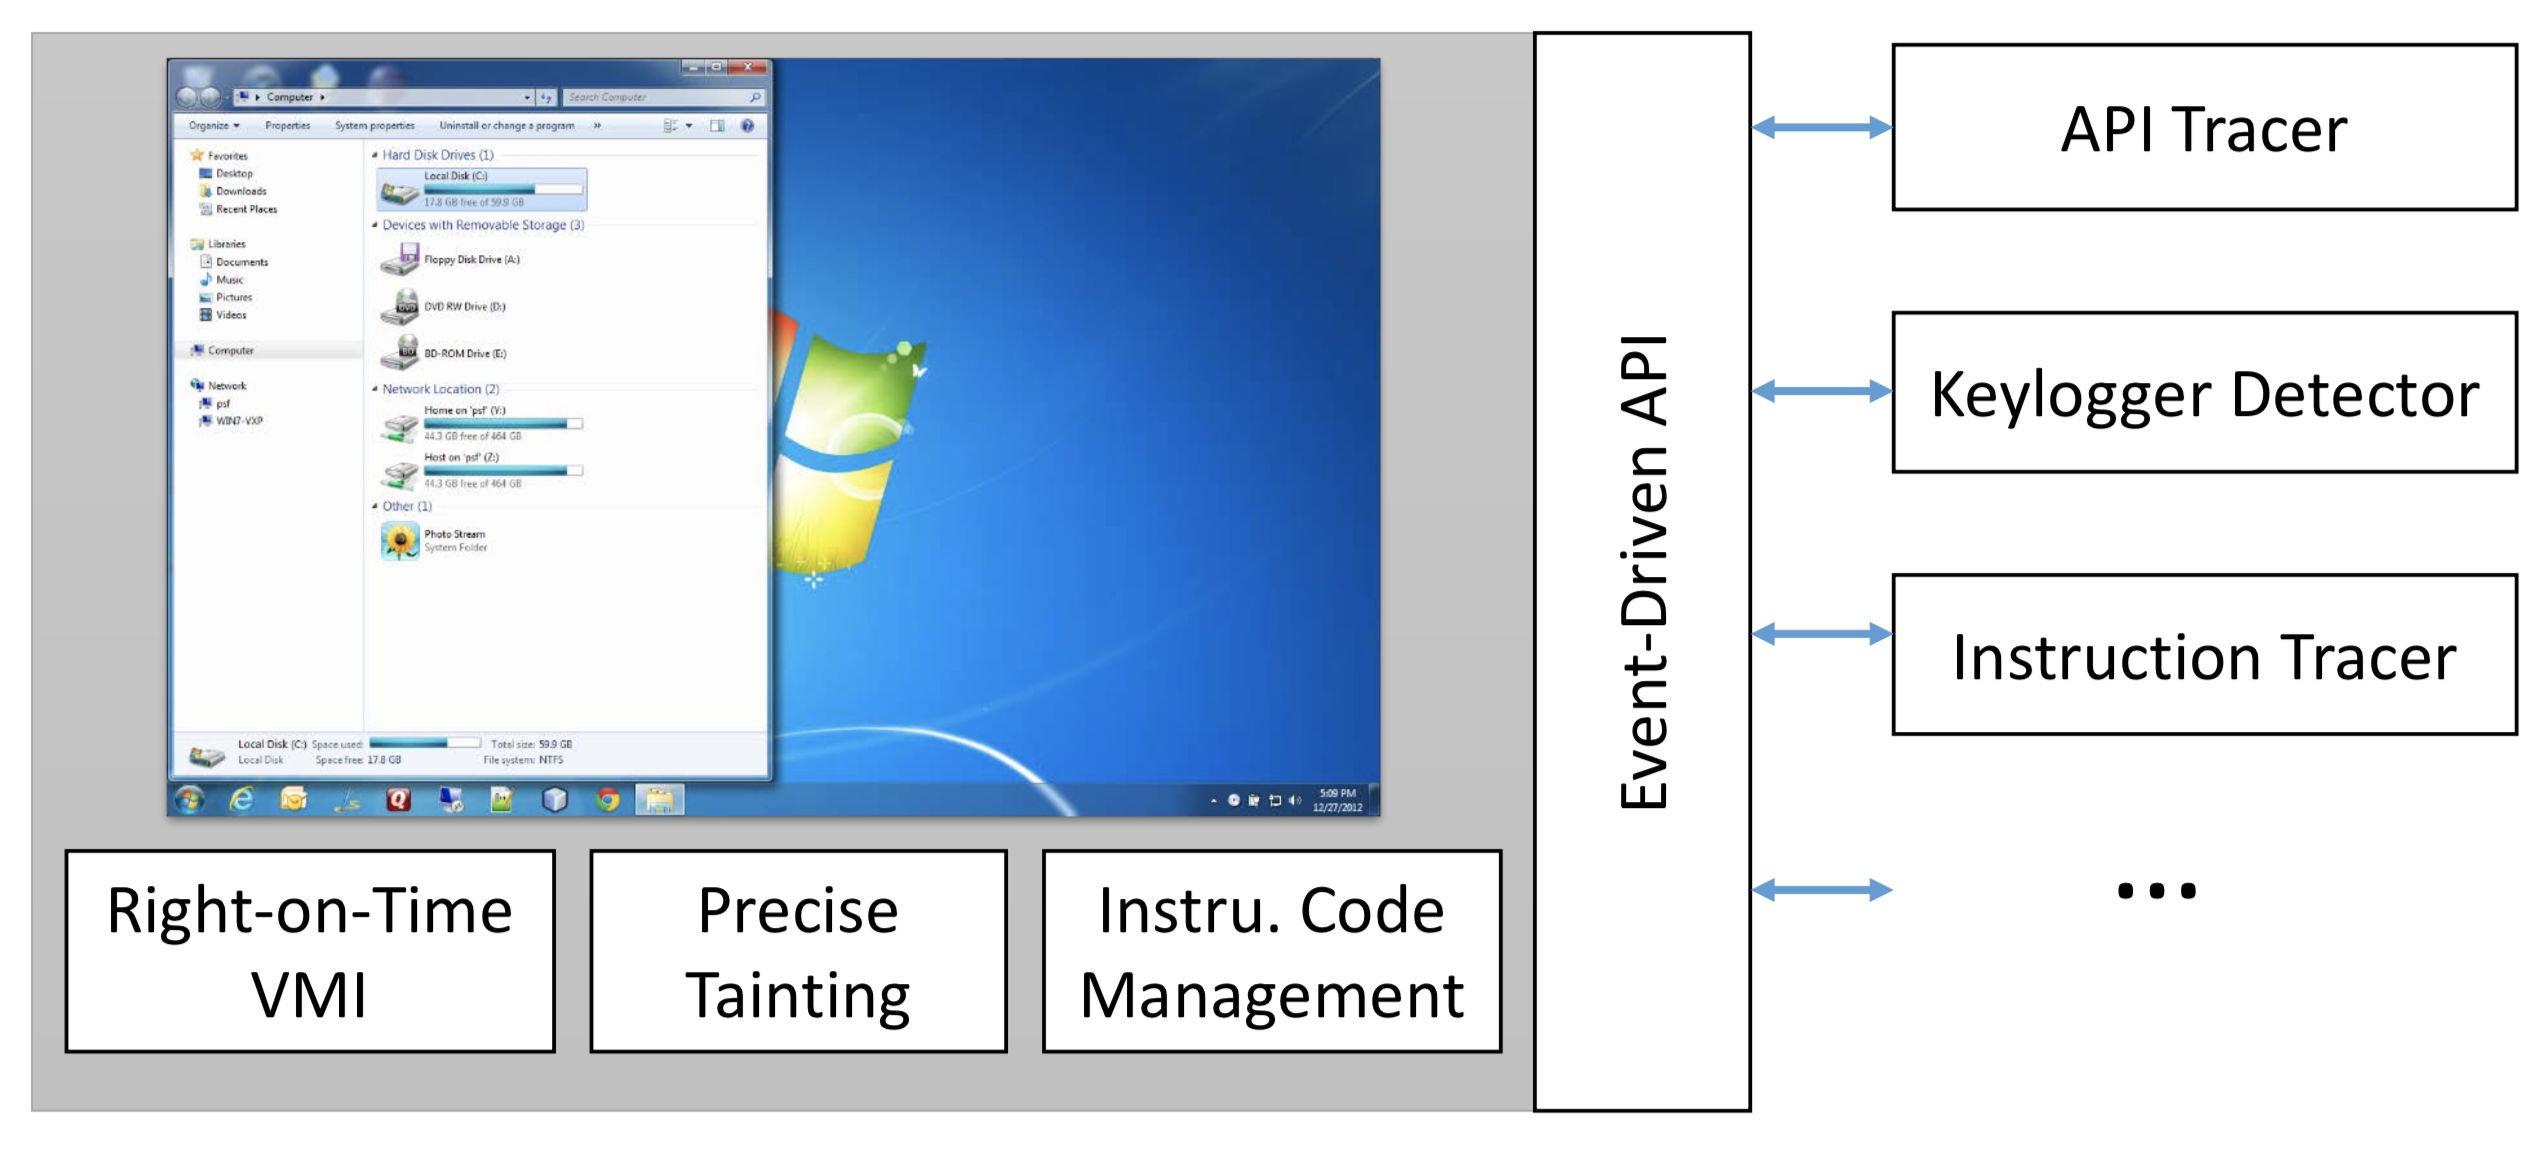 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
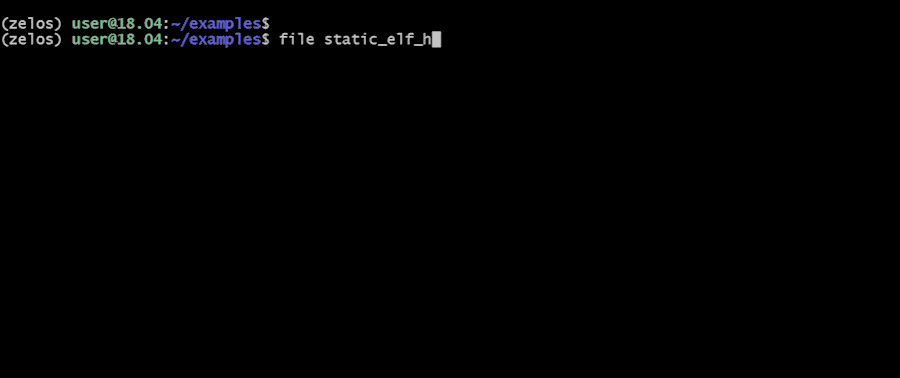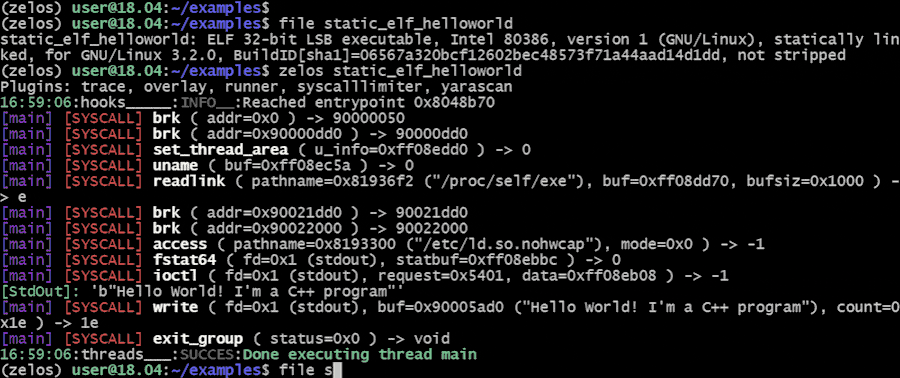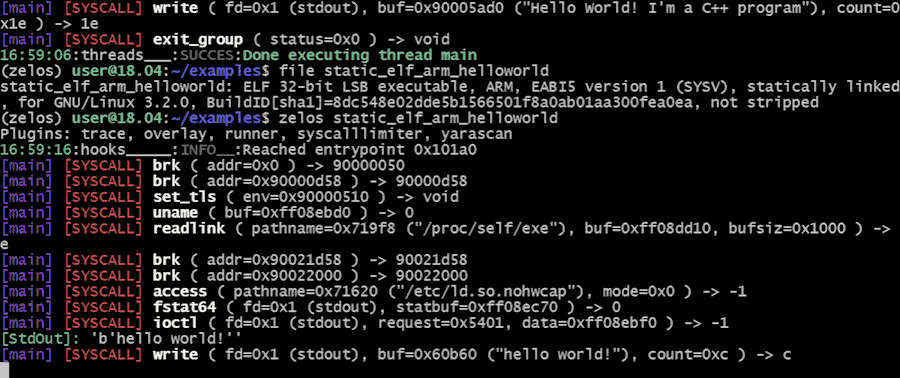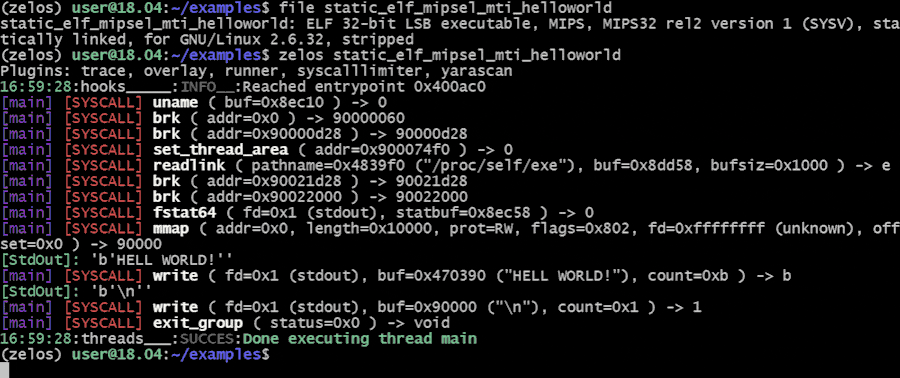 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.