
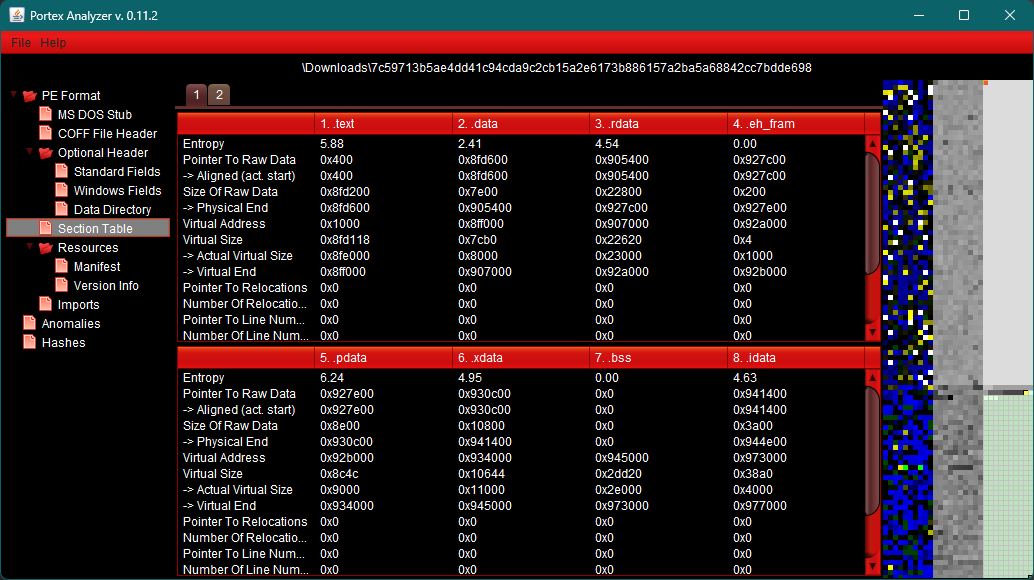
PortexAnalyzerGUI
 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
binary-analysisforensicshash-analysis+3
151
struppigel/portexanalyzerguiGraphical interface for PortEx, a Portable Executable and Malware Analysis Library
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 matheuzsecurity/nullsection
ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 x86byte/obfusk8
Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
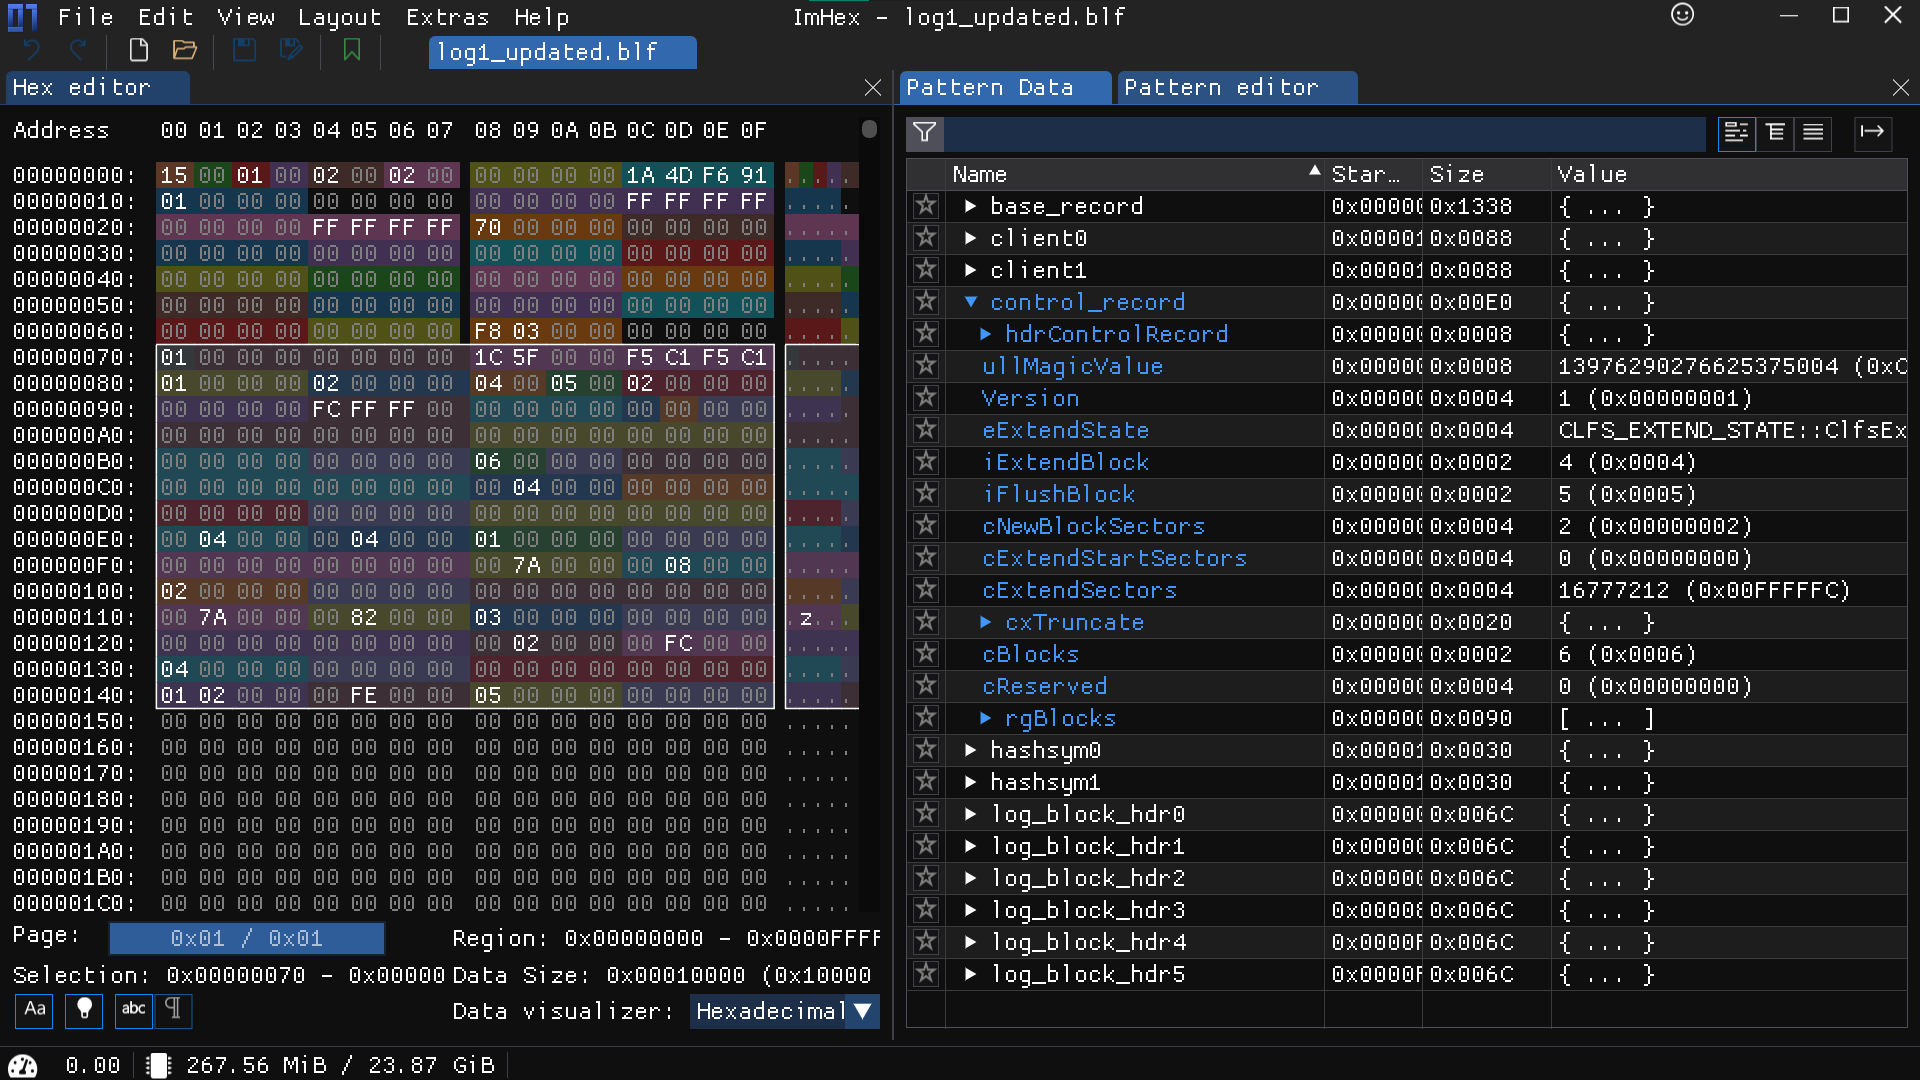 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 mandiant/dncil
The FLARE team's open-source library to disassemble Common Intermediate Language (CIL) instructions.
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.