
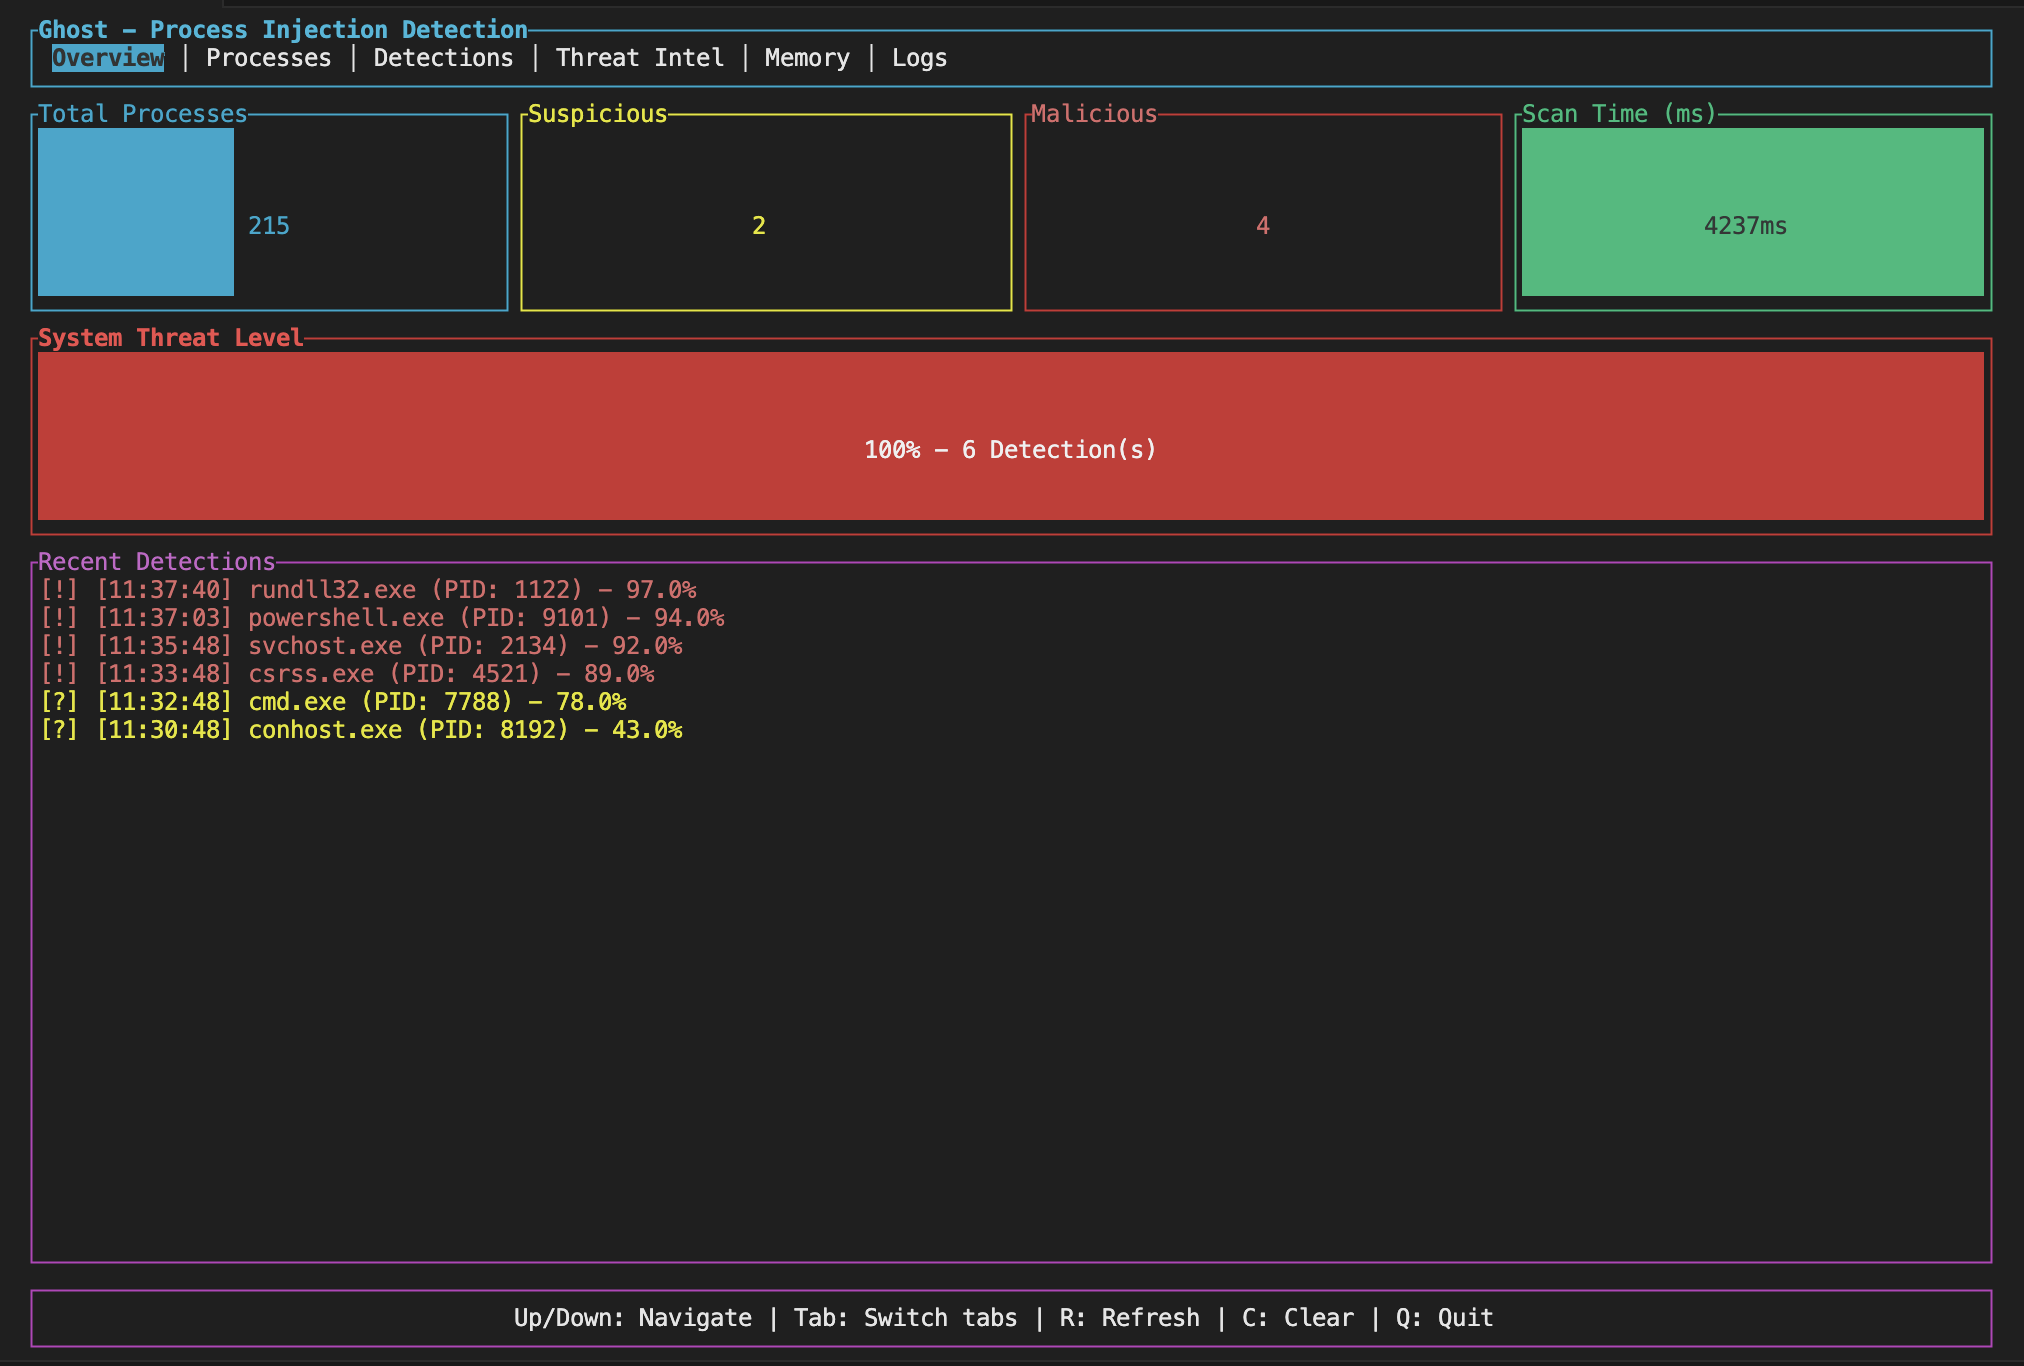
ghost
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
393
pandaadir05/ghostDetects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…