

CVE-2025-4275
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
binary-analysiseducationexploitation+5
themalwareguardian/cve-2025-4275Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
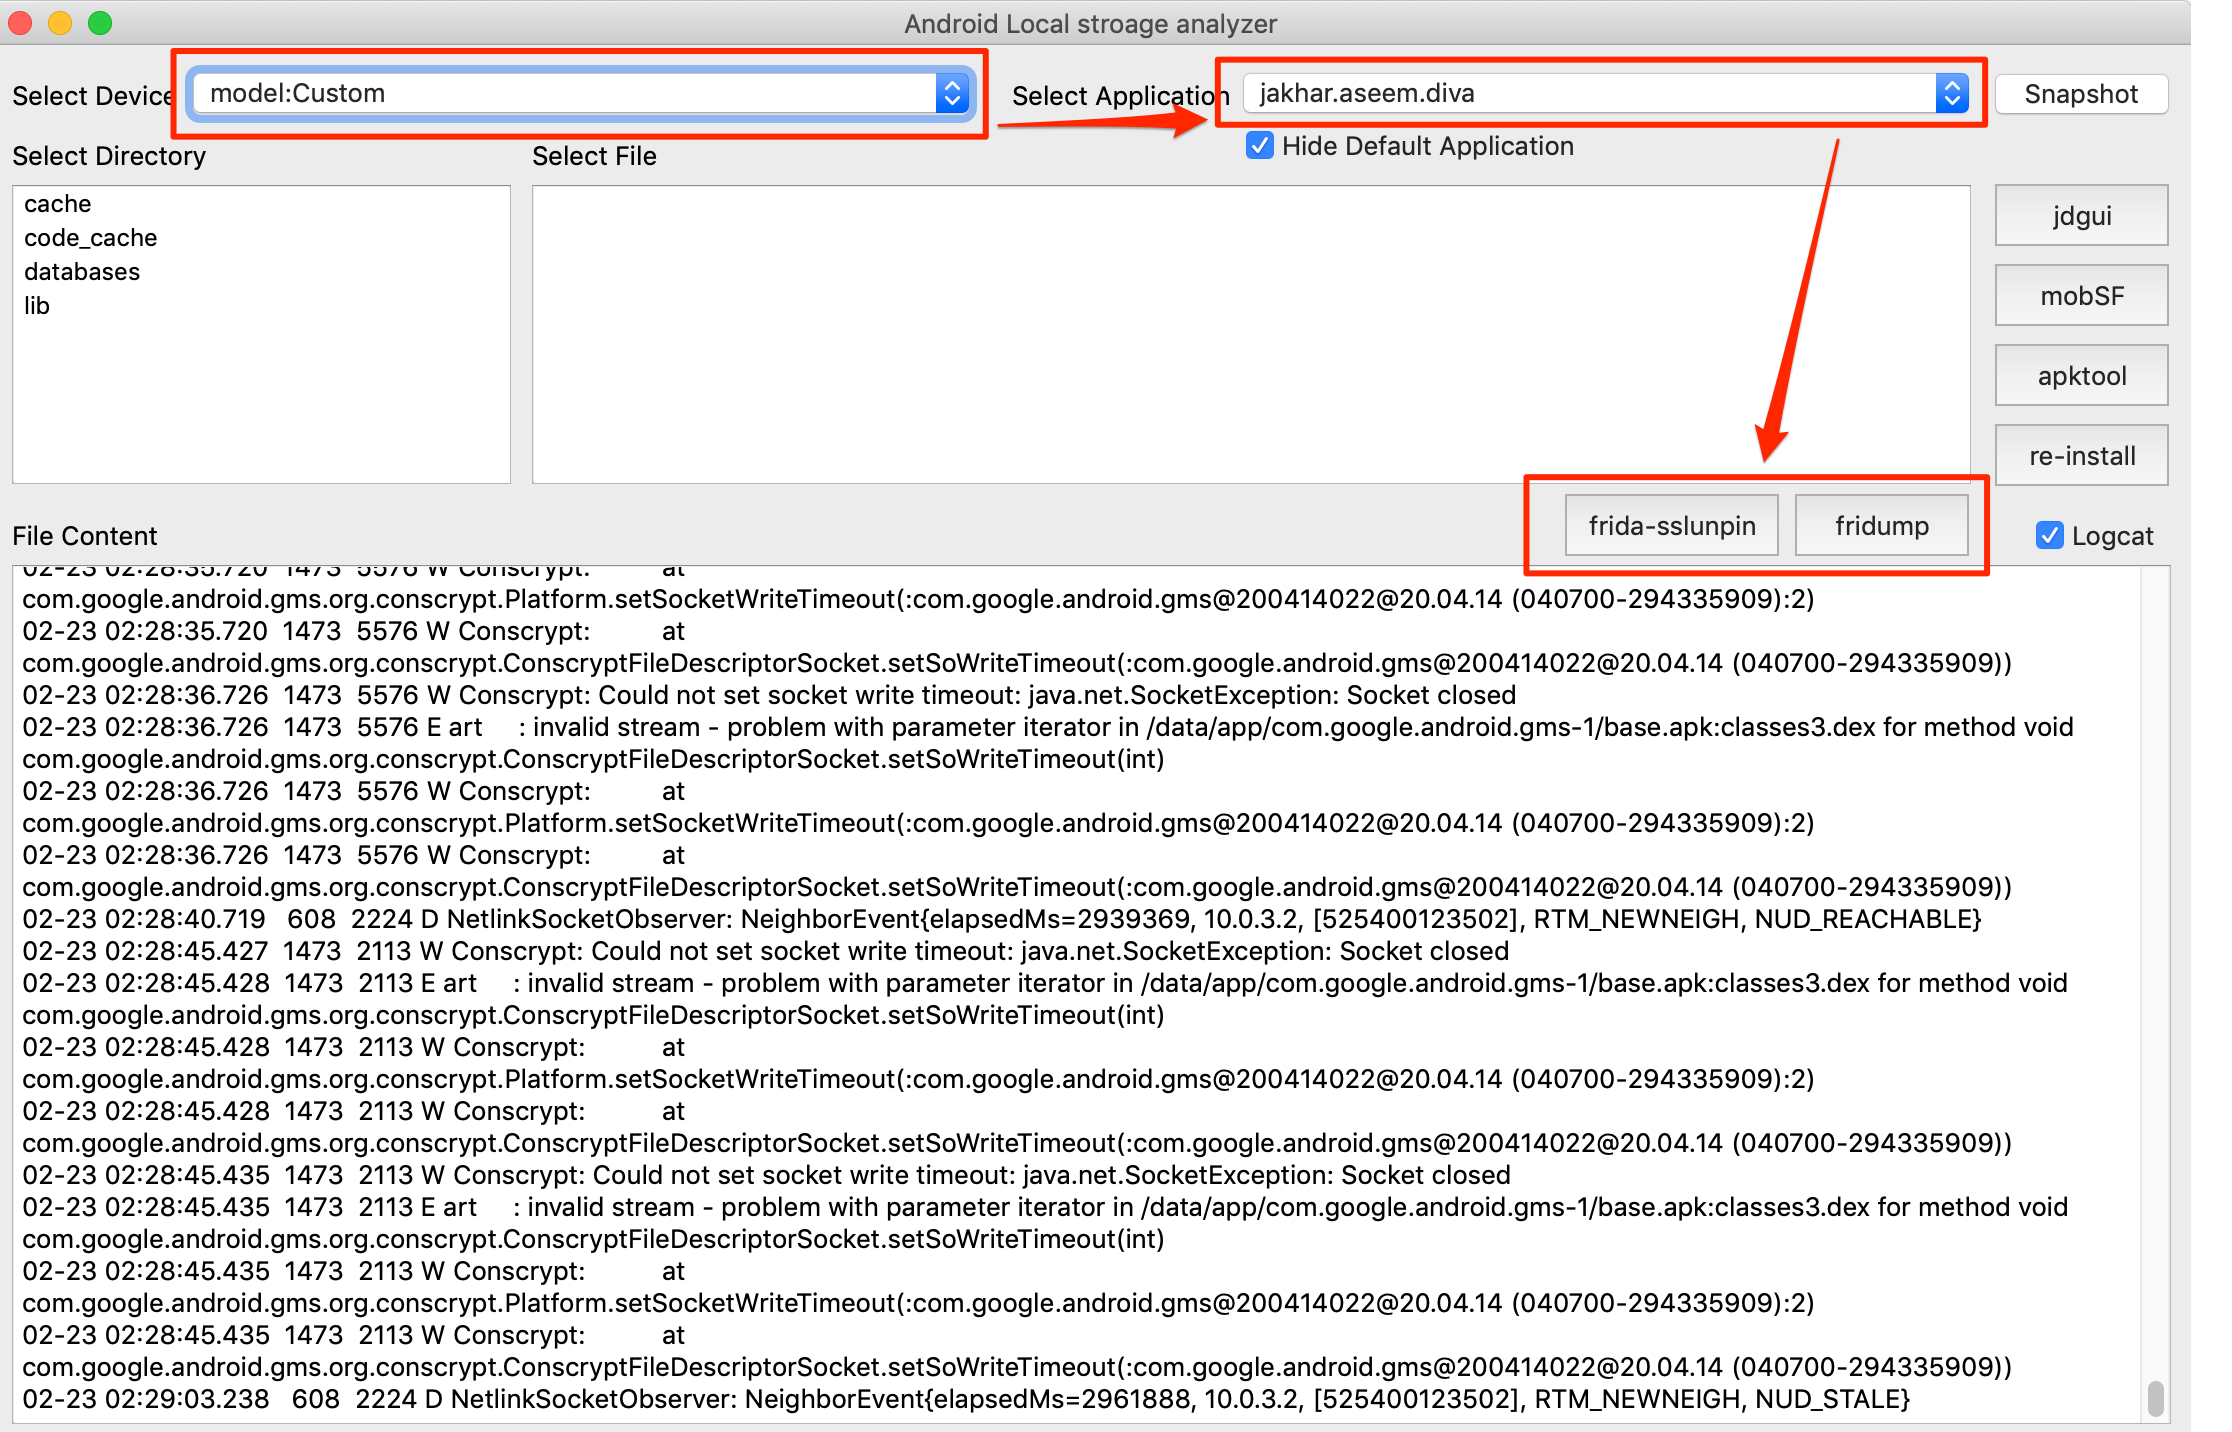 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 maoabc/nmmp
dex-vm used to protect the android classes.dex file
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 dissectmalware/xlmmacrodeobfuscator
Extract and Deobfuscate XLM macros (a.k.a Excel 4.0 Macros)
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
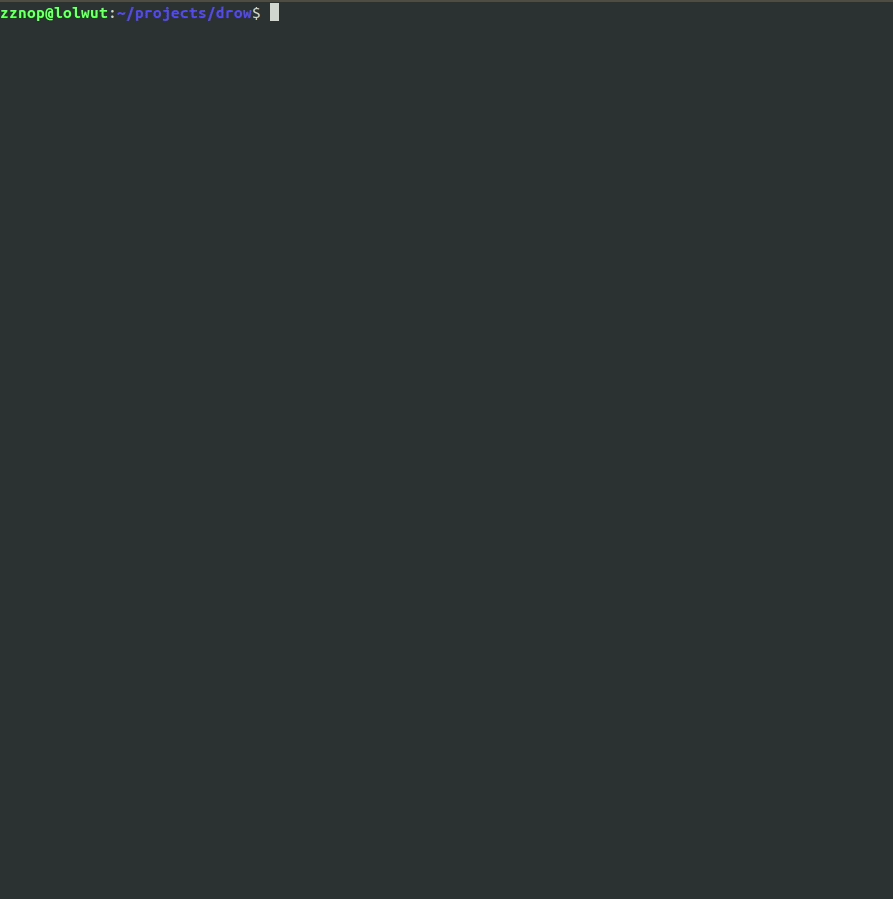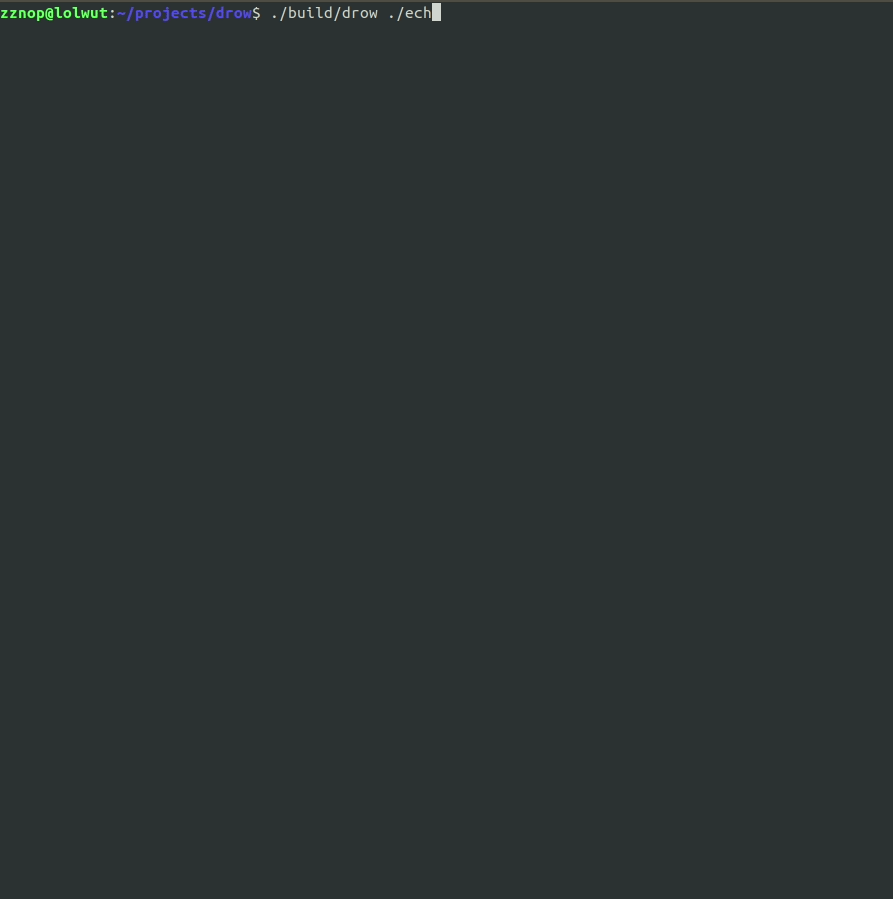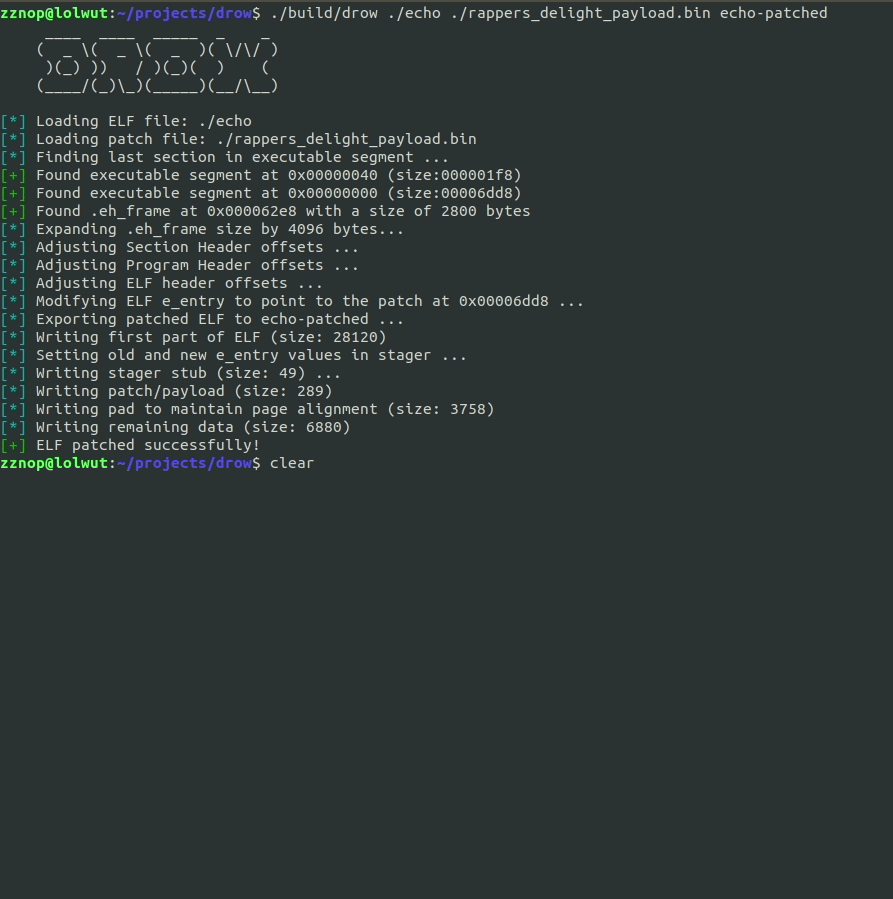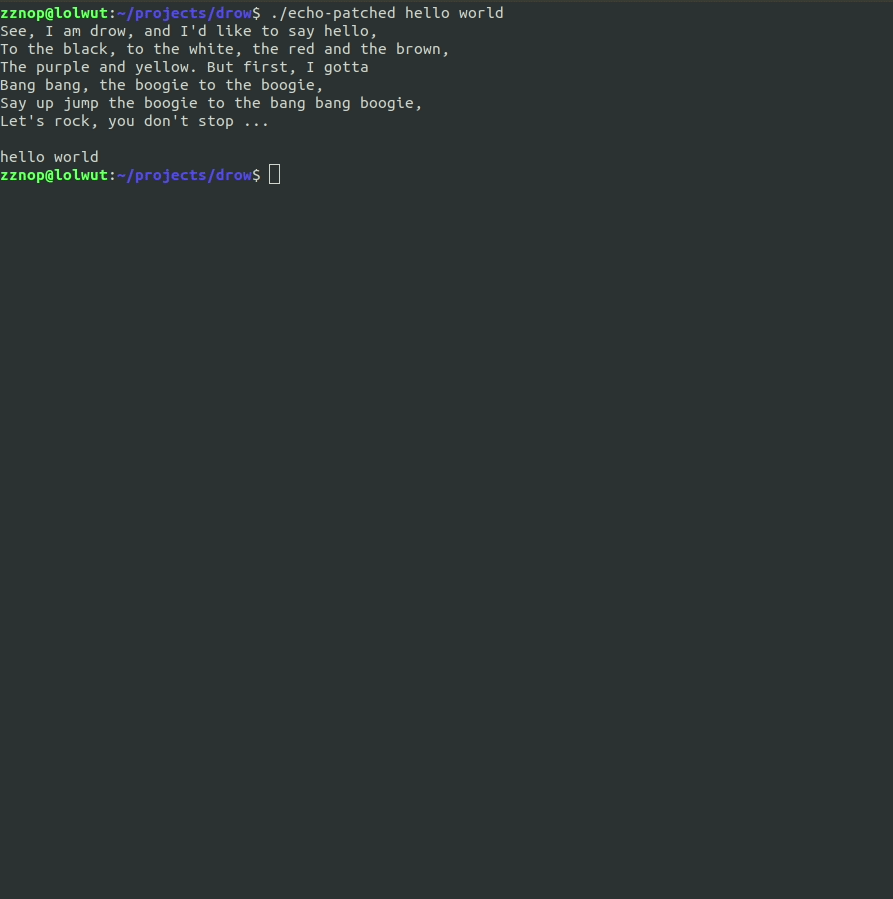 zznop/drow
Injects code into ELF executables post-build
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 nickcano/xenoscan
Open source memory scanner written in C++