
gdbgui
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
binary-analysisdebuggersreverse-engineering+1
10.3k
cs01/gdbguiBrowser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…
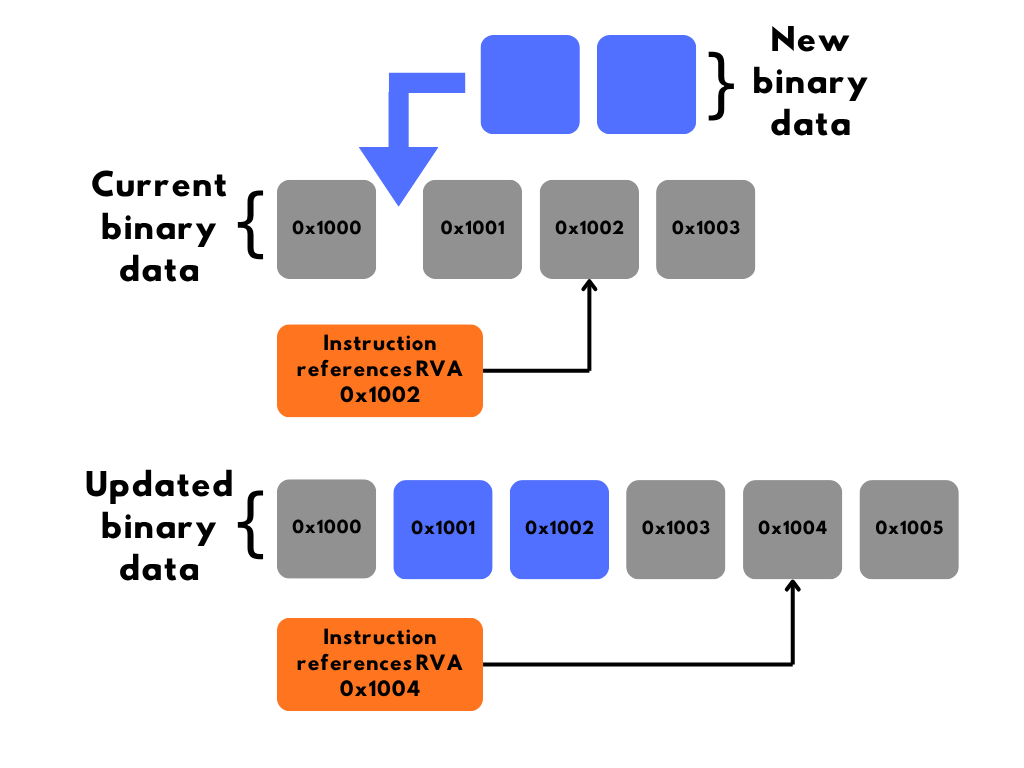 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
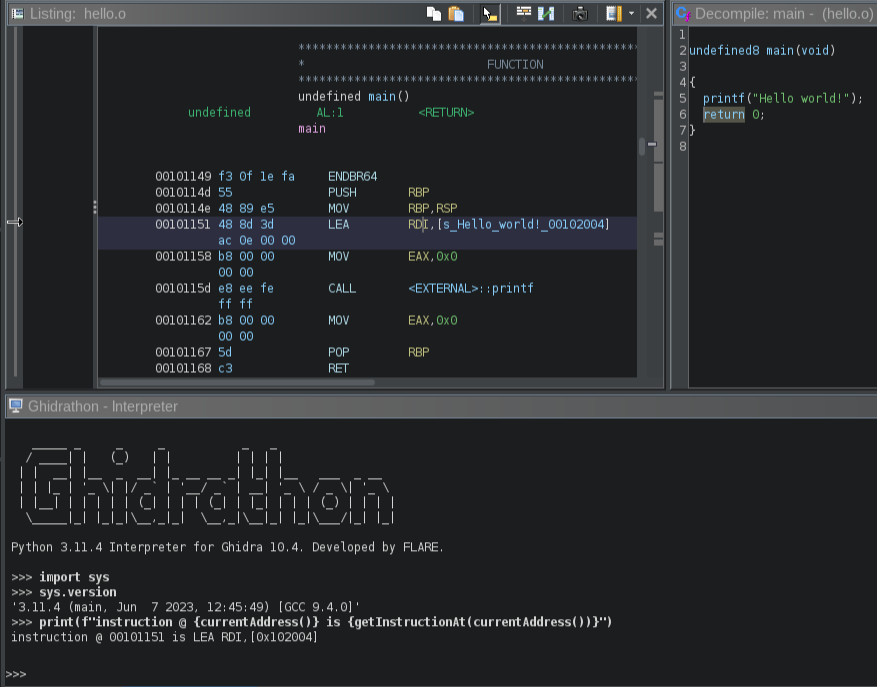 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
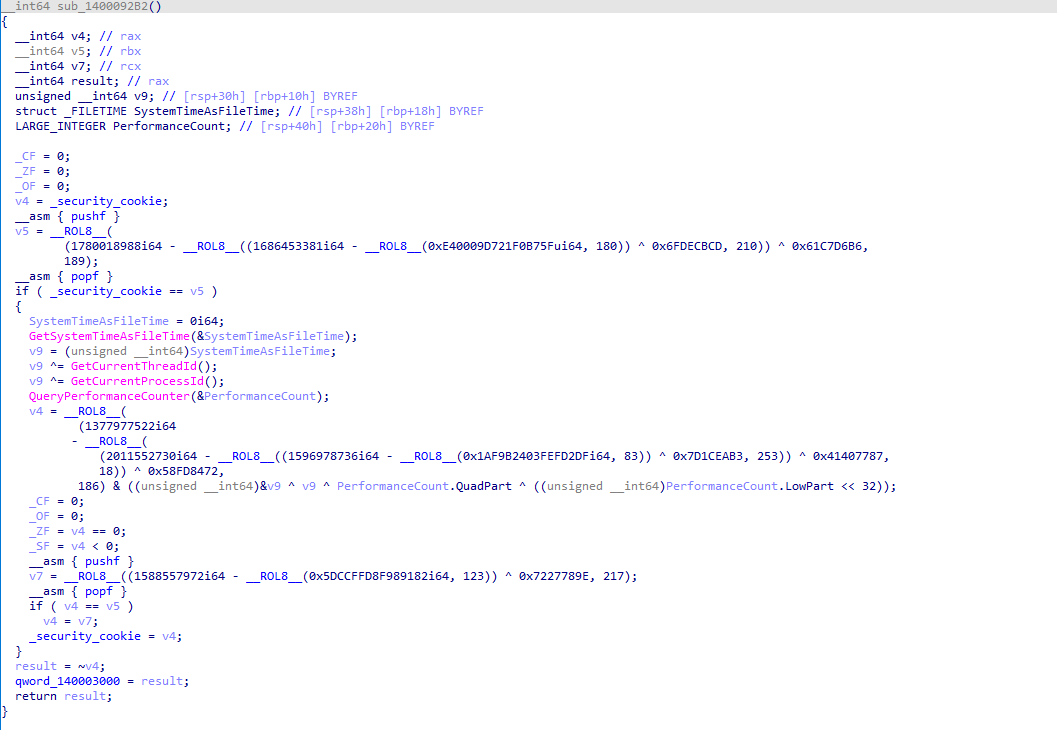 weak1337/alcatraz
x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
 eset/ipyida
IPython console integration for IDA Pro
 therealdreg/masm32-kernel-programming
masm32 kernel programming, drivers, tutorials, examples, and tools (credits Four-F)
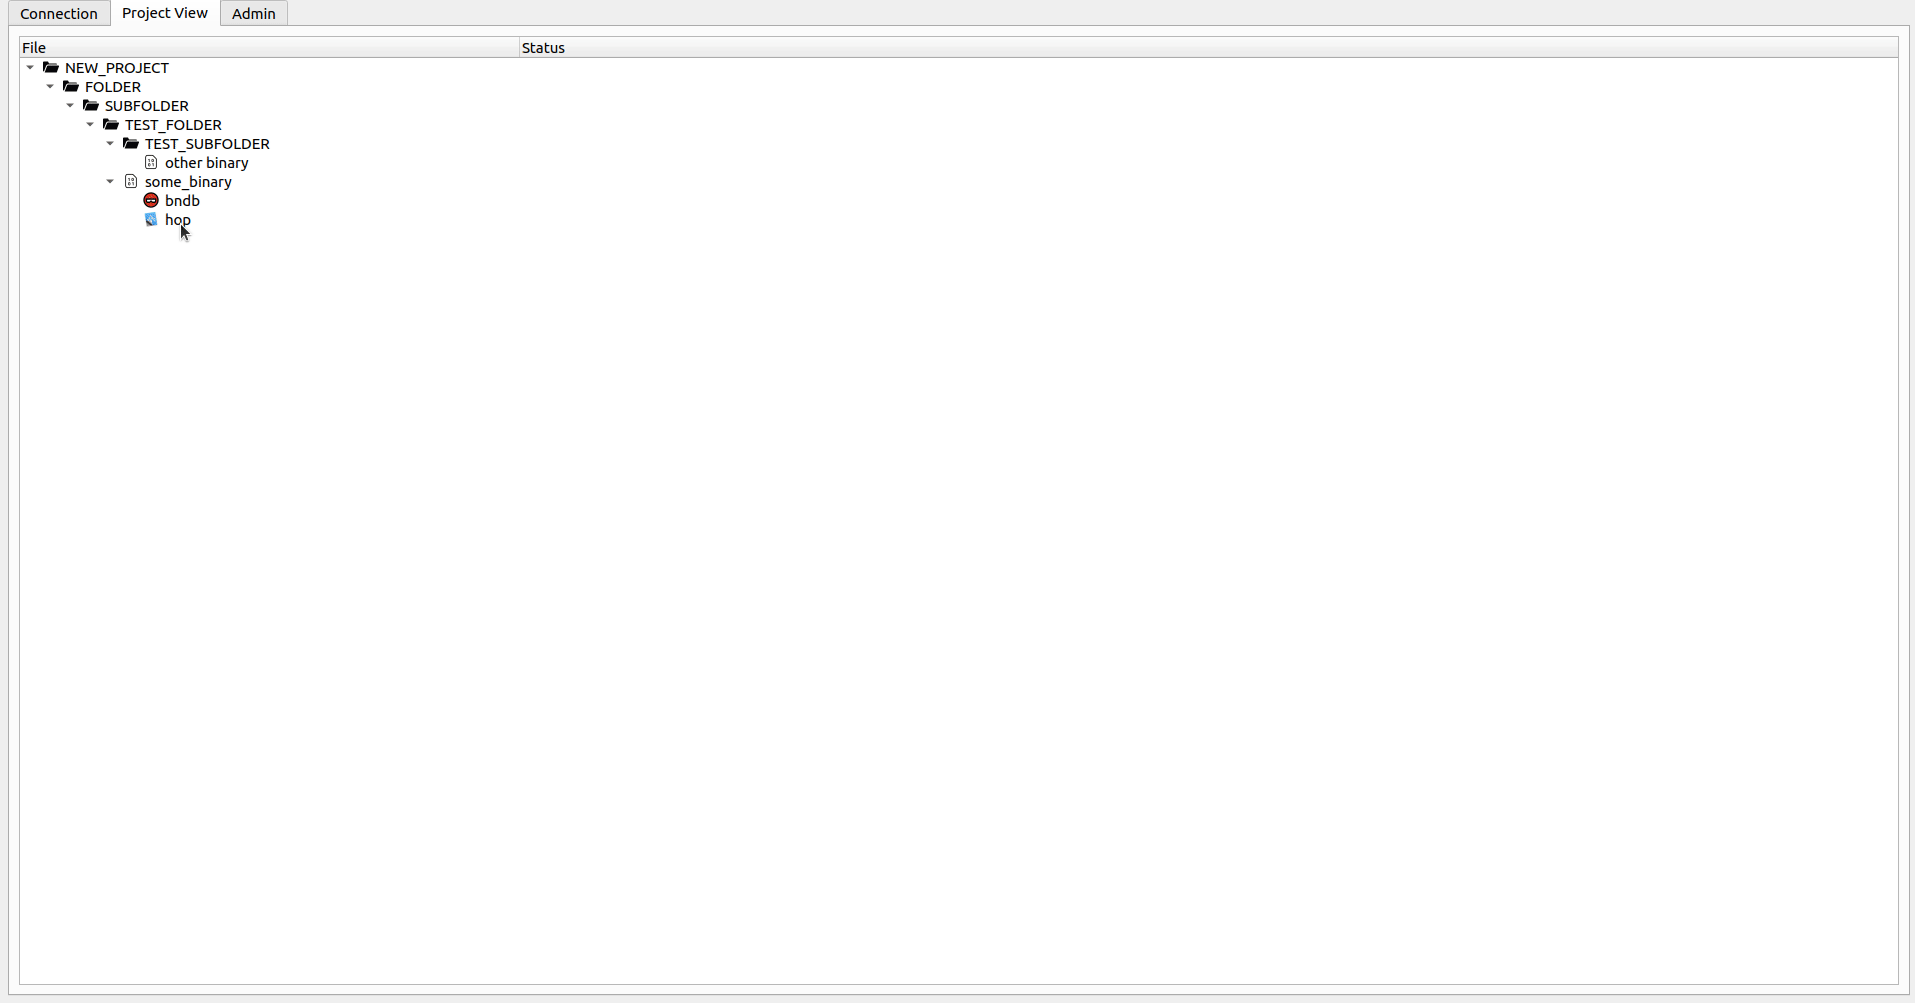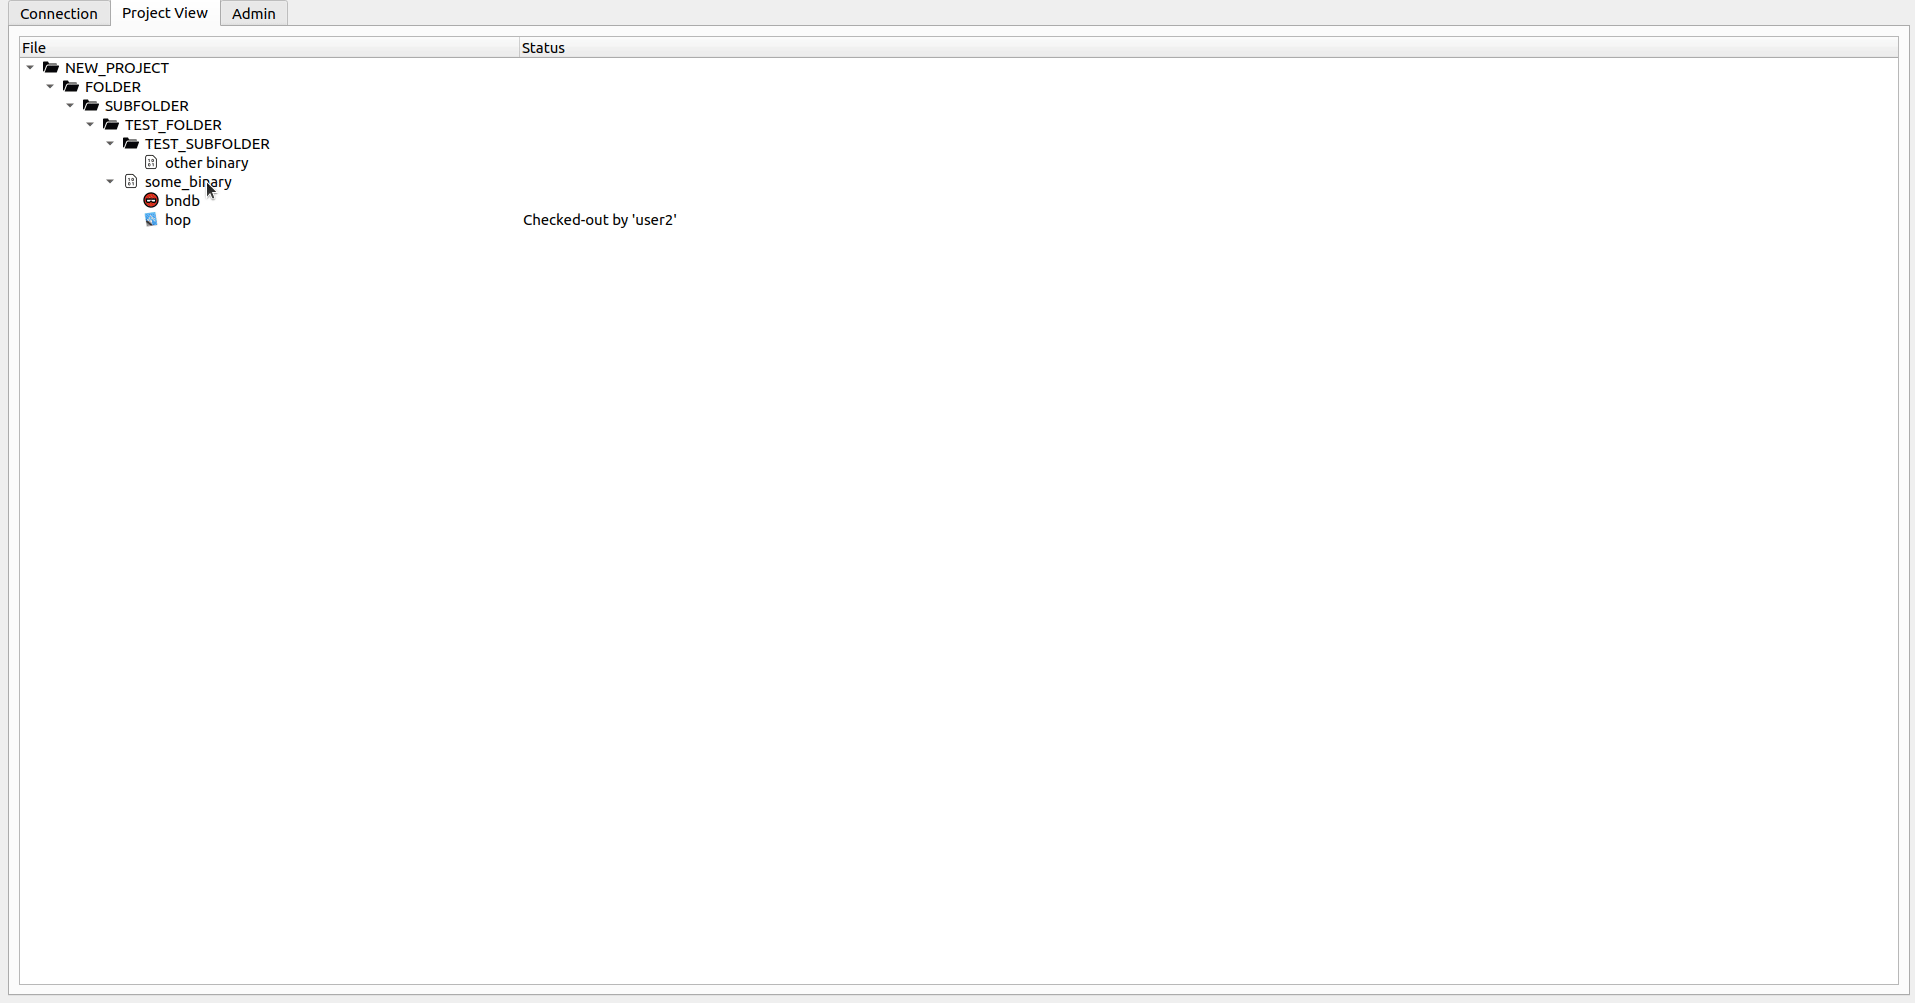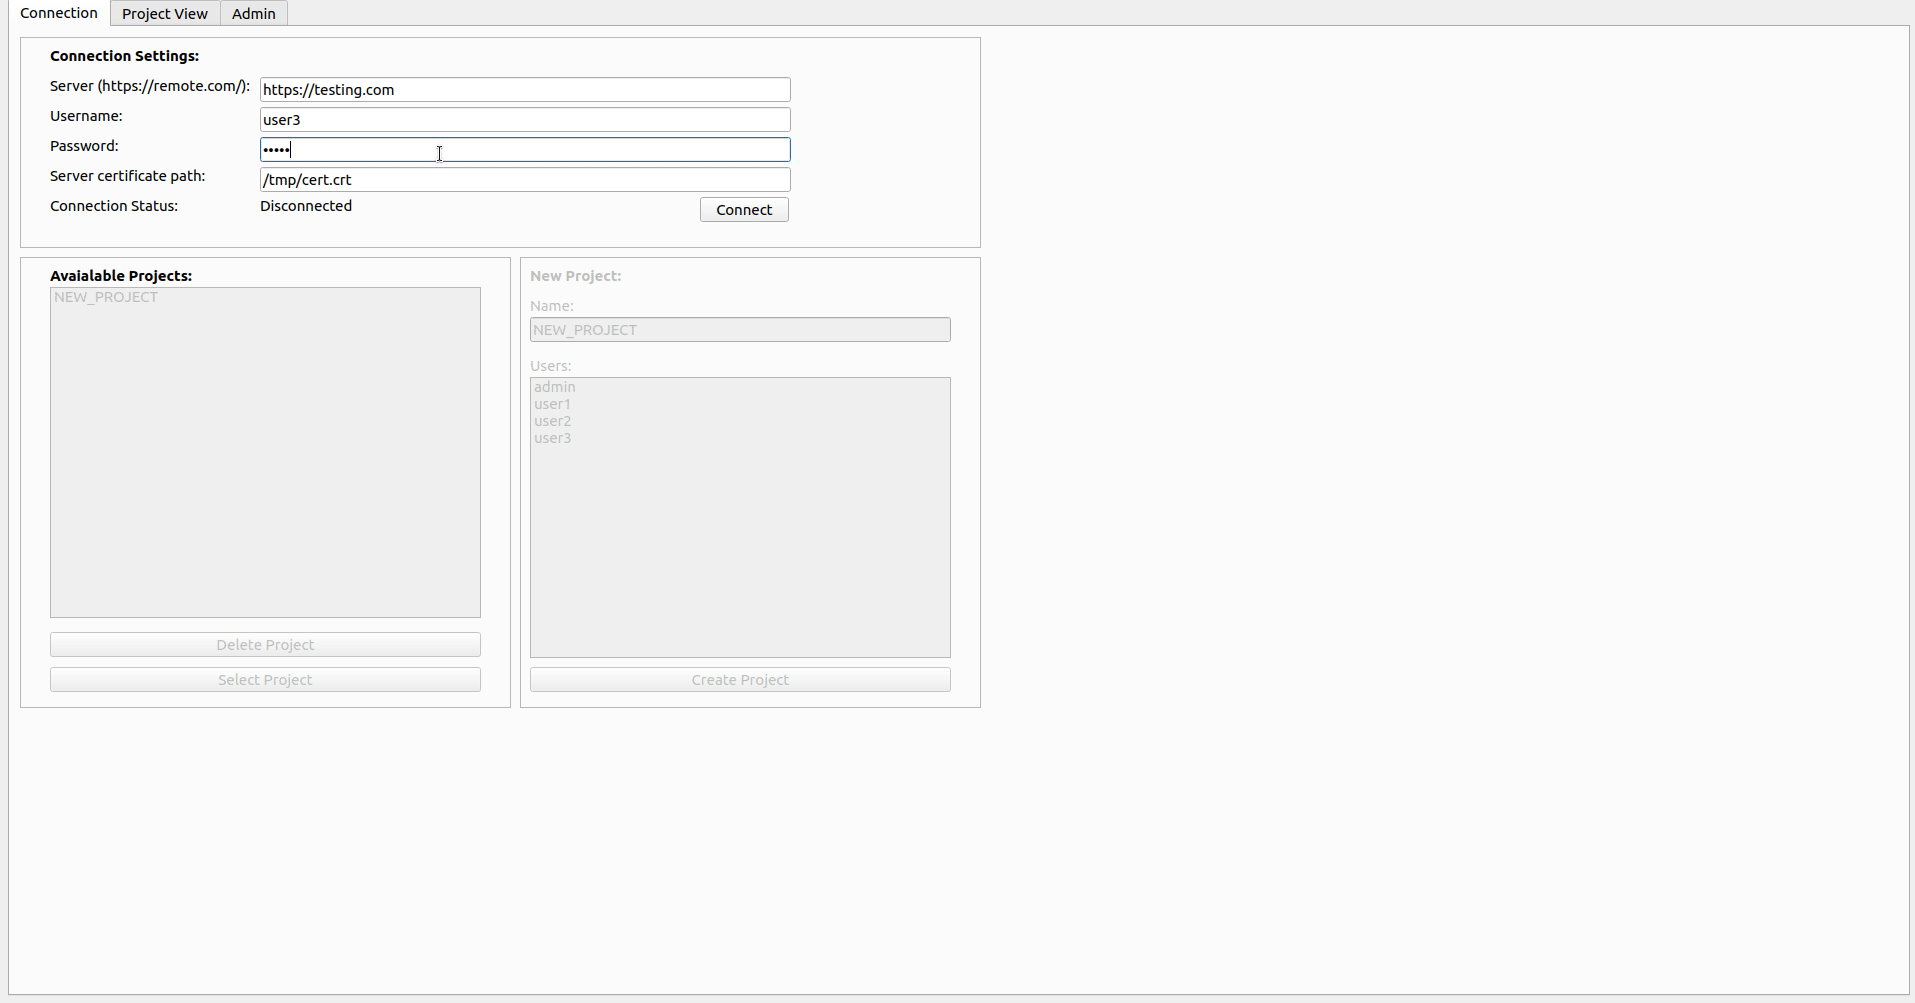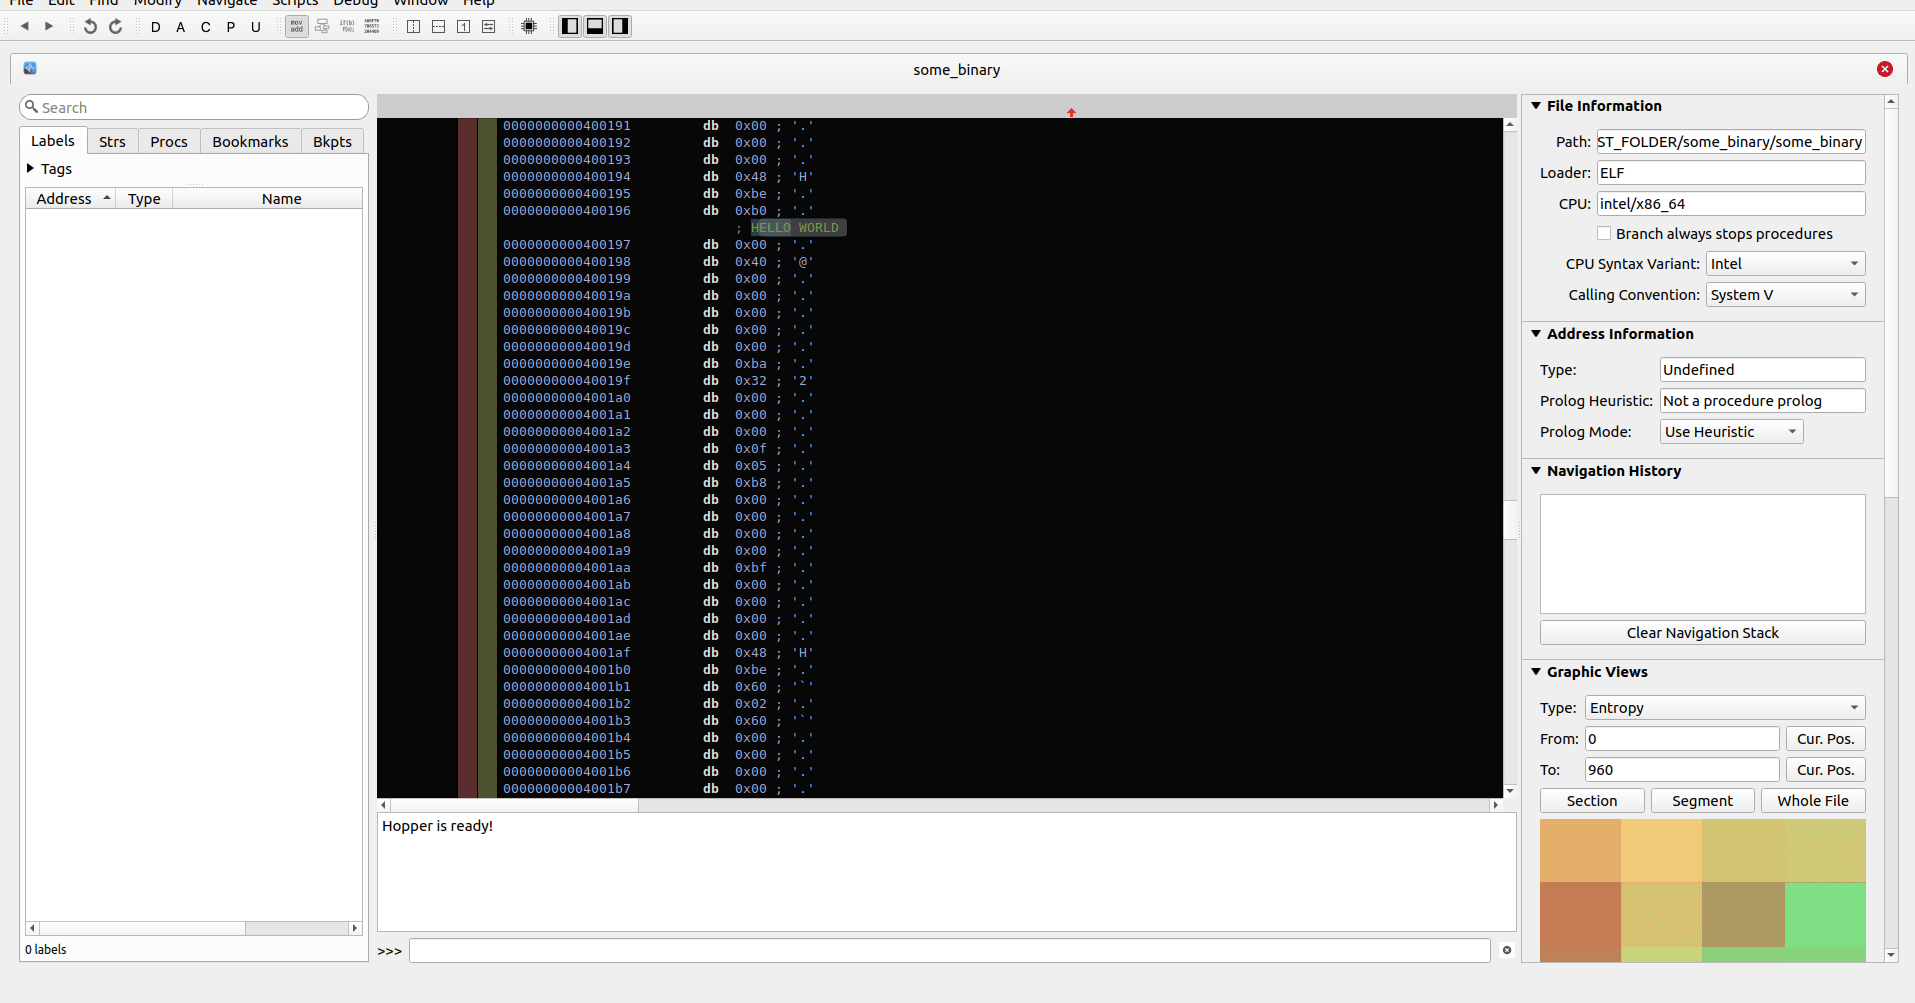 martyx00/collare
Multi-tool reverse engineering collaboration solution.