
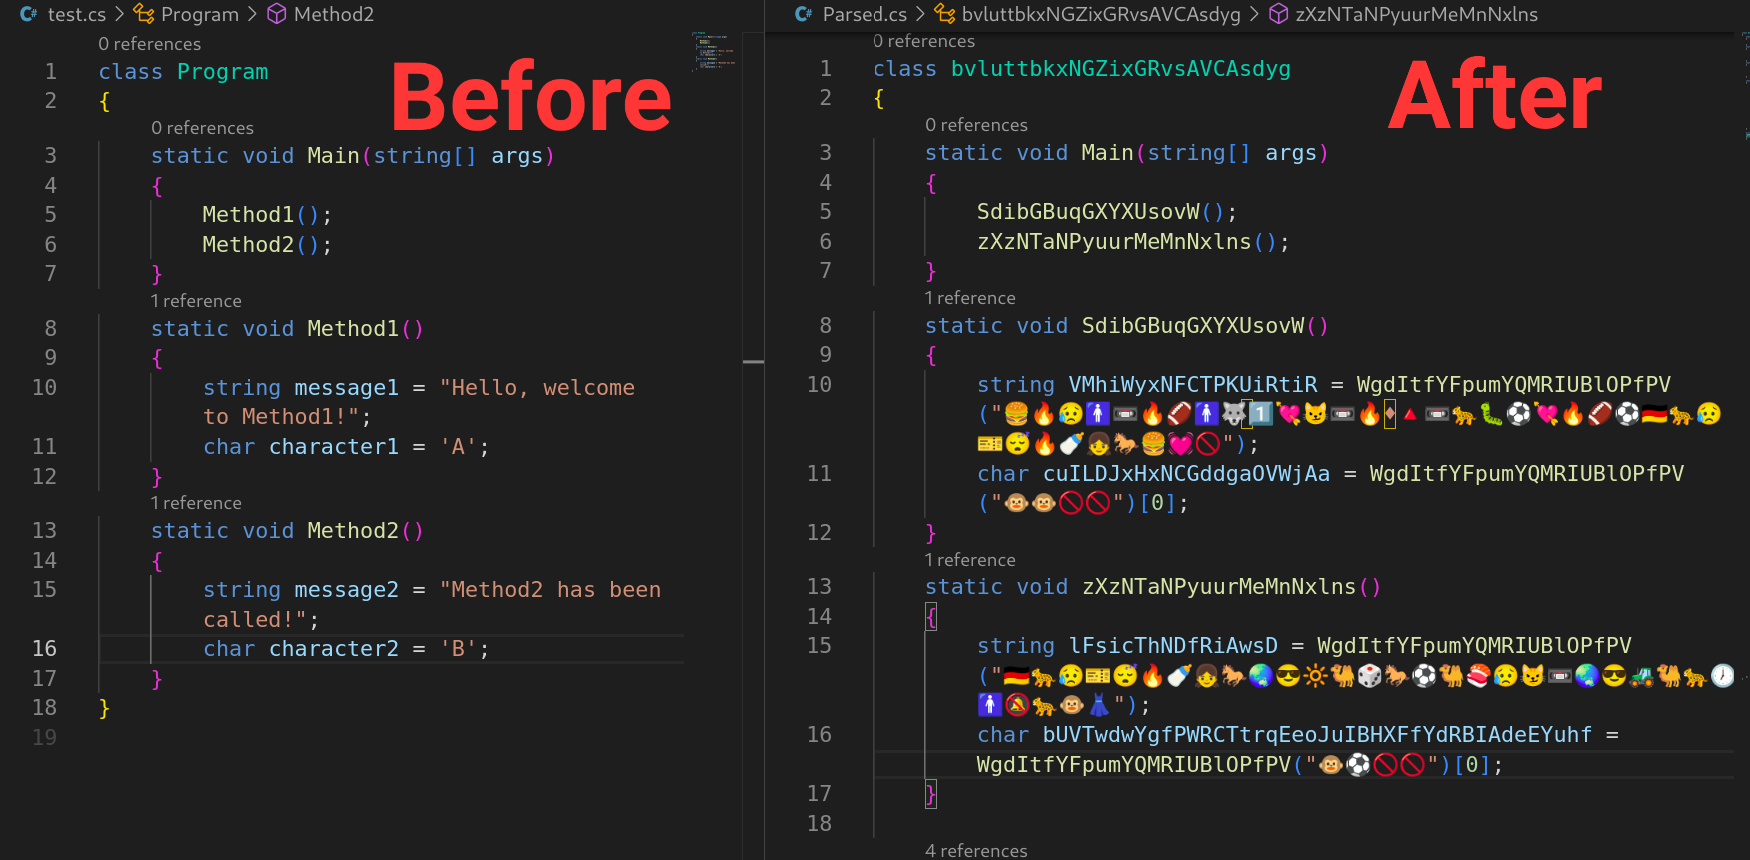
Emojify
 tomiwa-ot/emojify
C# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…
code-analysisreverse-engineeringstatic-analysis
tomiwa-ot/emojifyC# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…
 nighthawkk/audioserver-voip-recorder
🔬 An advanced Android research tool for real-time VoIP audio capture (Uplink/Downlink) by dynamically hooking libaudioflinger.so. Tested and built…
 dangokyo/cve-2017-3000
A full exploit of CVE-2017-3000 on Flash Player Constant Blinding PRNG
 bytev0rtex/cve-2026-65349
Proof-of-concept for an out-of-bounds write in XNU's vfs_attr_pack_internal (getattrlist) on iOS 26.6, demonstrating kernel heap corruption and…
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 cuteaplane/cve-2026-98260-for-opd2501
Android kernel LPE exploit for CVE-2026-98260 (POSIX CPU timer UAF), ported to OPPO Pad Air 5 / MT6878, gaining temporary root and loading KernelSU.
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 ffri/xprtestsuite
A collection of scripts and documents to help future XProtect Remediator (XPR) research
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
 nccgroup/binja_arch_ref
A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
 starry2233/cve-2026-25262-poc
CVE-2026-25262 (Qualcomm BootROM) deep-dive on the Black Hat Asia 2026 'A journey through Sahara' talk + read-only Sahara/EDL recon harness. GPLv3.
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 finngineering/ch55x_firmware_extractor
Firmware extractor for CH55x microprocessors
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 xrzcc/s26-m1q-ghostlock-selinux
GhostLock CVE-2026-43499 research for Galaxy S26 (SM-S942U1/m1q): SELinux Permissive achieved, KASLR + tracefs port, uid=0 boundary documented
 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)