
xed
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
binary-analysiscode-analysisdebuggers+3
1.6k
intelxed/xedLow-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
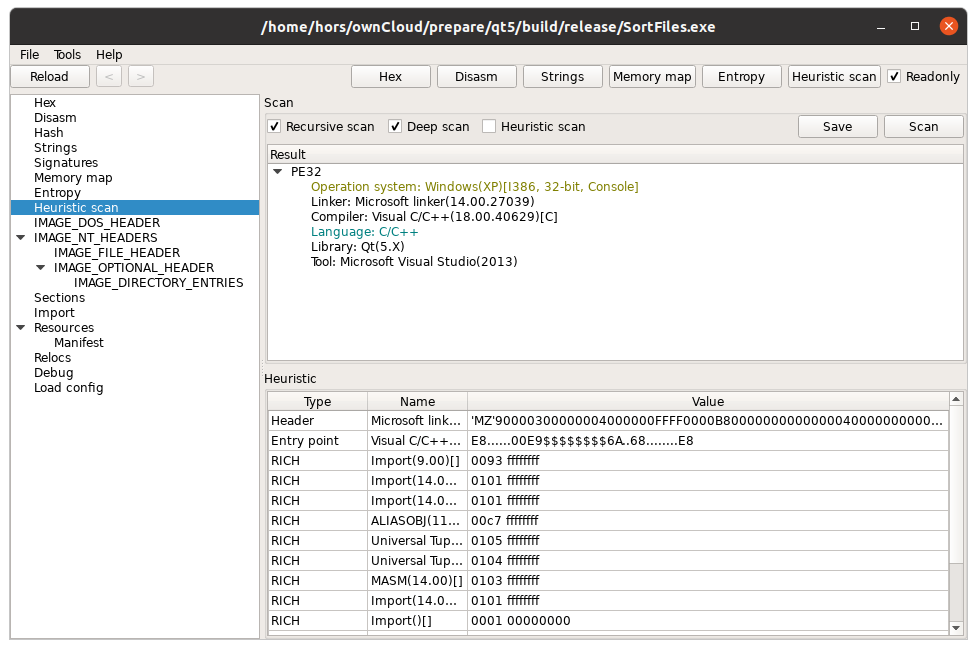 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…
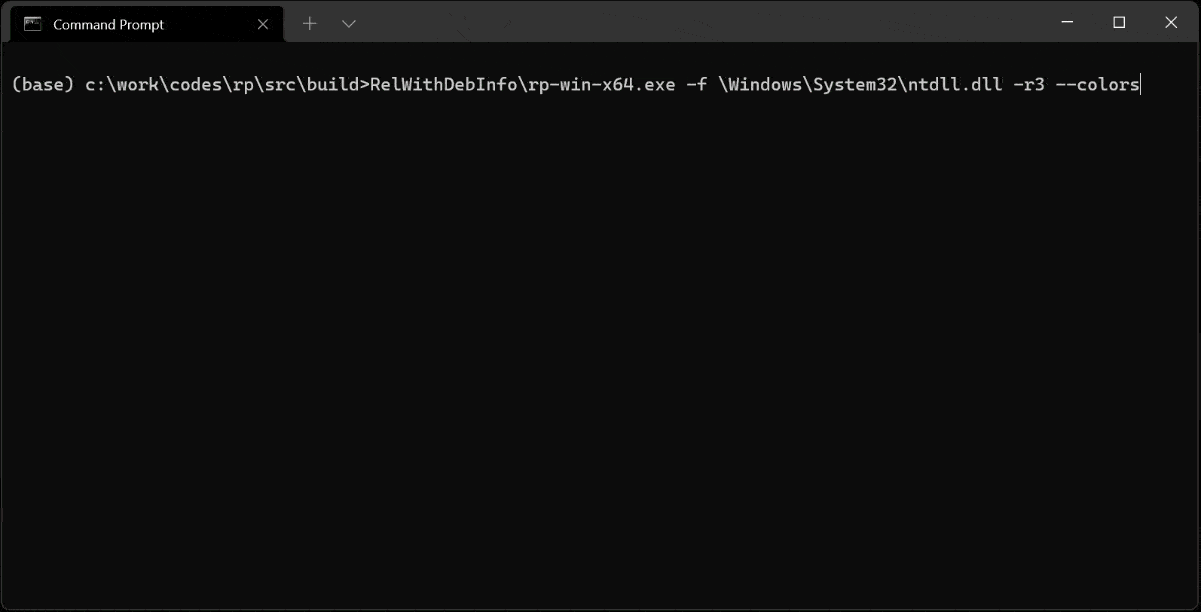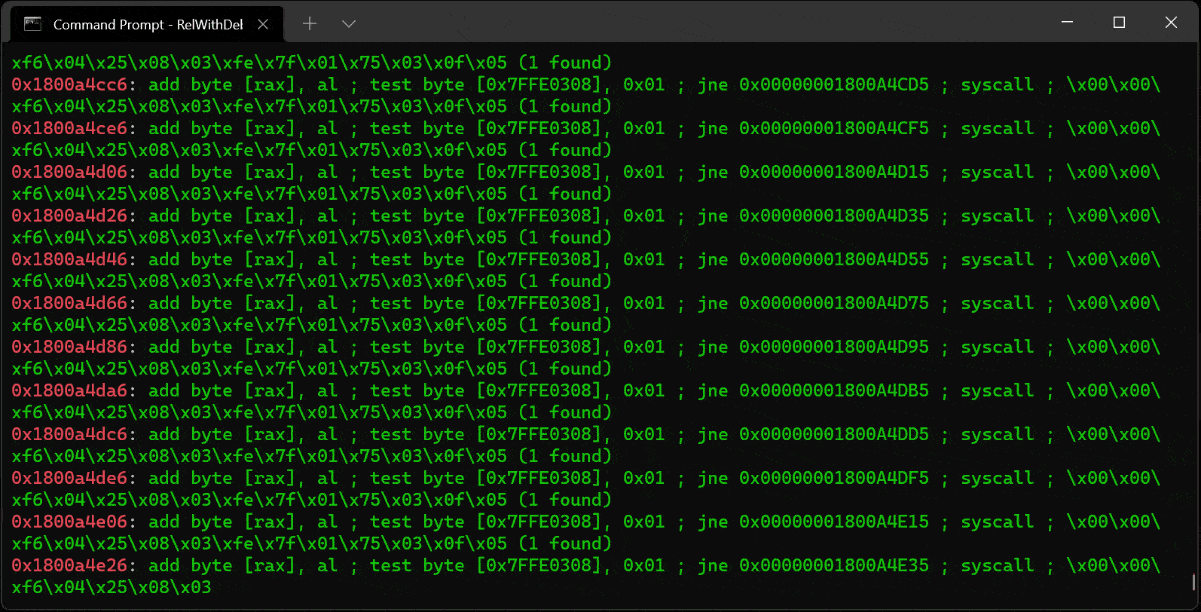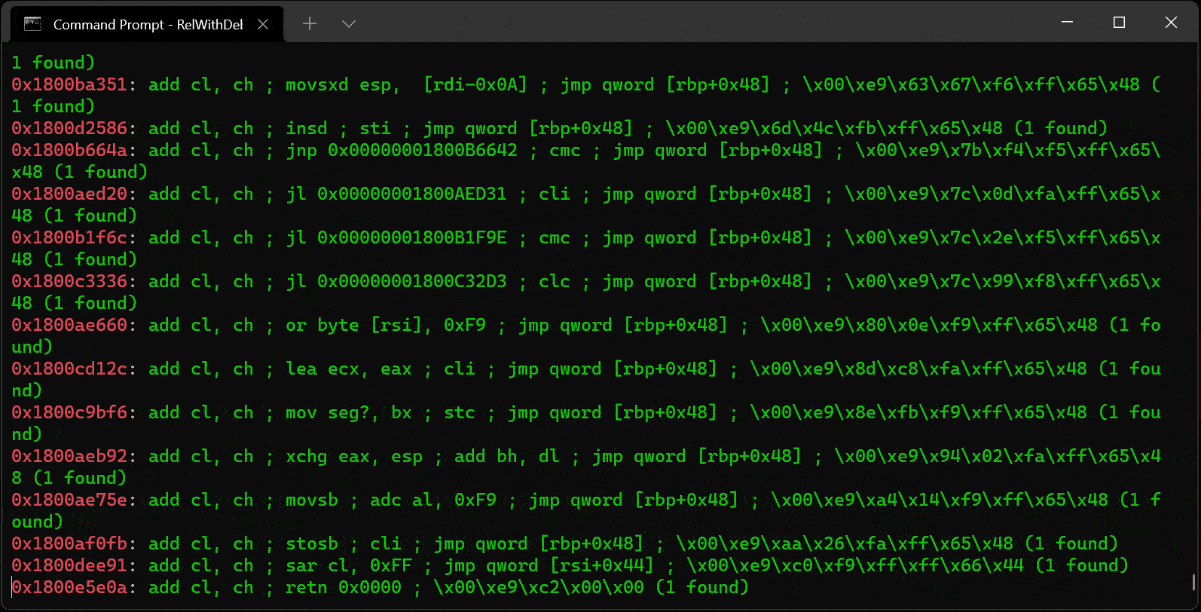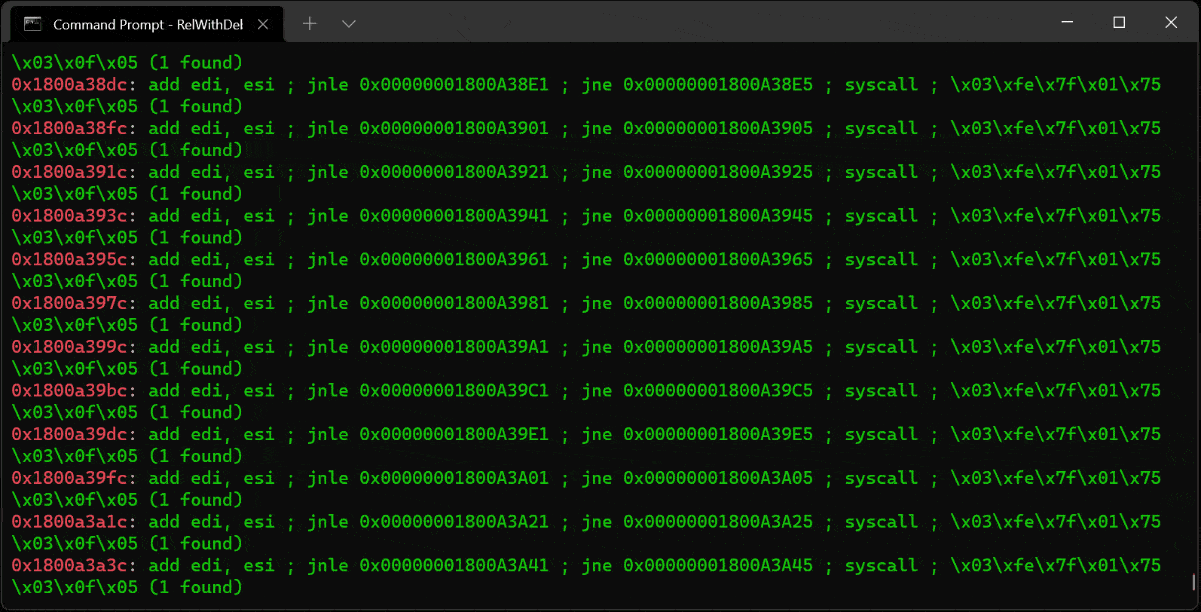 0vercl0k/rp
Fast C++ ROP gadget finder for PE/ELF/Mach-O binaries across x86/x64/ARM/ARM64 architectures, enabling efficient return-oriented programming chain…
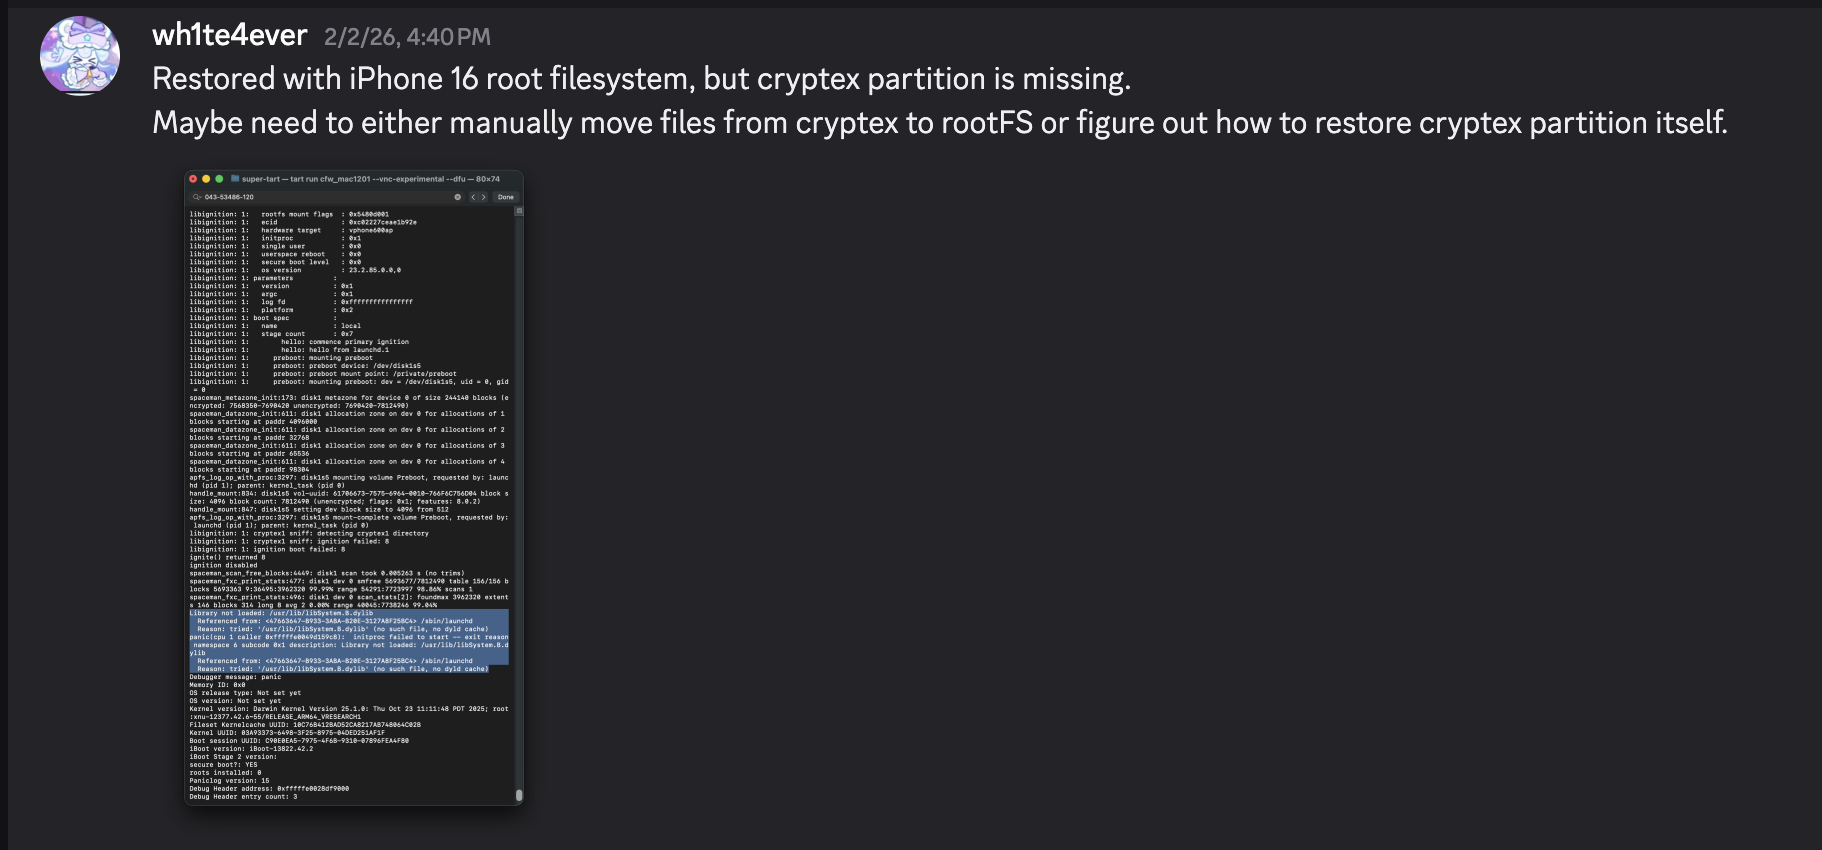 wh1te4ever/super-tart-vphone-writeup
Guide to building a virtual iPhone using VPHONE600AP components from Apple's PCC firmware, with firmware patching, bootchain modification, and kernel…
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…
 ergrelet/unlicense
Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.
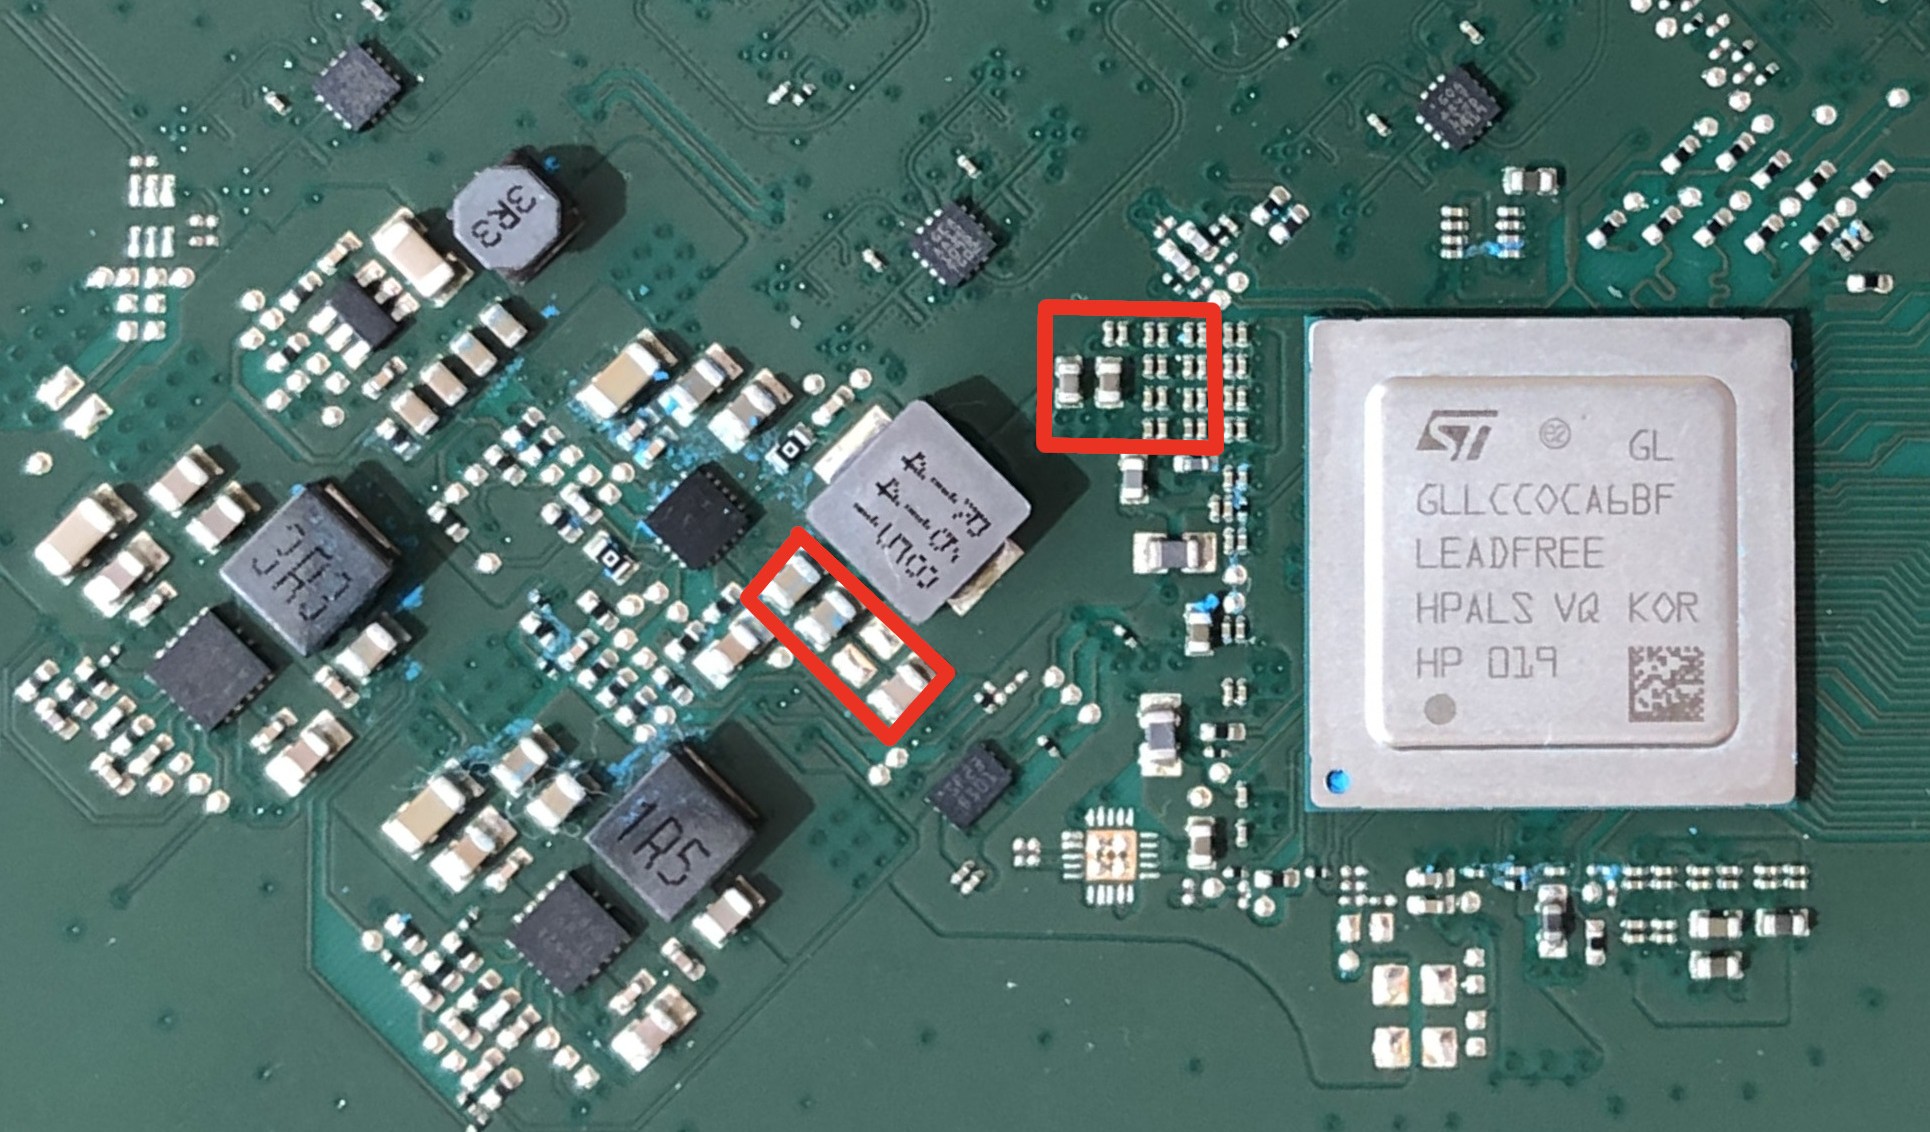 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
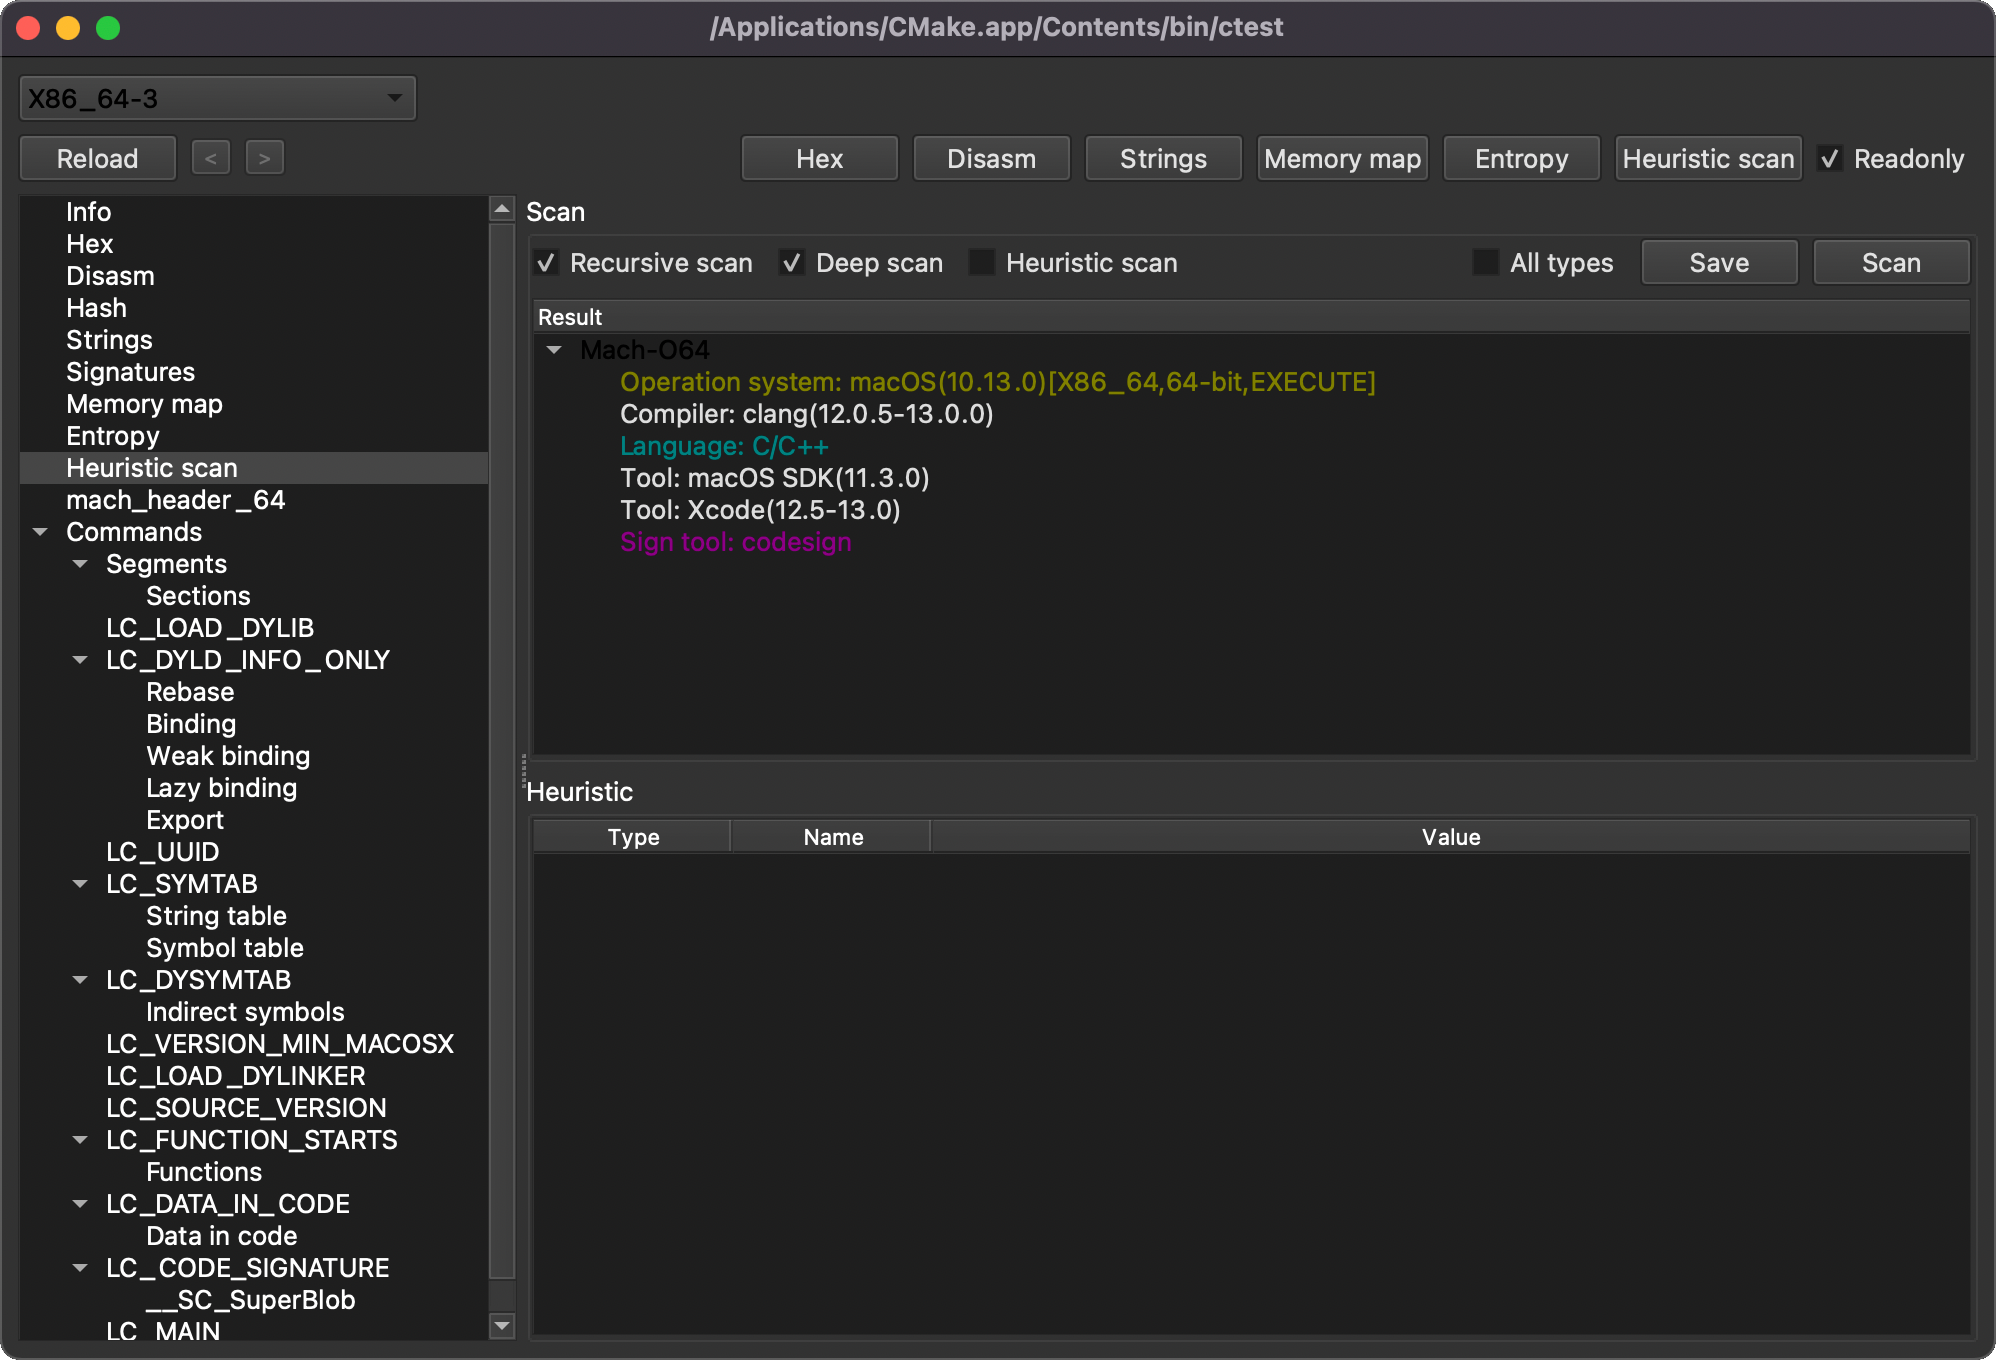 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques