zte-blade-v40-vita-unlock

Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…

Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…

Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…

Research implementation demonstrating interaction with Linux eBPF subsystem related to CVE-2021-3490. Includes BPF map creation, syscall wrappers,…

Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…

ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…

Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具

Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.

An ArchLinux based distribution for penetration testers and security researchers.

Gives you one-liners that aids in penetration testing operations, privilege escalation and more

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .

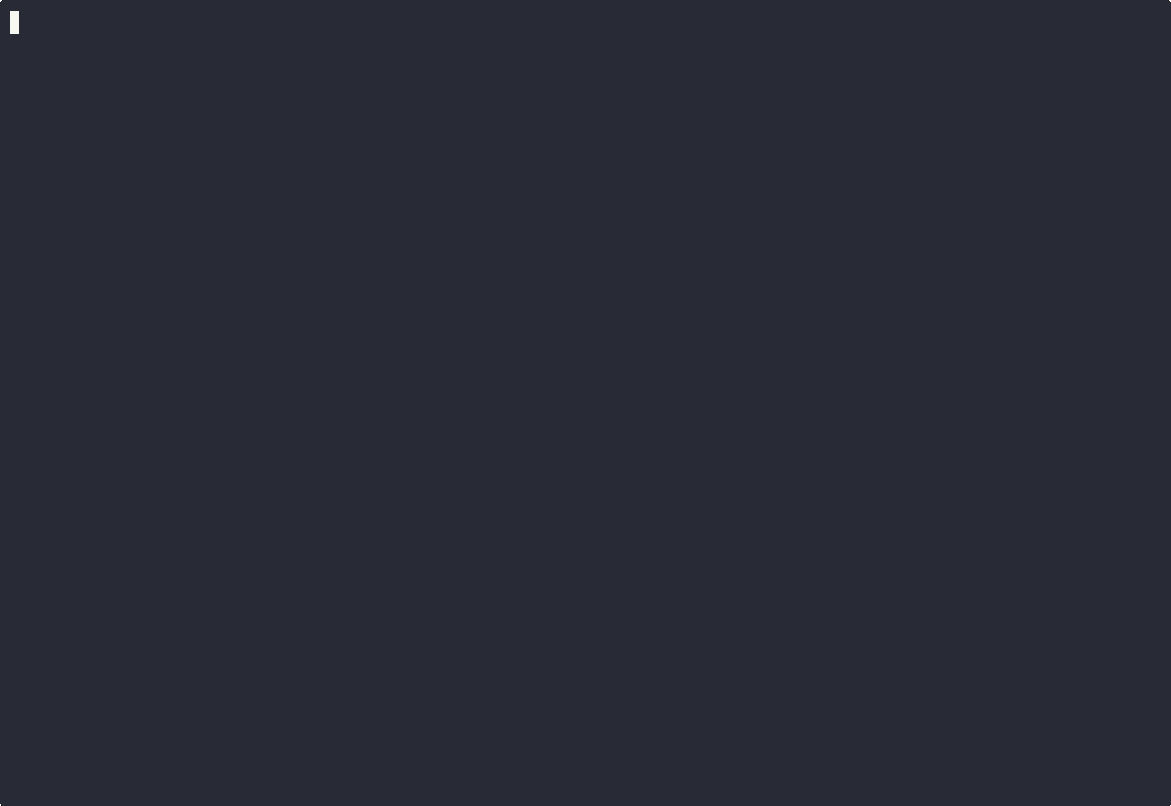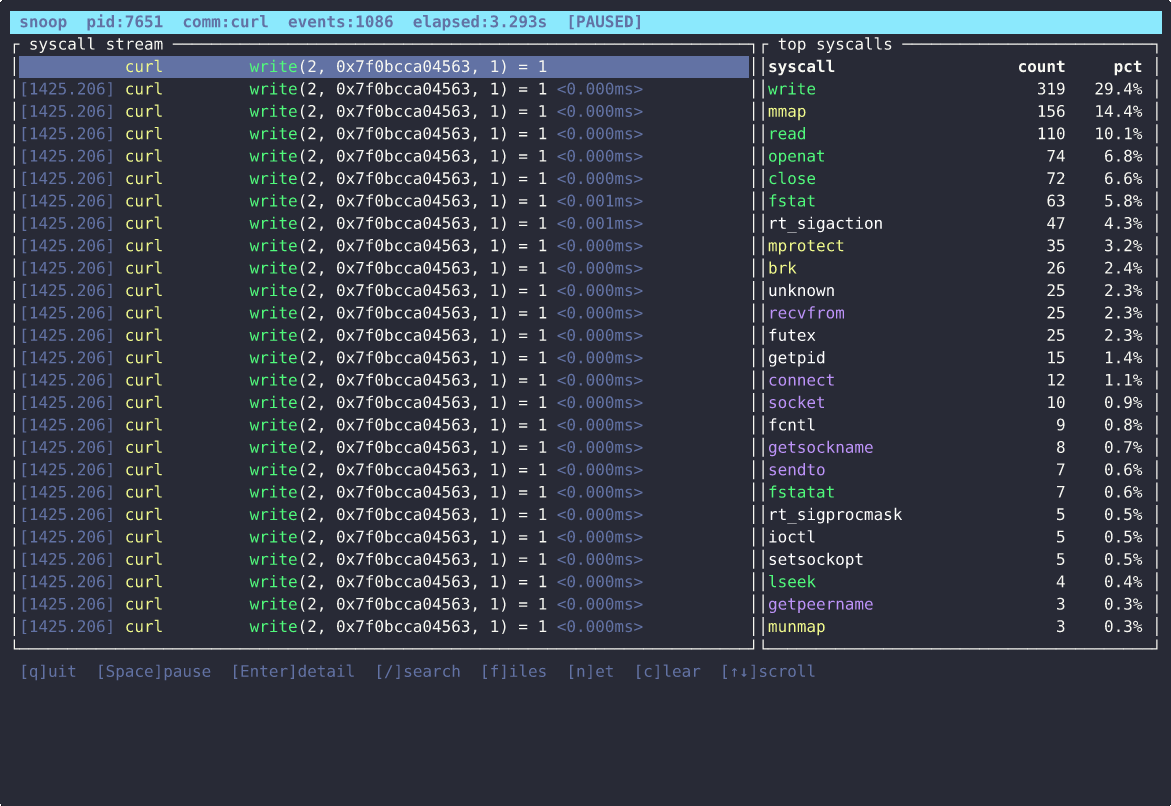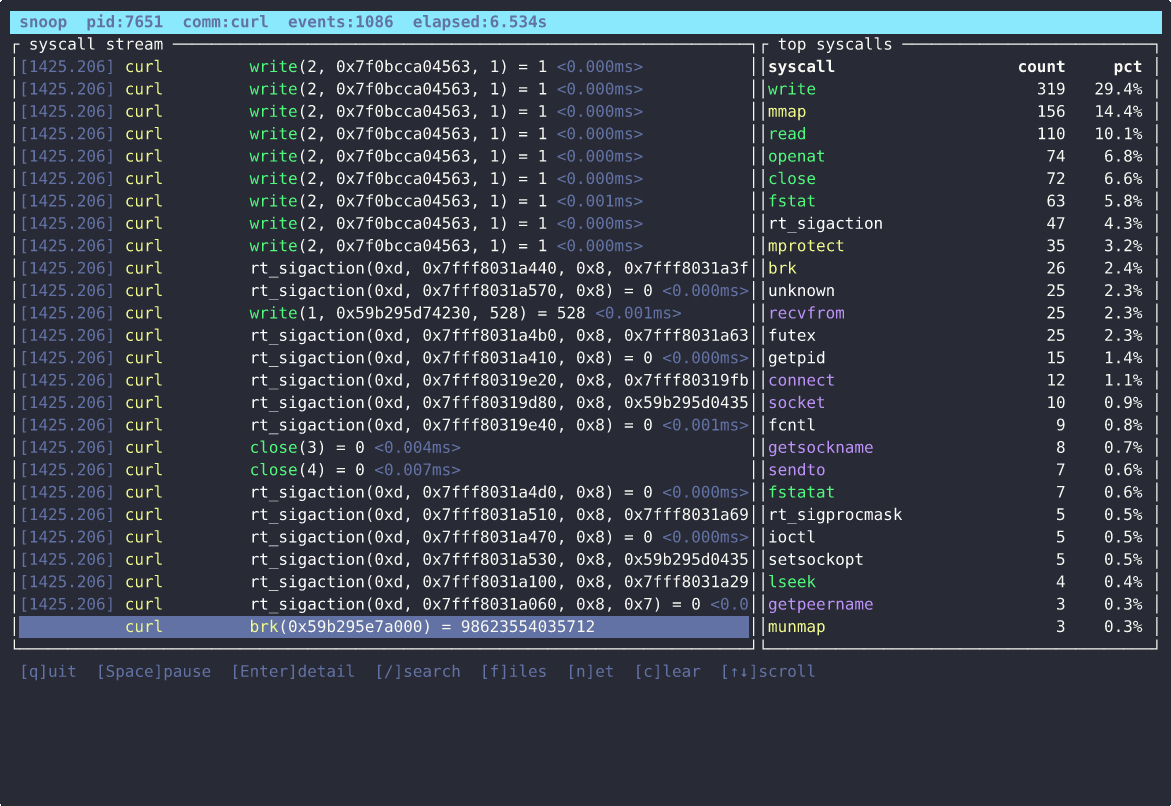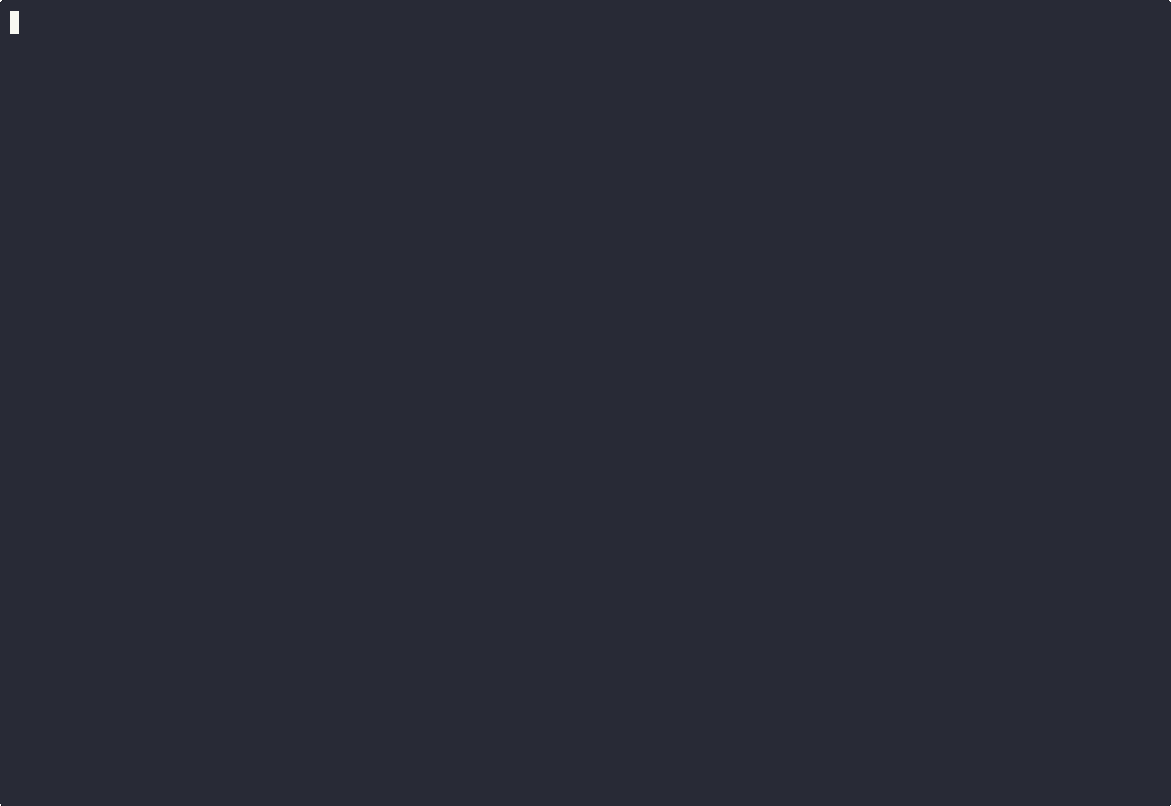
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.

A True Instrumentable Binary Emulation Framework


A curated list of resources related to Industrial Control System (ICS) security.


Curated collection of security research papers, CVE exploit writeups, reverse-engineering analyses of Apple internals, and commissioned security…

Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…

Automatically exported from code.google.com/p/firmware-mod-kit