

FUD-C2-Framework
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
7
x3r0day/fud-c2-frameworkA fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 darioi/droidcarve
Android Reverse Engineering Framework
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
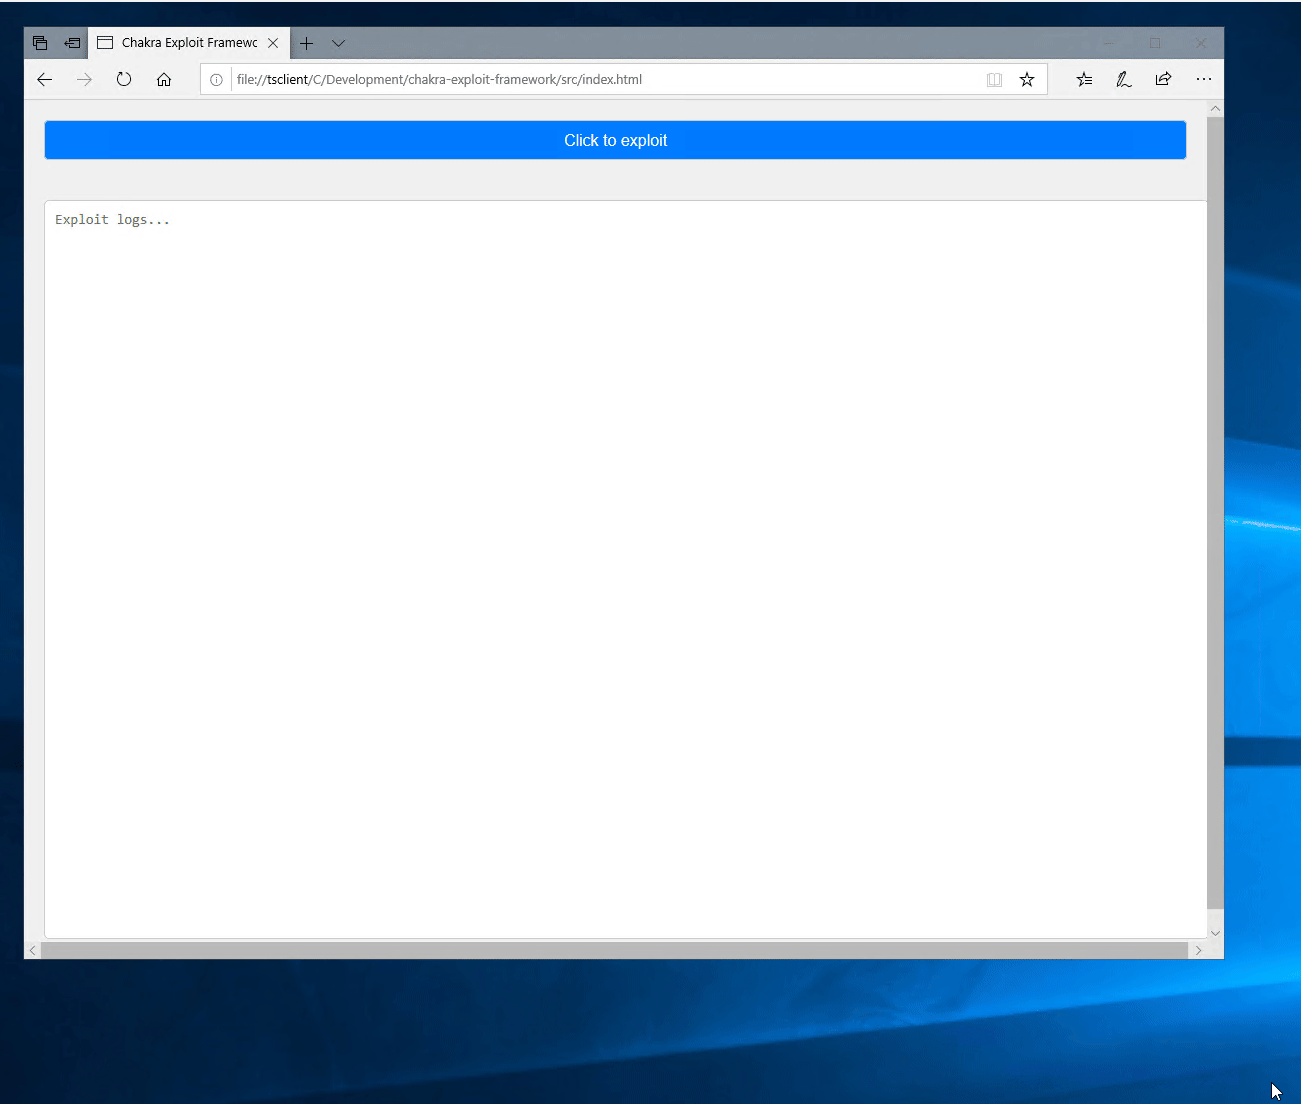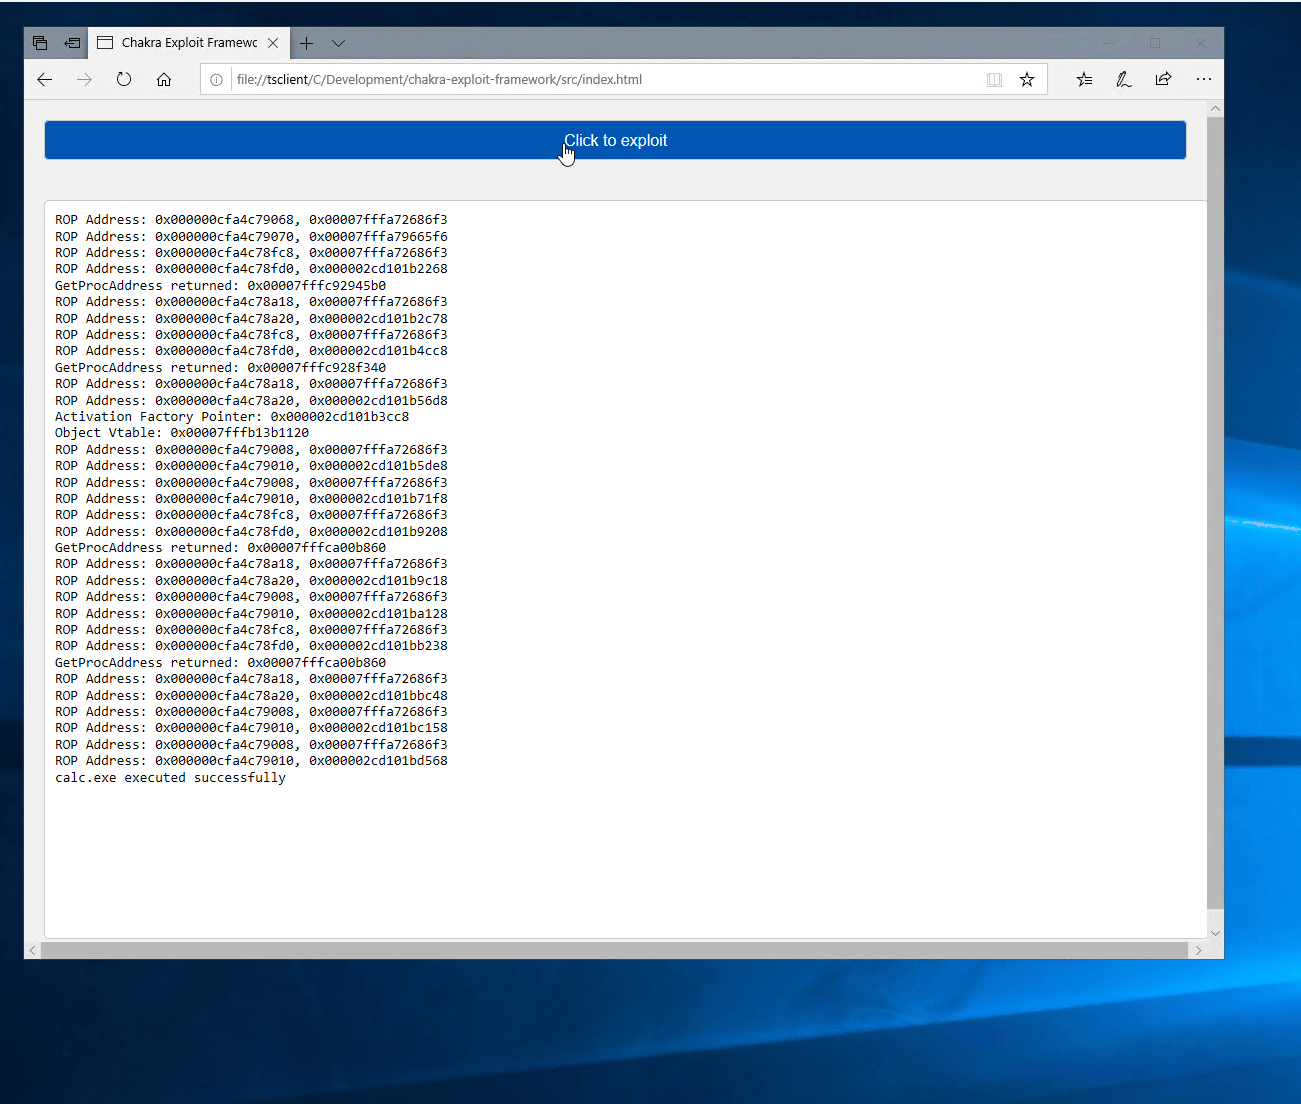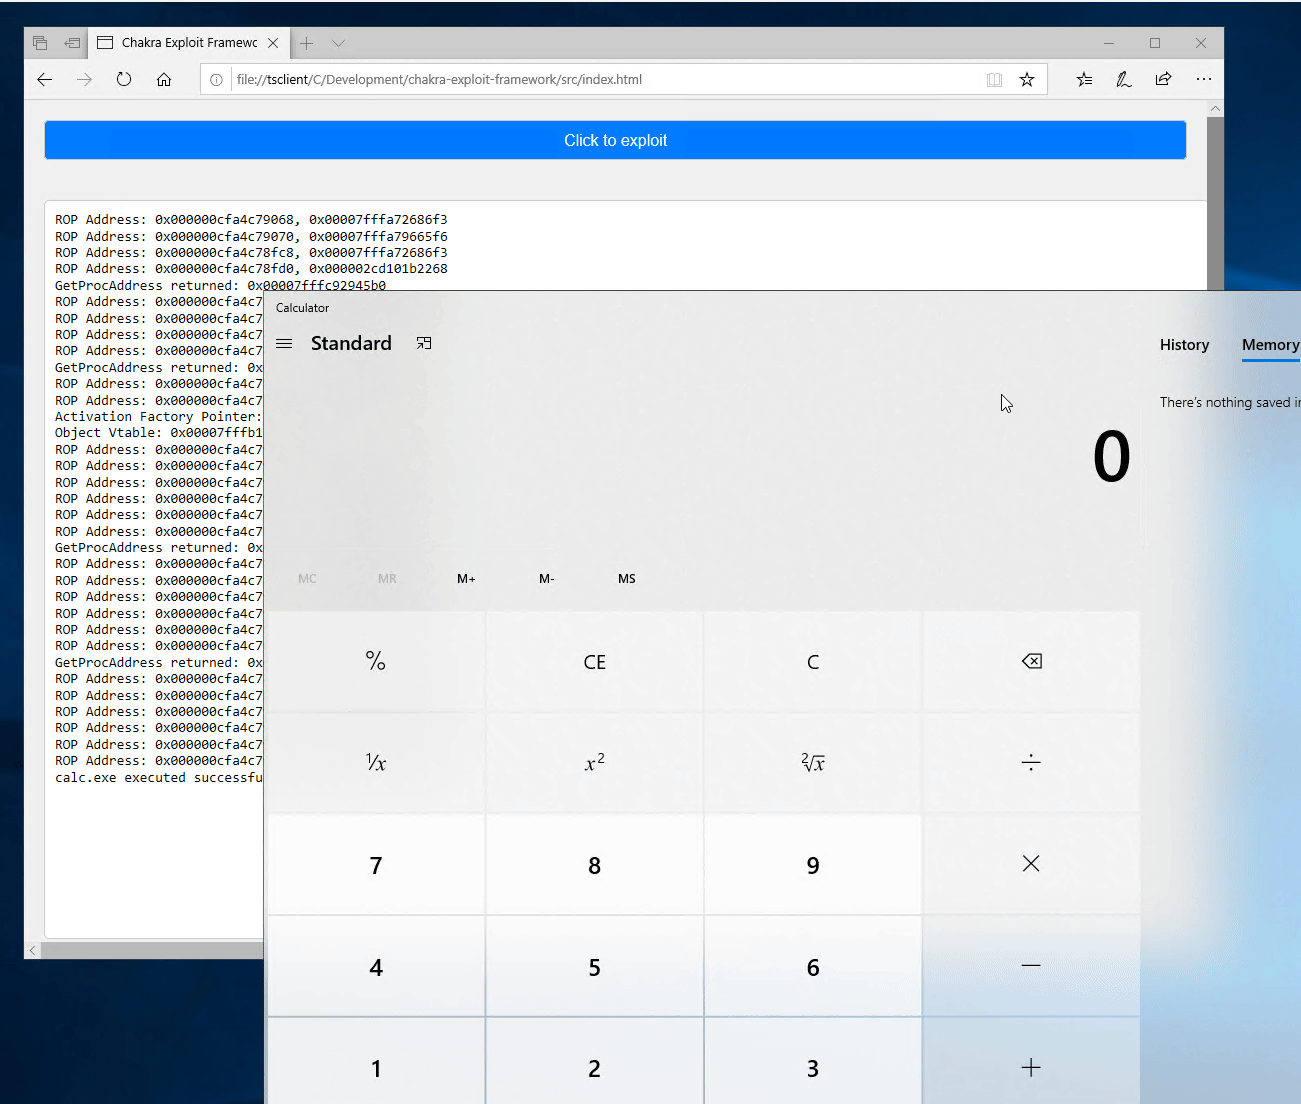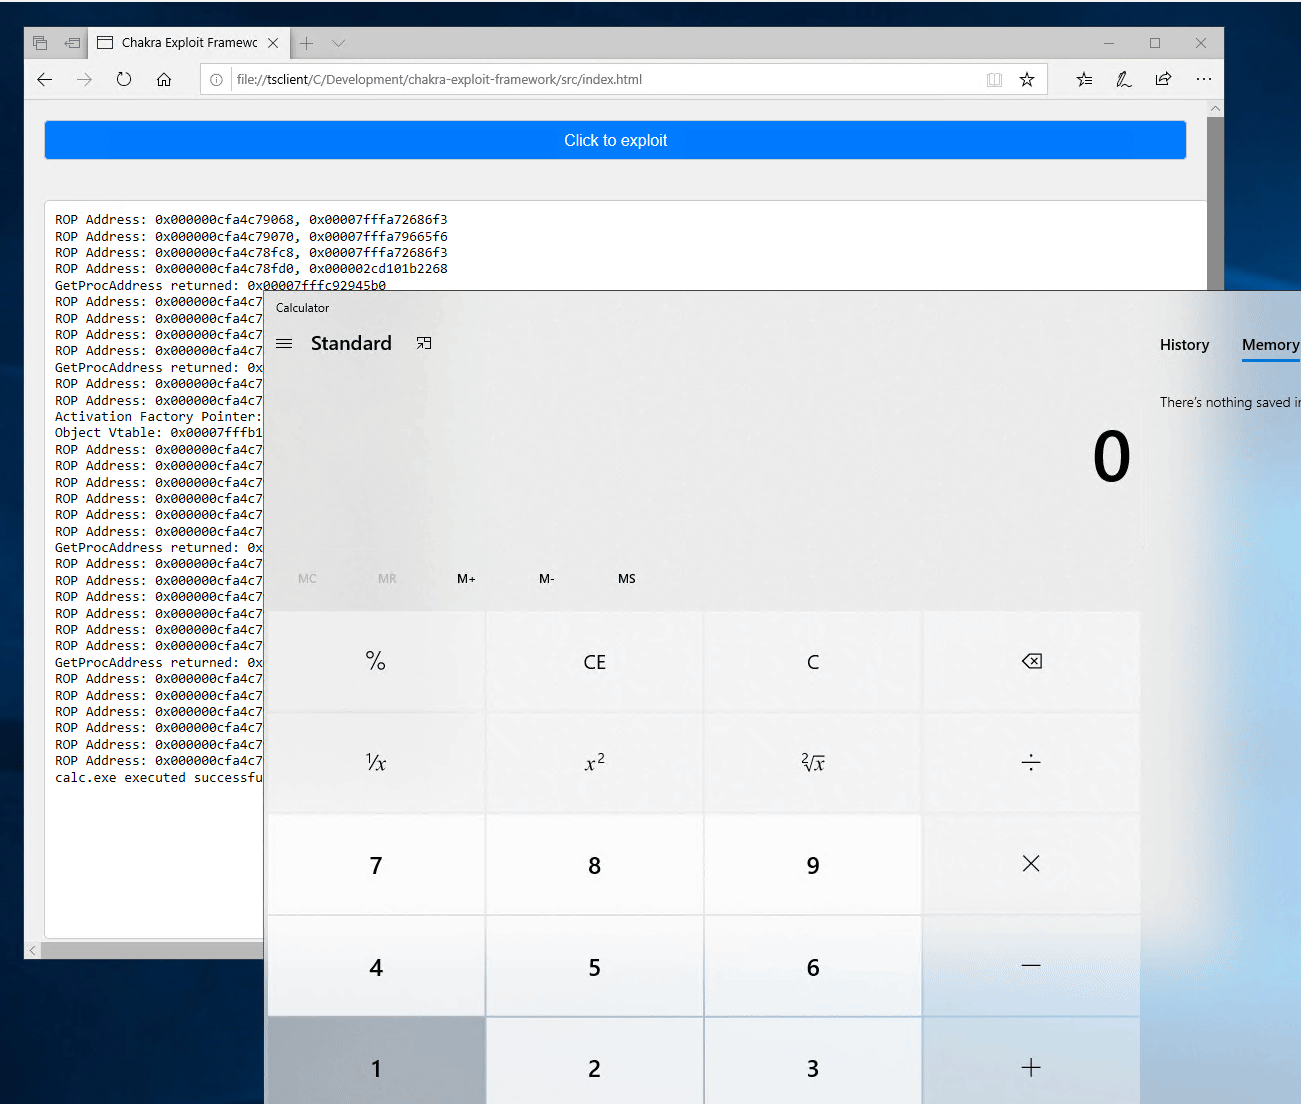 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 ptswarm/reflutter
Flutter Reverse Engineering Framework

 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 angr/angr
A powerful and user-friendly binary analysis platform!
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
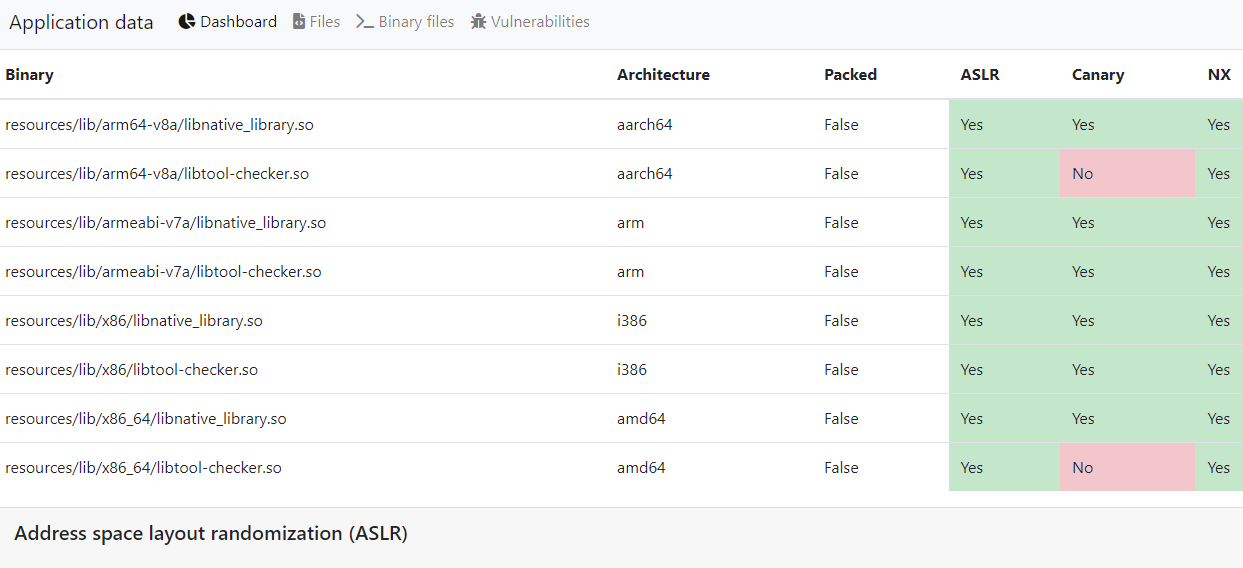 stefan2200/aparoid
Static and dynamic Android application security analysis
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection