

boxlambda
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
debuggerseducationembedded-systems-security+5
epsilon537/boxlambdaFPGA based microcomputer sandbox for software and RTL experimentation
 watchfulip/tp-link-decrypt
Decrypt TP-Link Firmware
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 dpt/chasehq
Chase H.Q. for ZX Spectrum — reverse-engineered and reconstructed in portable C
 trailofbits/manticoreui
The Manticore User Interface with plugins for Binary Ninja and Ghidra
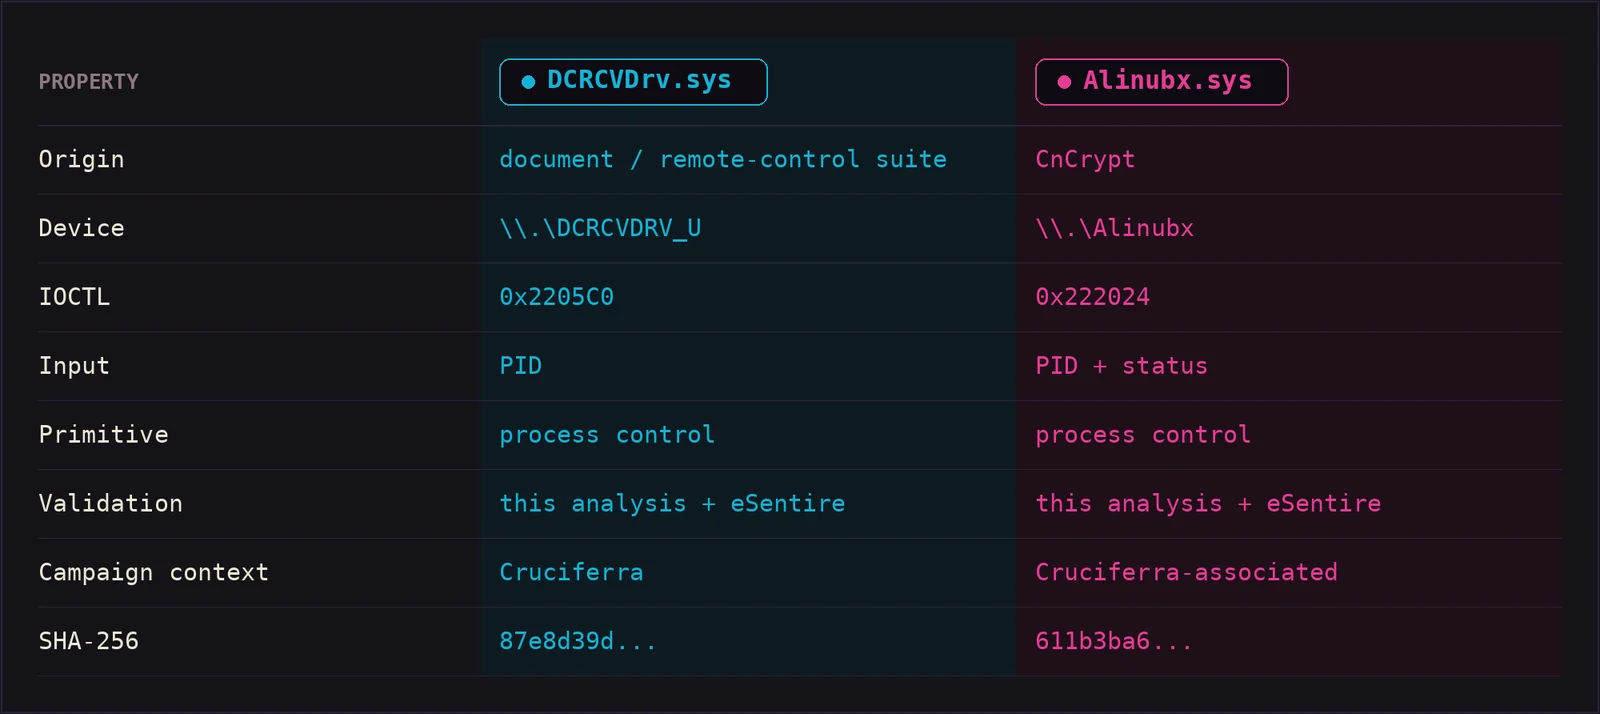 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
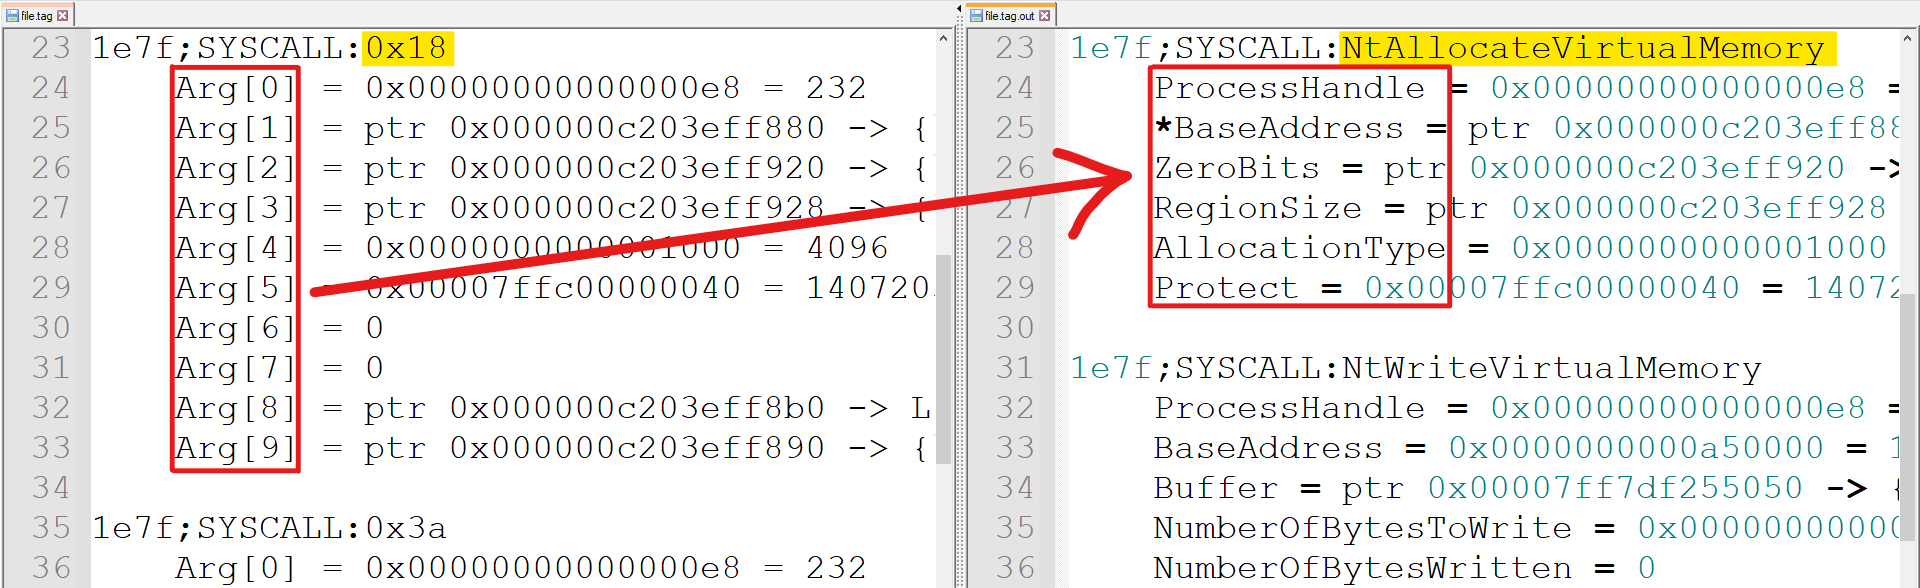 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 ethanedits/iqvw64e-privilege-escalation
Educational proof-of-concept for CVE-2015-2291 local privilege escalation via Intel Ethernet driver IOCTL abuse, demonstrating arbitrary kernel…
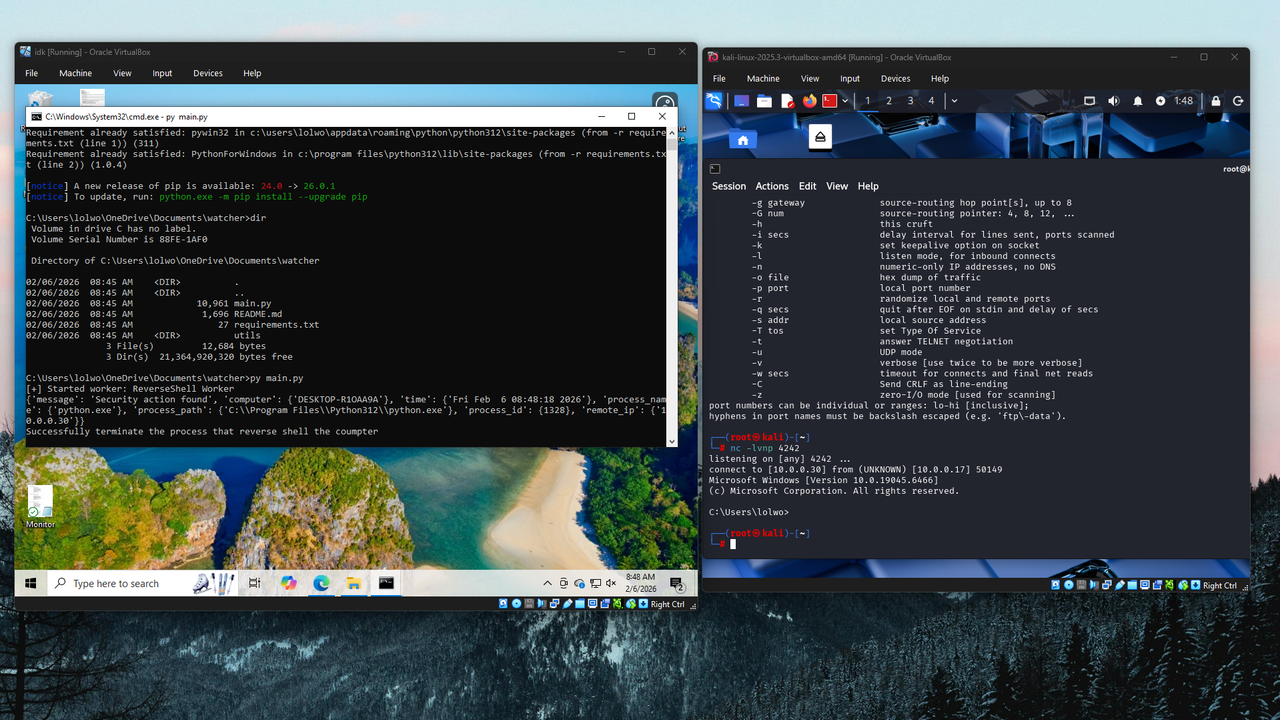 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…