
cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Windows tool for dumping malware PE files from memory back to disk for analysis.

A collection of malware samples caught by several honeypots i manage

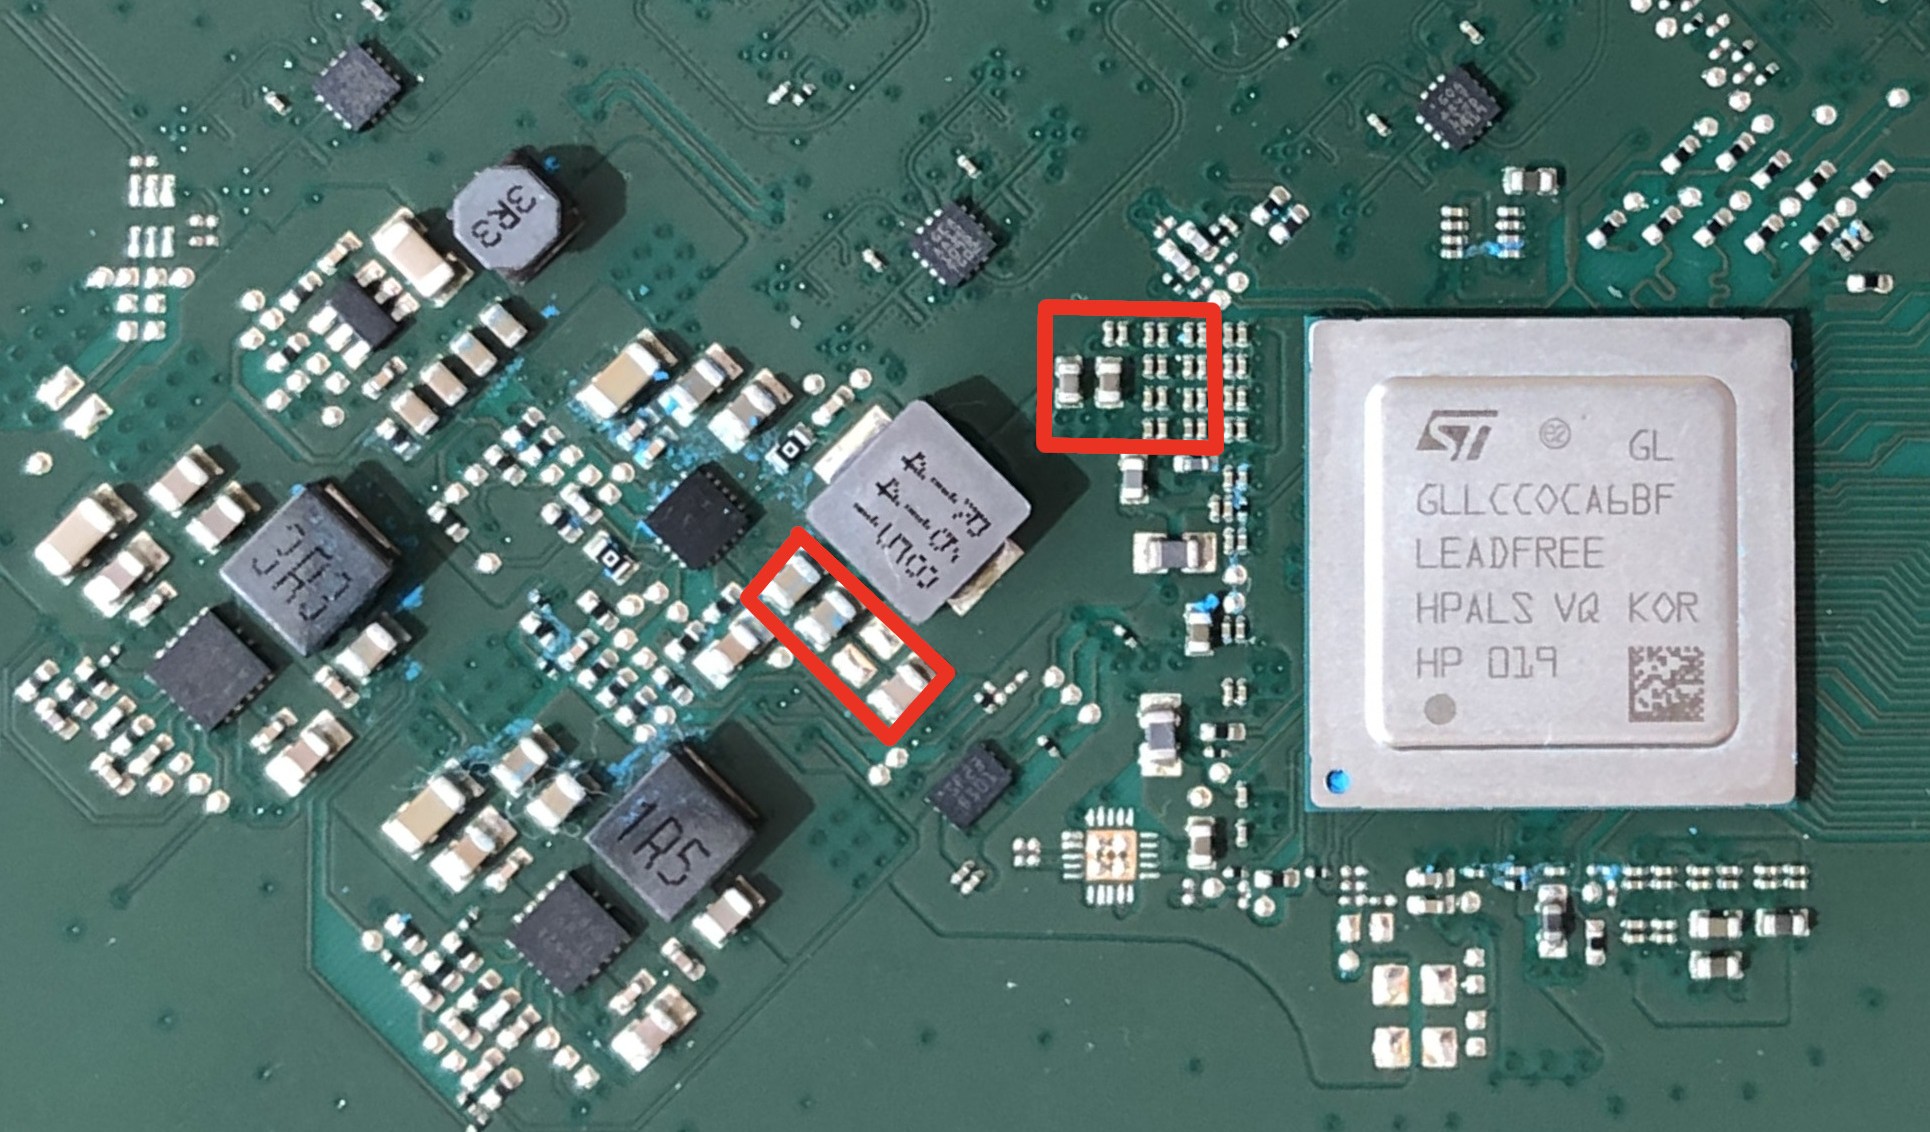
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…

Framework to test any Anti-Cheat


Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.


Configuration Extractors for Malware

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

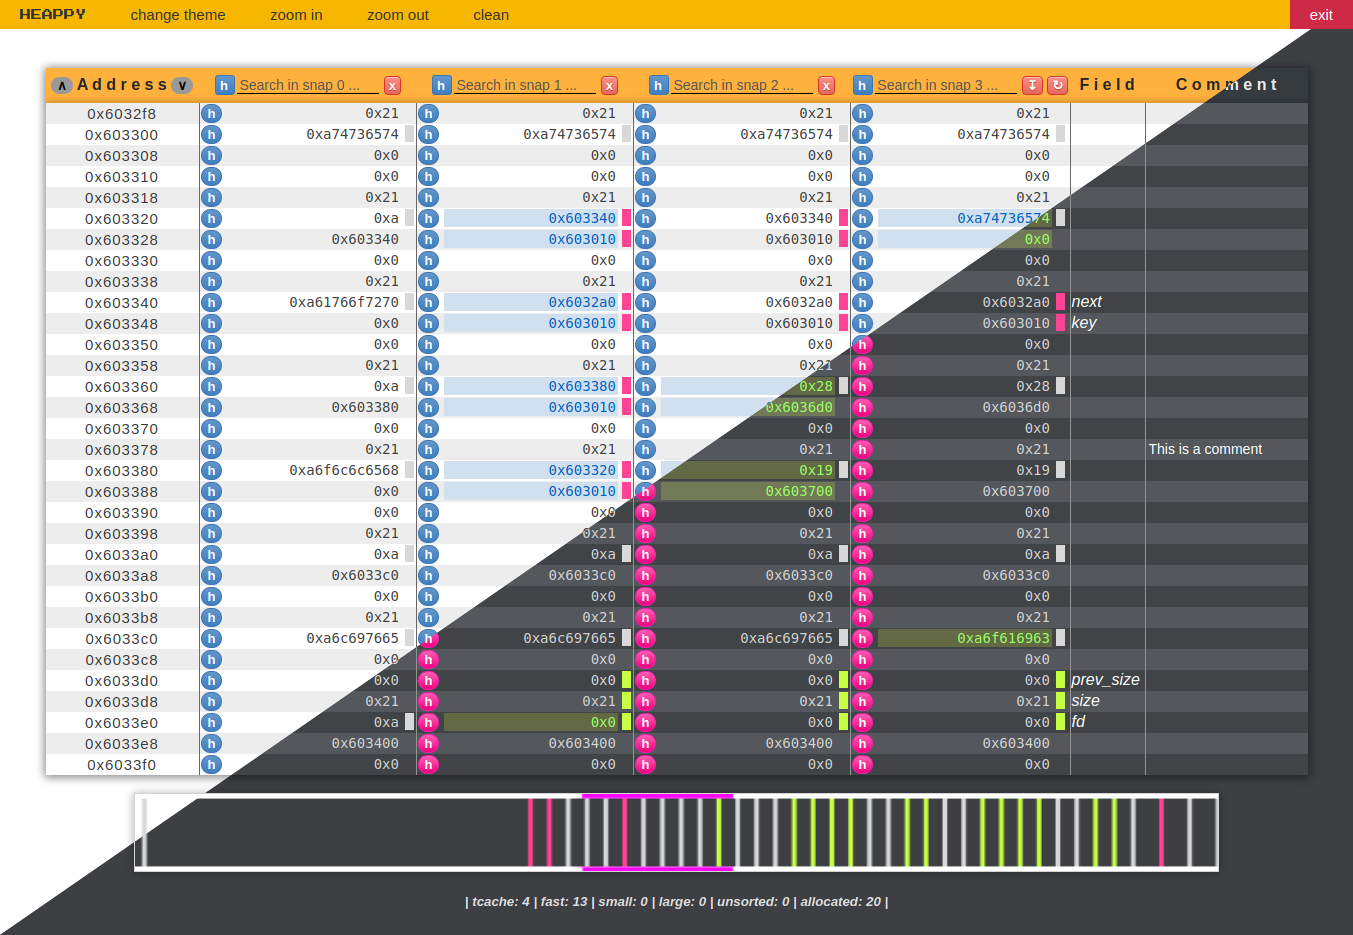
A happy heap editor to support your exploitation process :slightly_smiling_face:

Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian

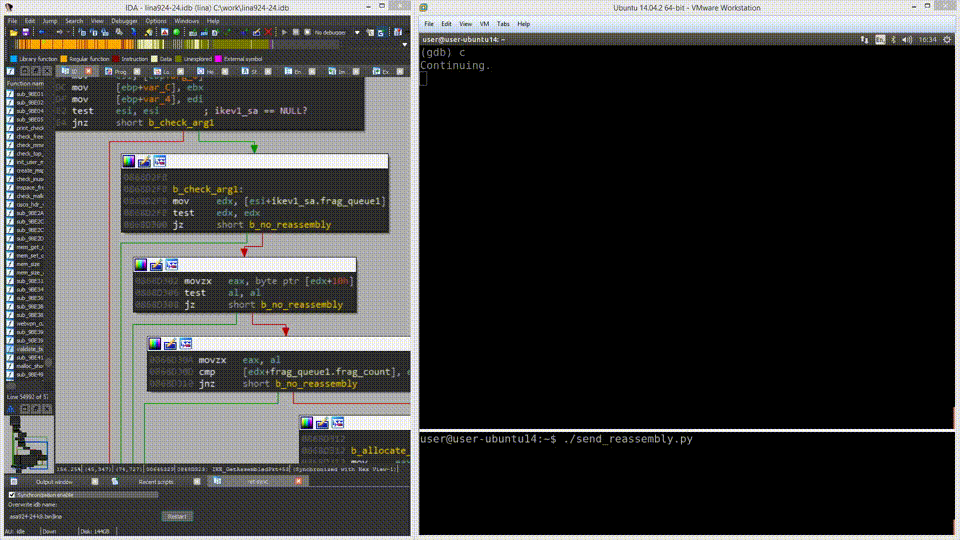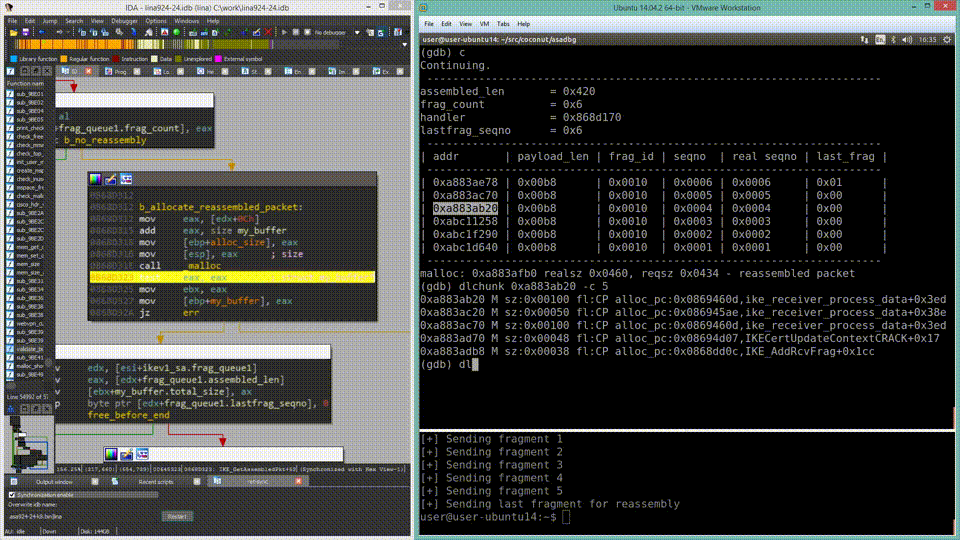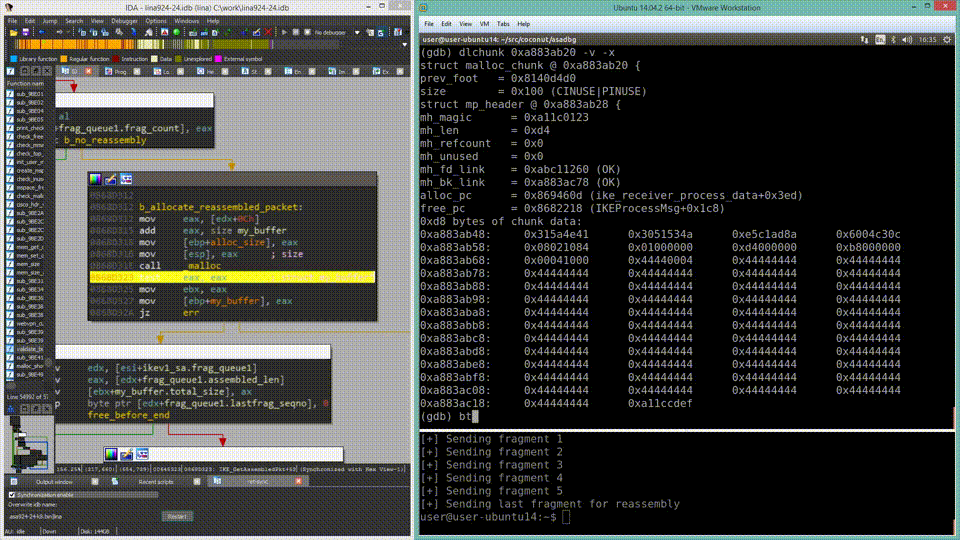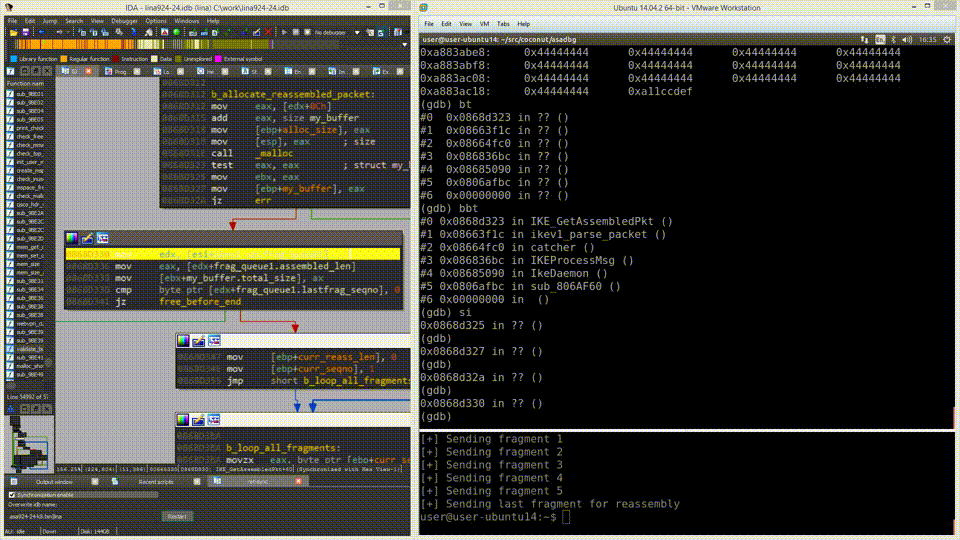
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices

A library for intercepting native functions by hooking KiFastSystemCall

Personal research into the Xbox Series Architecture

Compile-time AES string obfuscation for C++

A dependency-free C++ PLAYER for Yamaha SMAF (.mmf) ringtones: the polyphonic-ringtone format of the 2000s MA-3 / MA-5 phone chips, rebuilt with its…

CVE-2026-36425 OPSWAT AppRemover (ardrv.sys) improper access control advisory