ROP_ROCKET
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
binary-exploitationexploitationexploit-frameworks+4
182
bw3ll/rop_rocketROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
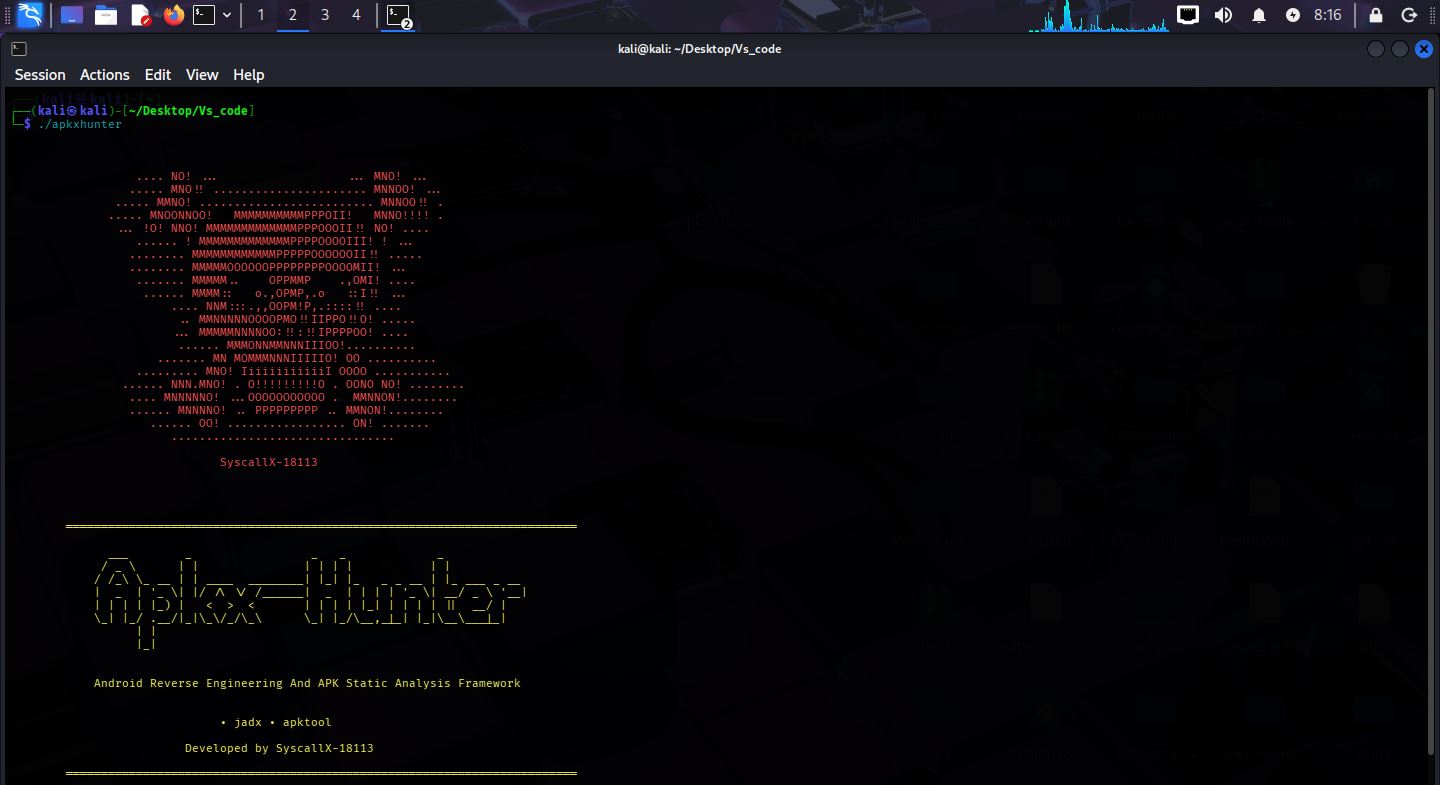 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 darioi/droidcarve
Android Reverse Engineering Framework
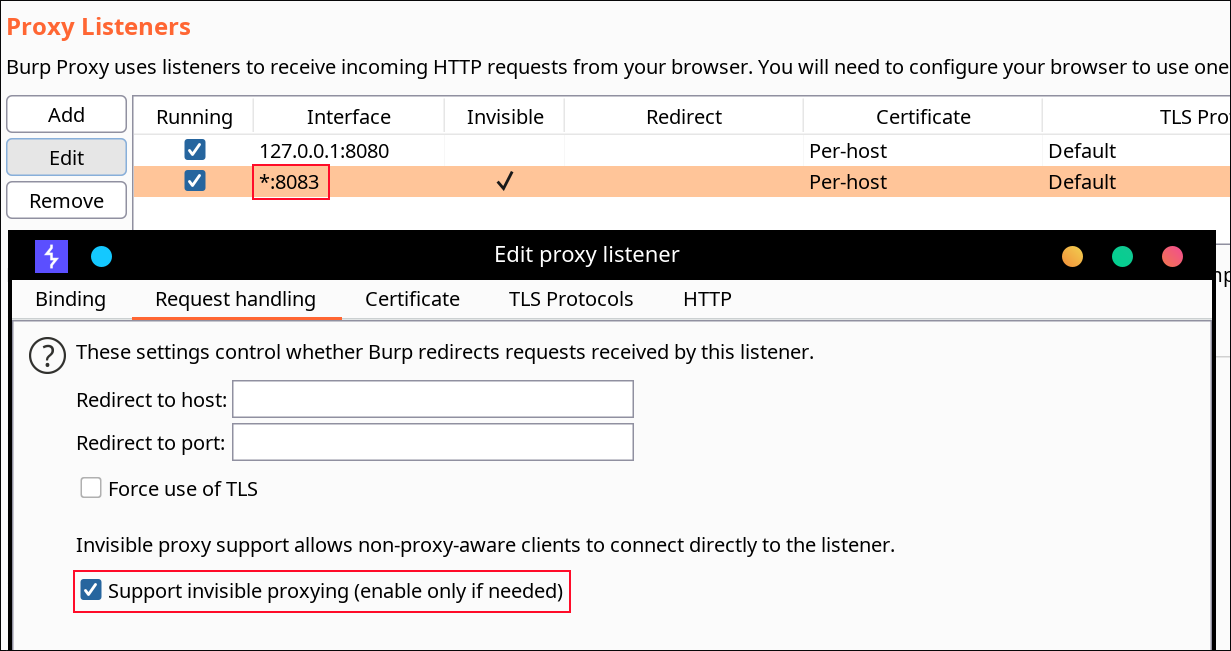 ptswarm/reflutter
Flutter Reverse Engineering Framework
 viper-framework/viper
Binary analysis and management framework
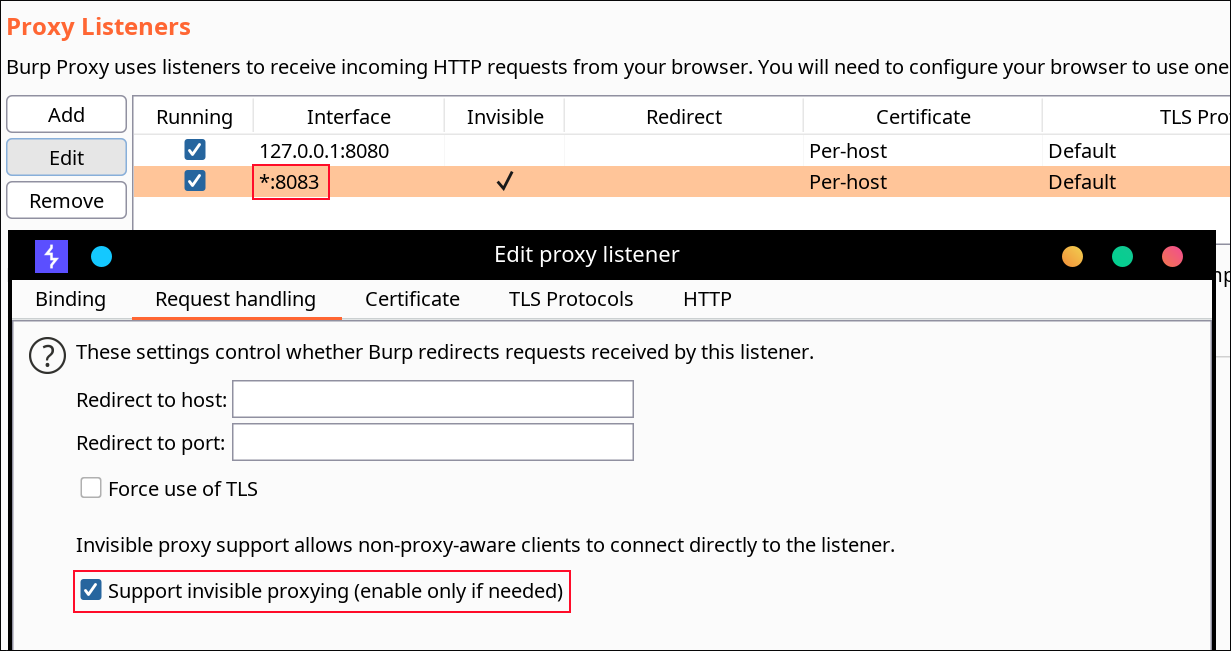 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 stefan2200/aparoid
Static and dynamic Android application security analysis
 jacobsoo/amtracker
Android Malware Tracker
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…