windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.

Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

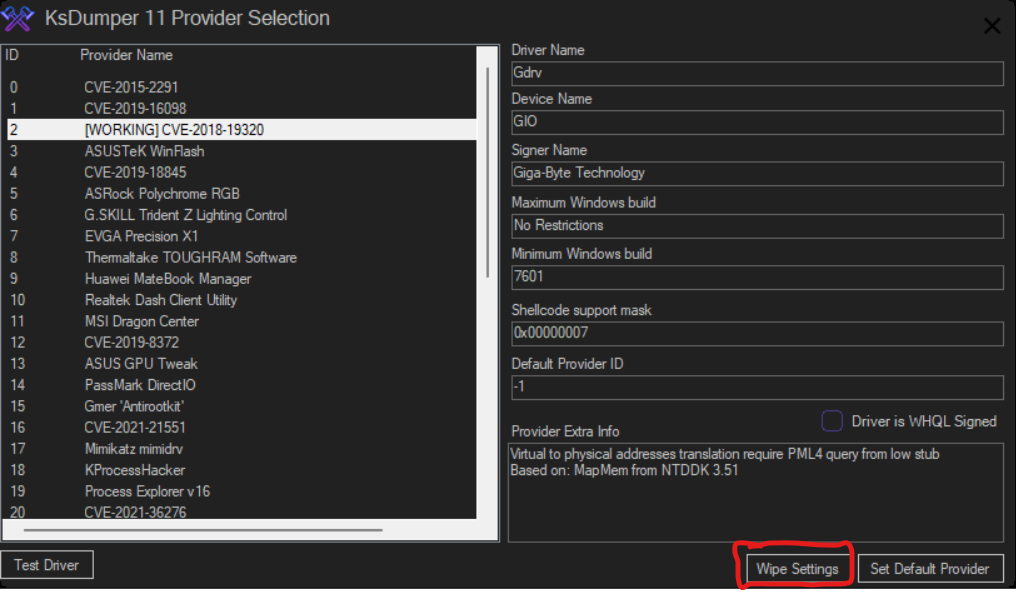
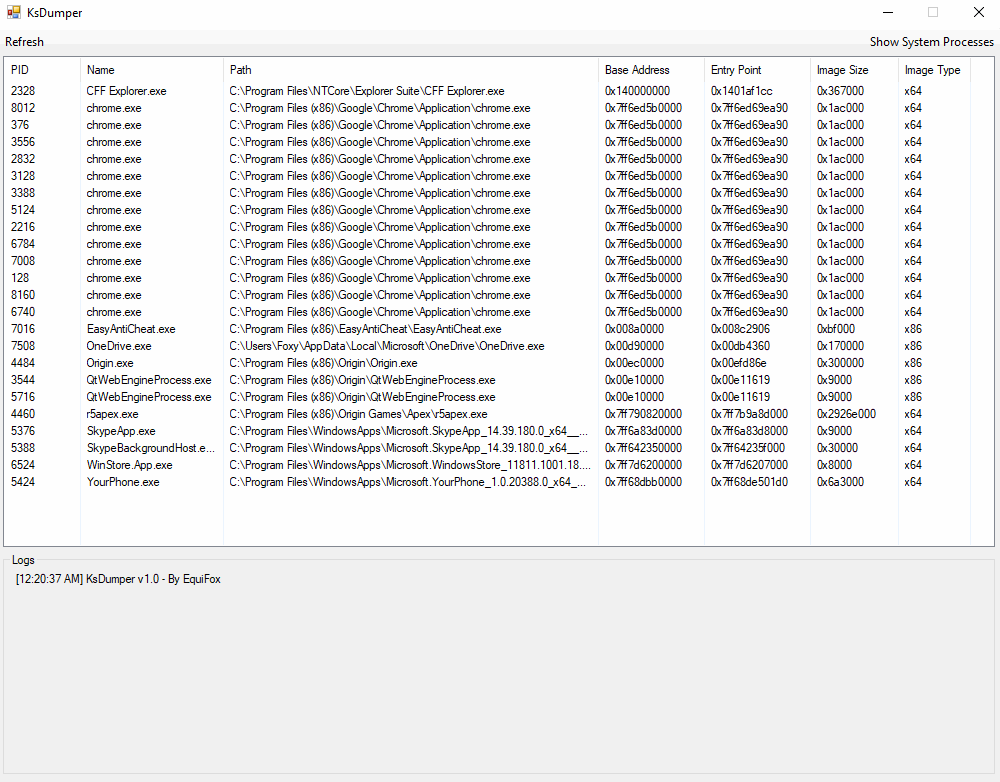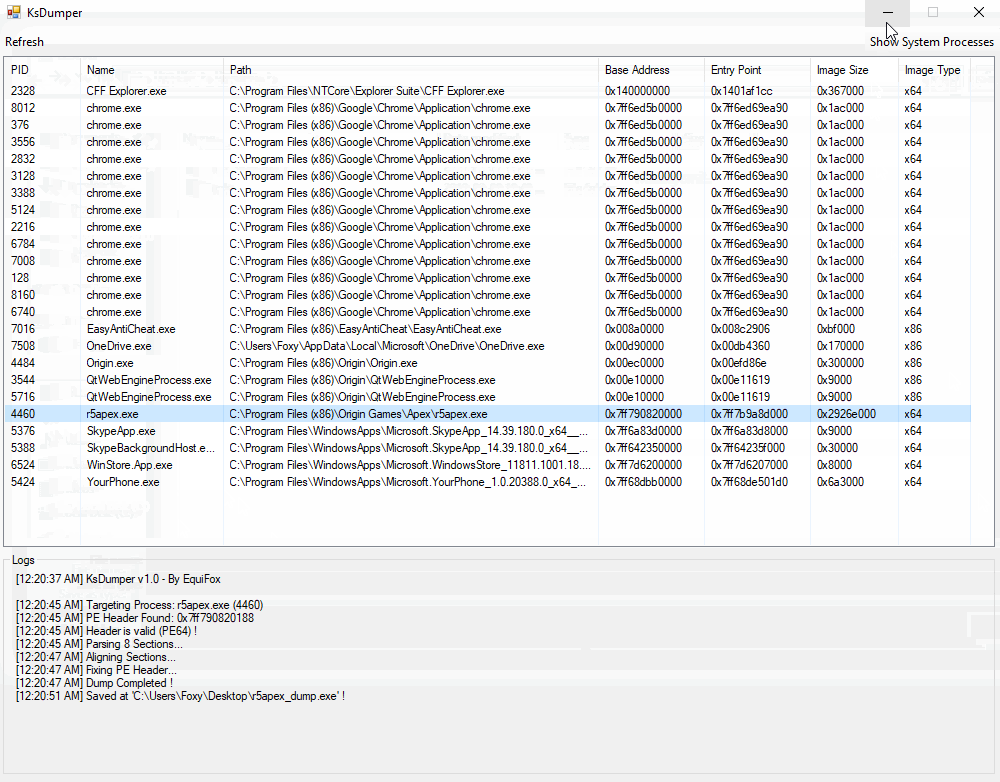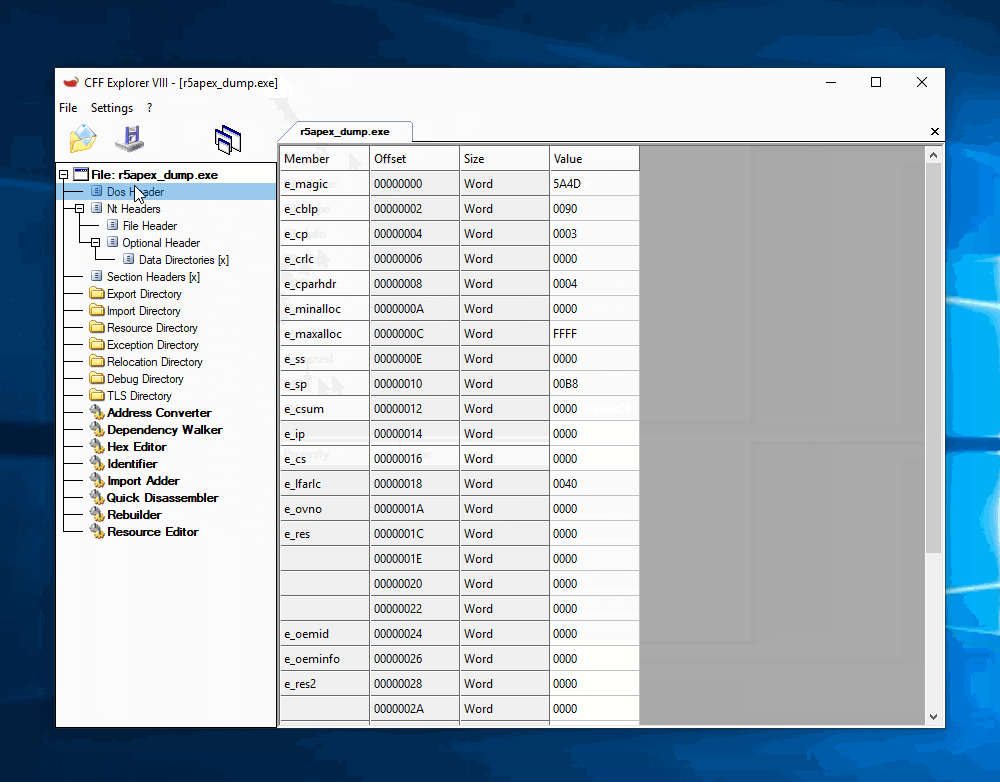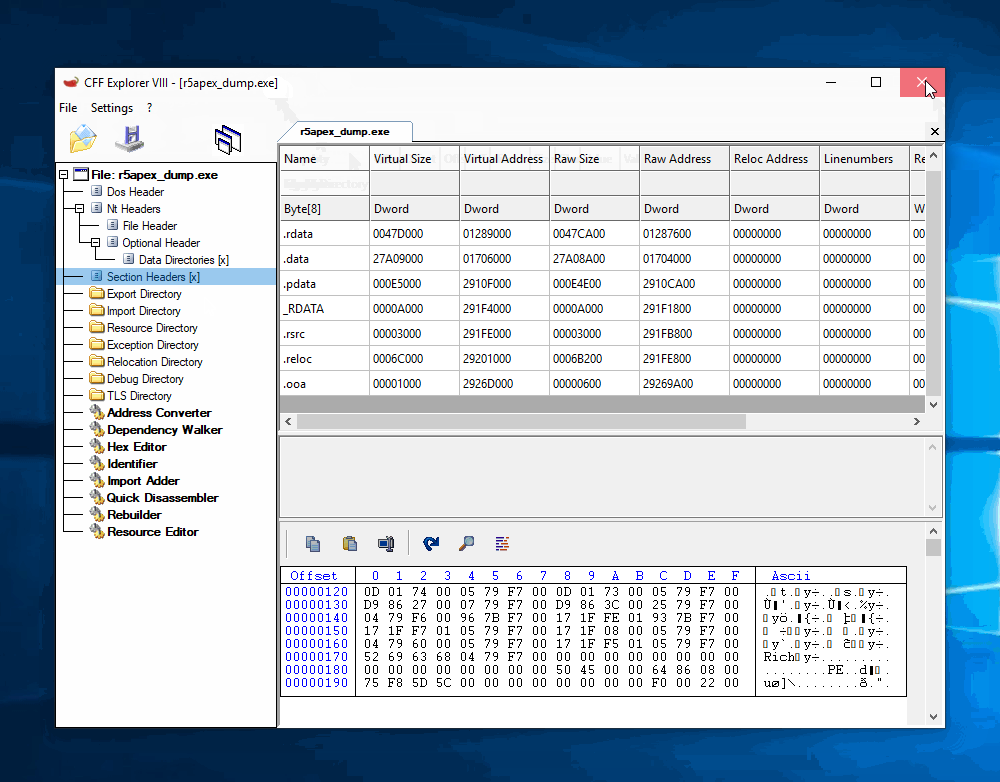
A revival of the classic and legendary KsDumper

ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.

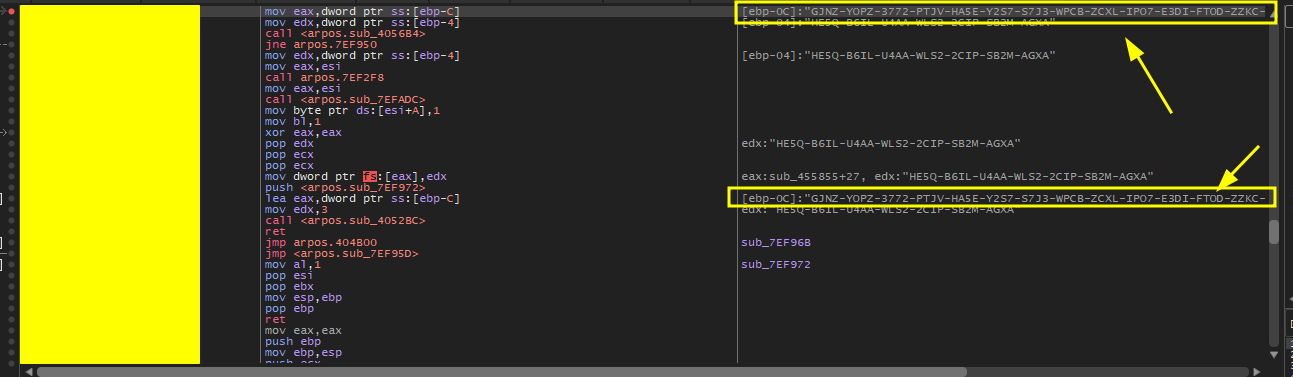
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…

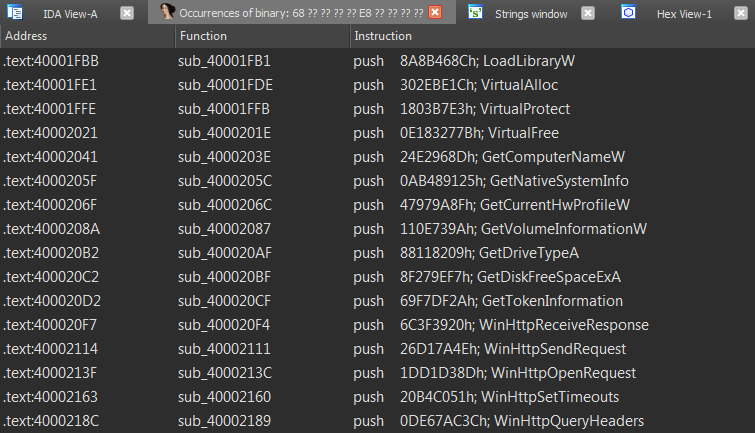
A small utility to deal with malware embedded hashes.

Dumping processes using the power of kernel space !

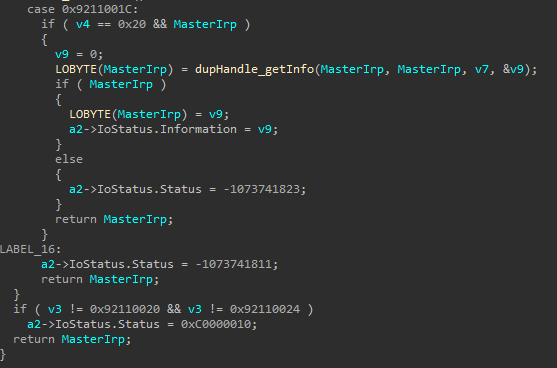
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

An API hooking framework for intercepting and monitoring Windows applications