
MagicArch
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
exploit-frameworksforensicsinformation-gathering+8
2
magicbytes/magicarchMagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 1n3/reverseapk
Quickly analyze and reverse engineer Android packages
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
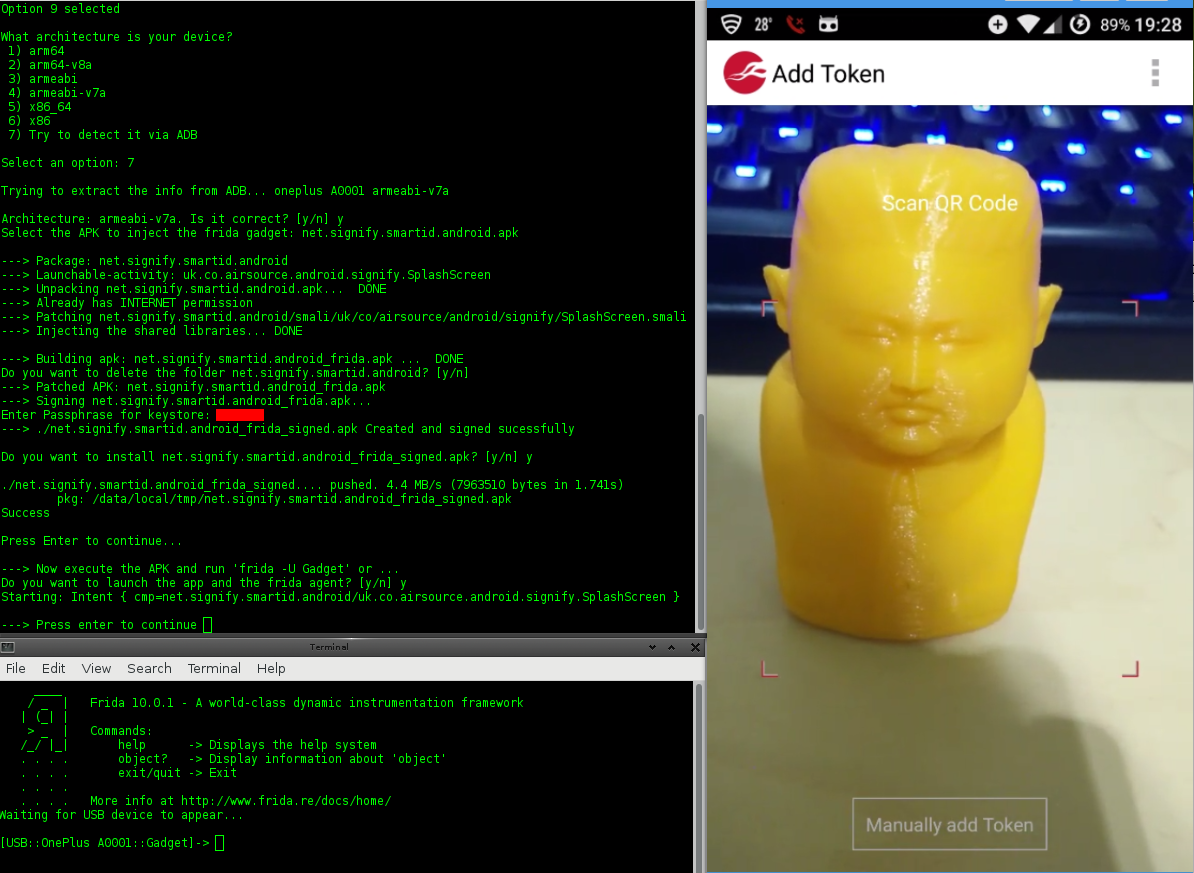 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 mouseos/aquos-r6-ghostlock
Temporary root exploit for Sharp AQUOS R6 A101SH S0029 using GhostLock CVE-2026-43499
 catxiaoshi/cve-2026-43499
PD2229B的43499(ghostlock)可行性研究
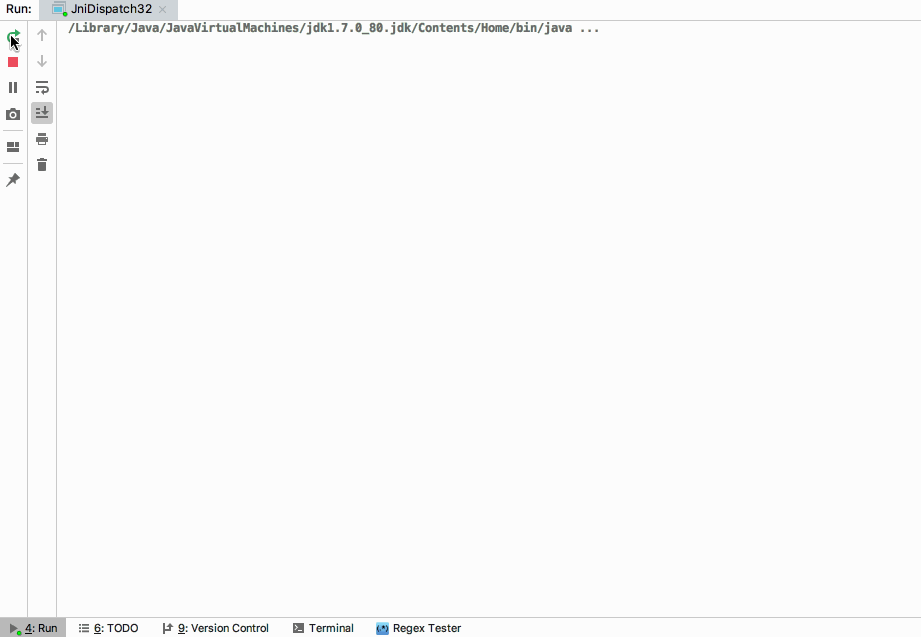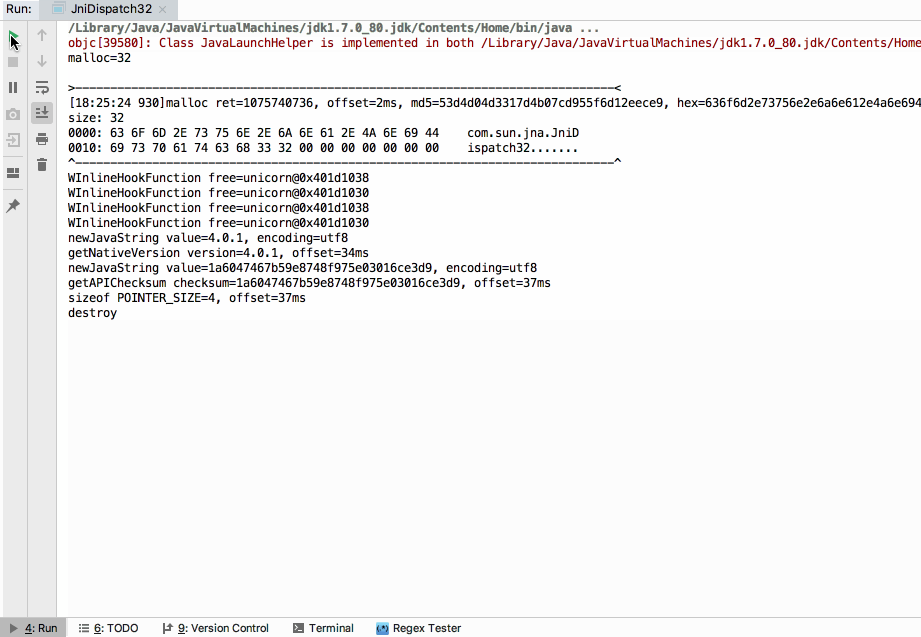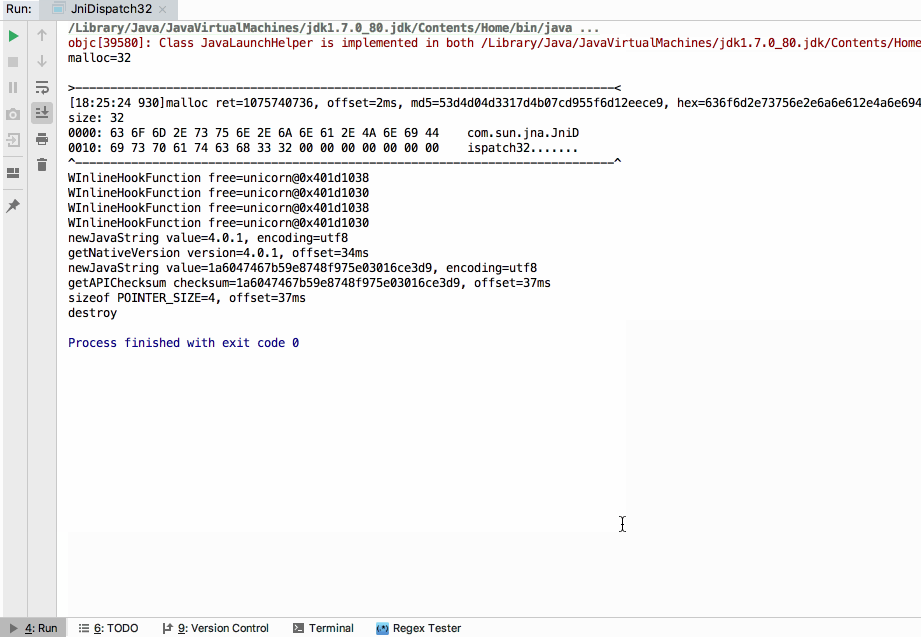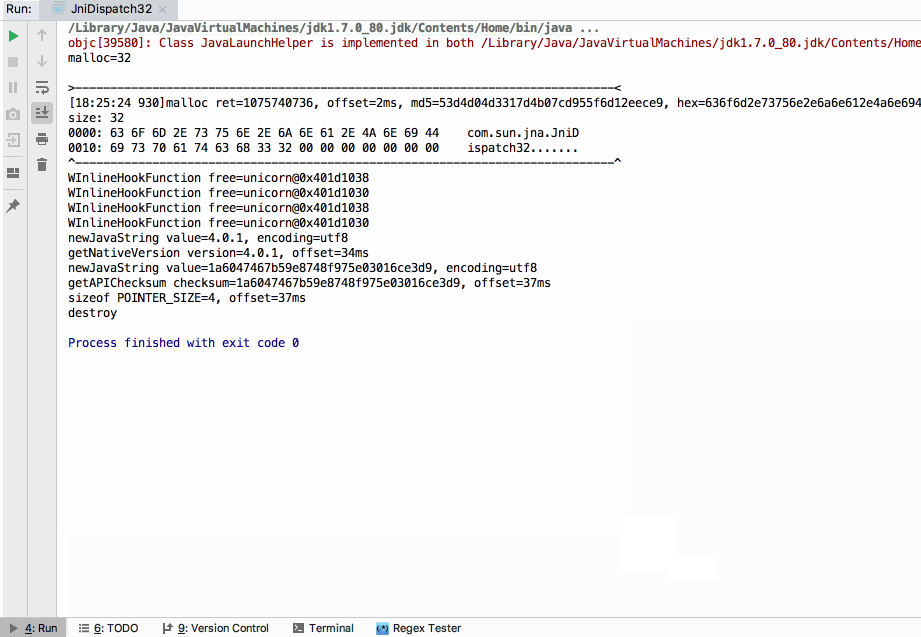 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 androguard/androguard
Reverse engineering and pentesting for Android applications
 worawit/blutter
Flutter Mobile Application Reverse Engineering Tool
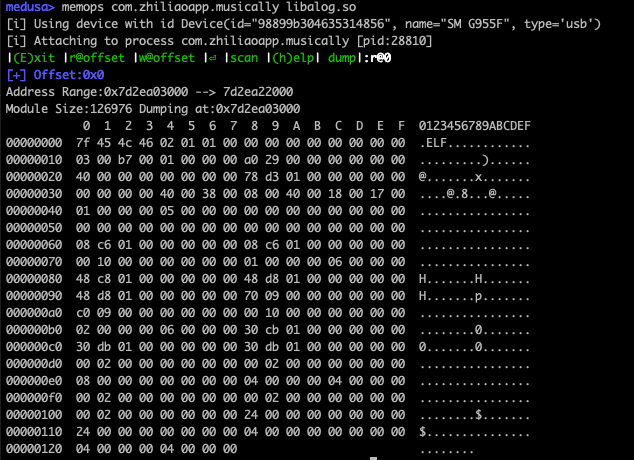 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
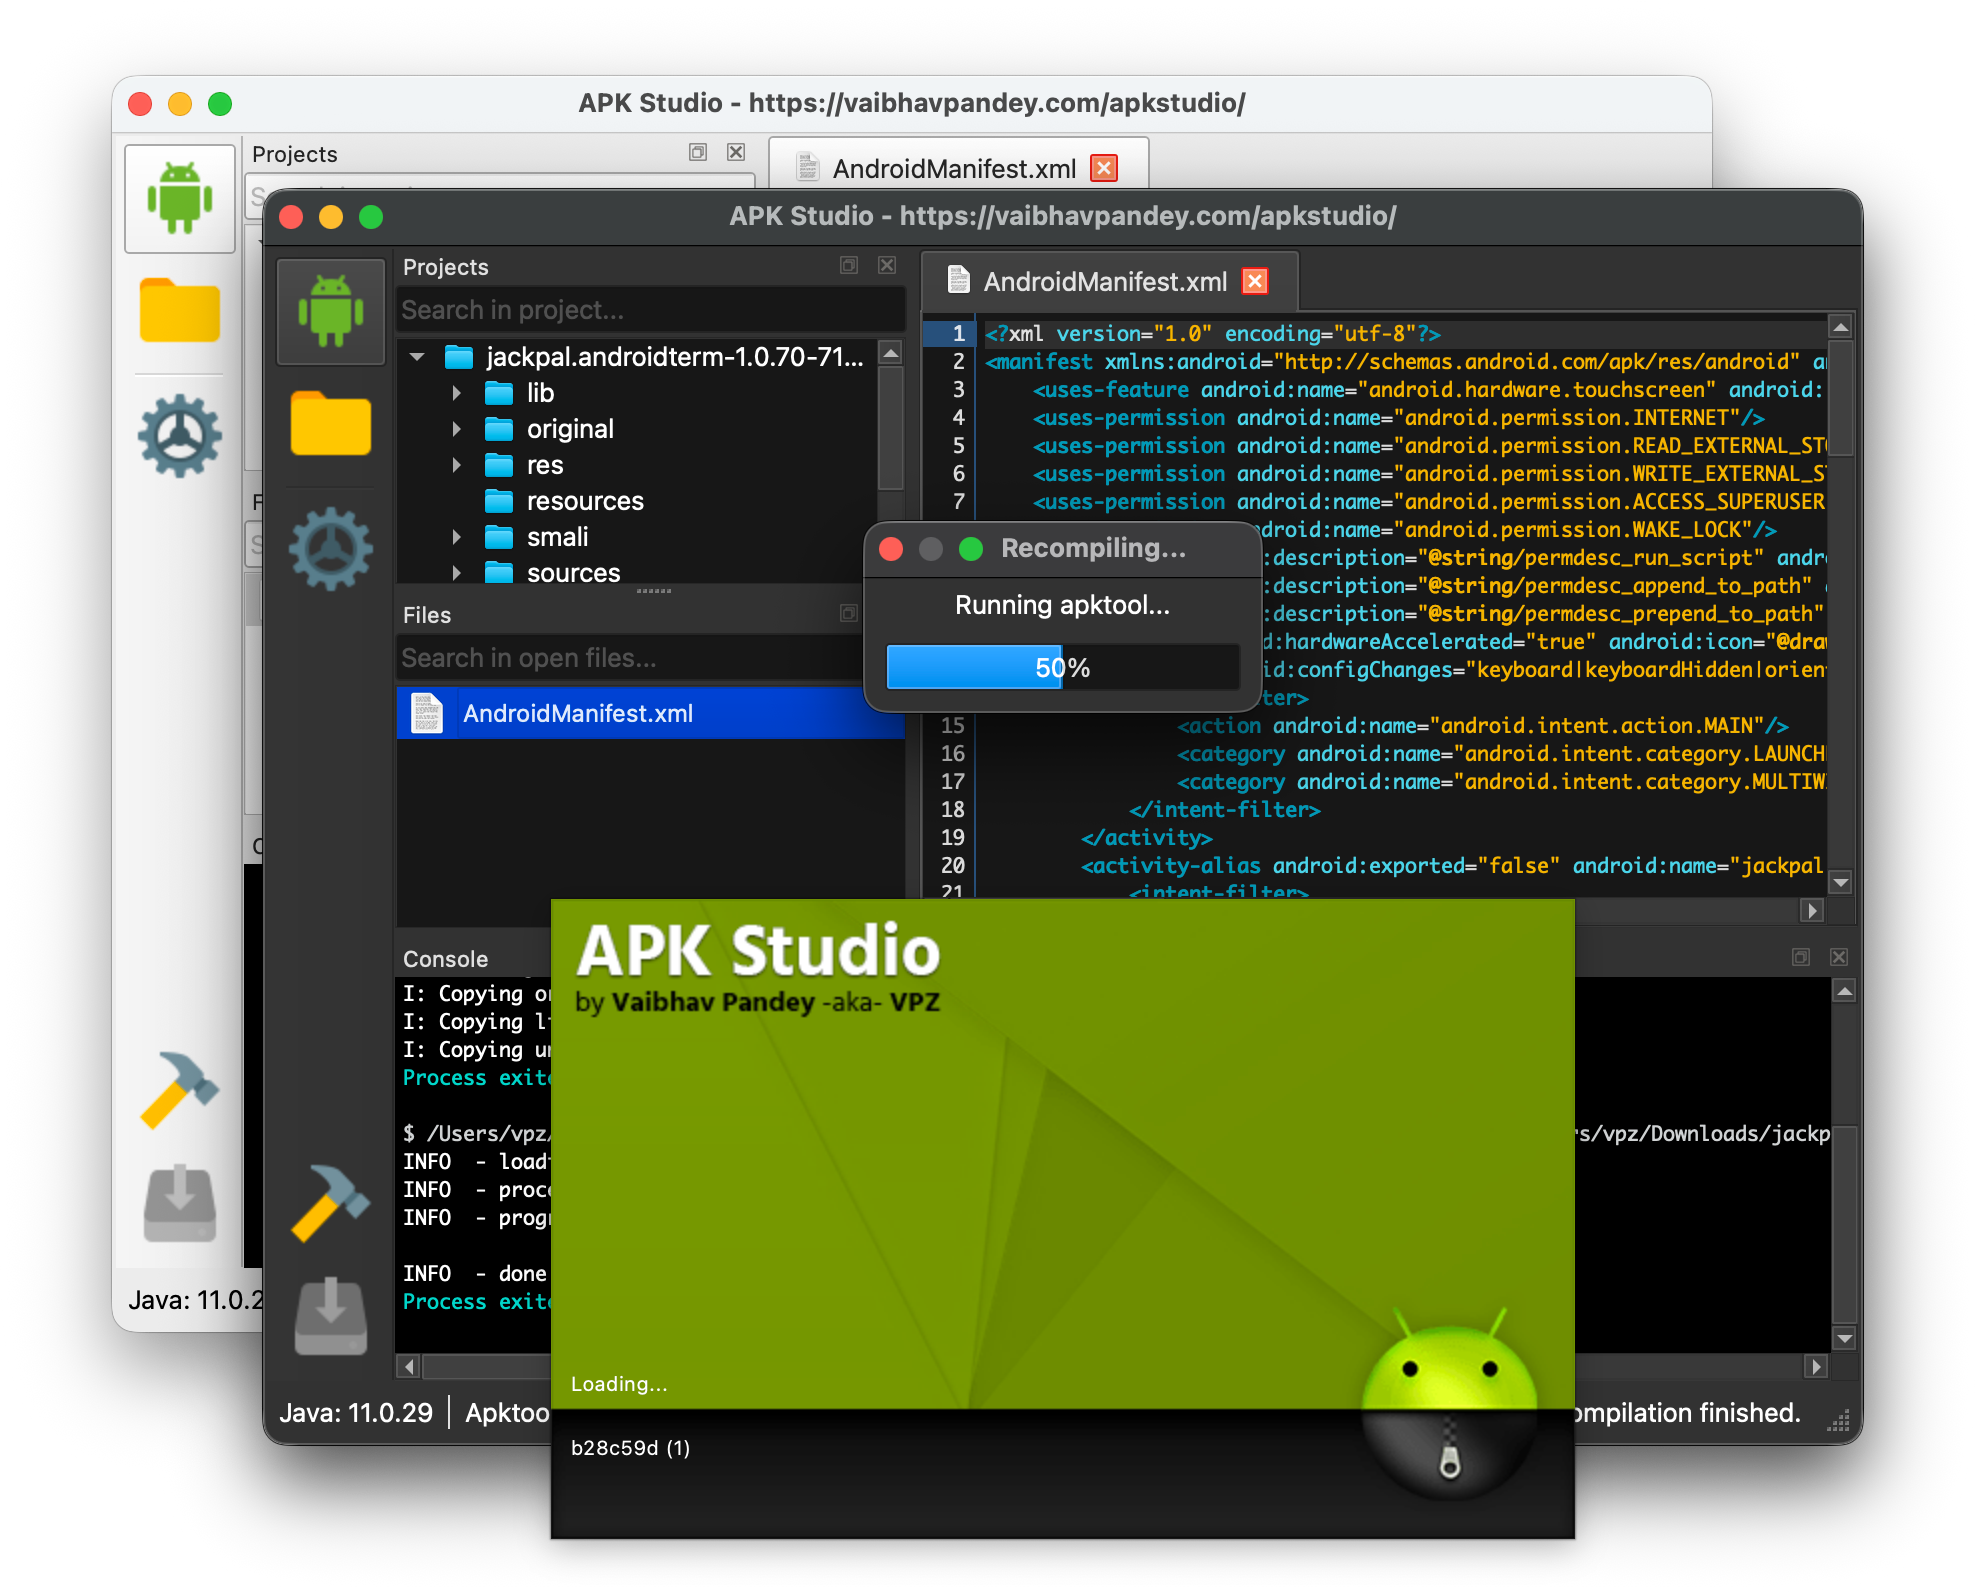 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…