
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
35 results
gr-qradiolink preview

gr-qradiolink

GitHubsupermagnum/gr-qradiolink

GNU Radio out-of-tree (OOT) module for QRadioLink blocks.
cryptographydigital-forensicseducation+7
15 months ago
linux-kernel-debugger preview

linux-kernel-debugger

GitHubgmh5225/linux-kernel-debugger

Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
4 years ago
ICALL-GADGET preview

ICALL-GADGET

GitHubgmh5225/icall-gadget

Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
binary-exploitationexploitationids-ips-evasion+5
12 years ago
CVE-2023-50564 preview
Archived

CVE-2023-50564

GitHubipuig/cve-2023-50564

Proof-of-concept exploit for CVE-2023-50564 targeting Pluck CMS, delivering a reverse shell via malicious module installation.
exploitationpayload-generationreverse-engineering+2
2 years ago
octopus preview
Archived

octopus

GitHubfuzzinglabs/octopus

Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
binary-analysisdynamic-analysis-sandboxingfuzzing+2
4945 years ago
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…

binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
uefi-firmware-parser preview

uefi-firmware-parser

GitHubtheopolis/uefi-firmware-parser

Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
binary-analysisembedded-systems-securityfirmware-analysis+2
9192 days ago
firmware-mod-kit preview

firmware-mod-kit

GitHubrampagex/firmware-mod-kit

Automatically exported from code.google.com/p/firmware-mod-kit
embedded-systems-securityfirmware-analysishardware-security+1
9968 months ago
rpef preview

rpef

GitHubmncoppola/rpef

Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
embedded-systems-securityexploitationfirmware-analysis+6
12413 years ago
ShadeBIOS preview

ShadeBIOS

GitHubffri/shadebios

PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025

binary-analysiseducationembedded-systems-security+5
681 year ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker

android-securitycommand-and-controlinformation-gathering+3
282 years ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
binary-exploitationdefensive-toolseducation+7
516 days ago
F9360-CVE43499 preview

F9360-CVE43499

GitHube-r-butch/f9360-cve43499

SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
android-securitybinary-exploitationeducation+5
45 days ago
ghostlock-app preview

ghostlock-app

GitHubariyanpegu/ghostlock-app

GhostLock One-Tap Execution App (CVE-2026-43499)
android-securitybinary-analysisbinary-exploitation+8
1 month ago
Rootsmart-v2.0 preview

Rootsmart-v2.0

GitHubcrackercat/rootsmart-v2.0

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
android-securitycommand-and-controldata-exfiltration+8
24 years ago
CVE-2025-3052 preview

CVE-2025-3052

GitHubthemalwareguardian/cve-2025-3052

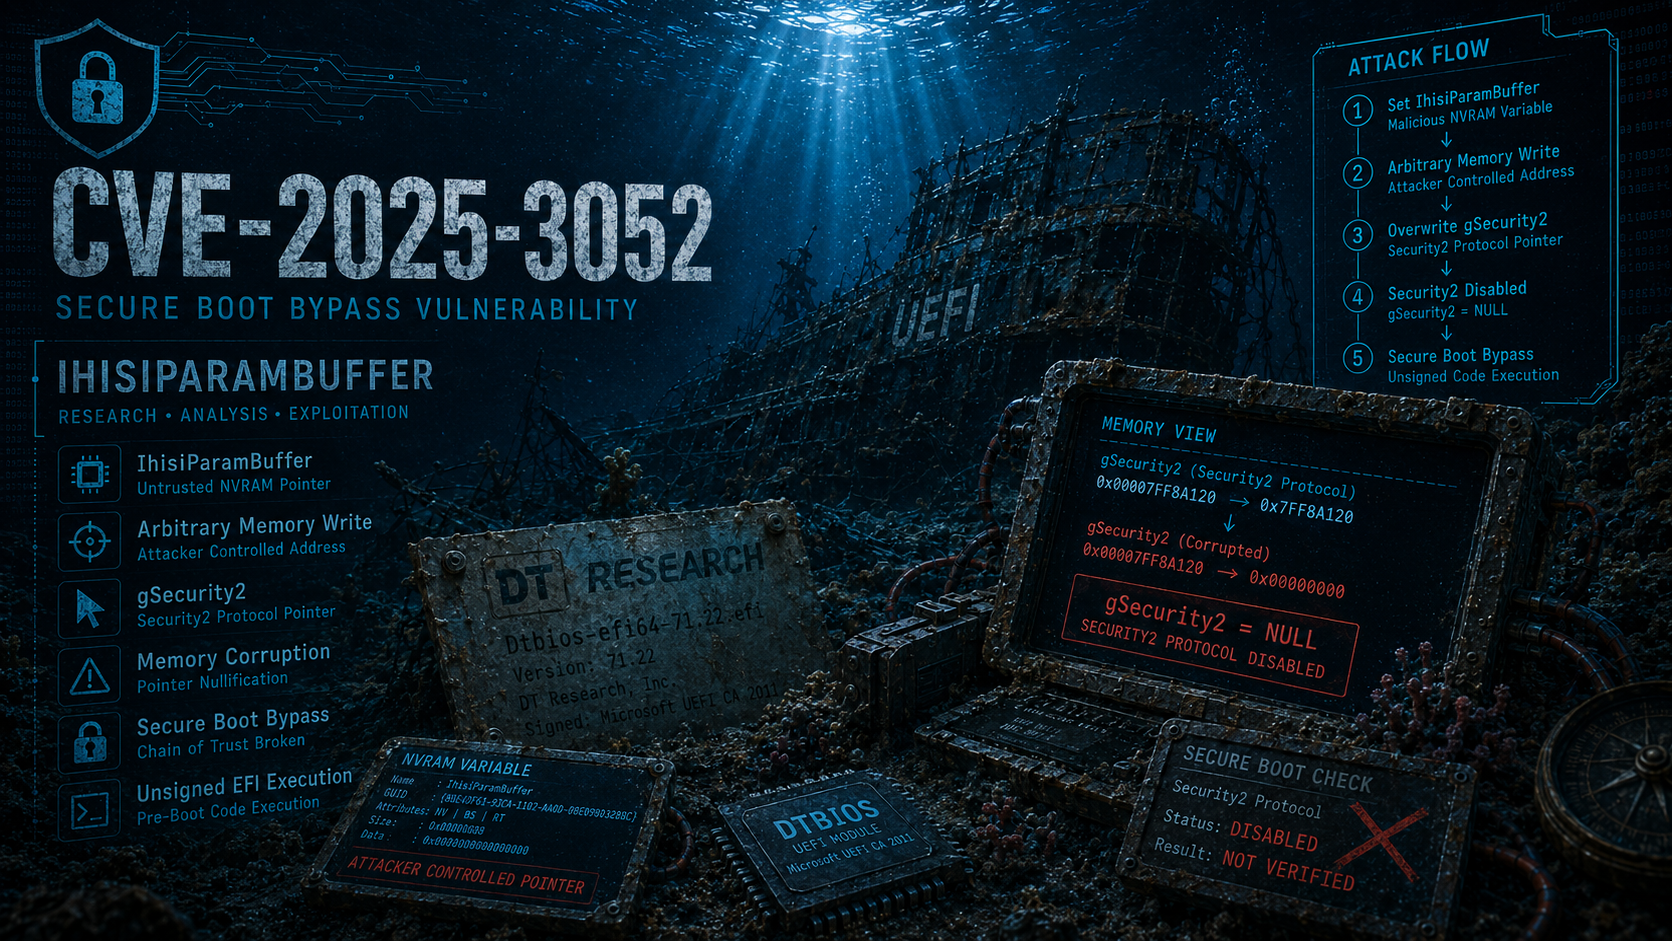
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
binary-analysiseducationembedded-systems-security+5
2 months ago
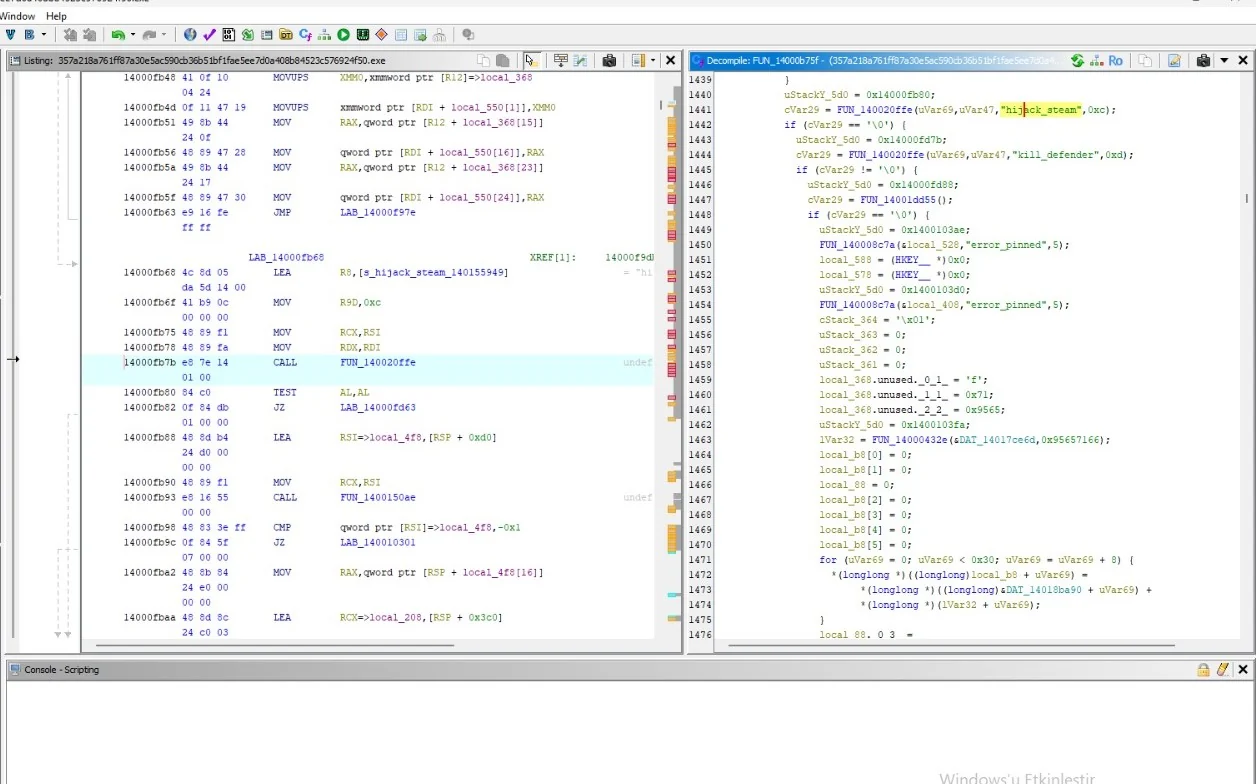
Rusty-Stealer-Keylogger-Screen-Streaming-Service-Persistence-Defender-Evasion-Analysis preview

Rusty-Stealer-Keylogger-Screen-Streaming-Service-Persistence-Defender-Evasion-Analysis

GitHubkaandemir993/rusty-stealer-keylogger-screen-streaming-service-persistence-defender-evasion-analysis

Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…

binary-analysiscommand-and-controldefensive-tools+6
1 day ago
Previous12Next